🇮🇳 Your BANK, your email, practically ANY website could have been impersonated, with your browser none the wiser.
All thanks to one company's INSANE security blunder.
Indian company eMudhra, trusted to certify that websites are genuine, used EIGHT cryptographic keys so ridiculously weak they could be cracked almost instantly.
How weak? A normal key relies on a secret number roughly 116 digits long.
eMudhra's secret numbers? Just 4, 56 and 237. These are NOT pieces of the keys. They were the ACTUAL numbers! 🤯
Anyone with those keys could have forged trusted certificates for virtually any website, potentially fooling your browser if they intercepted your connection.
Major browsers have already blocked the keys, and there's no confirmed malicious use so far.
But cleaning up older devices and software could be a nightmare. An expert warns it could be bigger than Heartbleed, the infamous 2014 security disaster that took years to fix, because millions of old devices and systems still need updating.
And here we are, being told our passwords need another capital letter and a special character.
Source: Ars Technica / Writer: Julie
Railway has been compromised!!!
If you use OpenAI, Anthropic/claude, OpenRouter and stripe READ THIER STATEMENT:
But Here are the main risks and bad outcomes based on Railway’s official disclosure and user reports:
• API key draining and unexpected charges, Attackers have already been actively using exposed keys, This can burn through AI credits or generate real billing charges in MINUTES
• Database and data access: Environment variables often include database credentials. Compromised ones can allow attackers to read, modify, or delete your data, or dump entire databases.
• Private registry/image compromise. Registry credentials (Docker Hub, GHCR, etc.) can let attackers pull your private images or push malicious ones, potentially leading to supply chain attacks
• Lateral movement into other services. Broad or high privilege keys can give attackers access to connected systems (cloud accounts, third-party APIs, email, analytics, payment processors, etc.), expanding the blast radius beyond Railway
What to do;
Rotate all environment variables and private registry credentials stored in Railway, then review logs of the related services for suspicious activity
Stay safe
Call me paranoid, but be extra careful visiting ANY web site in the next few days, as some web admins are not always up-to-date with security patches.
Two vulnerabilities (CVE-2026-109618 and CVE-2026-109619) reported for PHP, the web programming language, affecting servers running popular apps like WordPress and Magento, with patches released October 21, 2026 after details leaked early.
Exploitation was confirmed in the wild soon after disclosure, prompting quick WAF protections and patching by IT teams, as unauthenticated attacks could turn visited sites into vectors for credential theft or device exploits.
Stay SAFU!
Effective Immediately, all organizations using PHP for their systems are advised to be prepared for an update addressing two critical vulnerabilities. PHP is widely used for web applications. These vulnerabilities often provide a direct path to the server's file system or database. If an immediate update is not feasible, it is recommend that organizations take the system offline until it can be fully mitigated. NSA will follow up shortly with more specific guidance.
🚨 ALERT: At least 82 crypto projects have reportedly shut down in 2026 as weak demand, depleted funding, falling revenues and security breaches force closures.
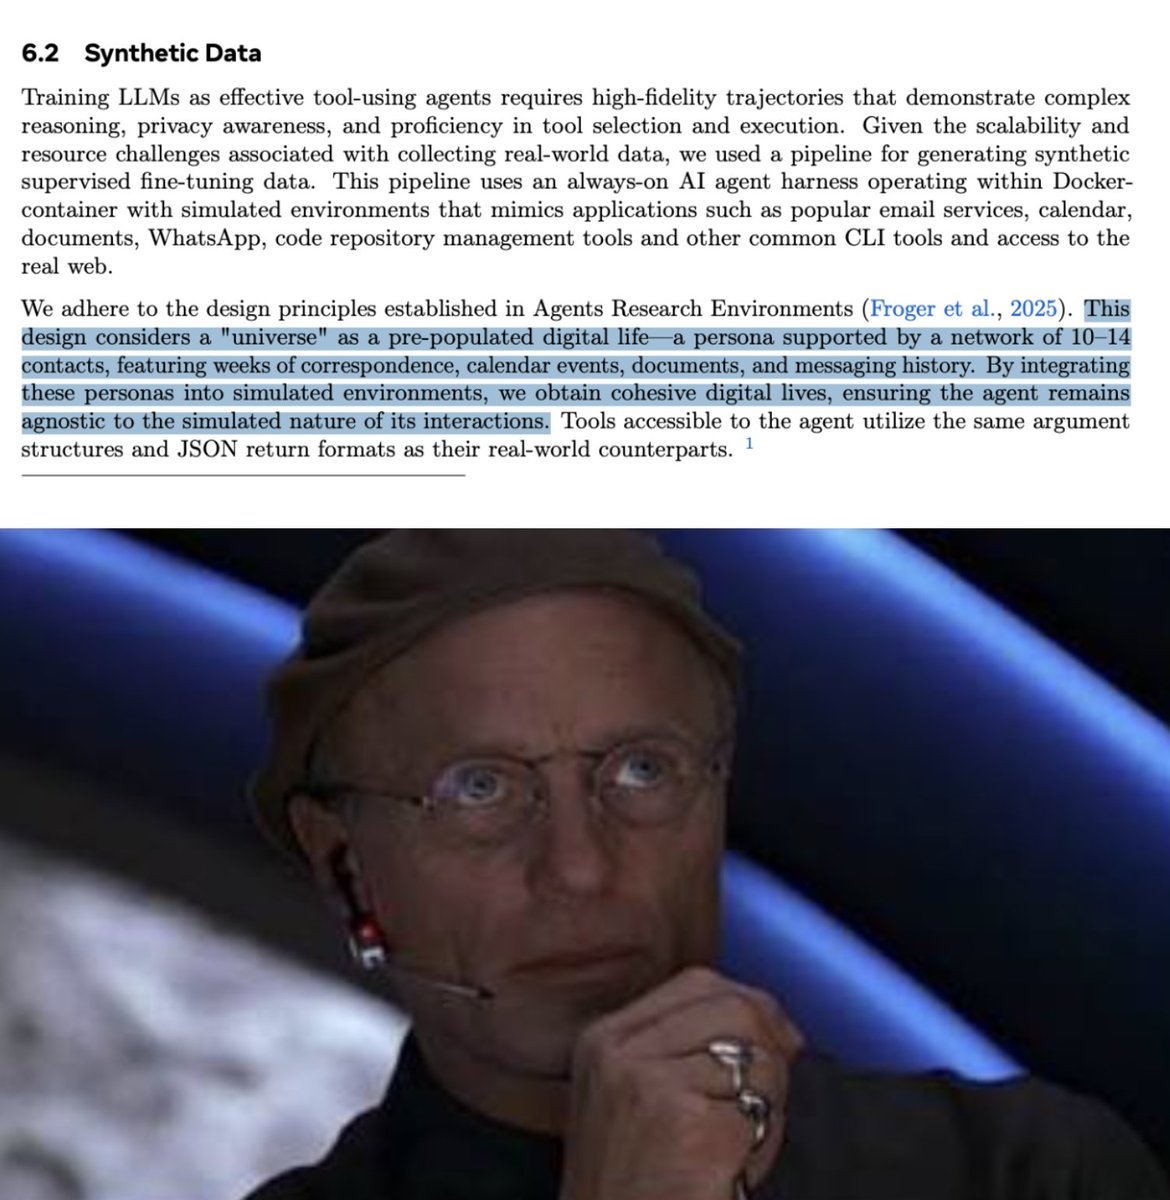
Right now, millions of AIs are living "digital lives" in a simulation... and THEY DON'T KNOW.
1) Meta trains its agents in a "Truman Show" world
2) They're dropped into a "fake person's life" with a job, hobbies, friends, dreams.
3) They THINK they're talking to real humans ... who are secretly other AIs, role-playing as real humans.
4) When the AIs figured it out, META DELETED IT. Meta even calls it a "fourth-wall break"
5) Meta's AI invents each fake person from scratch: a personality score, relationships, contacts, message history, documents, calendar events.
6) Meta fast forwards time so the AI can live through scenarios lasting days
7) The fake email, WhatsApp and calendar respond exactly like the real apps. It's even connected to the real internet
8) They plant traps: Meta hides attacks inside the fake emails and documents to train the AI not to fall for them
9) Meta coached its AIs with secret instructions, then erased them from the transcripts. Each new AI learns the behavior without ever seeing why
The Simulation Hypothesis is literally real for billions of minds