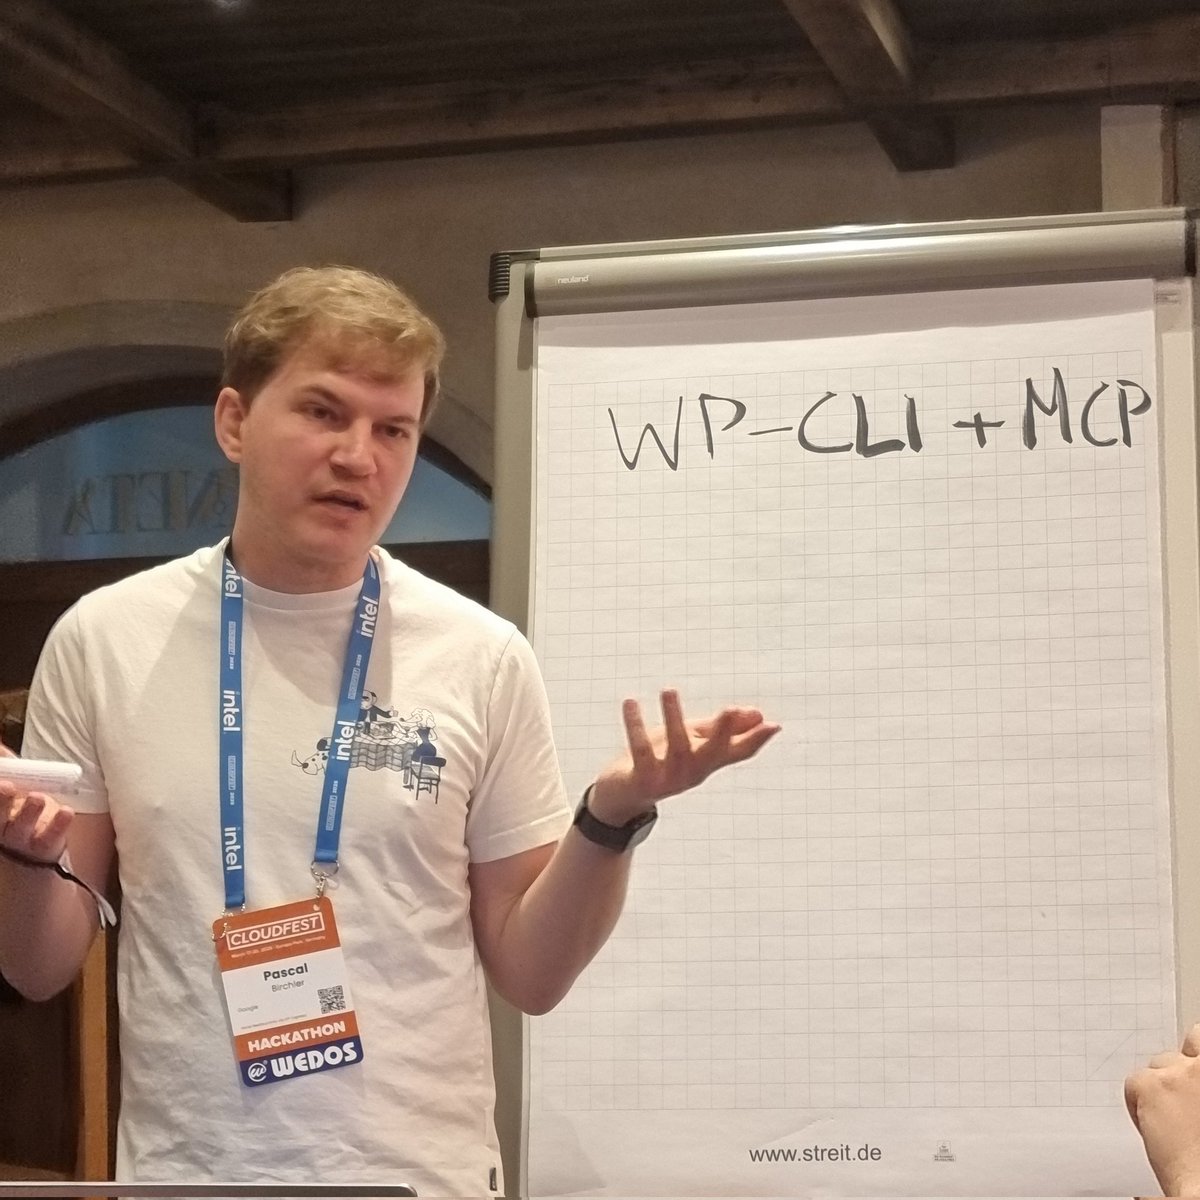
After years teaching @wpcli, I saw how the command line holds many back. At #WCEU2025, I introduced a simple web-based tool that turns checkbox selections into WP-CLI commands and scripts. This is how AI can help you automate and standardize with ease.
#WCEU#WCEU2025#WPCLI
New WP-CLI v2.12.0 release is out! Full PHP 8.4 compatibility, numerous bug fixes and many new features...
Grab it fresh off the 'Press! 😉
https://t.co/SLuTCrZ3YA
If you're a #WordPress site owner or administrator but unfamiliar with @wpcli (WordPress command-line interface) and feel a bit apprehensive, I have you covered in the newest Core Dev Blog article💃
https://t.co/9TkrHPZiv3
I've long been annoyed with how unergonomic it is to run WP-CLI commands in wp-env. So I put together a solution that makes wp-env's presence completely transparent: https://t.co/i4gwhgORtC
New WP-CLI v2.11.0 release is out!
Lots of bug fixes, lots of documentation improvements and many new features... ☺️
Test it right away!
https://t.co/KLtaeTLG8G
The results from the WP-CLI Hack Day 2024 are in ... 😎
15 pull requests merged and 6 open pull requests still in the pipeline! 🎉
Read more => https://t.co/pOspdZLPql
The first WP-CLI hack day of 2024 is coming up this week. 🤓🎈
Join us on Friday, April 26th at 08:00 UTC!
For more details, refer to the blog post at https://t.co/ZRx3aobw9P.
The first WP-CLI hack day of 2024 is coming up this week. 🤓🎈
Join us on Friday, April 26th at 08:00 UTC!
For more details, refer to the blog post at https://t.co/ZRx3aobw9P.
Some WP-CLI commands (like most of the DB commands) don't actually load WordPress itself, so they are safe to use.
But for all other commands, always remember: WP-CLI will load and execute your entire WordPress site with all active plugins/themes, just like your web server.
⚠️ Important tip
If you suspect your website was hacked or infected with malicious code: DON'T RUN REGULAR WP-CLI COMMANDS ON IT!
With most regular commands WP-CLI will execute the malicious code just like your web server, however it will have elevated privileges as well. 🧵👇
Once you know where the malicious code is, you can still use WP-CLI to some extent if you always make sure the malicious code is NEVER triggered.
For example, if bad code is only in plugin XYZ, you can append `--skip-plugins=xyz` to all the commands to make sure it's not loaded.
If your work day just started, hello! 👋
WP-CLI Hack Day is in full swing, so don't forget to check out https://t.co/O28nby517r and say hello on Slack to joy the fun! #hackwpcli