My team at Apple SEAR is hiring an intern to work on cellular baseband security research!
Apply here: https://t.co/oR77dX9WBv
We're looking for students who love digging into baseband firmware, building emulators, and hunting for vulnerabilities in cellular stacks and protocols.
Feel free to reach out if you have any questions.
#infosec
After 25 years, the original Xbox's last hidden ROM has finally been dumped: the CPU's microcode!
This has been a goal of mine for over 6 years, and I've worked on it off and on ever since.
Over the last couple of weeks, while building inventory and shipping orders, I've also been running hardware tests 24/7. This poor Xbox has rebooted over 50,000 times in those two weeks alone.
And it finally paid off.
The dump covers the entire 4,096-line microcode address space. The ROM itself occupies 3,200 of those lines, roughly 12 KB of microcode.
I can't overstate how huge this feels. After all these years, I finally have it.
A full write-up is coming next year!
📢Last call to sign up for our #BBOT training at @BSidesCHS, this Friday Nov 6. Free and hands-on, but you need to register to hold your seat and availability is running low. We hope to see you there!
https://t.co/uIt3nvK7KU
Just cleaned up the docs for the Abductor. 🔧
Adapter that lets CW312 targets run on the ChipWhisperer CW308 UFO.
UFO socket on one side. CW312 card-edge on the other.
https://t.co/C5Se8nQqNN
I finally found the recording of my talk: Glitching in 3D, low cost EMFI attacks here:
https://t.co/cWGFDBZxu4
Check it out if you want an intro to EMFI!
Frog put the keys in the HSM. "There" he said "now we cannot leak the private key". "But our servers can ask the box to sign with the key" said Toad.
"that is true" said Frog
@PalmerLuckey Nice! Just ordered mine, have some fun hardware hacking projects planned with it.
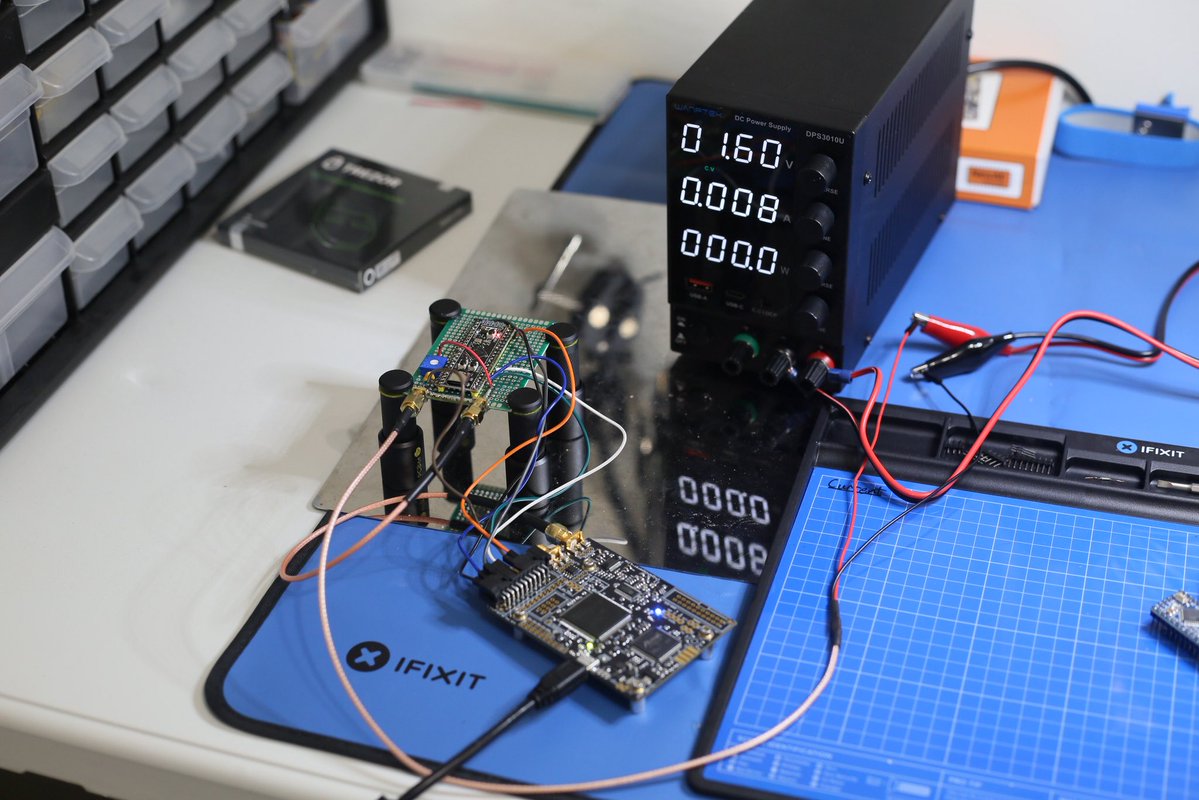
Because, who doesn't want to control their EMFI rig with a GBC?
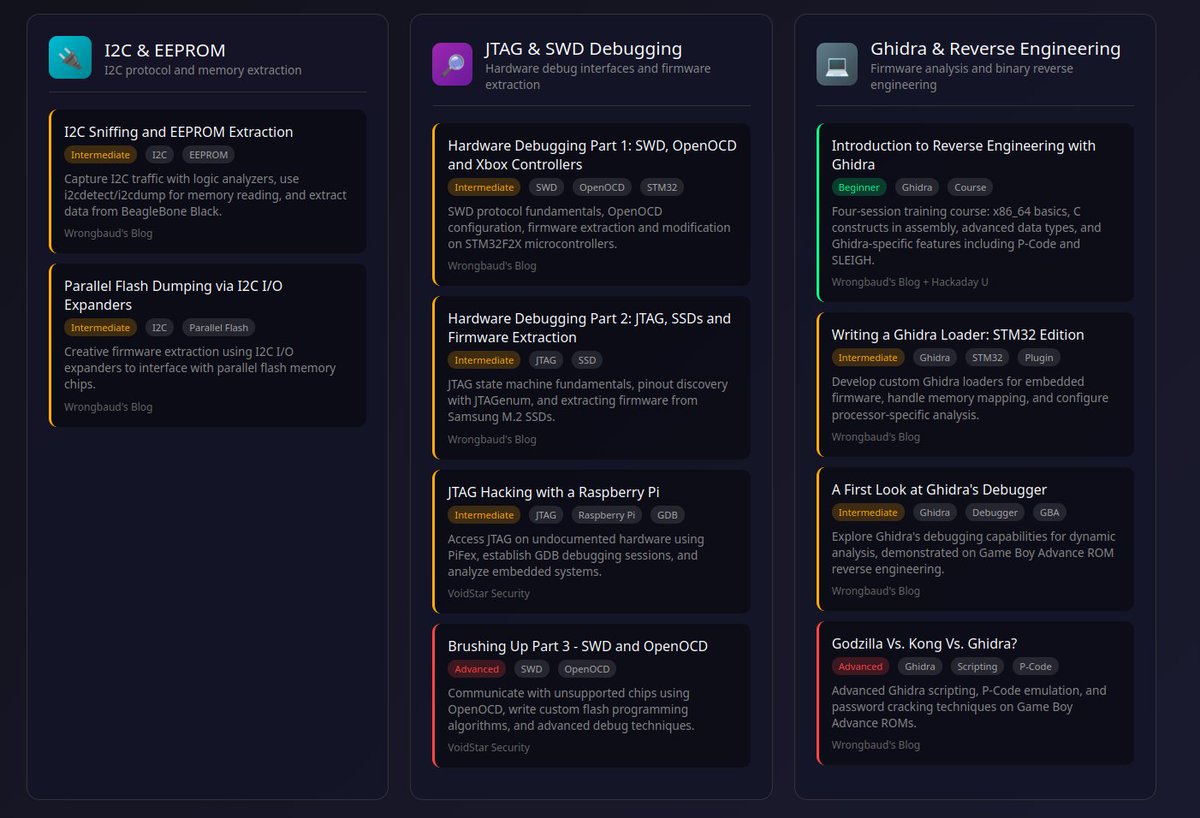
I asked CLAUDE to categorize and organize all of my blog posts and conference talks over the last 8 years and it generated an awesome roadmap for people looking to learn more about hardware hacking - all backed by my original content and writing:
https://t.co/V883lp4kXo
I finally found the recording of my talk: Glitching in 3D, low cost EMFI attacks here:
https://t.co/cWGFDBZxu4
Check it out if you want an intro to EMFI!
New blog post!
Extending Scapy for Hardware Reverse Engineering
https://t.co/cvezXY4RXp
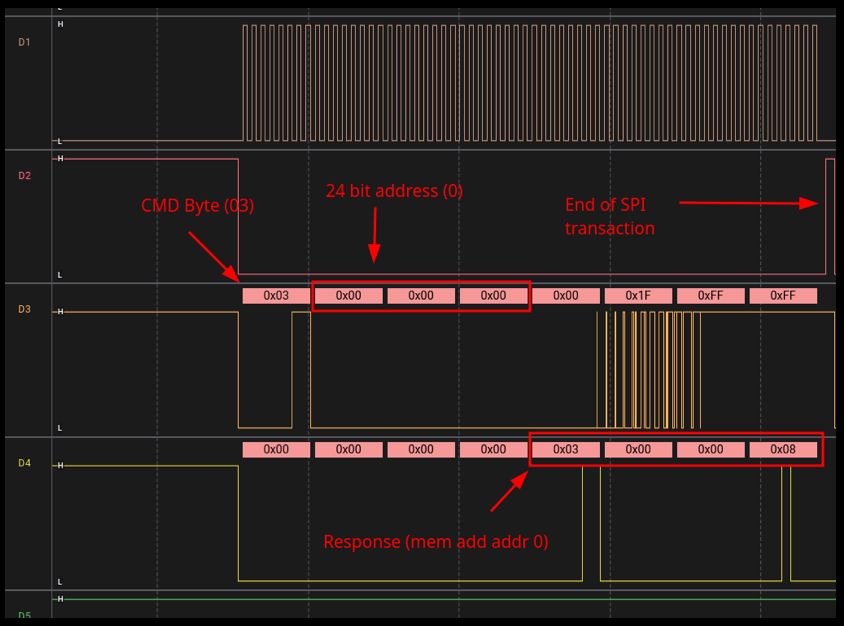
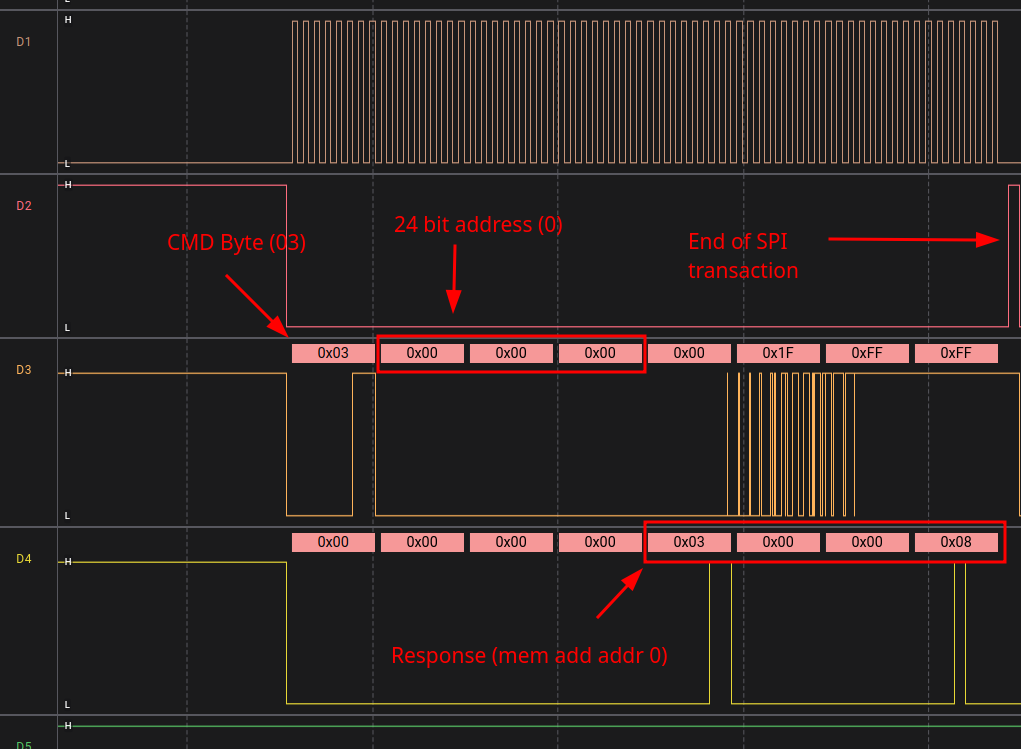
In this post we use Scapy to reconstruct a SPI flash image from a logic capture, with an introduction to QSPI!
@PalmerLuckey@glennbeck@anduriltech This is an incredible project, and chance you all are looking for hardware security research? Id love to be a part of this.