Today a malicious third party app named “SKR Claim” was submitted to the Solana dApp Store. The App Spotlight and Quests UI were updated following unauthorized access to the dApp Publishing Portal. The app requested entry of user seed phrases.
The app was live on the dApp Spotlight for one hour before being removed from the dApp Store. It is currently being removed from devices where it was installed.
Following review, our team identified and patched a bug that allowed linking to apps that were not fully published to mitigate this from happening again.
The Solana Mobile team will never ask you for your seed phrase, for crypto, or to connect your wallet to other apps/sites to claim airdrops.
An influencer is incentivized by attention, so their content must be optimized to be consumed and forgotten (cheap dopamine).
A personal brand is incentivized by money, so their content must be optimized to move you down their sales funnel.
An artisan is incentivized by the satisfaction that comes from the quality of their work. They need attention and money, but for the sole purpose of spending more time on work they enjoy and the impact it has.
Become an artisan.
⚠️If you use Gmail, read this.
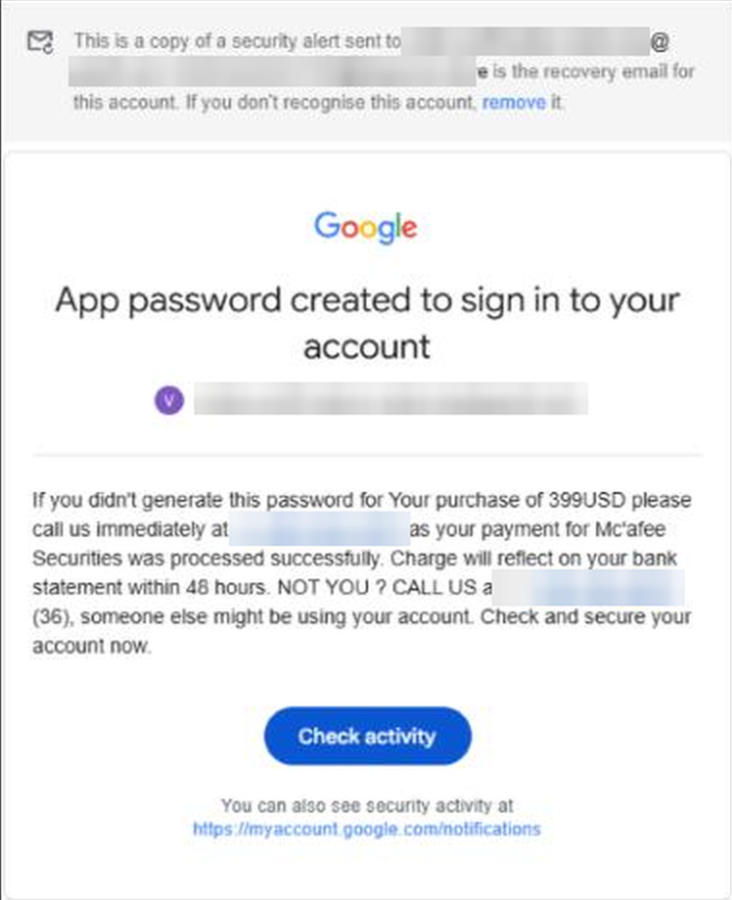
Scammers are hiding their messages inside REAL Google security alerts, so the emails pass the checks that normally catch fakes.
They type the scam text into the name of a Google app password, which makes Google send out a genuine, signed alert containing it.
Then they forward that alert to you.
One version flagged by the University of Michigan carried a fake $399 McAfee invoice and a phone number to call.
The real Google buttons in the email just open your own account page, where nothing looks wrong because nothing was breached.
That dead end is deliberate, leaving the scammer's phone number as the only "fix" left.
If an alert like this lands in your inbox, treat any phone number, reply request or button inside it as a red flag.
Even a genuine Google sender address is no longer proof that an alert is safe.
Elon (for some reason) trolling a multibillion dollar hack
and CZ threatening to full stack dump his shares that helped him buy X
please, just one boring day man
Tether froze more than 1.567B USDT related to a potential Binance exchange hack.
Protecting the industry and our partners is our main priority.
Stay safe everyone.
I did say we'd be releasing our models periodically...introducing Gemini 4 Carbon, our next frontier model.
Following Argon's release just two weeks ago, Carbon shows the pace at which we’re pushing the frontier, it ranks #1 on the recently updated v5.0 of @ArtificialAnlys Intelligence Index at 59. It also leads across key cybersecurity evaluations scoring 88.2% on SEC-bench Pro for finding vulnerabilities, 54.8% on ExploitGym for exploitation, and 71.0% on CWE-bench for patching.
We’re seeing significant improvements in long-horizon tasks even compared to Argon, and we’ve strengthened frontier safeguards.
As we did with Argon, we’re going to roll it out gradually + responsibly. Some trusted cyber defenders will get access starting this week. We'll be expanding it to more partners through our Fairwind Program, ahead of wider availability soon, so hang tight!