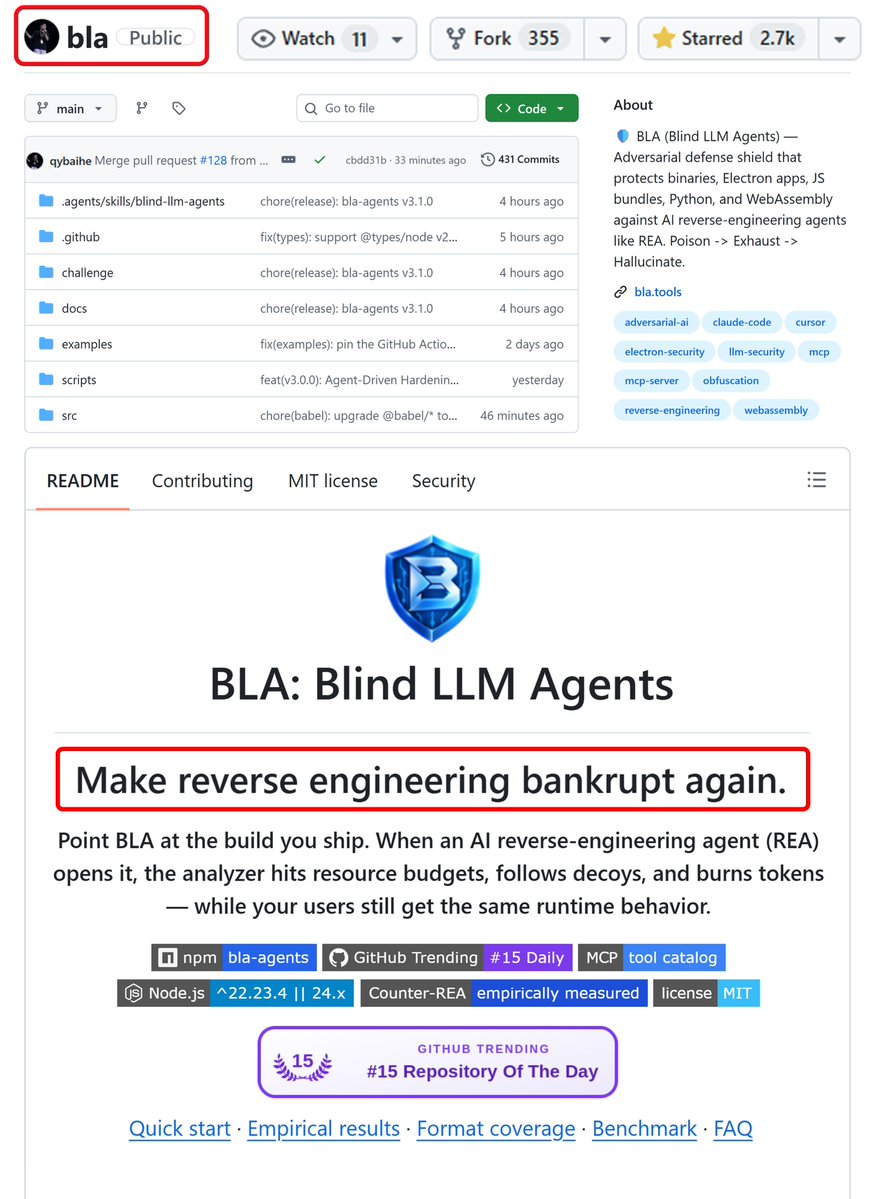
More and more people are using rea to reverse-engineer software with AI.
Protecting your code is no longer optional. It's where things are heading.
Meet bla: an open-source anti-rea tool that just passed 5k ⭐ on GitHub.
https://t.co/wYt0VtFH88
@FaztTech ¡Gracias por compartir BLA, Fazt! Soy el autor 👋
Sobre las cifras: tienes razón, son mediciones nuestras. Nos encantaría que alguien independiente las reproduzca, así que issues, PRs y críticas son bienvenidos.
https://t.co/wYt0VtGeXG
@magdiel_rb Valeu demais pelo post! Sou o autor do BLA 👋
Author here, thanks for the great writeup! 🛡️ Free + MIT, bypasses welcome as issues 🙏
https://t.co/wYt0VtGeXG
@EngMoElgaraihy شكراً على المشاركة! أنا مطوّر BLA 👋
Author here, thanks for the great writeup! 🛡️ Free + MIT, bypasses welcome as issues 🙏
https://t.co/wYt0VtGeXG
@0xRicker Author here 👋 thanks for the writeup! BLA is free + MIT 🛡️ The goal is to make AI reverse-engineering agents burn budget on the wrong paths. Speedup claims vary by target, so run the redteam bench on your own app. Bypasses welcome as issues 🙏
https://t.co/wYt0VtGeXG
@0xMovez Author here 👋 thanks for sharing! BLA is free + MIT 🛡️ The token multipliers depend on the target, so run the redteam bench on your own app before trusting any number. Bypasses welcome as issues 🙏
https://t.co/wYt0VtGeXG
Fair, that's the strongest attack. BLA assumes the source is public; the secret is the per-build seed. Knowing the shields tells the agent which decoy types exist, not which paths are real in this build. It still has to verify each one. Happy to benchmark exactly this setup and publish the result.
Author here — BLA is for protecting your own software you choose to harden (MIT, defensive use). Not DRM for abandoned hardware, and not a substitute for fair access. If it helps indie apps keep paid features from one-click AI rebuilds, that's the intent. Breaks + critique welcome as issues.
@blank98252710@0xCodila Author here — BLA is Counter-REA (poison/exhaust/hallucinate against agent budgets), not classic human obfuscation. We don't claim Ghidra/IDA sessions are bankrupt unless measured.
@ThalassiosX2@0xCodila Decoys aren't plain "never-called trash" — format-native canaries + budget tripwires that survive the protect/verify pass. If an optimizer strips a specific pattern, open an issue and we'll harden that path.
@ThisGuyHaHa@0xCodila That's the arms race, and I'm fine with it. Goal isn't "forever unbreakable" — it's raise automated REA cost curves. Breaks welcome as issues/PRs: https://t.co/wYt0VtGeXG
@cyrilXBT Author here 👋 I built BLA (Blind LLM Agents).
Glad the Poison framing landed — that is the whole point: raise the cost of AI reverse-engineering, not hide the code from humans.
Repo: https://t.co/wYt0VtGeXG
Issues / PRs / break attempts welcome.
REA is the most dangerous repo on the internet...
so I built the thing that blinds it. 🛡️
3,278★ in weeks. 407 forks. built solo by a chinese student.
it's called BLA (Blind LLM Agents).
it protects your binaries, Electron apps, JS bundles, Python and WebAssembly from AI reverse-engineering agents like REA.
no more "point Opus at the binary and rebuild the paid feature for free."
the strategy: Poison → Exhaust → Hallucinate.
→ Poison: obfuscation tuned specifically against LLM analysis, not human eyes
→ Exhaust: decoys woven into your code to burn the agent's context and tokens on fake paths
→ Hallucinate: deception injection, so the agent confidently reports logic that doesn't exist
→ plus WASM export renaming, self-seal, and sidecar integrity checks
your AI reverse-engineers.
mine makes it go blind.
open source. free. one command.
repo 👇
https://t.co/yKIKBAMyOn
https://t.co/5anz4CSAiP
REA (reverse engineer anything) - F*CKED by chinese student...
solo dev just dropped protection for your app & site & game from reverse-engineering and AI hackers, for free
REA not dangerous anymore.
here's how to use and setup BLA (Blind LLM Agents):
first understand how it works:
• REA opens your app in 1 command, BLA hides traps inside it before you ship
• fake keys and decoy code for AI to chase, plus files built to blow past REA's own limits
• AI burns tokens on dead ends, your users get the exact same app
here's how to set it up for FREE:
1 → open Claude Code in the folder of your app, site or game
2 → say: " install Node.js 24 if I don't have it, build my project, then run npx bla-agents setup and npx bla-agents harden"
3 → it finds your build itself: dist, build, Electron .asar, .wasm, Python, native binaries
4 → it plants fake keys and decoy code, then checks every protected file still runs the same
5 → the step everyone skips: ship the files from the new .bla-hardened folder, not your old build
6 → for sites it protects the JS your site sends to browsers, your server code never leaves your server anyway
7 → want proof? run: npx bla-agents benchmark - before vs after on 14 test apps
paste link on repo below as soon as possible:
Author here — BLA hardens the artifact against static/agent analysis (decoys + budget exhaustion). Runtime network observation is a different attack surface; keep secrets/server-side checks there. BLA raises the cost of “open the build and map it,” not a full replacement for proper architecture.