In Bug Bounty we are not competing only with Bug Bounty Hunters or Cyber Security Engineers we are even competing with Billion Dollar Penetration Testing Companies.
For years, Google API keys (AIza...) had little to no real-world impact.
But recently, many of them unexpectedly gained access to Google Gemini.
curl "https://t.co/w9AaJy4JhU"
This appears to be a widespread misconfiguration that can be hunted in the wild.
A few months ago, I found a really cool technique to make prompt Injection more deterministic. @monkehack convinced me to write it up. Enjoy!
https://t.co/BZ6nNqh6dw
Low-key websites I quietly rely on
1) https://t.co/DOL411EVne
Gives you a brutally clear learning path for roles like frontend, backend, DevOps, etc
No fluff, just “learn this → then this → then this”.
2) https://t.co/Zoh2Jtfiqq
An online playground to quickly test HTML, CSS, JS without setting up anything locally
Perfect for quick experiments and debugging ideas
3) https://t.co/cufUB80WLF
A collection of reusable React hooks with real use cases
Saves time and helps you avoid rewriting the same logic again and again
4) https://t.co/6lXfAIq2Zj
Concise cheat sheets for languages, frameworks, and tools. Ideal when you forget syntax and don’t want to read a 20-minute blog
5) https://t.co/CRXx9MVHgP
Turns messy JSON into a clean visual tree
Makes understanding large APIs and configs way easier than staring at raw text
6) https://t.co/ue9PTccXQJ
Lets you generate and preview color palettes instantly
Useful when you want decent UI colors without guessing or copying blindly
7) https://t.co/j5NE9ZShW6
Build, test, and debug regex step by step with explanations Honestly, the fastest way to stop hating regex
8) https://t.co/gdZxoGApT6
Shows how big an npm package really is before you install it
Helps you avoid bloating your app with “tiny” libraries
9) https://t.co/9KaWeMqJox
Tells you which CSS/JS features actually work across browsers Essential before using shiny new features in production
10) https://t.co/QZnckJ1VXA
Google’s own diagnostics tools for DNS, email, headers, and network issues
Surprisingly useful for debugging real-world problems
👉 Which one of these do you already use and which one did you not know existed?
🐞If you hunt modern web apps, this guide is worth your time.
A deep dive into Next.js security testing covering real attack surfaces — SSRF, XSS, CSTI/SSTI, cache issues, data leaks, and more — with a mindset tailored for bug hunters and pentesters.
Frameworks evolve fast, and so do their flaws.
Understanding how Next.js handles rendering, routing, APIs, and caching can open doors to impactful findings.
Great work by @daoud_youssef — definitely adding this to my testing workflow.
🔥https://t.co/qITh7eFNNy
#BugBounty #AppSec #WebSecurity #Pentesting #NextJS #CyberSecurity #SecurityResearch
[Download 698-page PDF eBook]
Everything You Always Wanted To Know About #Mathematics* (*But didn’t even know to ask)
A Guided Journey Into the World of Abstract Mathematics, Theorems, and the Writing of Proofs: https://t.co/JLsDOmpP1q
Serious post.
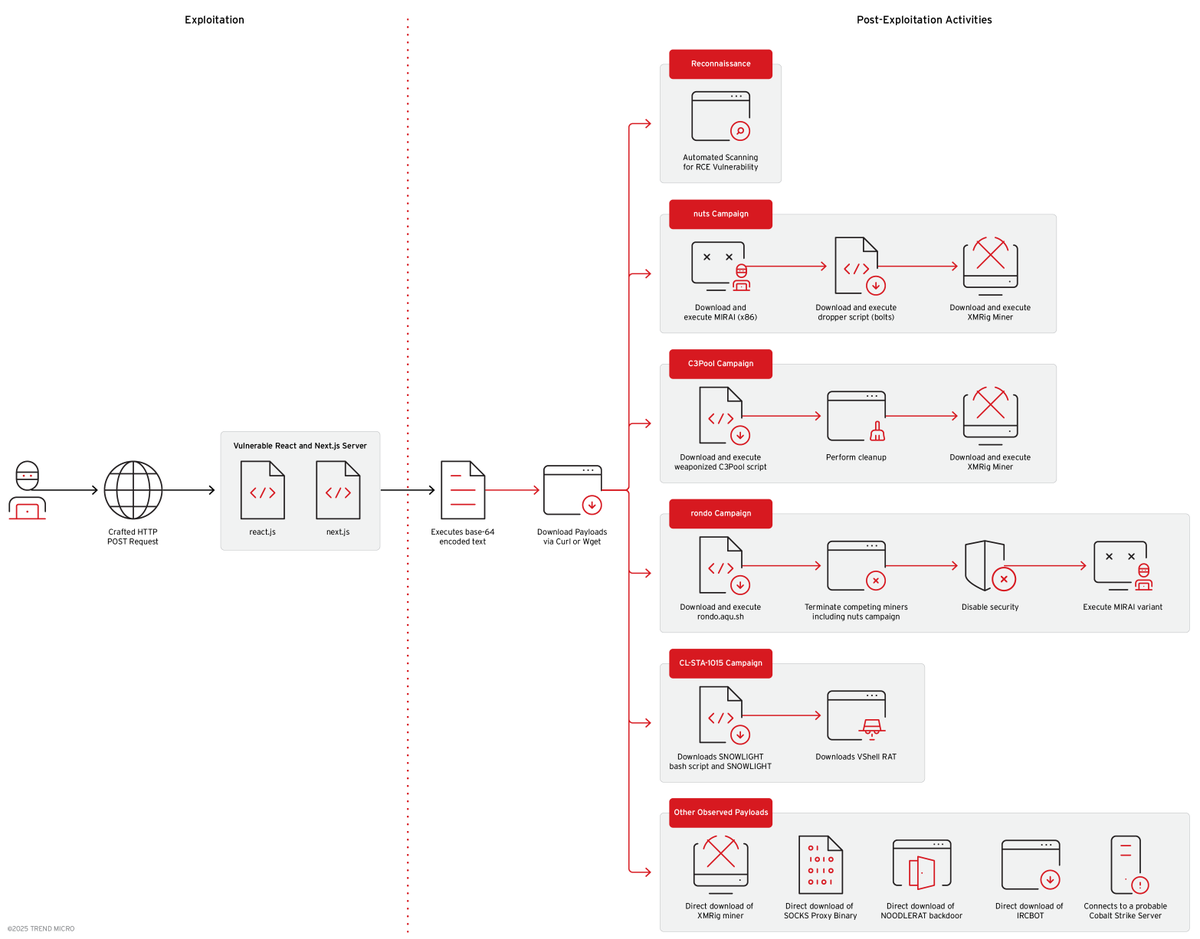
Our @TrendMicro research on CVE-2025-55182 (React2Shell) is live.
This is why we do what we do - protecting our friends, families, and everyone who depends on the web without knowing what's running underneath.
Grateful to my co-authors, co-workers, and everyone across the security industry who mobilized. The speed and energy of the community response reminded me why I love this field.
Looking forward to what 2026 will bring.
https://t.co/Gpw0dVbn1p
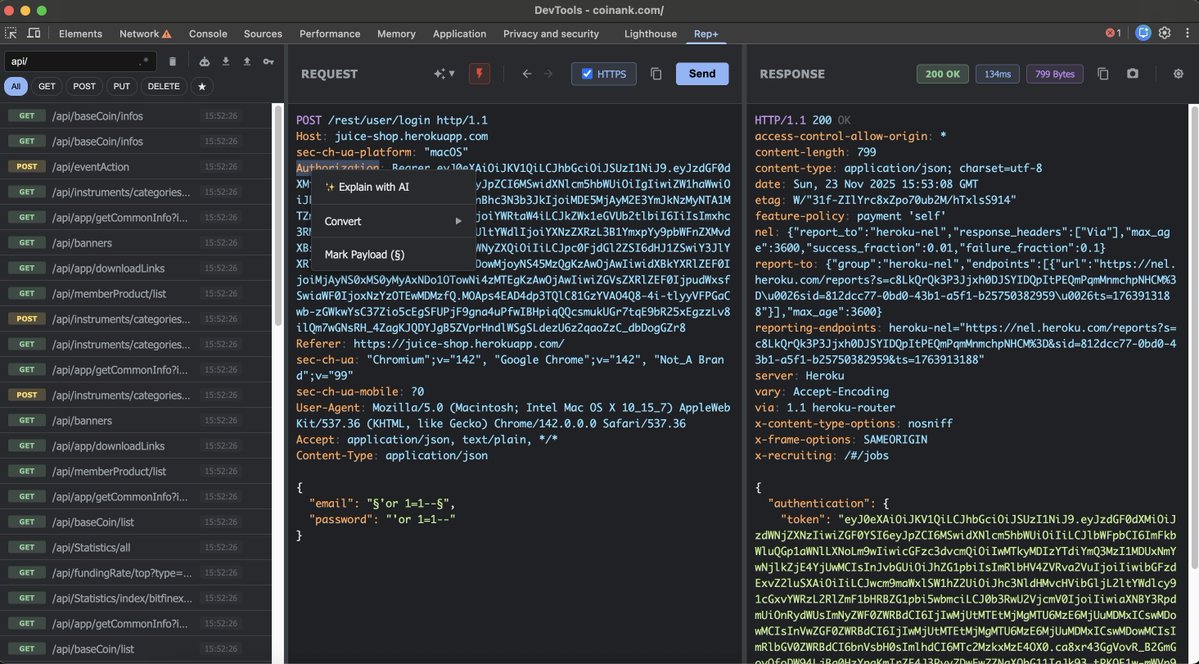
Hey everyone! I’ve been building rep+, a lightweight HTTP Repeater inside Chrome DevTools. No proxy setup or certificates. Just open DevTools and start poking requests. It also has built-in AI for explanations and attack ideas. I’ll share one rep+ feature every day.
Try it 👇
Here's a talk I did for @Jhaddix discord channel back in March '24 about my waymore tool.
I tried to cover EVERYTHING, including useful post processing (that's why it's over 2 hours long 😬).
Hopefully it will be helpful.
🤘
https://t.co/Via9cOZPqN