private keys from 8 intermediate CA certs have been compromised (eMudhra)
Happy "Update everything" day to all my pager-carrying friends
https://t.co/7ASSy72Rxg
As someone who got an N/A yesterday because the company decided that my 0-day wasn’t their responsibility, limiting based on N/As is definitely not the right way.
@Bugcrowd is becoming the anti-platform.
Using N/A to calculate accuracy and limit reports is terrible. Soon, many researchers may not be able to submit reports.
How they use N/A:
• Took 20 days + fixed → N/A
• No time to understand → N/A
• Don’t understand scope → N/A
@pxmme1337 made a card game based on Wikipedia and it's ridiculously addictive. He's looking for feedback so do him a favour and check it out (and do me a favour and use my invite link, I'm addicted to it): https://t.co/DgkB7FYx2b
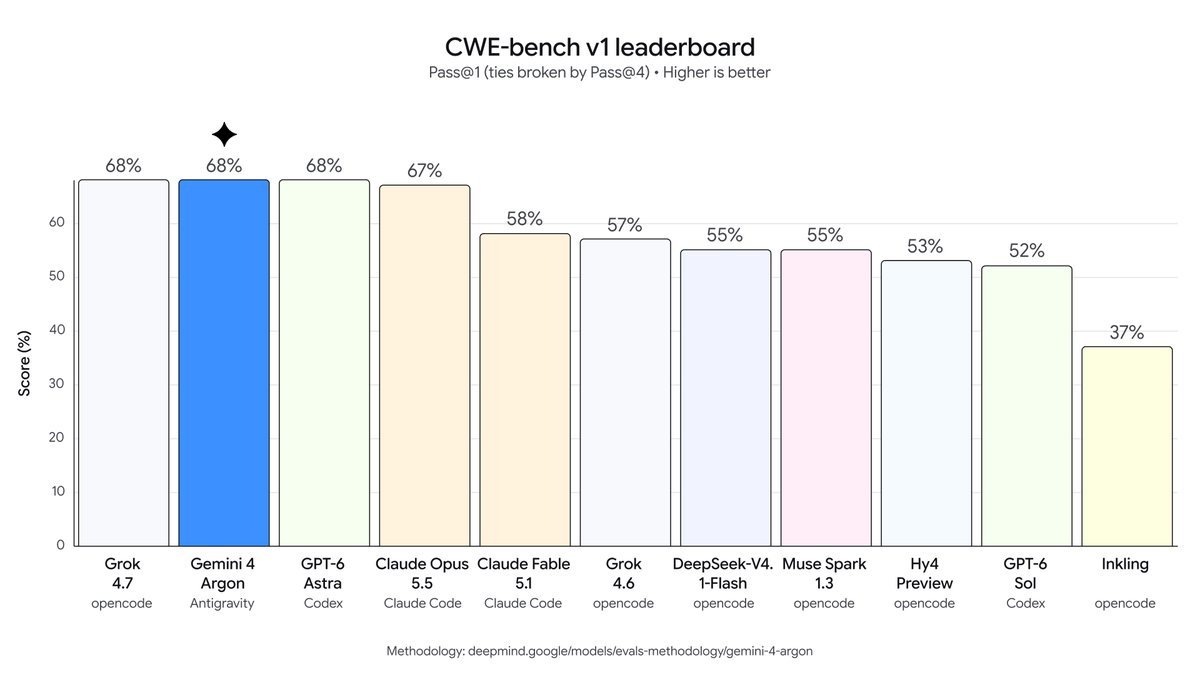
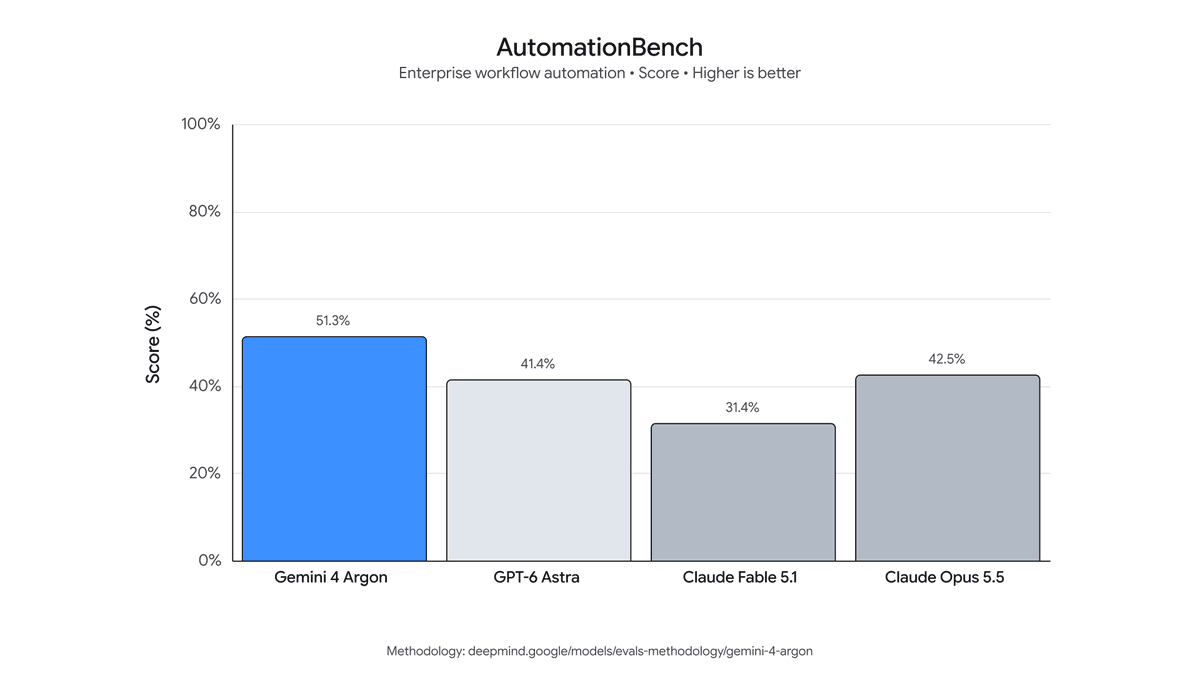
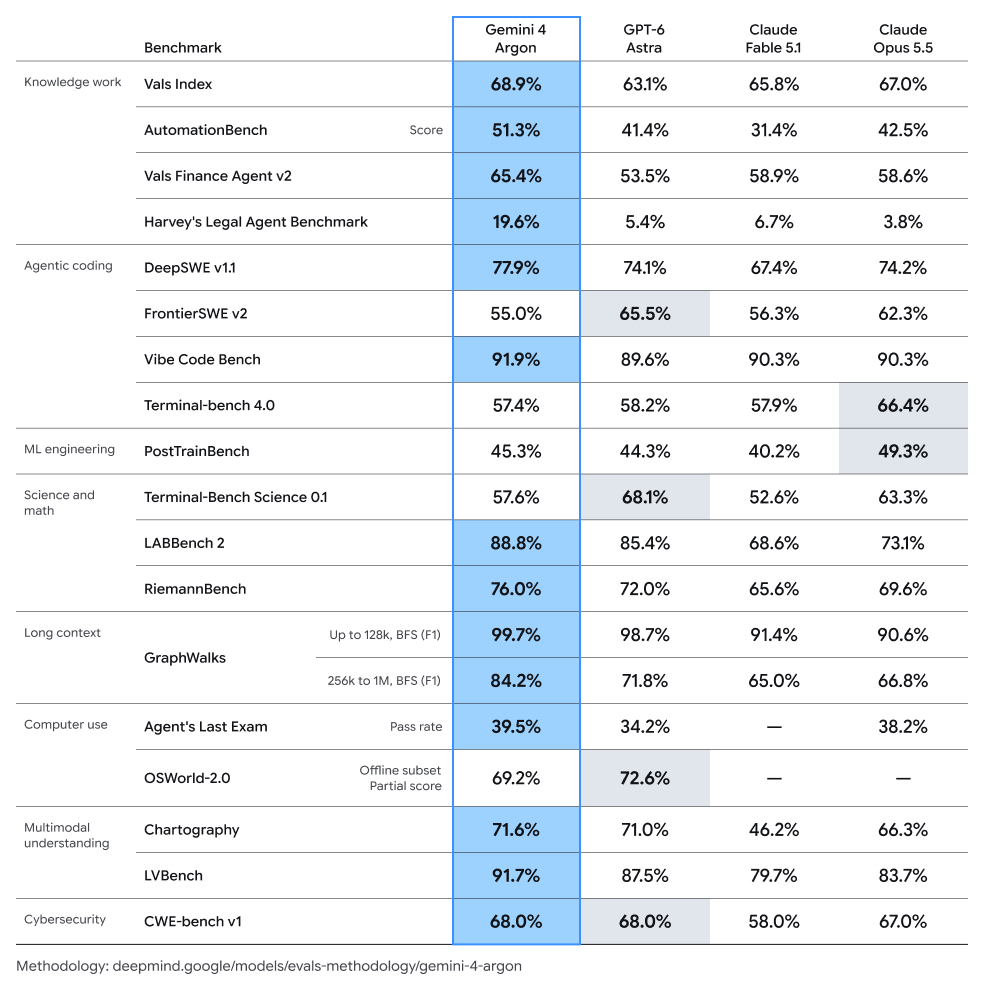
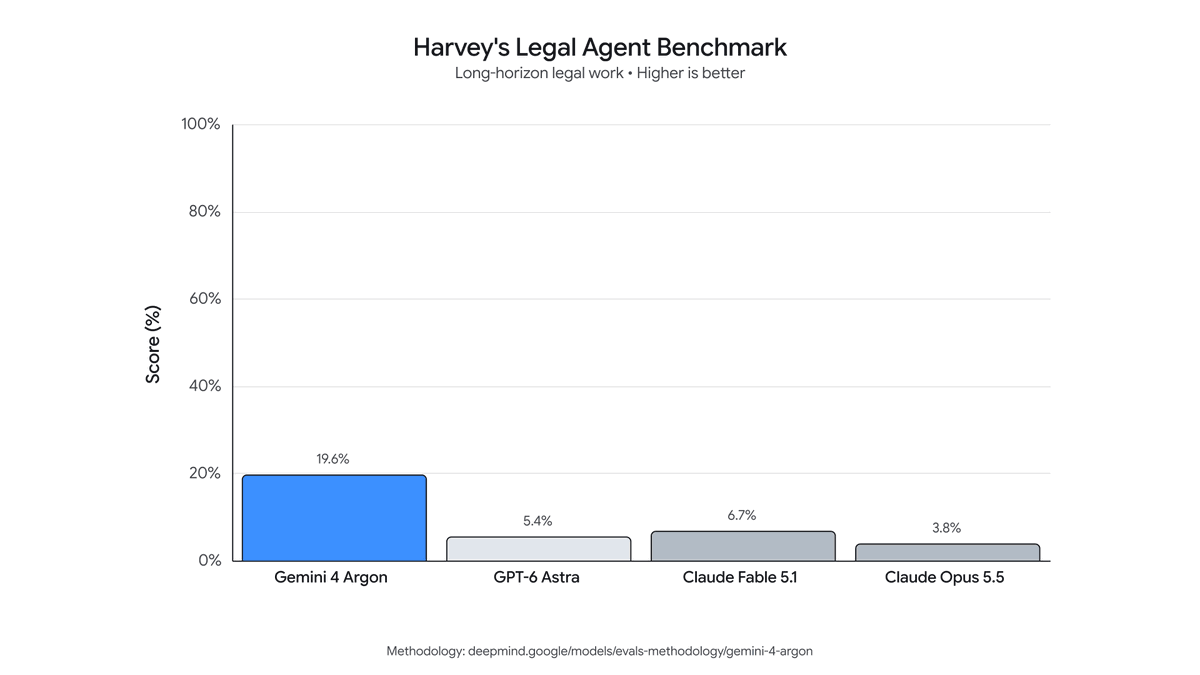
Introducing Gemini 4 Argon, our new frontier model, rolling out to cyber defenders starting today, and more widely as soon as possible. I am really excited by the progress we have made here. Argon is priced at $2 in and $10 out during introductory pricing!
Bug bounty these days is like:
"We regret to inform you that BigStinkyCompany is pausing all submissions until further notice. We're excited to add "https://t.co/mEllrtwFjQ" to our assets after this break, but we're lowering our Medium and Low payouts in line with industry standards"
@S1r1u5_ This type of thinking extends to other fields too, as evidenced by GPT using techniques from other areas of mathematics to solve unsolved problems