Outstanding! Nguyen Hoang Thach (@hi_im_d4rkn3ss) of STARLabs SG used a single integer overflow to exploit #VMware ESXi - a first in #Pwn2Own history. He earns $150,000 and 15 Master of Pwn points. #P2OBerlin
@cq674350529 & @zblee_ from Codesafe Team & TianGong Team, QI-ANXIN Group presenting super cool paper-𝐏𝐚𝐭𝐜𝐡 𝐃𝐢𝐟𝐟𝐢𝐧𝐠, 𝐘𝐨𝐮 𝐀𝐫𝐞 𝐌𝐲 𝐒𝐰𝐨𝐫𝐝! 𝐀 𝐃𝐞𝐞𝐩 𝐃𝐢𝐯𝐞 𝐢𝐧𝐭𝐨 𝐓𝐰𝐨 𝐂𝐫𝐢𝐭𝐢𝐜𝐚𝐥 𝐍-𝐝𝐚𝐲 𝐕𝐮𝐥𝐧𝐞𝐫𝐚𝐛𝐢𝐥𝐢𝐭𝐢𝐞𝐬 𝐢𝐧 𝐅𝐨𝐫𝐭𝐢𝐆𝐚𝐭𝐞!
Our exciting research work, in collaboration with @zhz__6951 , has been accepted by #BHASIA 2025!
See you all in Singapore this April! 🎉
Stay tuned for our talk! #BHASIA
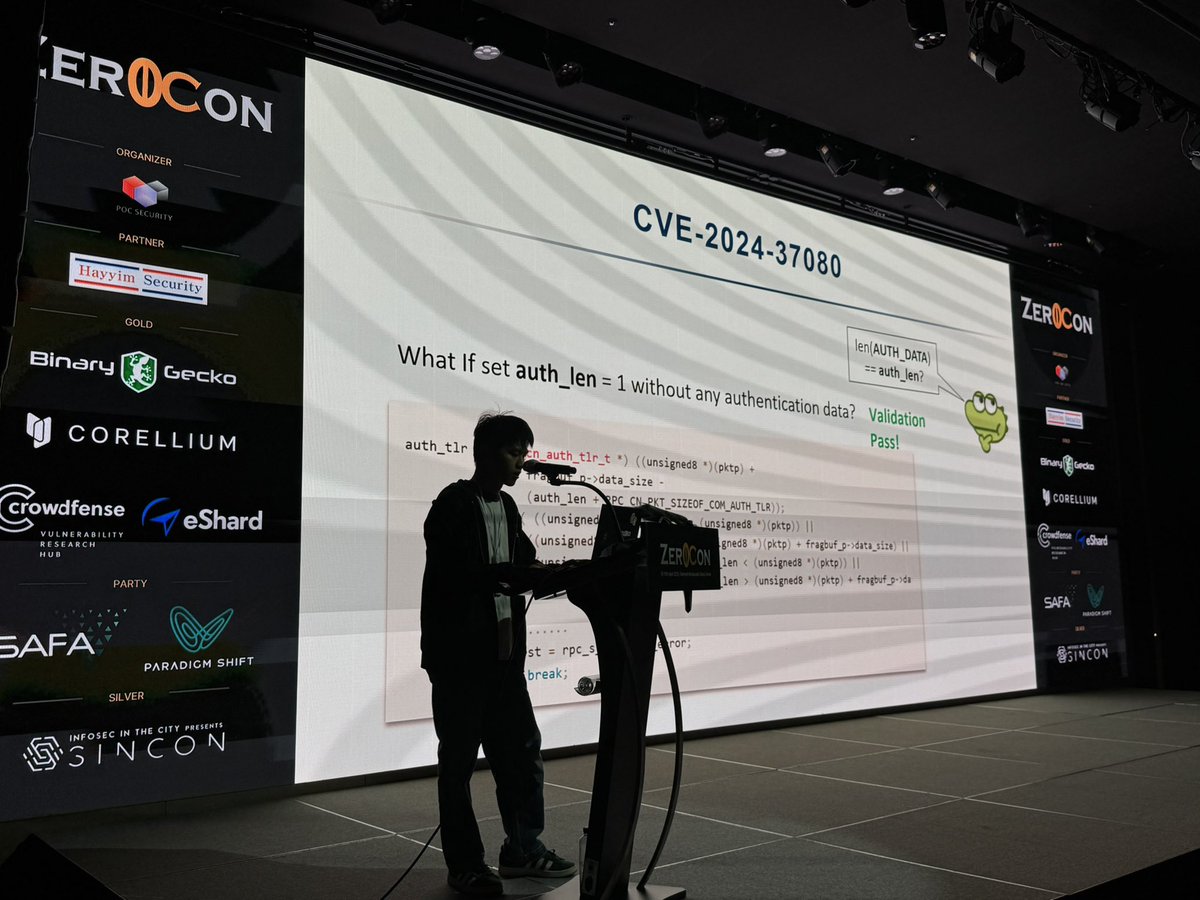
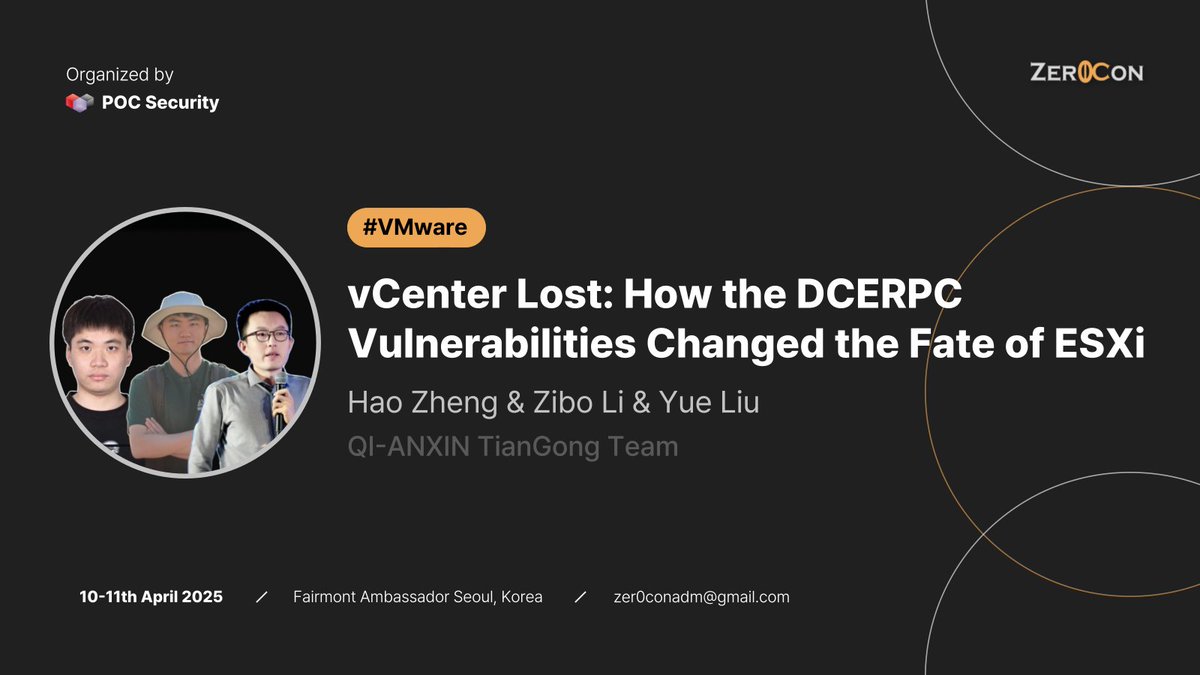
#BHASIA Briefing "Center Lost: How the DCERPC Vulnerabilities Changed the Fate of ESXi" you'll be provided a detailed overview of the DCERPC protocol and the four vulnerabilities we uncovered in its implementation within vCenter Server, which have been assigned CVE numbers CVE-2024-37079, CVE-2024-37080, CVE-2024-38812, and CVE-2024-38813. Register now >> https://t.co/z6RNI1vSjp
When CVE-2024-37079 was patched by VMware, it received quite a bit of attention. In their latest blog, the Trend Micro Research team details the root cause of this vCenter bug and shows how it can be used for RCE. Read all about it at https://t.co/uBGoiEpXMD
Also, our work accepted by #HITB and #DEFCON is such a honour, but I also want to say our team has lots of excellent researchers in different security fields, and we have shared lots of great contents, so be sure to check out our blog site!😀
https://t.co/3Tm8ksGUZe
Exciting news! 🚀 Just dropped my blogpost unveiling the universal Linux kernel LPE PoC for CVE-2024-1086 (working on v5.14 - v6.7) used for pwning Debian, Ubuntu, and KernelCTF Mitigation instances, including novel techniques like Dirty Pagedirectory 🧵
https://t.co/zFimVzjgYB
Congratulations to ZDI researcher Simon Zuckerbraun for winning a Pwnie Award for Most Underhyped Research. You can read his original blog here https://t.co/tpknXMdsWy