🎉 And that's a wrap for #POC2026!
Two days of brilliant research, good conversations, familiar faces, and a fair bit of catching up over drinks. 🍻 Not a bad way to spend a couple of days.
To our speakers, thank you for the incredible work you brought to the stage. To our sponsors, thank you for making it all possible. And to everyone who travelled near and far to join us, thank you for showing up and making POC what it is. 🙌
At the end of the day, POC has never been just about the talks. It's about the people, the ideas, and the community we've built together over the years. ❤️
We're already looking forward to doing it all over again. Same community, new bugs.
See you at #POC2027 ! 🚀
🪟 Our last speaker!
Alexandre Borges (@ale_sp_brazil) - “Eight Degrees of Exploitability: A Field Guide to Data-Only Windows Kernel Exploitation”
#POC2026
🤖 AI meets bug hunting!
Kyeongmin Kim (@hareh4ru) & Insu Yun (@insu_yun) - “1 Man, 1 Month, 45 Bugs: Scaling AI Bug Hunting to $100,000+ in Bounties”
#POC2026
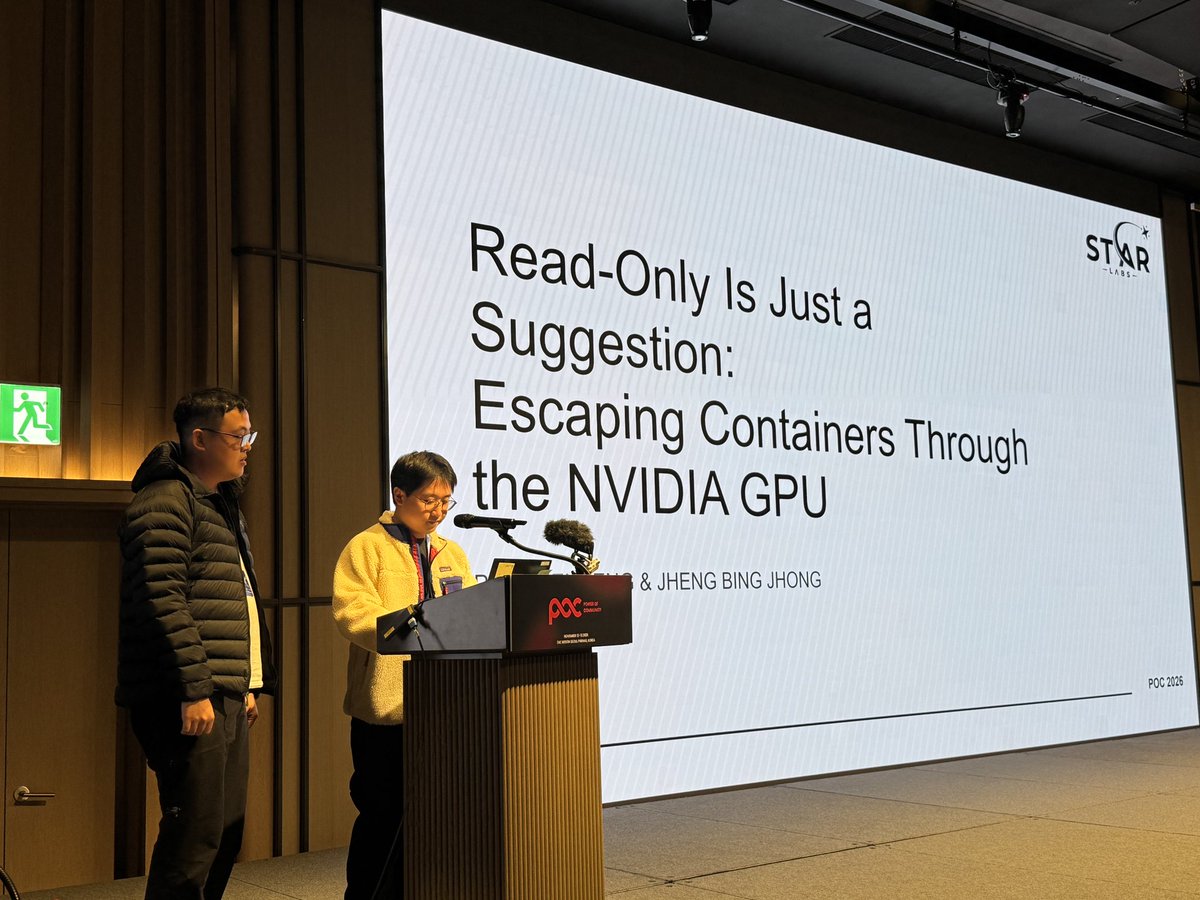
🎮 Let’s talk GPU security!
Pan Zhenpeng (@Peterpan980927) & Bingjhong Jheng (@st424204) - “Read-Only Is Just a Suggestion: Escaping Containers Through the NVIDIA GPU”
#POC2026
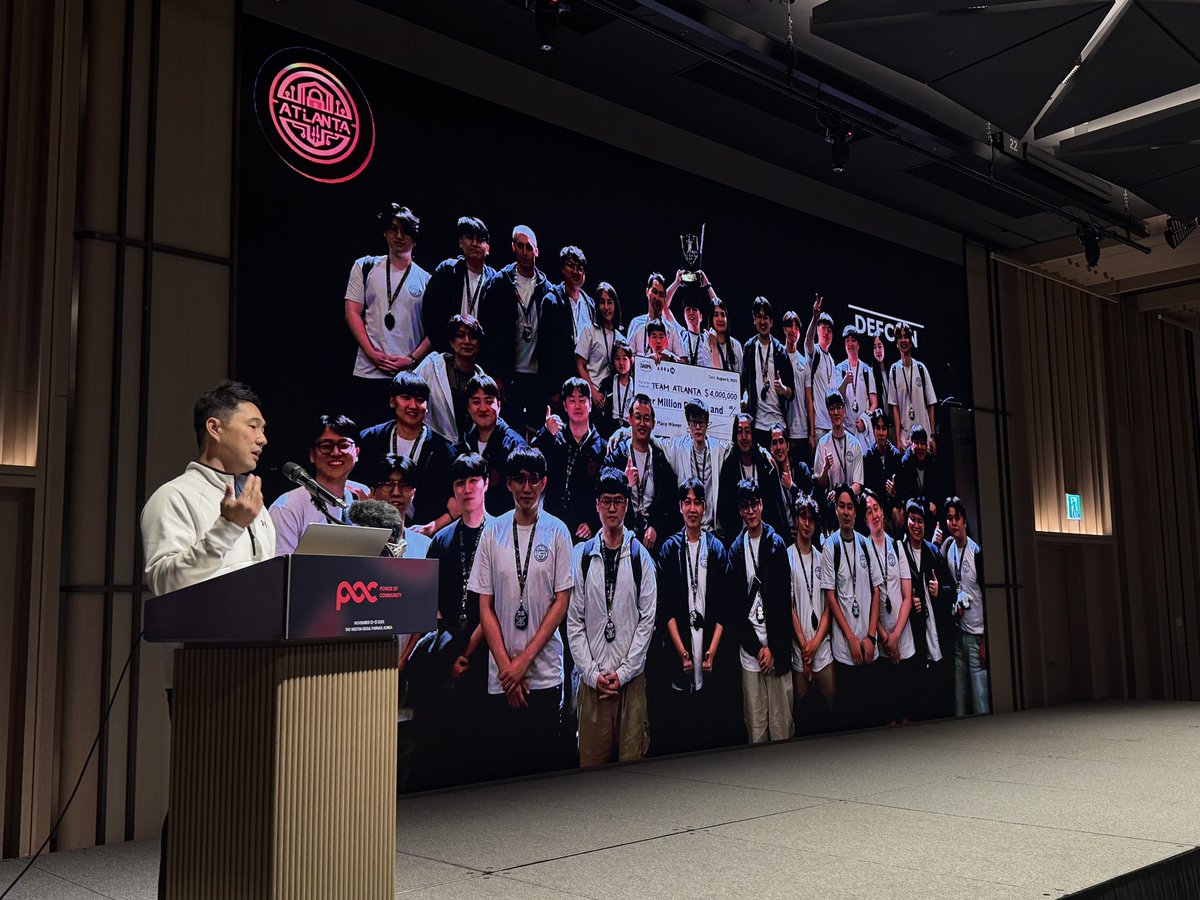
🎙️ Time for our panel discussion!
Panel Discussion: “Hacking in the Age of AI”
Speakers: Taesoo Kim, Youngjoo Lee(@ashuu_lee), Yechan Bae(@yechan_bae), Eunsoo Kim, Junghoon Lee
#POC2026
🔐 Let’s talk Windows security!
Bocheng Xiang (@crispr_x) & Hao Huang (@h4urek) - “TrustFall: When Windows Trusted Installer Betrays Its Trust”
#POC2026
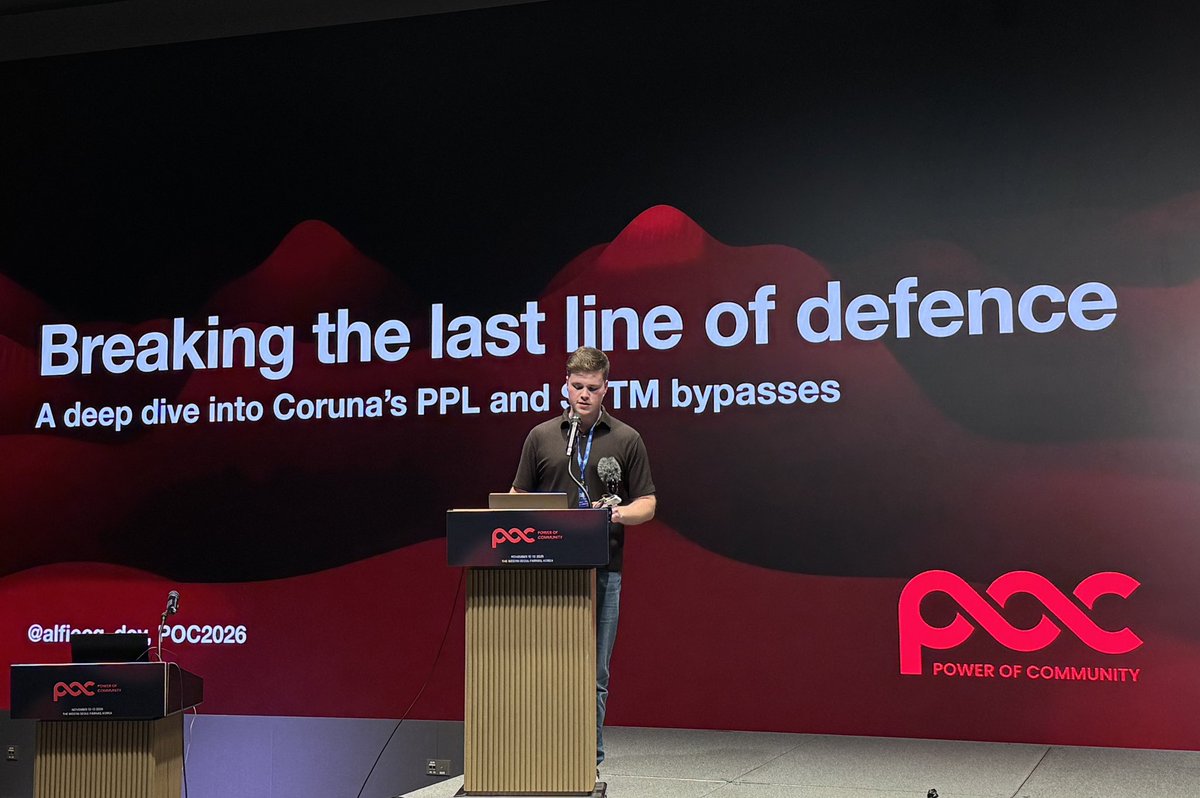
🛡️ Time for some iOS security!
Alfie CG (@alfiecg_dev) - “How a Nation State Broke the Last Line of Defence: Inside Coruna’s PPL & SPTM bypasses”
#POC2026
🕸️ Let’s talk WebKit!
Kuan-Ting Chen (@h3xr4bb1t) & Ting-Yu Chen (@terrynini38514) - “Obvious Was Only the Beginning: A WebKit Exploit Chain for Pwn2Own”
#POC2026
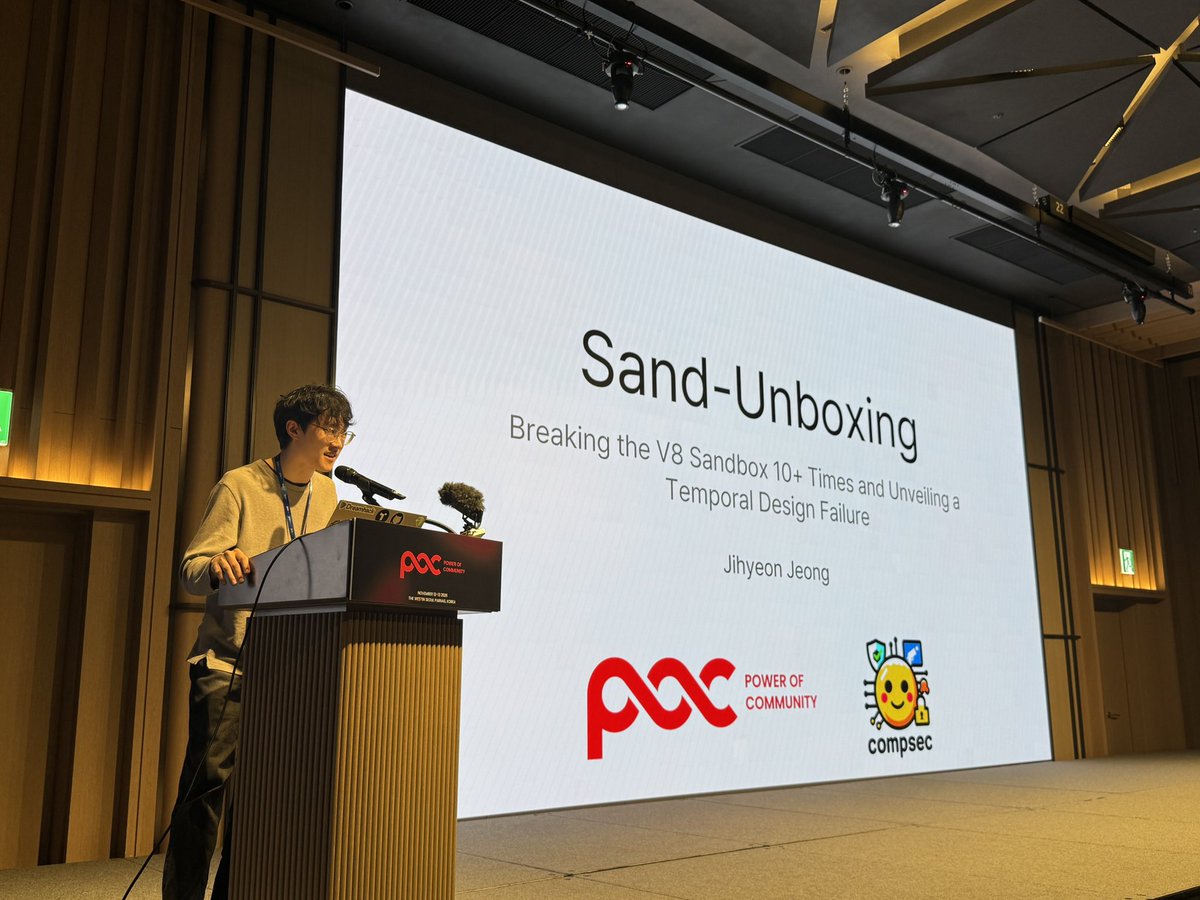
🏖️ Kick off with our first speaker!
Jihyeon Jeong (@symsool9143) - “Sand-Unboxing: Breaking the V8 Sandbox 10+ Times and Unveiling a Temporal Design Failure”
#POC2026