Been digging deep into the Windows Endpoint Security Platform (WESP) in Win11 25H2, definitely one of the most fascinating security features Microsoft has built in a while.
The concept is neat: compile rules to decision graphs in user mode, hand them to wesp.sys, and let the kernel evaluate them in-path while telemetry streams asynchronously in the background.
I did an AI-assisted reverse engineering dive into the whole stack (wesp.sys, espclient.dll, and wesp_elam.sys), documented the wire protocols, disposition tables, and the enforcement gate, and built esptool, a research harness with 118 XML rule docs so anyone can test live telemetry and in-kernel blocking.
Repo: https://t.co/ZPYPHfmCP4
Tech doc: https://t.co/P2s4geHEsI
Thanks to @yarden_shafir for putting this on my radar
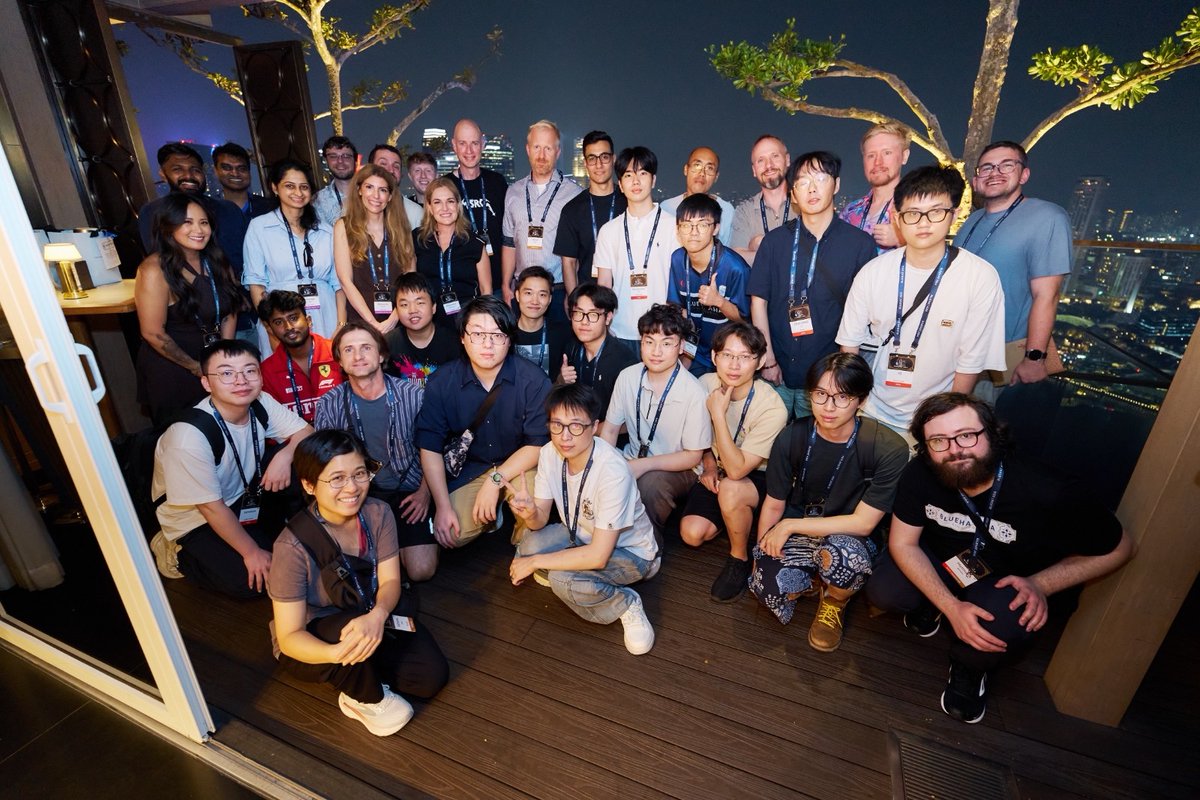
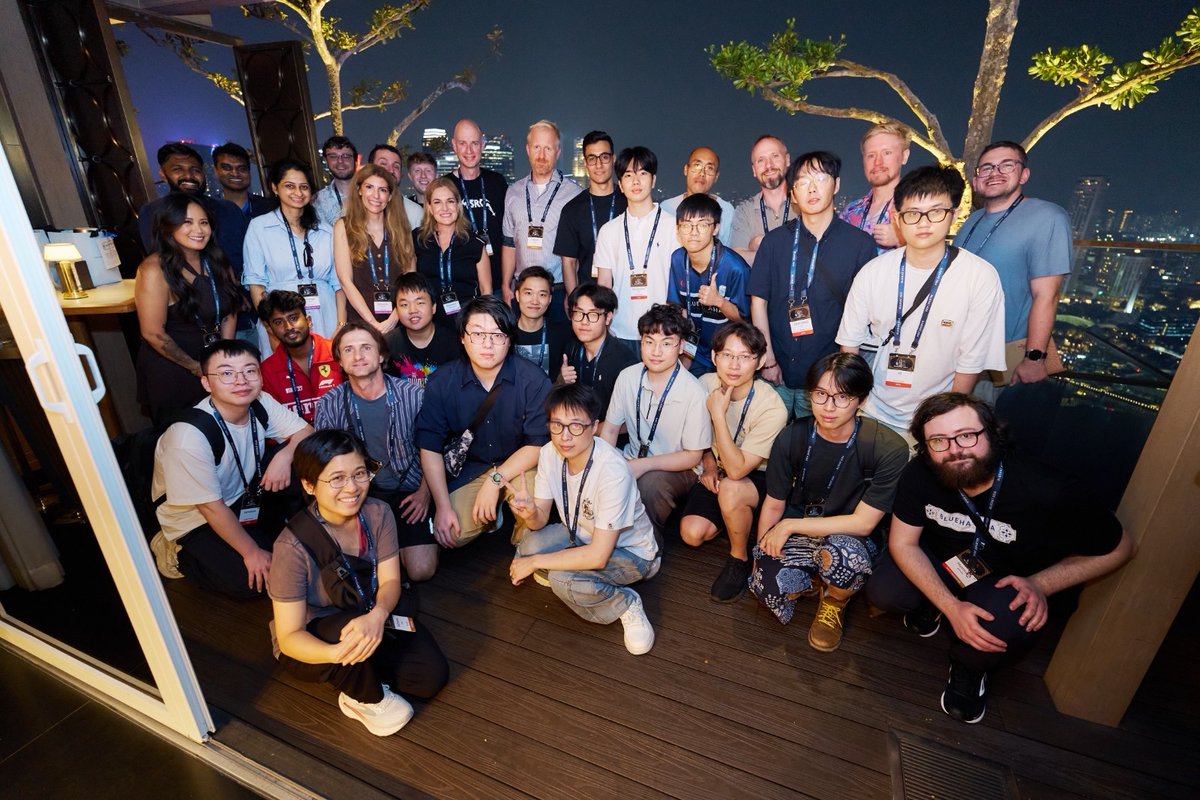
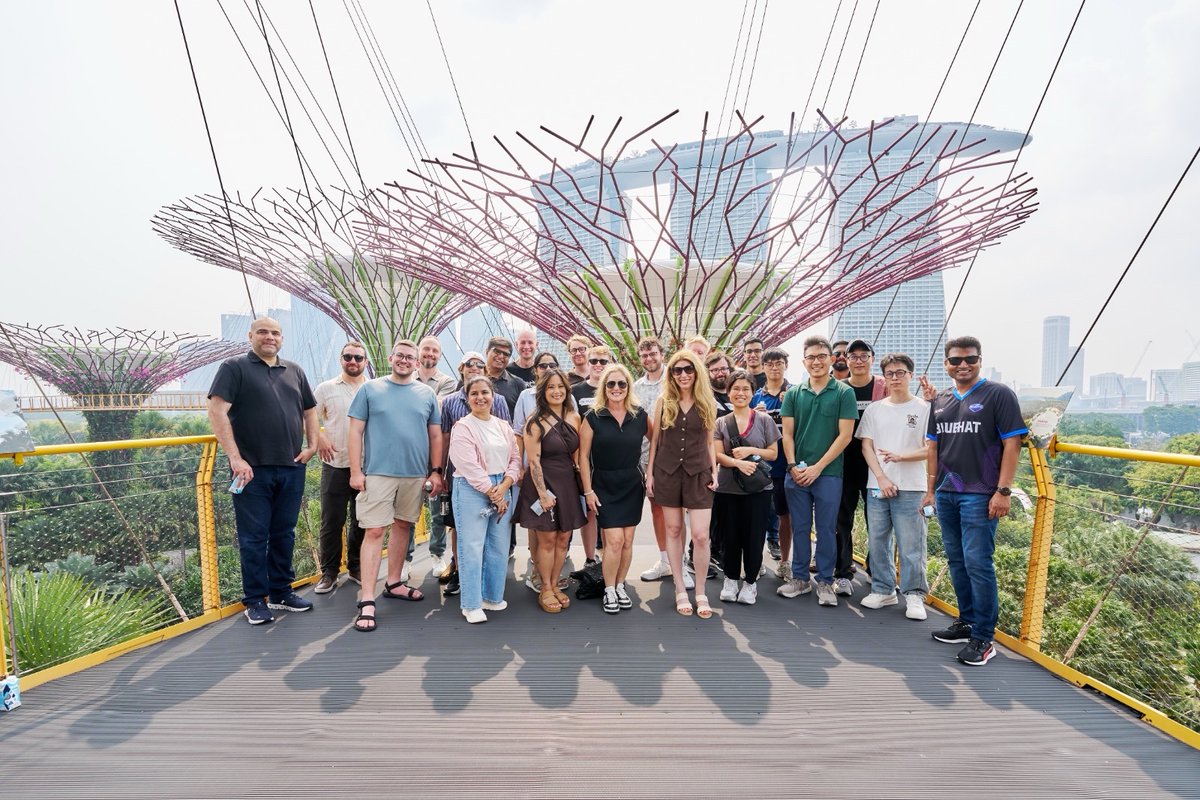
As BlueHat Asia kicks off, we had the opportunity to spend an evening with some of the people who make this community so special.
We started with a private tour of Singapore's iconic Gardens by the Bay before gathering at Marina Bay Sands, where BlueHat Asia presenters and Microsoft Most Valuable Researchers (MVRs) came together for an evening of conversation, connection, and collaboration.
A heartfelt thank you to our presenters and MVRs for sharing their expertise, insights, curiosity, and passion for advancing security. BlueHat is made possible by the incredible people who come together to learn from one another.
We're grateful for the presenters and MVRs who joined us in Singapore and look forward to the conversations, discoveries, and connections ahead.
Broadcom has released security updates for two security flaws impacting VMware Workstation and Fusion, including one critical bug that could result in arbitrary code execution under certain conditions.
The vulnerability, tracked as CVE-2026-59346 (CVSS score: 9.3), is an integer-overflow vulnerability that a local attacker with elevated privileges can exploit to run arbitrary code.
"A malicious actor with local administrative privileges on a virtual machine with VMXNET3 virtual network adapter may exploit this issue to execute code on the host," Broadcom said in an alert.
The tech giant credited @h4urek, @cameudis, and Stan S for discovering the issue.
Also patched by Broadcom is a stack-based buffer-overflow vulnerability in HGFS (CVE-2026-59347, CVSS score: 8.1), which can be exploited by a bad actor with local administrative privileges on a virtual machine to execute code as the virtual machine's VMX process running on the host.
Yeonghyeon Choi and Tianchu Chen of Tencent Xuanwu Lab have been acknowledged for reporting the flaw.
RedNova: From Arbitrary File Write to Command Execution Using COM in Windows
Months ago, I wrote a post (https://t.co/IwwfTJcGyX) about the unique method used in the RedSun exploit to turn a file write into command execution by using a COM object that can be triggered by a low-privileged user and runs as SYSTEM.
In that post, I mentioned that there are other COM objects that can be used in the same way.
I presented one object called CoFilterPipeline and noted that it needs some tricks before it can be weaponized.
Now I've written a full blog post on how you can find such objects and how you can weaponize them in exploits like RedSun.
The video below shows another COM object with the same behavior (windows 11). It's called PerceptionSimulationCoClass.
A low-privileged user can activate it, and it runs as SYSTEM. The video doesn't contain any exploit (it just replaces the COM server as administrator).
The goal is only to demonstrate how a file write can be turned into command execution as SYSTEM while being triggered by a low-privileged user.
https://t.co/Uz2whcSdYQ
Today, we're proud to recognize the Top 100 Microsoft 2026 Most Valuable Researchers (MVRs).
Security researchers play a critical role in helping protect customers by identifying and reporting vulnerabilities across Microsoft products and services. We're grateful for their partnership and the impact they have made over the past year.
Congratulations to this year's Top 10 MVRs:
🥇C46F3708A45EF0041BD0A49DDAEA0E25
🥈ShinHyuiq & Alan Pang
🥉cherrypick
4. Brad Schlintz (@nmdhkr)
5. wtm (@wtm_offensi)
6. Asaf Cohen (https://t.co/8WLhdz05Oq)
7. bccc95a61a3cc79d7b2c4423c808f744
8. Felix B.
9. 142a423e2574abf10d65eba46891ca5e
9. Anonymous
This year, we updated the MVR leaderboard to rank researchers based on total bounty awards, creating a clearer connection between recognition and security impact. We also introduced Special Mentions to recognize researchers who submitted valid vulnerability reports during the recognition period, regardless of leaderboard ranking.
See our blog for the complete list of the Top 100 MSRC 2026 Most Valuable Researchers and the top researchers by bounty program: https://t.co/tkDVvFbFEr
Thank you to every researcher who partnered with us this year to help protect customers worldwide.
So here is new local privilege escalation zero-day I discovered, not patched yet too :).
In simple terms, if you have a service like RDP that exposes an RPC server, there many system services running as SYSTEM connect to it as RPC clients. If that service is turned off (RDP is off by default), it seems that any other process in Windows can expose the same RPC server using the same endpoint.
Now all the RPC calls from that SYSTEM processes will come to this fake server and If the process that deployed the server has SeImpersonatePrivilege, it can escalate to SYSTEM by impersonate the RPC client.
In the white paper below, I describe five exploit paths you can abuse.
However it's architecture problem and maybe there are more. It's Not A Potato
https://t.co/DOfRFgYqI9
Here’s an IDA plugin for transforming data with CyberChef, directly within IDA. 400+ operations that you can chain, and then patch or comment right back into the IDB
https://t.co/A7XpwaGHZC
https://t.co/OMivVgB0oW
4/The full post covers the prompting spectrum (7 levels), agent frameworks, MCP's plateau, RAG in 2026, computer use, and why safety isn't a separate workstream.
Companion to my 60-min talk. Slides on GitHub.
https://t.co/r7wnTmTPt4
When you try to harden Windows PrintNotify callbacks, you end up exposing vulnerabilities in other protocols like EPMAP that have been sitting around (or even more) for 20 years
https://t.co/QXM8ONUrzR
If you missed HEXACON 2025 or want to rewatch some of the talks, they’re now available on our YouTube channel 📽️
Enjoy the content, and see you in 2026!
https://t.co/KHHVAGY48M
RPC 7 is live. In this part, I talk about the internal tools you can use for RPC research. I mention RPCView, which lets you extract RPC interfaces with a GUI, NtObjectManager, which helps you build internal fuzzers, and a logging tool called RPCMon.
https://t.co/gWzlas5Y8T
RPC Part 6 is live. I cover the toolset for external RPC research, demonstrate how to enumerate network interfaces without authentication using rpcmap, and show how to call custom RPC functions with Impacket to help develop an external fuzzer.
https://t.co/CrTKM6vrD9
I also found this vulnerability a few weeks ago, but it was already fixed in the Canary version at that time, need to be quick next time.🧐https://t.co/ilvlP70Ttz
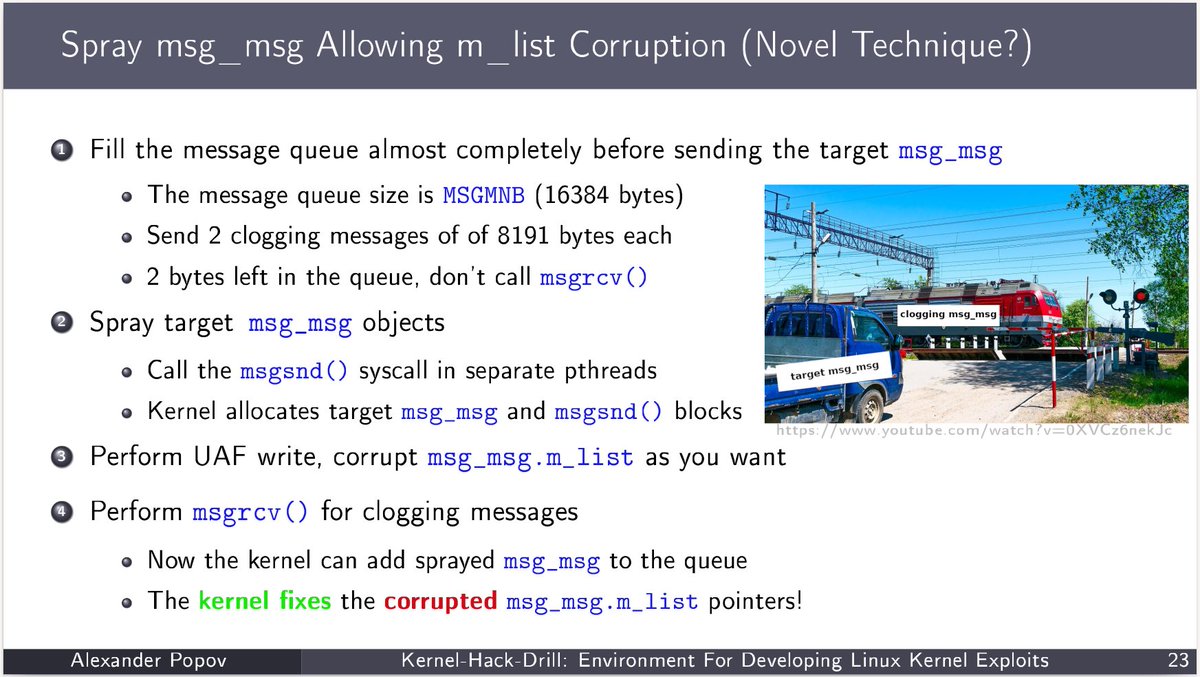
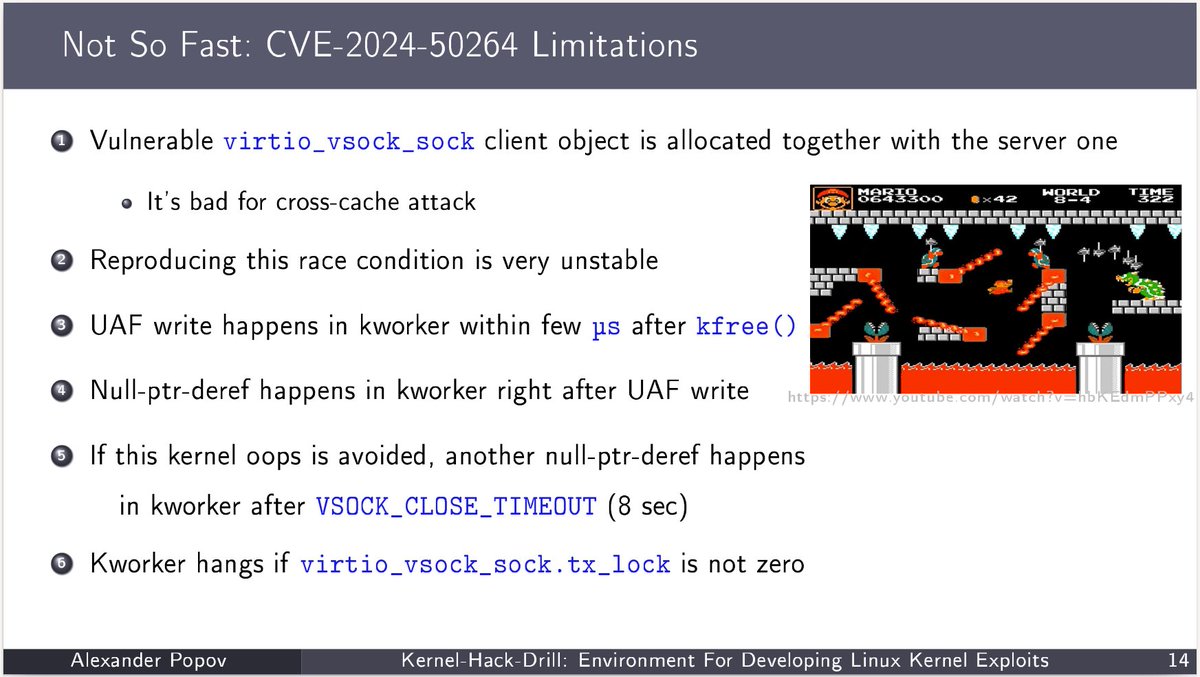
Slides of my talk at #Zer0Con2025!
⚡️ Kernel-Hack-Drill: Environment For Developing Linux Kernel Exploits ⚡️
I presented the kernel-hack-drill open-source project and showed how it helped me to exploit CVE-2024-50264 in the Linux kernel.
Enjoy!
https://t.co/84DqT4rdvm