Thank you @reconmtl for this wonderful conference, what a way to discover Canada!
Following up my talk, here are the slides & tool from the demo: https://t.co/tgoGa4wwJV
Blogpost on @CrowdStrike's blog coming up soon!
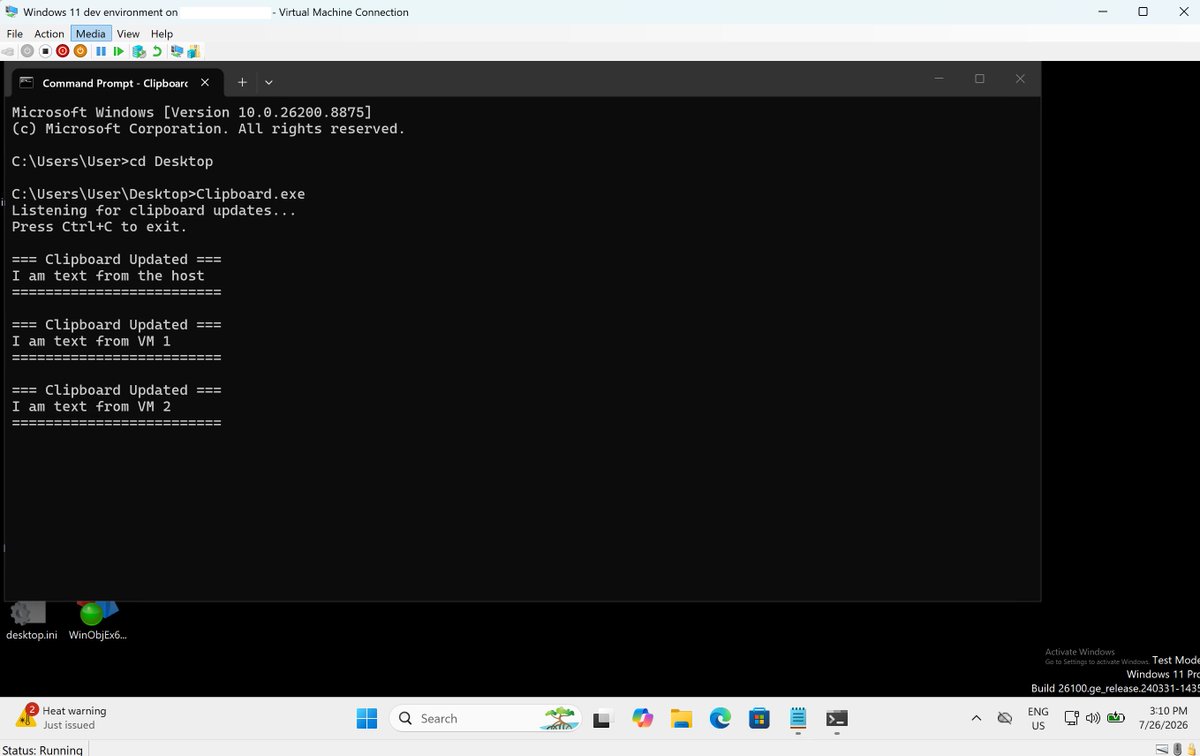
Very quick blog post to start the week: "enhanced session" shares your host clipboard with virtual machines, even if you didn't copy/paste anything from the VM itself.
Might be common knowledge but it surprised me so I'm sharing it here
https://t.co/DkCqYczoiS
I was presenting this morning at @reconmtl my RE journey of the ClickOnce technology.. that led to discover a new abuse on it!
If you've missed it, or are interested to learn about this little known feature, the research is also available on @CrowdStrike's blogspot below ☀️
Excited to return to @reconmtl in less than a month!
This time, we’ll be peeling back the layers of the ClickOnce technology and exploring a few things that probably weren’t meant to be seen 👀
Détails & schedule to come: https://t.co/jOgIQYMD5s
I often am asked for pointers on building a VM for malware analysis. I wrote a 40+ page chapter on this in my book Evasive Malware. You can download this chapter from the book on my blog for free here:
https://t.co/6yK5UGyQpb
Thanks @nostarch for allowing me to give it away 🤓
Looks like @BlueHatIL talks are online now, so here’s my talk for anyone who wanted to learn about the latest episode of KASLR and couldn’t make it: https://t.co/3uDeeRNHOs
FYI if you’re willing to link with ntdll or dynamically resolve it there’s a ton of APIs that return TEB/PEB or leave them in one of the registers.
(Don’t believe official return values. MSDN is a liar!)
WinDbg doesn’t have to win the battle!🧠💥
Join @MathildeVenault at SINCON 2025 for a hands-on reverse engineering workshop that helps you make sense of the Windows debugger.
📅22-23 May 2025 | 📍voco Orchard, SG
🎟️Pass: https://t.co/QBYmHpP8Xw
#SINCON2025#WindowsDebugging
Really excited to give a talk at SINCON this year!
I'll be presenting my tool https://t.co/deS2iEJwpw, that helps making the most of WinDbg in a minimum amount of time
Join @MathildeVenault at SINCON 2025 to discover how DrawMeATree helps reverse engineers visualise & decode complex systems faster.
📅22-23 May 2025 | 📍voco Orchard, SG
🎟️Pass: https://t.co/QBYmHpOB7Y
#SINCON2025
Save the date - @Blackhoodie_RE is partnering with
@offensive_con this year to bring a BlackHoodie training to Berlin! Students will learn how to place compiler backdoors in innocent code. Mark your calendars for May 15th! Registration opens tomorrow, space is very limited ☺️
I’m not saying you definitely have to go to @BlueHatIL this year, I’m just letting you know it’s free, by the beach and I’ll be there dropping kernel pointers to anyone who asks nicely
#CVE-2025-21419 2025-Feb Windows Setup Files Cleanup Windows Setup Files Cleanup Elevation of Privilege
#ghidriff uncovering arbitrary delete vulnerabilities 👀 🔍
Patch introduced new function DeleteFileEx_MSRC. Not your typical function name... 🧐
A patch diffing 🧵...