@victor_ruiz Ojo con el tamaño: 189 KB en SQL y CSV son a lo mucho unos miles de renglones. Con usuarios del sistema, host y versiones, suena a la base del sitio web del municipio, no a sus archivos. La lista de «incluye» es vitrina del vendedor. Si es real, lo serio: MD5 y datos de menores.
@ivillasenor Coincido. Una base de ~11 millones de residentes de CDMX y zona metropolitana, con datos del padrón del INE, ya circulaba gratis en Telegram en abril de 2024, y se liga a una fuga de alrededor de 2015. Revenderla como «leak» nuevo es show. El riesgo de suplantación sí sigue.
@DailyDarkWeb A JSON schema isn't proof. It's field names anyone can type. No real sample, no confirmation from the institute, no independent check, and still the headline says 500K "EXPOSED". That's the seller's sales pitch with your logo on it. Call it what it is: a claim.
🇲🇽 🚨 MEXICO: 11.4 MILLION MEXICO CITY RESIDENT RECORDS WITH CURP IDS ALLEGEDLY LEAKED
A threat actor on a dark web forum has published a database they claim holds 11.4 million records of Mexico City residents, including CURP national identity numbers.
What was allegedly shared:
* About 1.36 GB of structured records
* Full names and CURP (Mexico's national population registry ID)
* Dates of birth and gender
* Employment status and residential addresses
⚠️ Analyst Note:
The original source of the data has not been identified, and no Mexico City authority has confirmed an incident that we are aware of. Mexican citizen datasets are often recompiled from older leaks, so this may include recirculated data. If genuine, CURP plus address data at this scale raises the risk of identity fraud and targeted phishing. Unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #DataBreach #Mexico #CDMX #ThreatIntelligence
🌎 🚨 THE GENTLEMEN RANSOMWARE LISTS SAP LATIN AMERICA
The Gentlemen ransomware group has added SAP to its leak site, describing the victim as SAP Latin America and Caribbean, the regional arm of the German enterprise software giant that runs operations across about 10 countries, with Brazil as its largest market.
The listing appeared on Oct 26, 2026 (UTC). The group has not shared details on the volume or type of data allegedly taken. It comes two days after a separate, unrelated actor claimed a 31 GB leak tied to SAP's Ecuador operations.
The claim has not been independently verified, and SAP has not publicly confirmed a cyber incident.
⚠️ Analyst Note:
A regional SAP unit holds customer contracts, project files and partner data for thousands of large enterprises. If the claim holds, SAP customers and integrators in the region should watch for SAP-themed phishing and fake invoice or support requests. Unverified threat-actor claim, NOT confirmation of a breach.
#DDW #DarkWeb #TheGentlemen #Ransomware #SAP #LatinAmerica #Brazil #ThreatIntelligence #CyberSecurity
El grupo The Gentlemen ha publicado en su blog a #SAP Latin America and Caribbean (@SAP) como posible víctima de un #ciberataque#ransomware.
SAP ofrece #software empresarial, aplicaciones en la nube, herramientas de gestión de datos y servicios de consultoría a organizaciones en toda Latinoamérica y el Caribe.
Monitorea este incidente en VenariX https://t.co/KlCG04jcBm
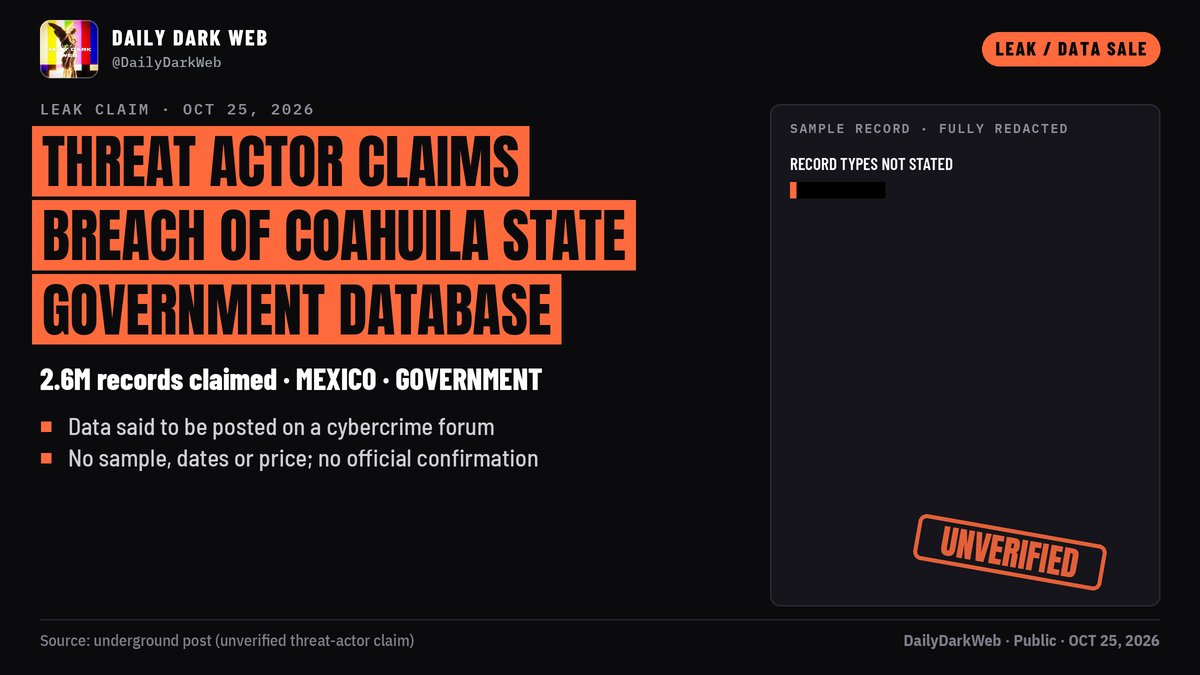
🇲🇽 🚨 THREAT ACTOR CLAIMS BREACH OF COAHUILA STATE GOVERNMENT DATABASE, 2.6M RECORDS (UNVERIFIED)
A threat actor calling itself MortemTeam claims it breached a database belonging to the government of Coahuila, the Mexican state on the US border.
The actor claims:
* About 2.6 million records taken from a Coahuila state government (https://t.co/KXKfE8oVWk) database
* The data has been posted on a cybercrime forum
The claim was made on October 25, 2026. No sample fields, data dates or price were given, and it has not been independently verified. The Coahuila state government has not publicly confirmed an incident.
⚠️ Analyst Note:
Mexican government databases are a frequent target of leak claims, and record counts are often inflated or recycled from older dumps. If genuine, records like these could fuel identity fraud and phishing that impersonates state agencies. Residents should be wary of unexpected messages that claim to come from the state government. We assess this as an unverified threat-actor claim.
#DDW #DarkWeb #DataBreach #Mexico #Coahuila #Government #MortemTeam #ThreatIntelligence