I shared my research at HITCON titled "Shuttling Through Secret Pipes: Unveiling Vulnerabilities in Leading VPNs." I open-sourced NamedPipeMaster, the tool I used to identify the vulnerabilities.
See demo: https://t.co/2OEgJdCs3O
https://t.co/VqjF40geYV
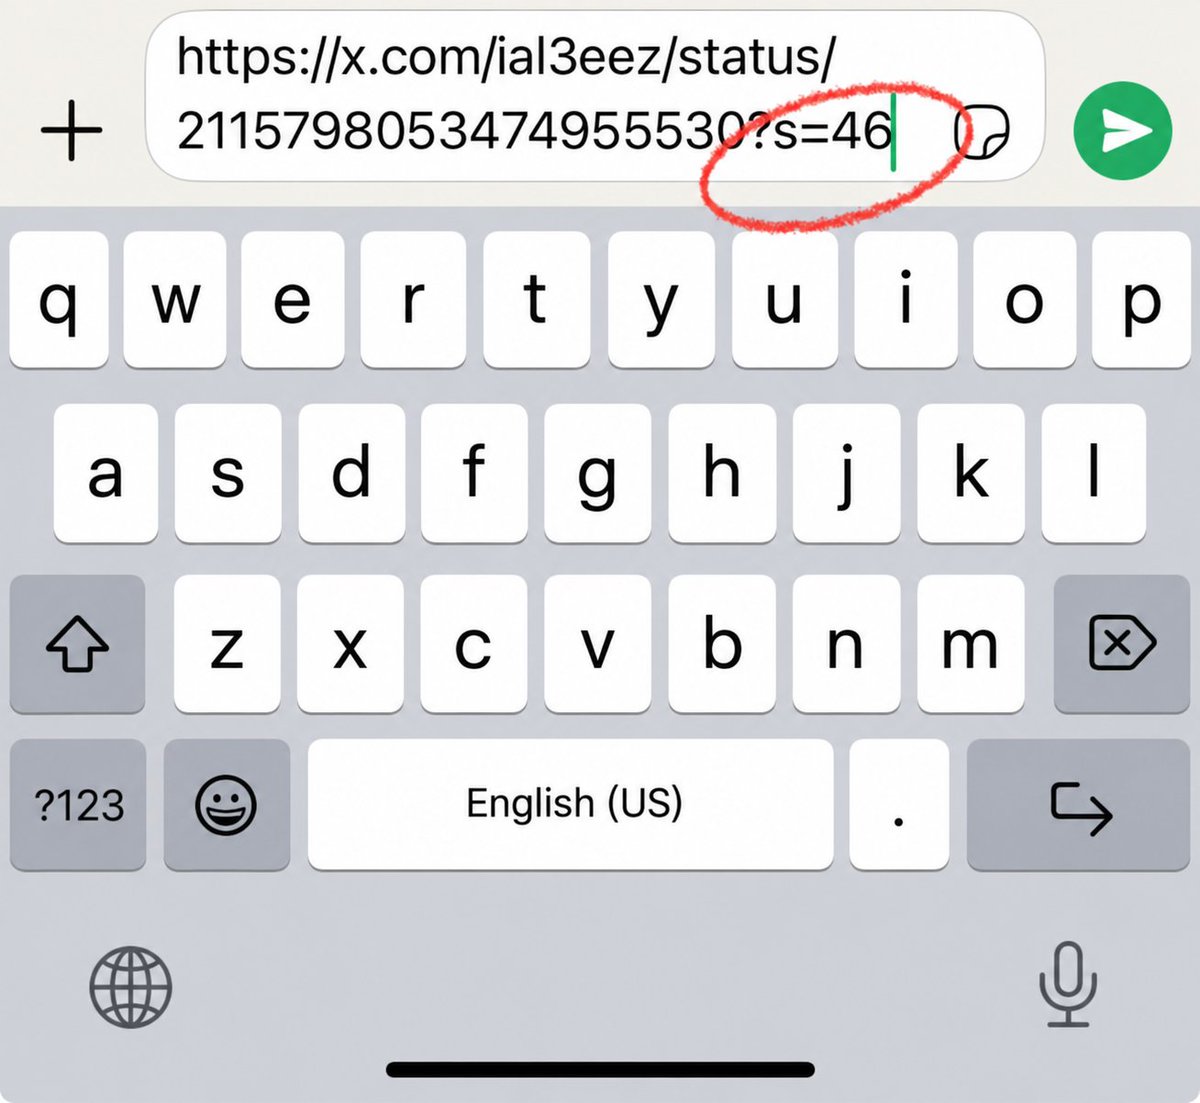
Did you know Twitter links can reveal which device was used to share them?
Check the URL ending:
s=46 → iPhone
s=20 → Web Browser
s=19 → Android
Try it yourself by copying a tweet link.
Technology is interesting, isn't it?
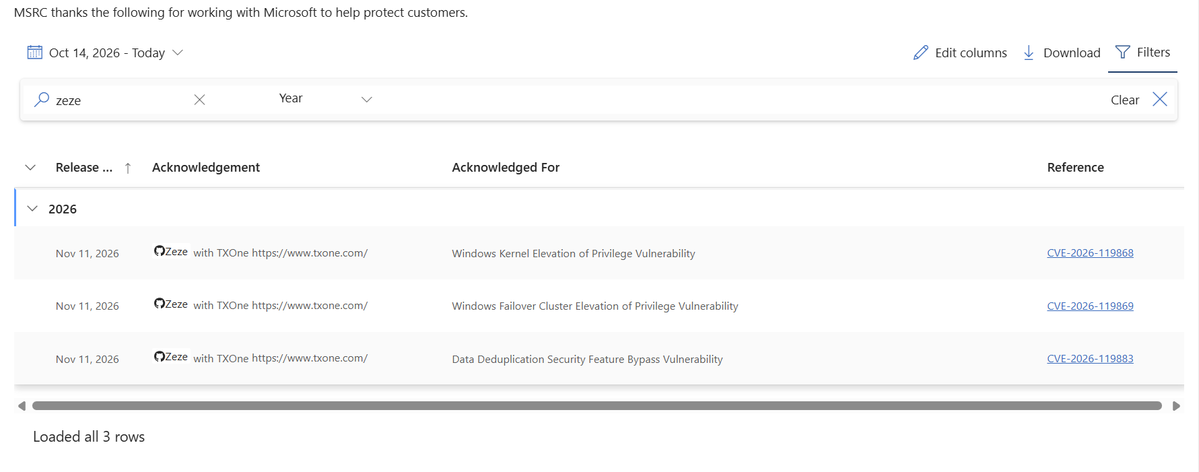
My 2 Process Monitor bugs CVE-2026-100205 and CVE-2026-105729 were fixed in October Patch Tuesday. Procmon is my favorite tool.
CVE-2026-96318 was aslo fixed, and it's my first time duplicate to Yuki Chen.
https://t.co/LCTYx0jt4W
https://t.co/mT5dJPBVtV
https://t.co/gnxjlJVn2z
Security updates for October 2026 are now available. Details are here: https://t.co/ue1BEvKRNp
As security update packages address more CVEs, prioritization can become more complex. In a new blog, we explore risk cohorts, an approach to grouping CVEs around shared deployment, exposure, and trust-boundary questions to help customers make vulnerability analysis more manageable.
Learn more: https://t.co/dsHO0kPev6
🚨 BREAKING: A Steam vulnerability (0-Day) on Windows lets any normal user silently escalate to full SYSTEM privileges ‼
Showcase attached below, credits to @killa
PoC could be found in the first comment.
@Steam
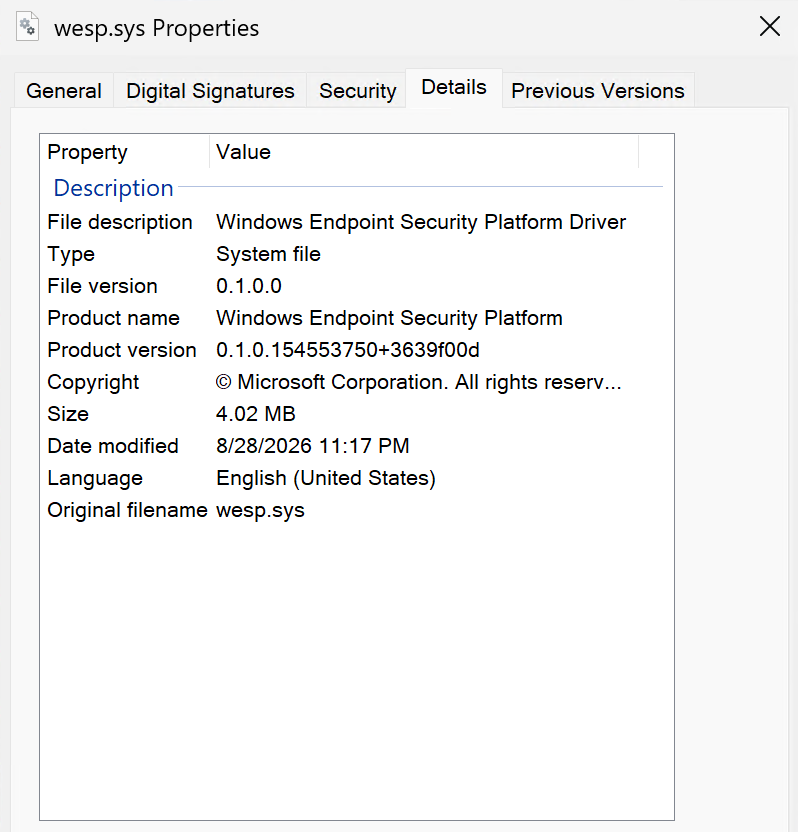
Latest preview build (29661) ships wesp.sys! The long-awaited initiative that should make it easier for EDRs to move capabilities to user mode and stay more resilient against kernel-level attacks.
Microsoft killed my exploit 😢
This Friday on @offby1security I'll talk to @Steph3nSims about what why, how and if this is the end for this class of exploit techniques
He copied a value out of the Windows Event Log.
Pasted it into his special browser.
And he was signed into Microsoft Entra as the user who had just authenticated.
No password. No phishing link. No stolen private key.
@MGrafnetter's Black Hat USA 2026 research...
My #BHUSA 2026 slides are online!
It was an honor to share our AFD research and how a different perspective led to 30+ Windows kernel vulnerabilities.
Blog post coming soon — check out the slides here:
https://t.co/l8xIaRtL7V
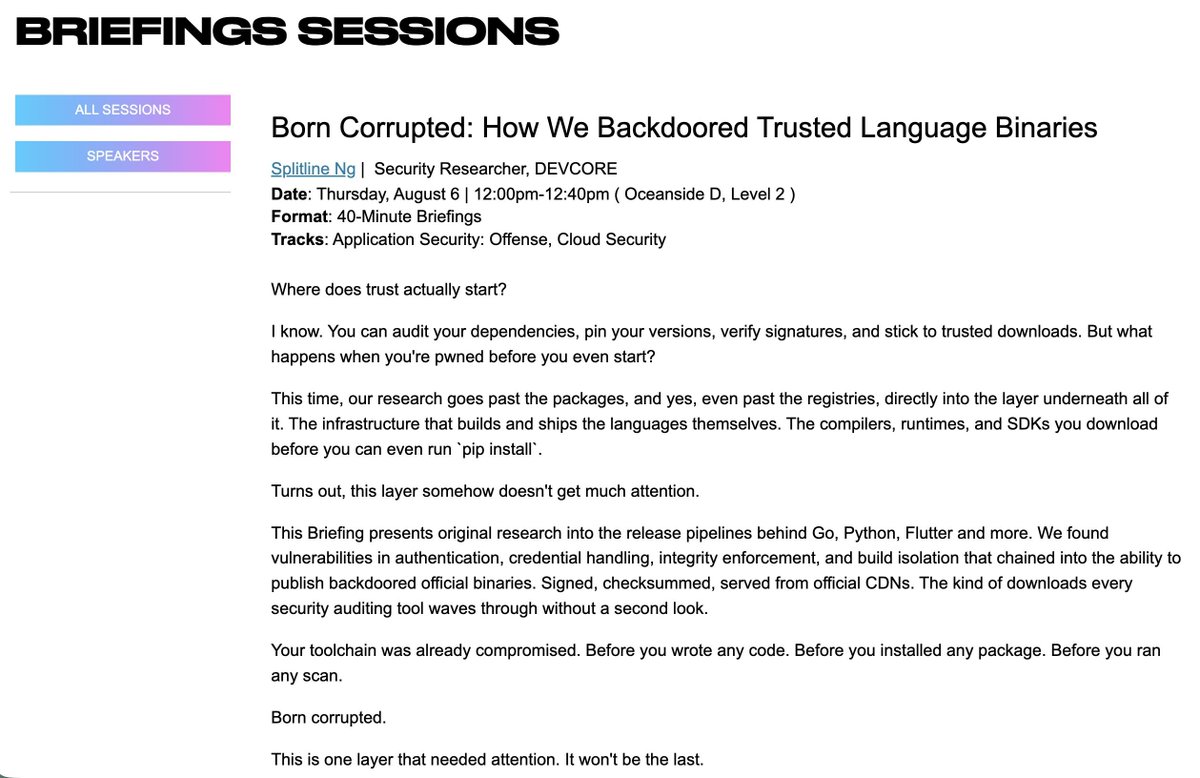
Next week at @BlackHatEvents#BHUSA, I'll present “Born Corrupted: How We Backdoored Trusted Language Binaries”
We found ways to compromise Python, Go, Flutter & Julia at the supply-chain layer, turning trusted bins into whatever hackers want them to be!
Check out the abstract: