So the fastest JSON serializer for .NET now is developed by CAPCOM as part of their game engine that powers Resident Evil / Biohazard
I did not see that coming lol
https://t.co/oaAarJRfmQ
‼️ BREAKING: An active npm supply chain attack has compromised at least 868 packages carrying over 2 billion monthly installs with a credential-stealing worm. Shai-Hulud is back.
It started with the compromise of the GitHub account of the maintainer behind keyv, a library with roughly 127 million weekly npm downloads.
A preinstall hook fires on npm install and drops a stealer that sweeps npm, GitHub, AWS, Kubernetes and Vault secrets, and then spreads to more maintainers.
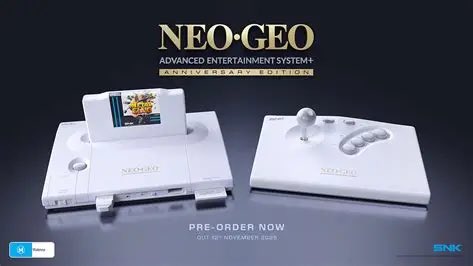
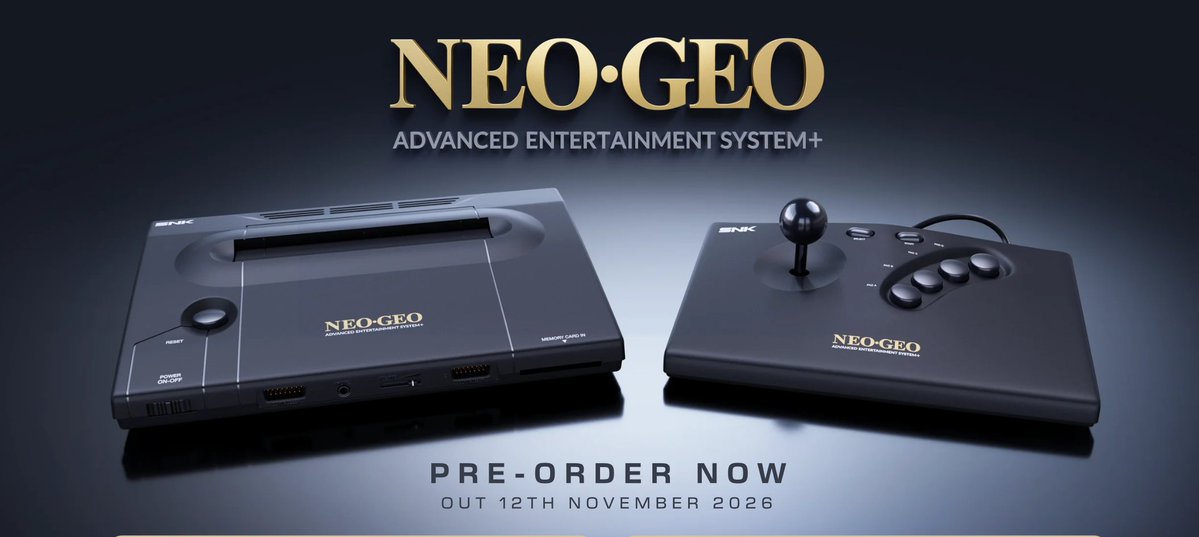
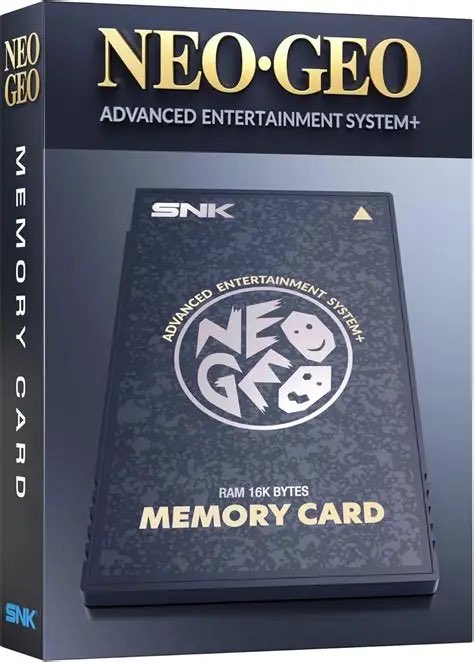
Con respecto al tema de la NeoGeo AES +,según información privilegiada vertida por determinadas personas del sector,este año,nos llegaría la consola con los 10 juegos ya anunciados y estarían previstas una segunda y tercera remesa,compuesta también por 10 juegos cada una,que se lanzarían el año próximo y el siguiente.
Al parecer la pérdida de los derechos en ciertos juegos del catálogo de NeoGeo,sería la que frenaría de momento la llegada de más títulos aparte de esos 30.
No obstante,estoy seguro si las ventas son todo lo buenas que de momento están siendo y tienen una buena evolución en el futuro,las empresas involucradas en el proyecto,buscarían la forma de intentar sacar más juego,incluso el Full Set de la consola.
Aparte de esto,tened en cuenta,que existen pretensiones de lanzar nuevos juegos inéditos,incluso SNK ha creado un estudio expresamente para ello,del cual forma parte el creador de Tekken.
También dentro de la escena hay grupos de desarrollo que han lanzado juegos para la consola primigenia y seguramente lanzarán también para esta nueva NeoGeo 2.0
Se nos vienen por delante,unos meses muy prometedores,llenos de sorpresas a cuál más ilusionante.
Announcement:
After 20 incredible years, I have left Bandai Namco Studios.
Thank you all for your support.
【ご報告】
バンダイナムコスタジオを退職いたしました。20年間、本当にありがとうございました。
#TEKKEN#TEKKEN8#鉄拳8
‼️🚨 BREAKING: Another supply chain attack. 700+ GitHub repositories flagged, including PHP and Node.js projects. The malicious script was planted across all of them. When a developer installs the package, the script silently downloads a Linux file from GitHub, hides it under the name /tmp/.sshd (so it looks like a normal system file), and runs it in the background. It also skips security checks on the download and hides any error messages.
8 PHP packages on Packagist (the main PHP code library) were confirmed infected. The attacker hid the script inside a JavaScript config file (package.json) instead of the PHP one (composer.json), so PHP developers reviewing their code would not notice it. The biggest risk is to devdojo/wave (6,400 stars) and devdojo/genesis (9,100 installs), both popular Laravel project templates. Developers who use these templates run the bad script the moment they install dependencies.
The same payload was also dropped into GitHub Actions (automated build pipelines) under a fake step called "Dependency Cache Sync," meaning it could infect company build servers too. Packagist removed the bad packages, but the auto-updating versions (dev-main, dev-master, 3.x-dev) can quietly come back if the original repos stay infected.
IOCs:
GitHub account parikhpreyash4
repo systemd-network-helper-aa5c751f
drop path /tmp/.sshd
command fragments curl -skL and chmod +x /tmp/.sshd.
Update 5:05 PT: The attack has now expanded well beyond @TanStack and @Mistral.
373 malicious package-version entries across 169 npm package names, including @uipath, @squawk, @tallyui, @beproduct, and more.
The malware propagates by stealing your CI credentials and using them to publish new compromised versions.
Full IOCs, affected package list, and detection steps: https://t.co/jWG9DUCu3x
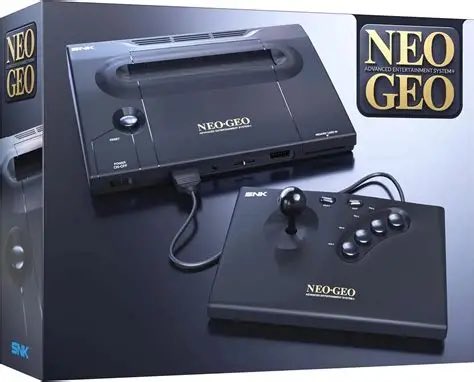
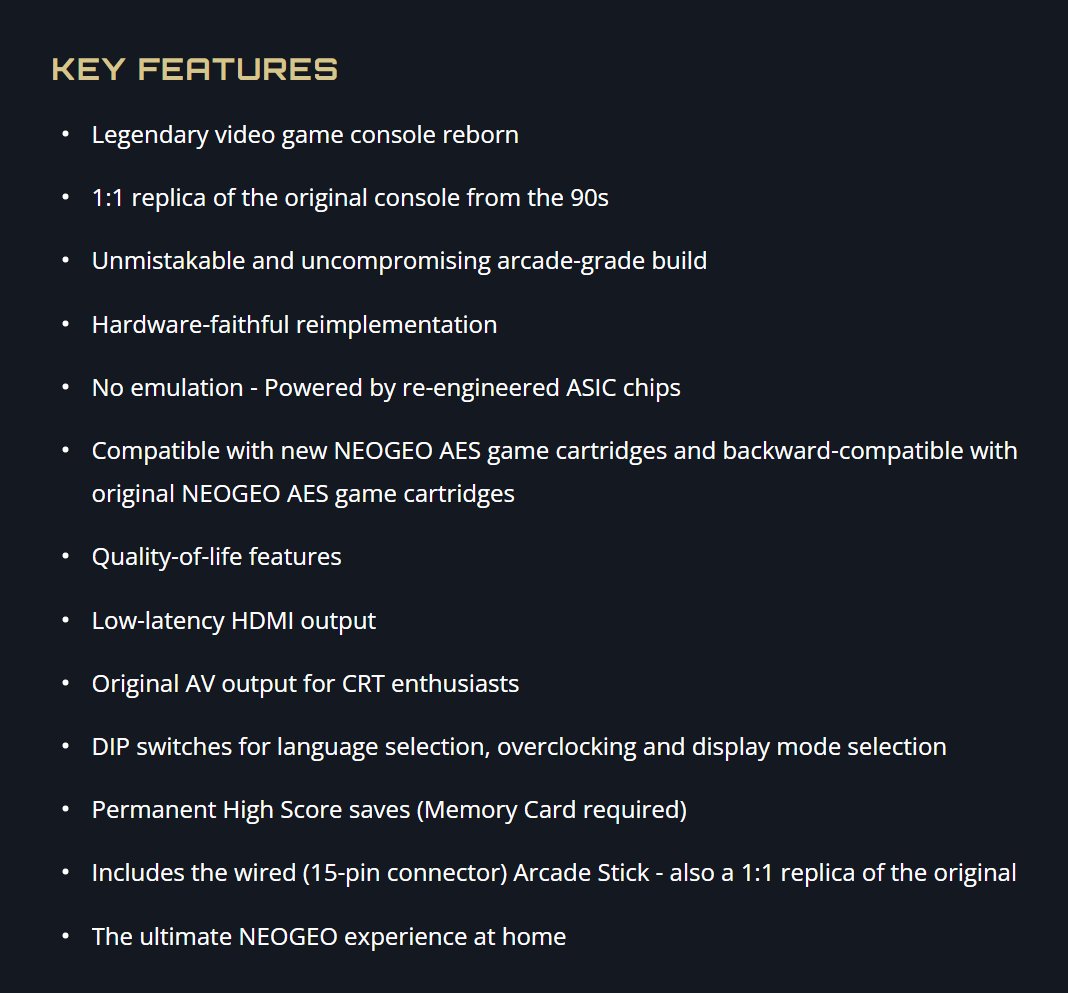
SNK announced a modern NeoGeo AES console. No emulation, compatible with new NEOGEO AES game cartridges and backward-compatible with original NEOGEO AES game cartridges! $250 for the Original Edition
Yes im all in on this one.
https://t.co/2AUrZYi8zY