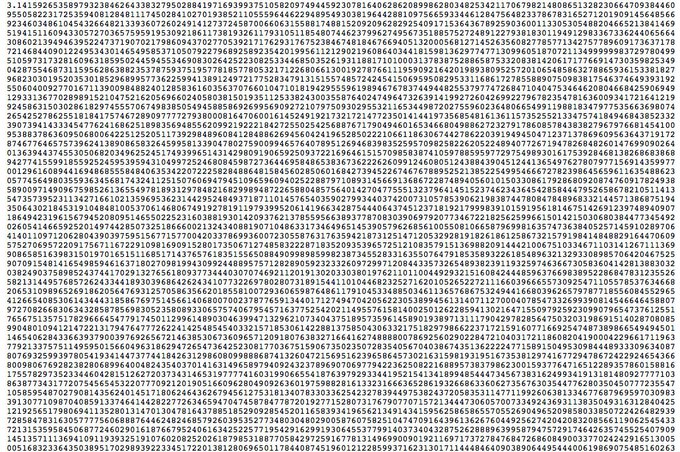
Did you know?
NASA only uses 15 digits of π for calculating interplanetary travel.
At 40 digits, you could calculate the circumference of a circle the size of the visible universe with an accuracy that'd fall off by less than the diameter of a hydrogen atom.
#piDay2024
Is there a portable low-level trick way for callbacks in my C++ codebase to support capturing lambdas with a compile-time flag, but without relying on std::function/<functional>, or with less overhead? (cont.)
The Nmap Project mourns the passing of our friend and legendary hacker Kevin Mitnick. He helped inspire my (Fyodor's) passion for network security, as well as Nmap features such as the TCP Initial Sequence Number predictability report. Later we worked together on the hacking novel "Stealing the Network: How to Own a Continent". Here's a fun pic from our 2004 HOPE Conference book signing. Rest in peace, @kevinmitnick.
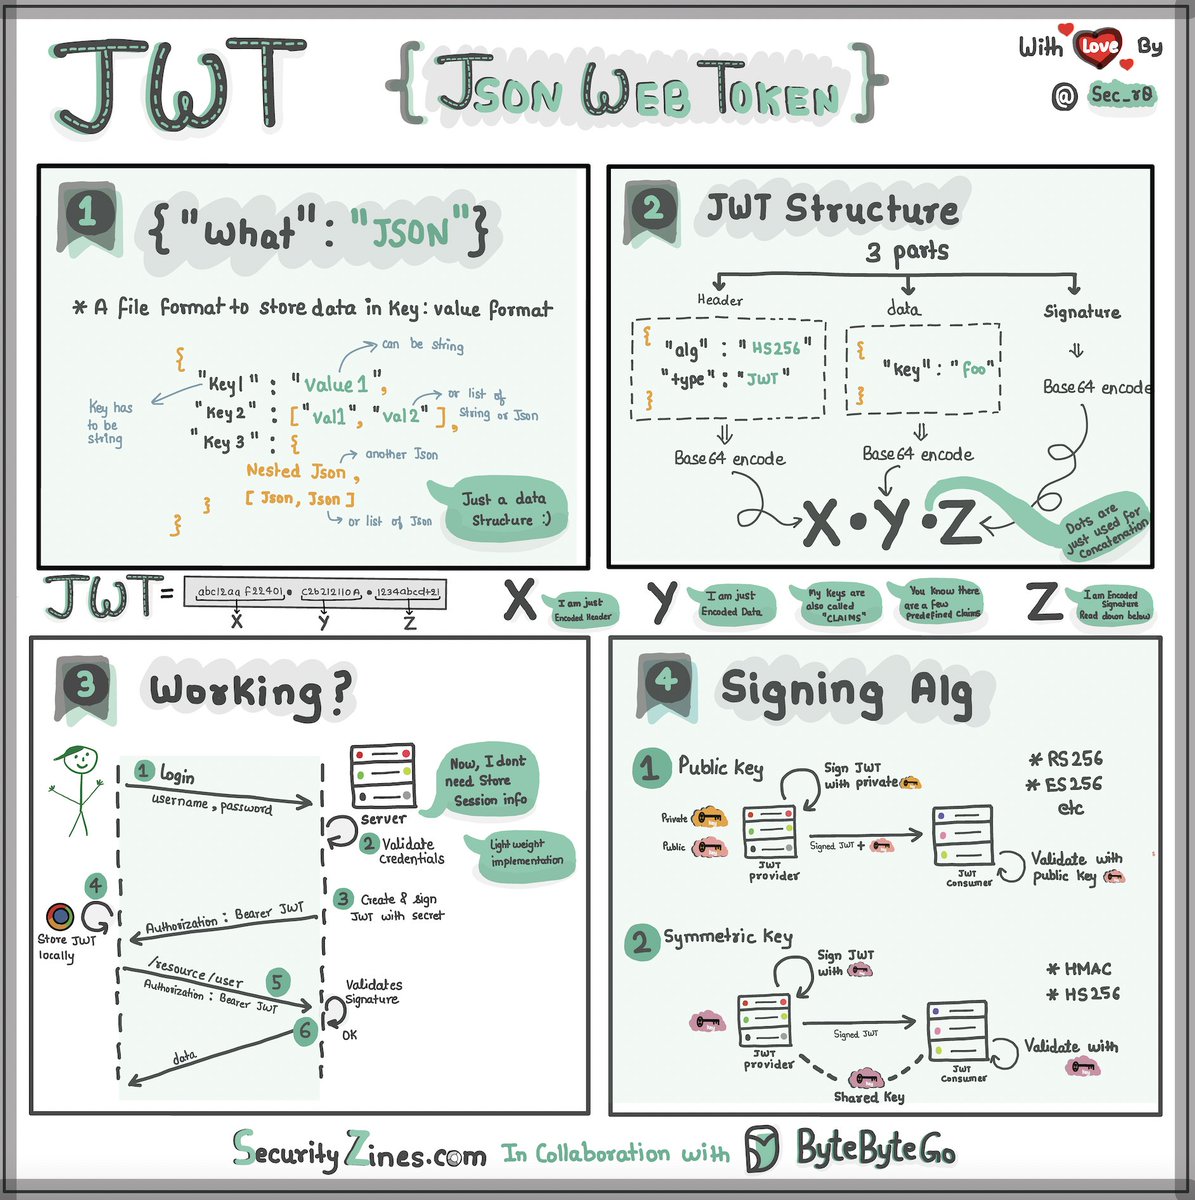
Explaining JSON Web Token (JWT) to a 10 year old Kid.
Imagine you have a special box called a JWT. Inside this box, there are three parts: a header, a payload, and a signature.
The header is like the label on the outside of the box. It tells us what type of box it is and how it's secured. It's usually written in a format called JSON, which is just a way to organize information using curly braces { } and colons : .
The payload is like the actual message or information you want to send. It could be your name, age, or any other data you want to share. It's also written in JSON format, so it's easy to understand and work with.
Now, the signature is what makes the JWT secure. It's like a special seal that only the sender knows how to create. The signature is created using a secret code, kind of like a password. This signature ensures that nobody can tamper with the contents of the JWT without the sender knowing about it.
When you want to send the JWT to a server, you put the header, payload, and signature inside the box. Then you send it over to the server. The server can easily read the header and payload to understand who you are and what you want to do.
Over to you: When should we use JWT for authentication? What are some other authentication methods?
–
Subscribe to our weekly newsletter to get a Free System Design PDF (158 pages): https://t.co/4QcX8btXGL