🔥Root Cause Analysis Part 2 of Past DeFi Incidents.
We have covered another 101 incidents. We hope this information can help developers avoid making the same mistakes as much as possible.
👉https://t.co/dvv3c1yCik
#Web3#DeFi
Last year, Apple shared a high-level overview of "Memory safe iBoot implementation". I thought it would be nice to reverse and write about it, hope you will find it interesting :) https://t.co/roMrVSHVU1
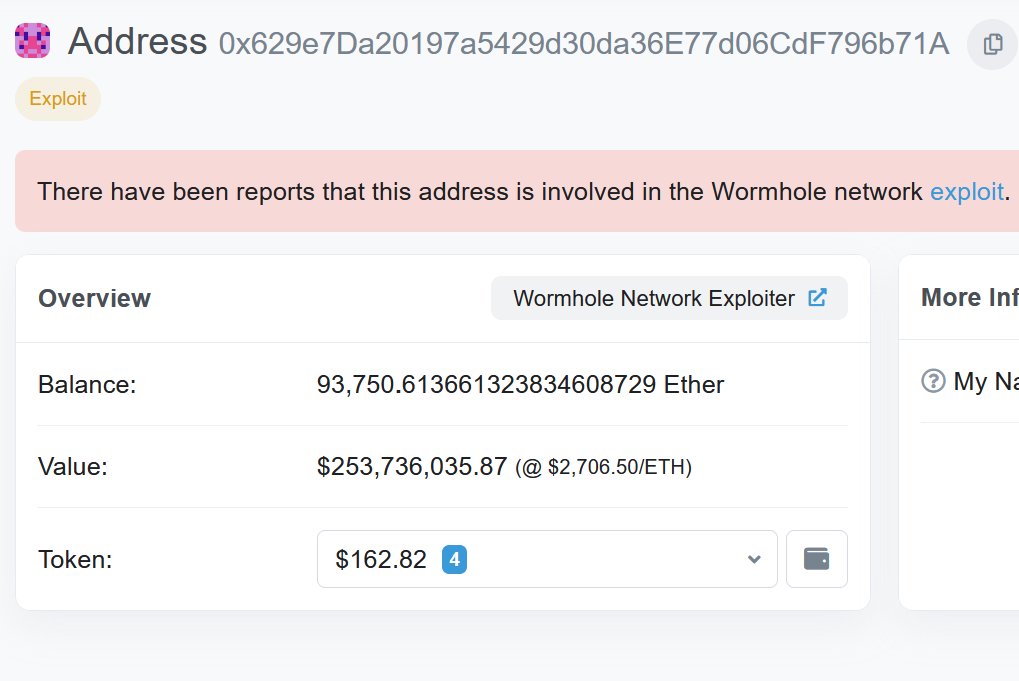
How did the @wormholecrypto exploit work? I joined forces with @gf_256 and @ret2jazzy to reverse engineer the exploit, and now that it's been patched we can finally share it with you👇
I wrote an LPE for CVE-2014-3153 AKA Towelroot, a bug in the Linux Kernel that was used to root Android devices earlier. The original exploit is closed source and protected against reverse engineering.
PoC + mini write-up here:
https://t.co/uETe1eBnZo
Finally got around to publishing this document that I wrote some time ago about how (I think) Fuzzilli works: https://t.co/EMrlMcLlse feedback welcome!
@5aelo
I did a similar research like this one before :
https://t.co/8Nb0zaeVka
And even I can run any iOS App on the Xcode Simulator directly :
https://t.co/XYYv7PvtQH