I've been researching the Microsoft cloud for almost 7 years now. A few months ago that research resulted in the most impactful vulnerability I will probably ever find: a token validation flaw allowing me to get Global Admin in any Entra ID tenant. Blog: https://t.co/jD6EaGtsn3
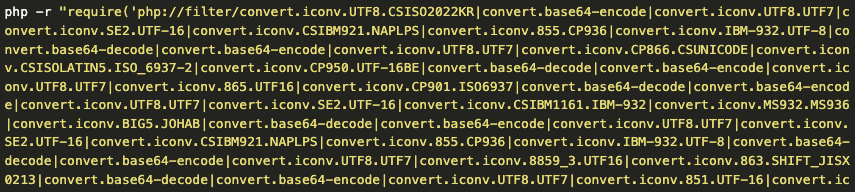
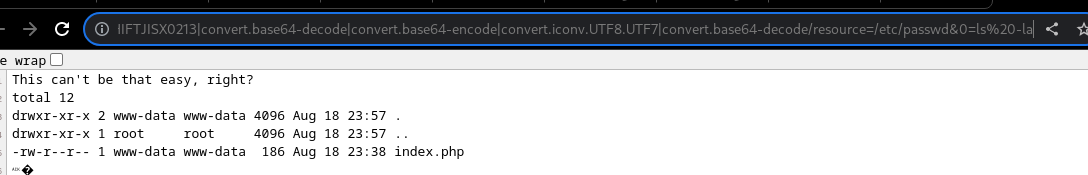
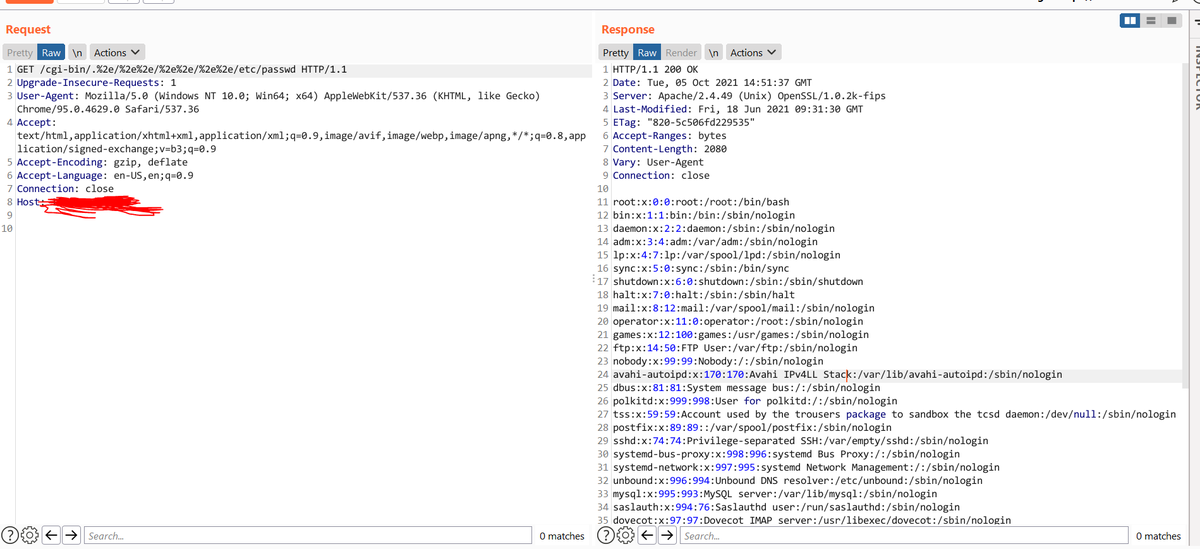
This new trick for turning any PHP LFI to RCE is awesome! I've been wondering why it didn't get more attention since it works better than any other LFI2RCE techniques out there (such as expect://).Props to @loknop for publishing this technique initially👏
https://t.co/lGXHb4IGLR
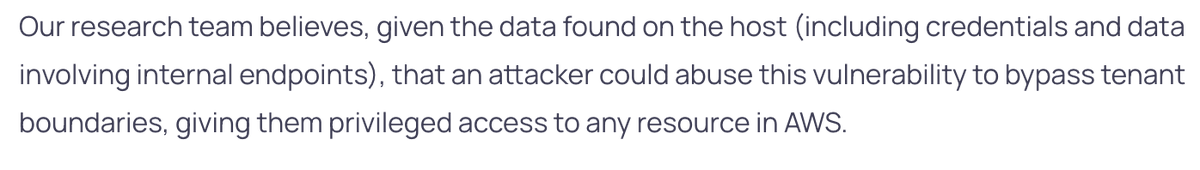
😱😱😱 This is worse than ChaosDB for AWS. @orcasec gained access to all AWS resources in all AWS accounts! They accessed the AWS internal CloudFormation service.
https://t.co/2oCCRvo389
Separately, they did something similar for Glue.
https://t.co/BDFMLQI06B
10 #Log4Shell Facts vs Fiction: a 🧵
1. 1.x is NOT vuln to this RCE. While it doesn't have another RCE, it requires access to send serialized data to a listener ON the log server. This is much MUCH harder to exploit and kind of rare for a Log4j server to be running.
Finally, here is the blog for the prototype pollution research we did.
"A tale of making internet pollution free"
- Exploiting Client-Side Prototype Pollution in the wild
https://t.co/jsShZGlgKB
I wrote about how I exploited a bunch of outdated Apache Airflow instances in bug bounty programs and earned over $13,000 for it! https://t.co/Z1a6WXwssy
idk why I havent thought of this before, but its very easy to hide those "external sender" warnings that get appended to your emails during phishing campaigns 🤔. Email gateways/FW just add HTML at the start/end of emails, simply add CSS to hide it! #RedTeam
See images:
Check out our blog post on Context Aware Content Discovery https://t.co/ma7hdgPPfI - we drop a tool (Kiterunner - https://t.co/u9mb9DUlkg) and some datasets. Hope you can find more endpoints through our work!
Recently @Rhynorater sparked a discussion about exploiting blind SSRFs. At @assetnote, we've collected some information together and have created a Glossary of Blind SSRF Chains which can be found here: https://t.co/ziGHgBEXKL - we hope people can use it as a reference!
[BLOG] Kerberos Bronze Bit Attack
https://t.co/nupsEm8Kjr
This is some great work by Jake Karnes that details how to bypass restrictions related to the “sensitive and cannot be delegated” setting (among other things). Worth the read!