🚨 PHP is going to be dropping emergency security updates tomorrow (October 21st, 14:00 UTC).
- CVE-2026-109618 & CVE-2026-109619 are unauthenticated RCE vulnerabilities both with a score of CVSS 9.2
- The RCE appears to work on default installations of many services & frameworks such as WordPress, Magento, Laravel and more
- PHP versions >5.4.0 affected
- Discovered by team @calif_io
i've even made typo refering "deepseek" while reporting this to ASRC🤦♂️. Initially, i've found this vulnerability on deepseek first, then it it turns out qwen is vulenrable as well lol
non-sandbox XSS on qwen chat💀
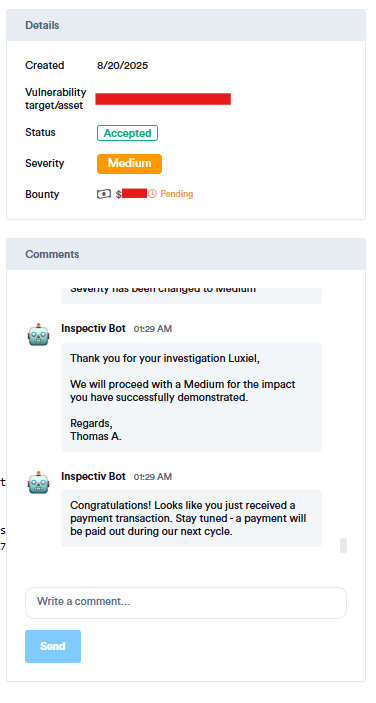
they patched the vulnerability and got medium sev bounty :V
I've also open an issue to Deepseek as well, yet there's still no response (same payload)
Check it out:
https://t.co/3ZduxYWYme
#Bugbounty#XSS#EthicalHacking
Hi everyone!
I built this tool to automate the deep dive domain recon on Virustotal. It recursively hunts subdomains and URLs.
feel free to enhance it🤗
https://t.co/8Z8Mj6GPr7
full case study here: https://t.co/uAfOUjFemV
If you find it useful, a star ⭐️ is much appreciated
Holy shit… the exploitation of CVE-2025-55182 has reached a new level. There’s now a publicly available Chrome extension on GitHub that automatically scans for and exploits vulnerable sites as you browse. Absolutely wild. 🤦♂️