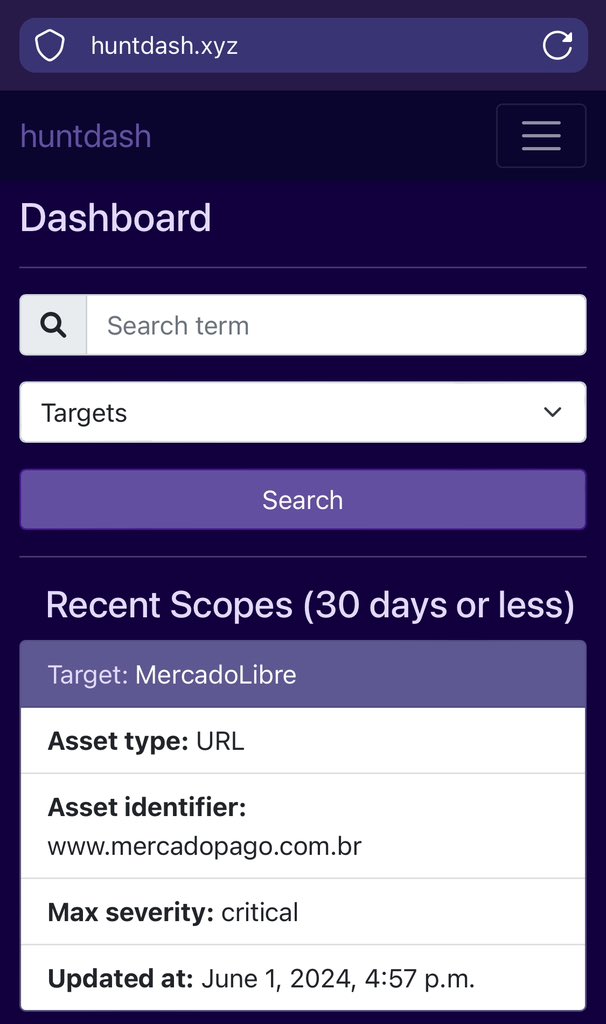
I made https://t.co/cduulFMmkv some time ago and its gaining a bit of traction now 🥳
The idea is for it to be like a hackernews (upvote and downvote / comments) of links to bug bounty and infosec writeups.
Would love to hear any opinions!
Want to grab coffee, swap stories about the wild things our hackbots are doing, or just chill? Join @busf4ctor and me at Cafe Cuto, Saturday 9–10 AM. https://t.co/36WJP1TgU5
¿Sabías que Montevideo Flowers usa la tecnología de Agentify para conectarse con vos de manera más rápida y sencilla?
Con nuestros agentes de IA, ahora podés explorar su catálogo completo de Meta y hacer tus pedidos por WhatsApp sin complicaciones.
¡Descubrí cómo la inteligencia artificial simplifica el proceso de compra para que te enfoques en lo realmente importante
Más info en https://t.co/eg3m2AZPbh
@levelsio I’d love to know your take on affiliate programs for a startup and some basic commison numbers that make sense to you.. currently trying to figure out pricing and sales for a side project 🫶🏾
New episode focused on Browser Extension Hacking is live with @MtnBer!
We cover the structure of browser extensions, the threat model for each component, and some practical vulnerabilities/common mistakes.
Very practical episode.
https://t.co/J2mSZu5Ays
🎉 Announcing ffufai!
Everyone knows ffuf is my favorite tool. @samwcyo had the idea today to let ai pick the extensions for ffuf.
This will make automation SO MUCH more accurate and useful. Check it out here:
https://t.co/twOsdNOmjK
Our security researcher @hash_kitten found one of the most critical exploit chains in the history of @assetnote. Affecting 40k+ instances of ServiceNow, we could execute arbitrary code, access all data without authentication. You can read our blog here: https://t.co/2yTgn1NzhY
At @assetnote, we published our research on Magento's pre-authentication XXE (CVE-2024-34102). @hash_kitten and I reproduced this issue together. It is a brilliant vulnerability originally found by Sergey Temnikov. You can read our research here: https://t.co/wENjzVSAYh
Just discovered "Reset Tolkien" , a shiny new tool from @AethliosIK for cracking time-based secret tokens with the sandwich attack. Random-looking tokens can contain so many flaws, it's great to see more eyes on this area.
https://t.co/lFBwChkneU
It's crazy how reading some old vulnerability blogs and adapting to today's infrastructures can be lucrative.. My favorite program, expect some reports soon!
🔥 Excited to finally release "The Art of Bypassing WAFs" by @Brumens2 from #NahamCon2024. This is a super Impressive workshop with live demos to try on your own! 👀https://t.co/16ReDBKAOQ