Microsoft Security has been tracking criminal actor DEV-0537 (LAPSUS$) targeting organizations with data exfiltration and destructive attacks - including Microsoft. Analysis and guidance in our latest blog: https://t.co/gTMXJCoPY5
Microsoft is monitoring escalating cyber activity in Ukraine & published analysis to give organizations the latest intelligence to guide investigations into potential attacks & info to implement proactive protections against future attempts. Read more at https://t.co/aIpMhoyHz9.
Twenty years ago this week, Bill Gates sent a now-famous email to Microsoft employees announcing the creation of the Trustworthy Computing (TwC) initiative. Here's how the TwC is going today: https://t.co/SRkoD6q5cy https://t.co/0rKBUYcWcd
We have observed a China-based ransomware operator that we’re tracking as DEV-0401 exploiting the CVE-2021-44228 vulnerability in Log4j 2 (aka #log4shell) targeting internet-facing systems running VMWare Horizon. https://t.co/6GOdRwRTjk
Microsoft is tracking threats taking advantage of the CVE-2021-44228 remote code execution (RCE) vulnerability in Apache Log4j 2 ("Log4Shell"). Get technical info and guidance for preventing, detecting, and hunting for related attacks: https://t.co/vOB7R1LXlj
Here I am waiting to argue for my virtual court hearing(s) and then the electricity gets cut off.
NDMC this has been happening on almost daily basis.
Why is this happening on Daily basis?
@tweetndmc#NoElectricity#virtualhearing
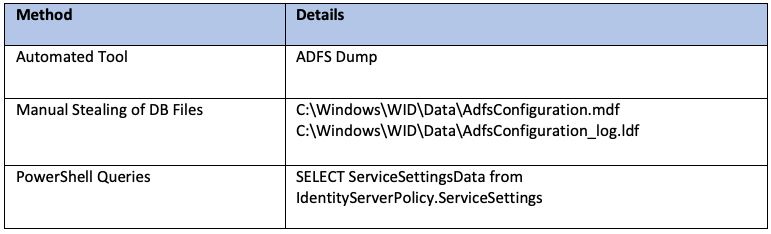
Backdoor #Office365 and #Azure AD by stealing AD FS certificate/key pair. Golden SAML attack will allow an attacker to:
> Bypass MFA to Azure / Office365
> Logon as any AD user regardless of password resets
> Method is usually valid for a year
https://t.co/16L9k10tB7
A few months ago Cellebrite announced that they would begin parsing data from Signal in their extraction tools. It seems they're not doing that very carefully.
Exploiting vulnerabilities in Cellebrite's software, from an app's perspective: https://t.co/9ar6ypnPe2