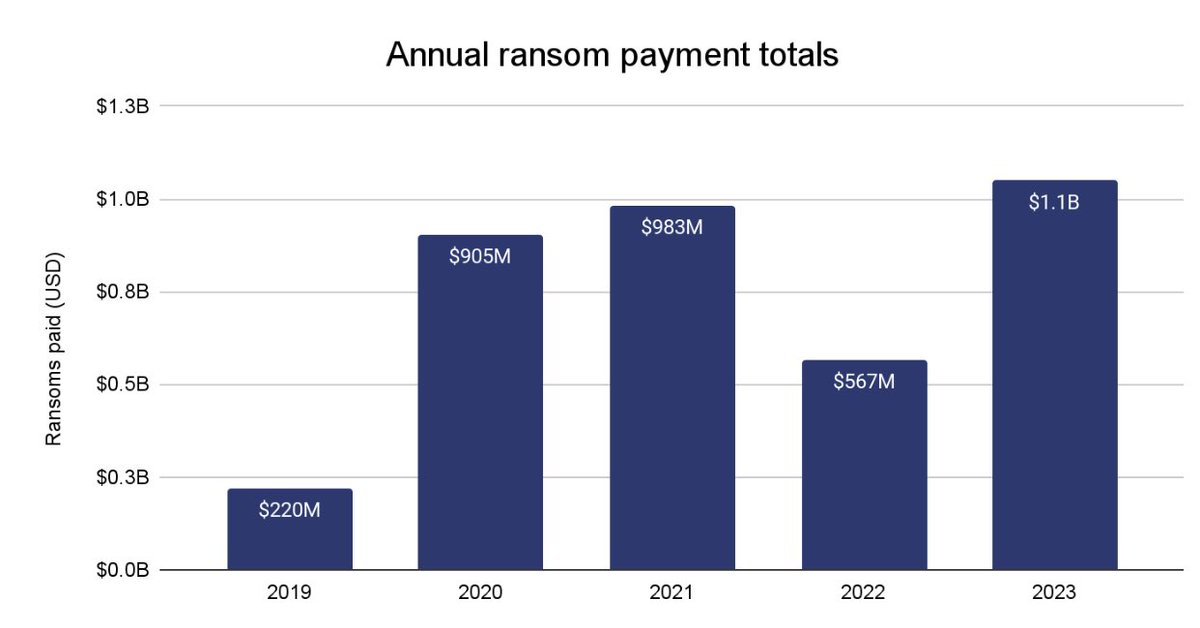
Our ransomware report is out today and it brings me no joy to share that 2023 was a record year in terms of ransoms paid — bringing us into the billions — a near doubling of 2022.
🧵1/6
📍 Researchers have found a backdoor called Effluence, which is deployed after exploiting a security flaw in Atlassian Confluence. This malware is persistent and cannot be removed by patching the Confluence software, according to Aon's Stroz Friedberg Incident Response Services.
This novel web shell “hijacks the underlying Apache Tomcat webserver and silently inserts itself between Confluence and Tomcat–making itself available on every webpage ...”
Interesting CVE-2023-22515 post-exploit behavior discovered by @StrozDFIR
https://t.co/HUlLGx1WeK #dfir
👨💻 #ScatteredSpider#UNC3944 has been targeting organizations across multiple sectors. The latest target being #MGMResorts.
🕵♂️ #StrozFriedberg has responded to multiple incidents involving this threat actor. We've published a client advisory that provides details into attacker techniques, recommendations and countermeasures.
Link: https://t.co/gb2x6aApw4
📄 Here are some highlights from the report:
1. A common thread across several investigations has been the utilization of social engineering tactics to gain access to privileged accounts.
2. This threat actor has demonstrated a significant level of knowledge and skillset when operating within an organization's cloud environment.
3. This threat actor has been observed sending personalized and threatening messages over email, phone, and SMS to gain attention from victim organizations. In some instances, they have contacted the media to add pressure and extract payment from companies.
4. This threat actor has been observed deploying ransomware on ESXi servers. This threat actor has loosely affiliated itself with the #ALPHV or #BlackCat ransomware group in some instances and has used the ransomware group’s negotiations and leak site infrastructure to post information about victim organizations.
This is a group that is very skilled and persistent. Please review the recommendations in our report to better protect your organization from this threat.
#StrozFriedberg #DFIR #IncidentResponse #CyberSecurity
@appSecExp@TCMSecurity ✅ Partha Alwar & Ann Romer, Directors at @StrozDFIR (A co-presenting session)
Topic: "Navigating EDRs: Unveiling Common Pitfalls in Configuration and Management"
🕵️♂️My colleagues @Fal_Forensics and Kostya gave an excellent talk on lateral movement at #VeloCon2023 today.
🚀 They also released a Velociraptor plugin that processes multiple lateral movement artifacts and gives you a normalized output.
👨💻 Check it out here: https://t.co/5tugoswiDB
#StrozFriedberg #DFIR #IncidentResponse
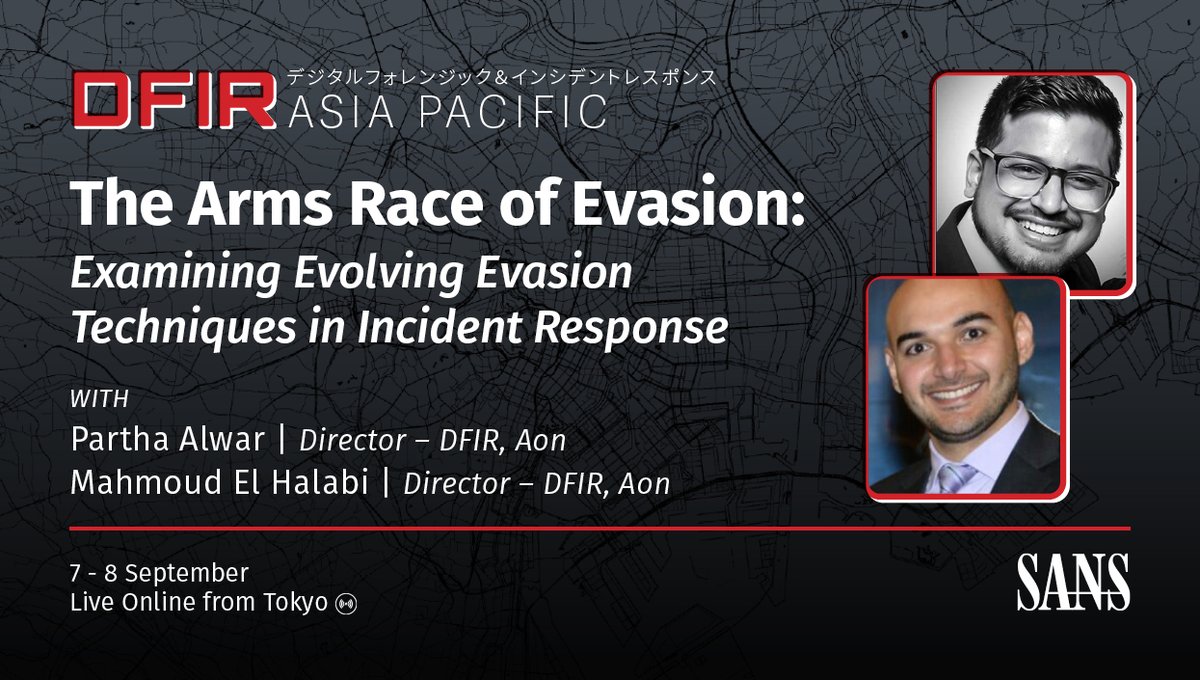
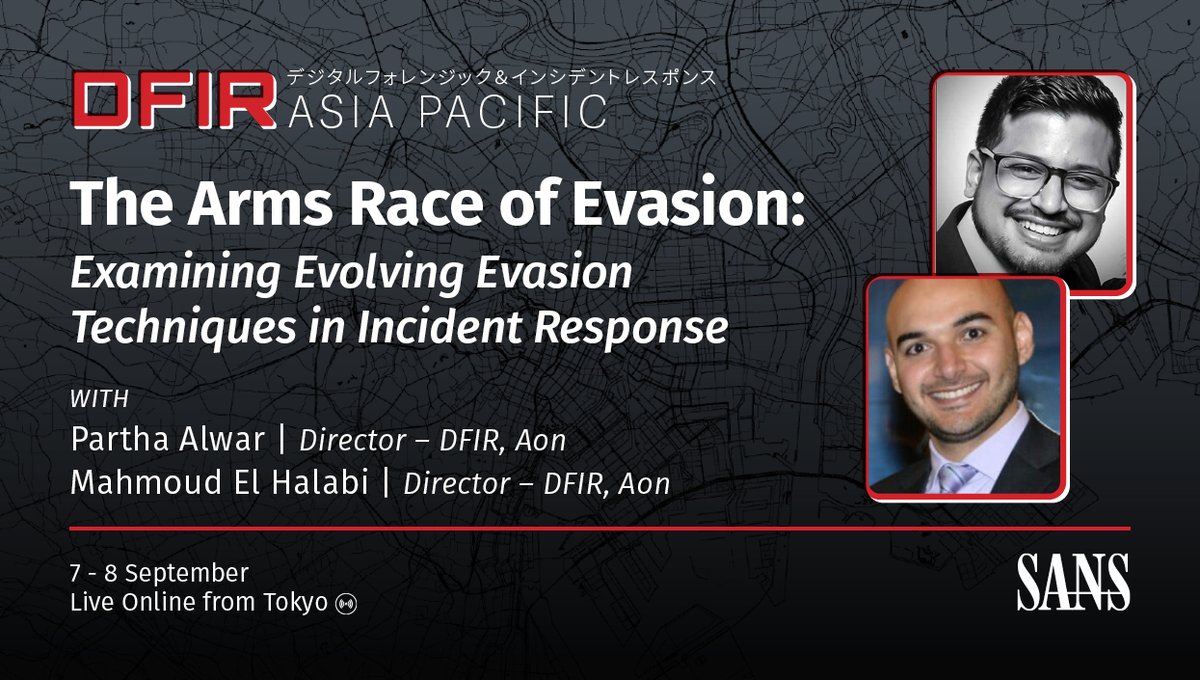
Don't miss this upcoming #APACDFIRSummit talk! 🗓️
🎤 The Arms Race of Evasion: Examining Evolving Evasion Techniques in Incident Response
👥 Partha Alwar & Mahmoud El Halabi, Director, DFIR, Aon
✍️ Join us September 7 - 8 for Free Live Online: https://t.co/hE7LkCT0n7
I’m very excited to be speaking with my colleague at the SANS APAC DFIR Summit on September 7th at 9:35 PM ET.
Our talk will cover creative defense evasion tactics seen by the @StrozDFIR team during cyber incidents.
Attend and register for FREE here: https://t.co/7q1AEuBr6r
#DFIR #CyberSecurity #IncidentResponse #SANS #APACDFIRSummit
I made some python (an IDA Python and standalone) scripts for analysis of Crytox/.wait ransomware. It deals with resolving the API hashes used by the malware.
https://t.co/c2XhTqBCt8
#DFIR#Malware#Crytox
Aon’s 2023 Cyber Resilience Report helps business leaders benchmark their organization's #cyber risk maturity against peers and make #BetterDecisions when managing cyber across six #risk areas. Read more about Aon’s insight in The Wall Street Journal: https://t.co/kYJjVCj31A
Hey folks! I'll be going on a conference tour in the next couple of months and presenting some research at the following cons:
- BSides ABQ (Sept 8-9)
- BSides KC (Oct 6-7)
- BSides Bloomington (Oct 13-14)
I'm honored to speak at these locations to represent Aon's Testing services team, particularly our red team, and really looking forward to seeing my old Depth Security crew in my favorite city (KC) in October. :)
I made a 4-minute teaser video regarding my research ("DUALITY") - it can be found here: https://t.co/9jMXWftFXf
You can find the talk's abstract in BSides Bloomington's schedule here: https://t.co/VFfl6uNm9M
There is a blog post coming soon as well.
tl;dr - we're simultaneously backdooring multiple DLLs on the fly with custom logic for init access and persistence (to keep each infected DLL alive) via a pipelines, C2 scripts, and a somewhat custom shellcode compilation (carefully written C->ASM) methodology. I'm hoping to take DLL proxying / sideloading to the next level, or at least provide an interesting alternative.
My LinkedIn: https://t.co/6NI9sBxMI7
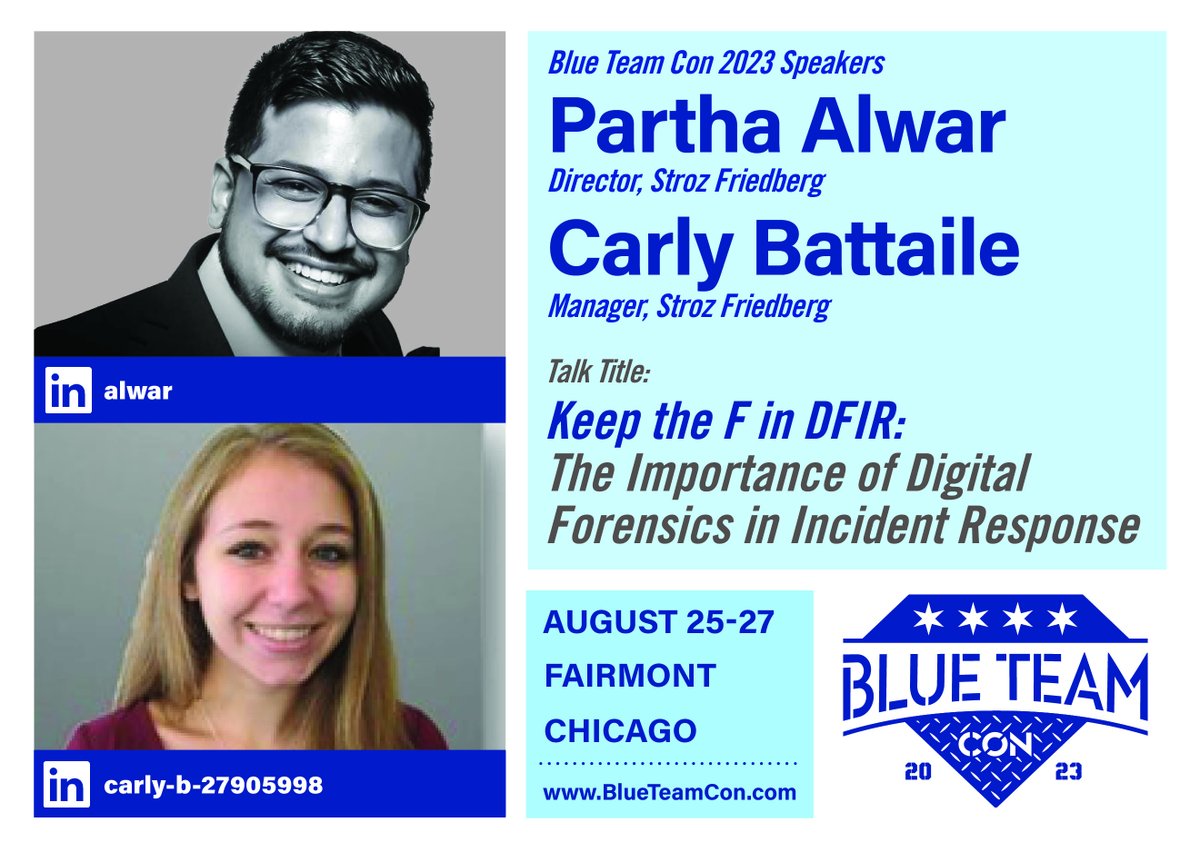
So excited to be speaking at @BlueTeamCon on August 27 in Chicago!
Attend our talk to learn more about the gaps in visibility with EDRs during IRs and how to resolve those gaps with traditional digital forensic artifacts.
We will also be discussing some fascinating real-life case studies!
#DFIR #IncidentResponse
📣 Blue Team Con 2023 Speaker Highlight 📣
Blue Team Con 2023
25-27 August 2023
Chicago, IL
Partha Alwar and Carly Battaile
Talk Title:
Keep the F in DFIR: The Importance of Digital Forensics in Incident Response
See abstract: https://t.co/OAieUgUqOf
Don't miss this upcoming #APACDFIRSummit talk! 🗓️
🎤 The Arms Race of Evasion: Examining Evolving Evasion Techniques in Incident Response
👥 Partha Alwar & Mahmoud El Halabi, Director, DFIR, Aon
✍️ Join us September 7 - 8 for Free Live Online: https://t.co/bvr9fQ5UMi
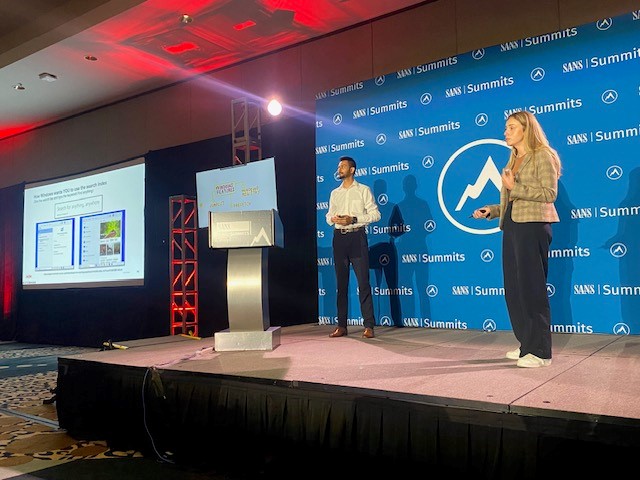
And that is all for this year's #DFIRSummit. We would like to thank our attendees, advisory board and speakers for making the 16th DFIR Summit a success!
We will see you next year 8/22-23 in #SALTLAKECITY!
#DFIR
Phalgun Kulkarni and Julia Paluch discuss how the Windows Search Index can be used as a source of evidence in #DFIR investigations.
Listen here: https://t.co/wdW6548mxp
#IR#IncidentResponse#DFIRSummit