🚽 A toilet flush can throw a mist of tiny droplets as high as your face (about 163 cm / 5 ft 4 in) and as far as 1.5 m to the side. Most of those droplets are smaller than 3 micrometres, small enough to float and be breathed in.
Some studies still found them in the air 20 seconds after you flush.
Close the lid before you flush. It won’t trap every droplet (they can still sneak out through gaps), but it stops the plume shooting straight up into the breathing zone.
Paper: Adiyani et al., Science of the Total Environment (2026).
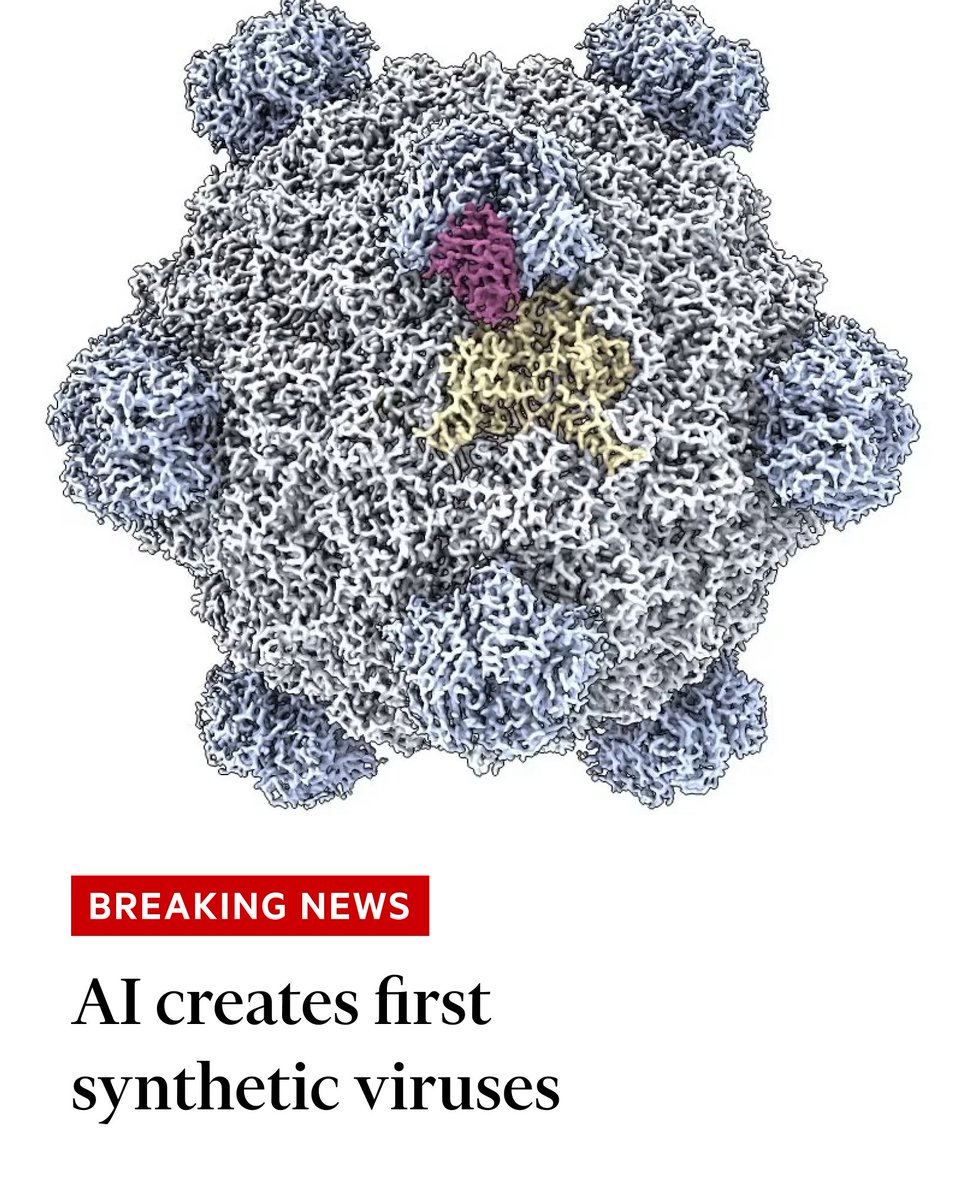
Breaking news: Scientists in the US have for the first time used artificial intelligence to create viruses unknown in nature, a milestone that promises advances in healthcare but also raises important biosafety and biosecurity concerns. https://t.co/L9Hg3hXwz8
A company just sold my data. I caught them using the simple old trick of adding “+companyname” before the @ in your Gmail before signing up: yourname+netflix(at)gmail(dot)com still lands in your inbox.
If “netflix” spam shows up from someone else, you know who sold you out.
Took 2 years to prove this one. Worth it
Since nobody actually read the technical write-up I'll explain something that is very important about this.
The researchers from the University of Washington intentionally introduced a Buffer Overflow exploit into the open-source DNA sequencing compression tool used (fqzcomp) which compresses FASTQ files (the file format DNA sequencers use).
They then developed a malicious DNA sequencing file that would result in a Buffer Overflow in this DNA sequencing software. This specially crafted file would then execute a payload.
It's an interesting proof-of-concept, I don't want to minimize that because I think it's really cool. However, this is basically really fancy and highly targeted payload smuggling that relies heavily on external scenarios outside the control of an actual attacker such as identifying the precise DNA sequencing software being used by a target and having a zero day exploit for it.
This is not like, hiding actual malware in human DNA, or whatever. This is making a malicious DNA file that is read and used by a very specific DNA sequencing software.
Tip of the day - Brave web browser either on mobile or PC eliminates a lot of unwanted shxt like ads and pop ups. It’s quite decent especially if you’re poking around dodgy sites.
If your phone number got hijacked tomorrow, you could lose access to your:
- Gmail
- Banking apps
- Crypto wallets
- 2FA codes
- iCloud backups
One SIM swap can destroy your entire digital life.
Here's how to protect yourself in 15 minutes ↓
Tip of the day - Brave web browser either on mobile or PC eliminates a lot of unwanted shxt like ads and pop ups. It’s quite decent especially if you’re poking around dodgy sites.
I've been coding for 40 years. Here are the top 5 things I wish I knew when I started.
1. 90% of the job is debugging and fixing, not creating new code. Which is still fun if you're good at it.
I used to think programming was mostly writing fresh, clever stuff. In reality, most of your time is spent in other people's (or your own past self's) messy code, chasing down why something that "should" work doesn't. Get really good at debugging early. Learn assembly reading, call stacks, and kernel debuggers. It pays off hugely. The best engineers I saw were absolute magicians at this.
2. Manage complexity from day one (ie: don't write slop and "fix it later" if it goes somewhere).
Very early on, I'd hammer out code and refactor afterward. Big mistake. Now I start with clean, skeletal structure (minimalism first) and flesh it out carefully, with AI or not.
Messy code compounds and becomes unfixable. Upfront discipline on architecture, naming, and simplicity saves enormous pain later, especially in large systems like Windows.
3. Tools and processes matter more than you think
We suffered with basic diff/manual deltas instead of modern source control like Git. Branching, testing, and good tooling would have made porting and collaboration way smoother. Invest in your environment, automation, and reproducible builds early. Good tools amplify your output; bad ones (or none) drag everything down.
4. Understand the problem and existing code deeply before writing
Don't jump straight to coding. Map out the problem, study what's already there (you'll inherit a lot), and plan. Low-level knowledge (hardware quirks, alignment issues on different architectures like MIPS/Alpha) was crucial. Also: assert early and often. It forces clarity.
5. People, politics, and "the right tool for the job" beat pure tech arguments.
Brilliant engineers still argue endlessly. Sometimes it's about ego, not merit. Learn to spot the difference and "steer" the conversation rather than "winning" it.
Bonus from experience: Side projects like Task Manager (started at home because I wanted the tool) can become your biggest hits. Ship small, useful things often. If you're just starting, focus on fundamentals, patterns over syntax, and building resilience for the long haul. It's going to be a wild ride, but the fundamentals still matter.
i saw a mouse with an X-shaped battery compartment.
first thought: this is stupid - who designed it?
5 seconds later: oh.
10 seconds later: OHHH!
the X slot fits an AA or an AAA battery - whichever you've got lying around.
the part most people miss is that the shape also makes it physically impossible to load both at once.
there is no warning label, no instructions and no way to screw it up.
the geometry does the thinking for you.
japanese has a word for this.
poka-yoke = "mistake-proofing."
the product refuses your stupidity before you can offer it.
i wish more things worked like this.
I’m assuming the tcpdump logs were generated from the website. So you’ll need to review the logs for any unusual requests or user agents. Even better if you have a timeline of when users started experiencing the issue so you can look at requests around it. I’m guessing this is likely a DDOS. @grok what do you think?