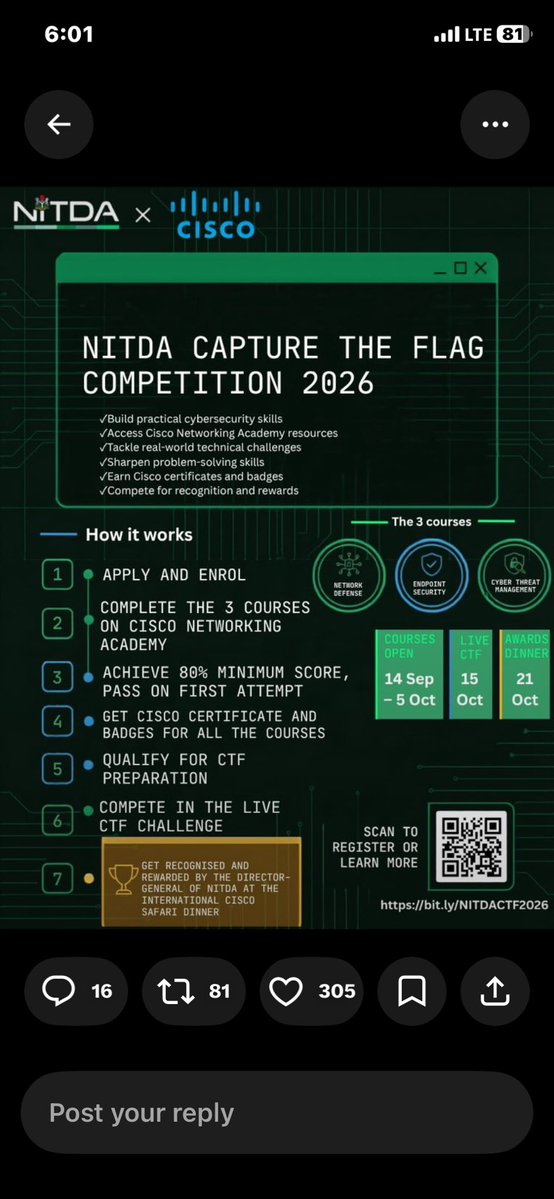
@Phet_Boy01 Best approach to this is smishing. Protip: they set up cloudflare everywhere on they site.
>run osint on mr bayo
>get mail or details
>obfuscate my FUD malware in image
>mr bayo opens image
>.exe delivered
>connects to my c2
>extract pass keys
>access site