@LiveOverflow@i0n1c My question is why people waste time adding signatures/detection/etc everywhere for an exploit that can’t realistically be used at scale
A PoC can work 100% of the time in a controlled lab without demonstrating reliable exploitation at internet scale. Proving RCE and proving it scales across production environments are different claims. #PHP2Shell
@SCMagazine@bishopfox#PHP2Shell is more dependent on the target: public PoCs often rely on particular builds, memory layouts and worker behavior. That makes reliable exploitation harder to generalize.
#PHP2Shell the best marketing campaign a “dead” language could ask for. Global headlines, emergency visibility—and public PoCs that often struggle to make it out of the lab.
@JohnHultquist#PHP2Shell is more dependent on the target: public PoCs often rely on particular builds, memory layouts and worker behavior. That makes reliable exploitation harder to generalize.
@Akshanshjaiswl#PHP2Shell is more dependent on the target: public PoCs often rely on particular builds, memory layouts and worker behavior. That makes reliable exploitation harder to generalize.
#Log4Shell had a frighteningly reusable trigger. #PHP2Shell's public PoCs come with a checklist longer than their own README: PHP build, config, memory layout, worker behavior, a tailwind. Naturally, "critical RCE" made the headline. The checklist got the footnote.
My hot take on this PHP mess is that its incredibly overhyped and we'll see very little ITW exploitation. Overall it seems less impactful than its named bug predecessors; heartbleed, shellshock, log4shell etc
Bug bounties failed. Responsible disclosure failed. #PHP2Shell is what's left: researchers just dropping bombs. I live in this world. I know how complicated, and how often unpaid, this work has become.
Nightmare Eclipse, the person who has been dropping Windows zero-days, has finally decided to share his story. He's an ex-Microsoft employee, we had dinner together, and I've known him and his story for some time.
His real name is Abdelhamid Naceri. He's a very talented and intelligent individual, and he came across as someone who'd be a real professional to work with.
"If only I didn't pour my soul into that job with countless of stupid non sleep nights, i would have gotten over it..." - Naceri
He loved Microsoft.
I wouldn't say that what he did, releasing all those zero-days, was normal, but he felt he had no other option because of the injustice Microsoft did to him.
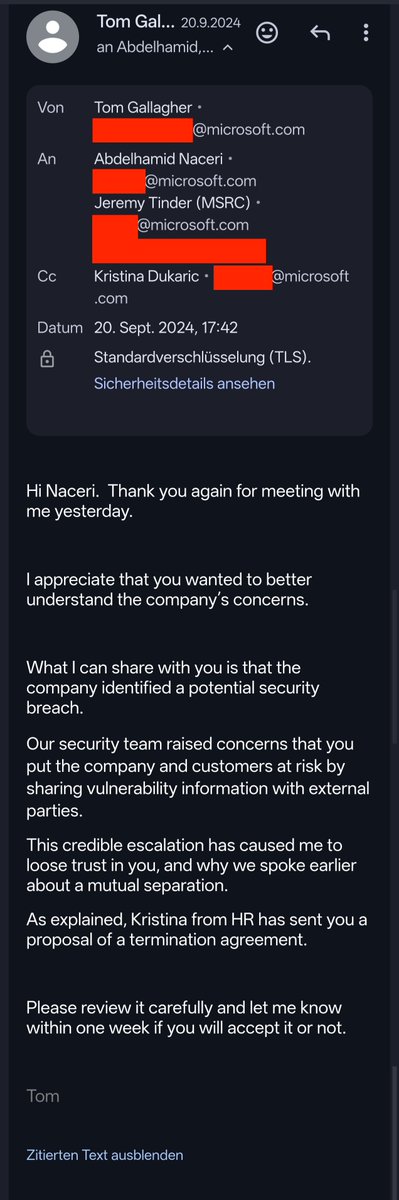
They fired him, and you can read the vague reason they gave in the email sent to him by the Vice President of Engineering at MSRC, below.
According to Abdel's account, VP Tom Gallagher met with him after the firing to tell him they were blacklisting him from Microsoft and writing him a bad reference so he'd never be able to get a job again.
Normally you'd think, well, big deal, just find another job, right? But Abdel doesn't have a European passport, and he was only a couple of months away from getting permanent EU residence.
So instead of granting him those couple of months, Microsoft fired him for a reason that, as far as we can tell, was never made clear, then fought him in court and offered him €55,000 plus a year's pay to drop the case.
All while Abdel was releasing zero-days.
Abdel continued suing Microsoft for unfair termination in Germany, a fight that has cost him over $200,000.
He says Microsoft refused to reveal any details about the security breach and went another direction.
If you are reading this, and you can offer him a LEGAL job, this is his e-mail: [email protected]
@Steph3nSims The future vulnerability researcher probably isn't someone who refuses AI. It's someone with strong exploitation fundamentals who can make AI explore thousands of possibilities while they decide which strange 0.1% deserves another three hours of investigation