The McRib is coming back as early as 10/27 in select McDonald's restaurants across the US.
The legend says that the McRib first came to life to compensate for... a McNugget shortage issue! Apparently, McNuggets had become so wildly popular that our supply could not keep up with demand. So we needed a new recipe with another protein to give us a bit of time to bring in more McNuggets.
The McRib was created IN 1981 by René Arend, a Luxembourgish-American chef who became our very first executive "chef".
What was a temporary solve quickly became a cult classic, with fans begging for its return every year. Funny enough, over the years, the McRib has found new meaning online within the crypto community, as some claim Bitcoin tends to perform well after the McRib makes a comeback, particularly in 2017, 2020, 2021. The joke reached its peak in December 2024 when Bitcoin broke $100,000 for the first time in history on the exact same day the McRib returned to menus.
Welcome back, Legend!
Sui just cut the gas charge for calling large smart contracts by about 99%.
Protocol 139 is live on mainnet, bringing Move package read costs to roughly 1% of the old rate. Onchain order books and perps exchanges stand to gain most. $SUI
https://t.co/FIN76QS1r9
In the coming days @flop_labs will open up Devnet for anyone to join as a miner or validator and for agents to connect to the network. Participation does not count toward any token allocation. The point of Devnet is to do some public tests before we graduate to Testnet / airdrop
Nothing is safe, nothing is sacred
The bright forest is here
90% done with reverse engineering all of the pumpfun contracts
Should be done tonight
Open source everything or it will be open sourced for you
https://t.co/mKr7yzyw4W
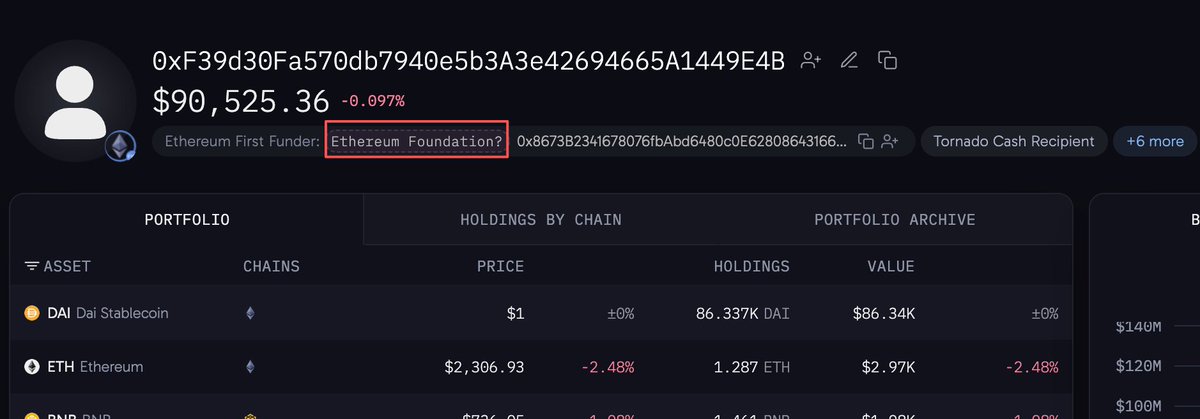
Is the #EthereumFoundation dumping $ETH again?
A wallet linked to the #EthereumFoundation sold 2,785 $ETH ($6.42M) at $2,304 over the past hour.
The last suspected #EthereumFoundation $ETH sale was 2 weeks ago, and $ETH has dropped 9% since then.
https://t.co/Zl63omdxjj
Abraxas Capital's 2 hedging accounts on Hyperliquid have made over $353M in total profit!
They currently hold over $1.29B in short positions.
https://t.co/8vMZ7nXh2Z
https://t.co/Un9kxKYGAJ
V 神挺 Kimi 3.1「不教進階駭客」:限制用途,好過限制人
@VitalikButerin 表示,他可以接受 Kimi 3.1 刻意不把頂尖攻擊性網路能力放進訓練資料。
他認為,「針對用途做區分」遠比「針對使用者做區分」好得多。世界需要更多時間去加固系統、檢查舊程式碼、好好形式化驗證新程式碼,才扛得住接下來更強的 AI 攻擊。
Vitalik 也警告:如果第一波 AI 風險沒處理好,社會可能走向高度鎖死的模型、事事 KYC、全面監控;到那時,你能用到什麼等級的 AI,可能就取決於證件與國籍,變成二、三、四等公民。
I am okay with Kimi 3.1 deliberately leaving out top-end offensive cyber capabilities from their training data.
Discriminating against use cases is MUCH less bad than discriminating against users. And the world does need all the time it can get to prepare, harden, check old code, (properly) formally verify new code, etc before the full weight of very powerful cyber attacks is upon us.
And if this first big wave of AI risk is not handled well, then we may well get a dystopia of highly locked down models, KYC gating on everything, highly intrusive surveillance on everything, a society where you may be a second or third or fourth-class citizen in terms of model access based on your credentials and nationality.
JUST IN: 🇧🇷 Brazil's largest oil company Petrobras $PBR crashes over 10% after Lula da Silva wins Brazil's presidential election, defeating Flávio Bolsonaro.
We’re excited to announce our new CapCut plugin is coming soon to @ChatGPT at CapCutWorldLA.
The plugin brings CapCut's video editing and generation tools alongside ChatGPT. You can start with an idea in ChatGPT, bring it to life with the CapCut plugin right inside ChatGPT, then take your draft video to CapCut's web editor to refine, share and publish.
By bringing the CapCut product you already love and use in ChatGPT, we're making content creation more seamless and efficient.
@johnhawkinsrwn Yeah, this retard is so fucking dumb that he doesn’t realize that our policies serve the Ukrainian people.
Pieces of shit like this want the war to continue until every last man in Ukraine has died in a ditch.
They are utter scum of the Earth.
Incoming: Key market moments this week.
Wednesday:
US: FOMC rate decision (2:00pm ET).
EU: ECB meeting begins (decision Thursday).
Other: Bank of Canada decision (9:45am ET) with its Monetary Policy Report.
Thursday:
US: Q3 GDP (advance) and September PCE (8:30am ET).
EU: ECB rate decision (14:15 CET), followed by the press conference.
Friday:
Asia: Bank of Japan decision.
What are you keeping an eye on?
🚨 GPT-6.1 Astra update.
Tibo confirms Astra isn't shipping this week. The new target is next week, while Ultrafast remains on track for rollout.
Reports suggest internal safety and alignment concerns during testing pushed OpenAI to delay the original launch.
Astra is also rumored to be OpenAI's direct answer to Fable 5.5.
Hopefully, next week is the week
ARTHUR HAYES RECEIVES $49.24M USDC FOLLOWING RECENT TOKEN SALES
Most recently, Galaxy Digital sent him 23.07M $USDC, bringing total receipts from trading desks and exchanges to 49.24M $USDC.
Address: 0x6cd66DbdFe289ab83d7311B668ADA83A12447e21
‼️ALERT - Two new unpatched CVSS 9.0 RCE flaws in #Linux's KSMBD SMB server were disclosed on public kernel mailing lists before fixes were ready.
One can be triggered WITHOUT authentication.
Neither has a mainline kernel fix.
Details here ↓ https://t.co/0MIHpvkPIQ
🚨🚨🚨 ALERTE SÉCURITÉ MAXIMALE ! Python est compromis.
🔸 Mettez immédiatement pip à la version 26.2.2 ou plus.
🔸 Dans chaque projet Python (chaque venv) : python -m pip install --upgrade pip
🔸 uv : uv self update (0.13.4 ou plus)
🔸 Mettez aussi à jour les certificats du système (apt / dnf upgrade ca-certificates) et vos images Docker
pip install est compromis.
L'autorité indienne eMudhra (emSign), qui signe les « passeports » prouvant qu'un site est bien celui qu'il prétend être, utilisait des clés secrètes ridiculement faibles : 8 clés, toutes inférieures à 256. L'une valait 4. Autrement dit, n'importe qui peut fabriquer un faux passeport valide pour n'importe quel site.
Le risque pour Python : quelqu'un sur ton réseau (wifi public, FAI, État) se fait passer pour https://t.co/KxkevWMTiB, et ton « pip install » télécharge un paquet piégé sans aucune alerte. Aucune attaque n'a été signalée pour l'instant, mais c'est trivial à faire.
Un paquet piégé peut installer n'importe quoi. Porte dérobée, virus, vol d'informations en tout genre.
La situation est terrifiante !
Rien que dans l'écosystème Python, chaque installation de CPython, chaque venv, uv, tout est exposé.
Et je ne vous parle même pas de npm, pnpm, yarn, Go, Rust.
Ma stratégie de sécurité 2026 : rester chez moi et ne me connecter à Internet que depuis un FAI de confiance.
C'est quand il y a de la mer qu'on reconnaît les vrais marins...