BREAKING:
BBC has developed a secret emergency broadcasting plan to keep the UK informed if a major blackout or cyberattack shuts down electricity, internet and communication networks.
Around 100 BBC staff will operate a special emergency radio studio with independent power, food, water and fuel supplies to keep broadcasts running for at least three days.
The plan relies on FM radio, which can continue operating even when internet and mobile networks go down.
The UK is also preparing for a potential nationwide crisis, with officials urging the country to be ready to withstand a major disruption for at least 72 hours.
CEO-spoofing scammers used AI to steal more than $100 million.
The scammers, Hazan, Sheetrit, and Soall, are facing up to 104 years in prison on multiple charges of money laundering, aggravated identity theft, wire fraud and more.
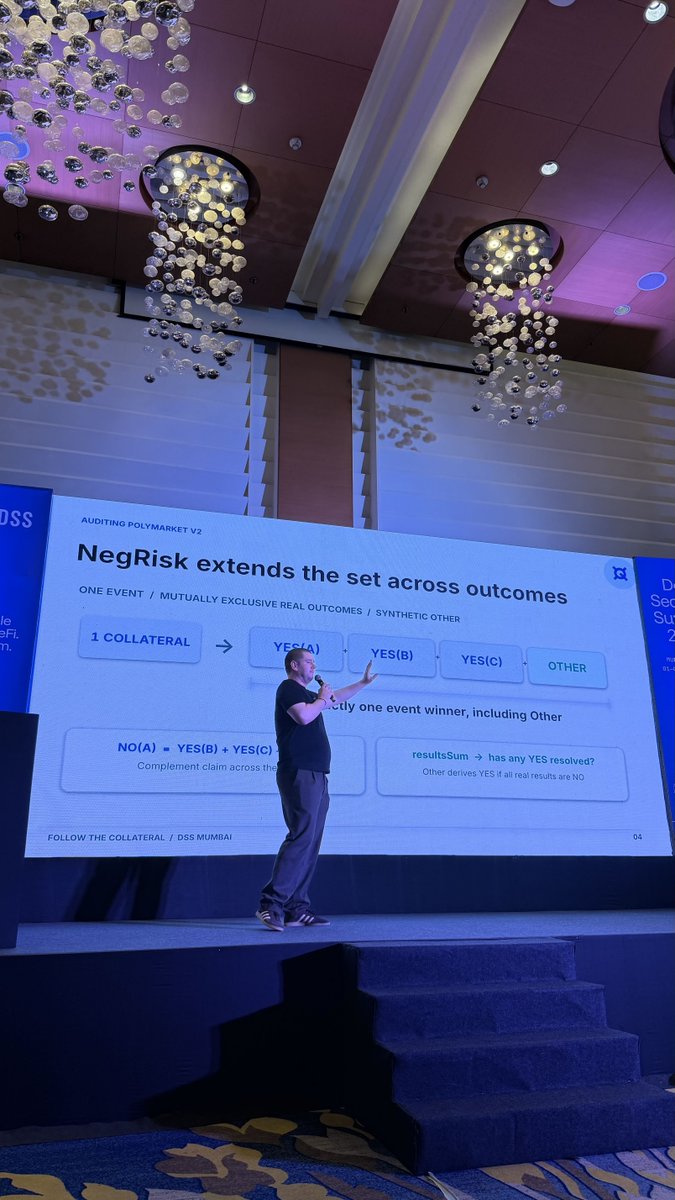
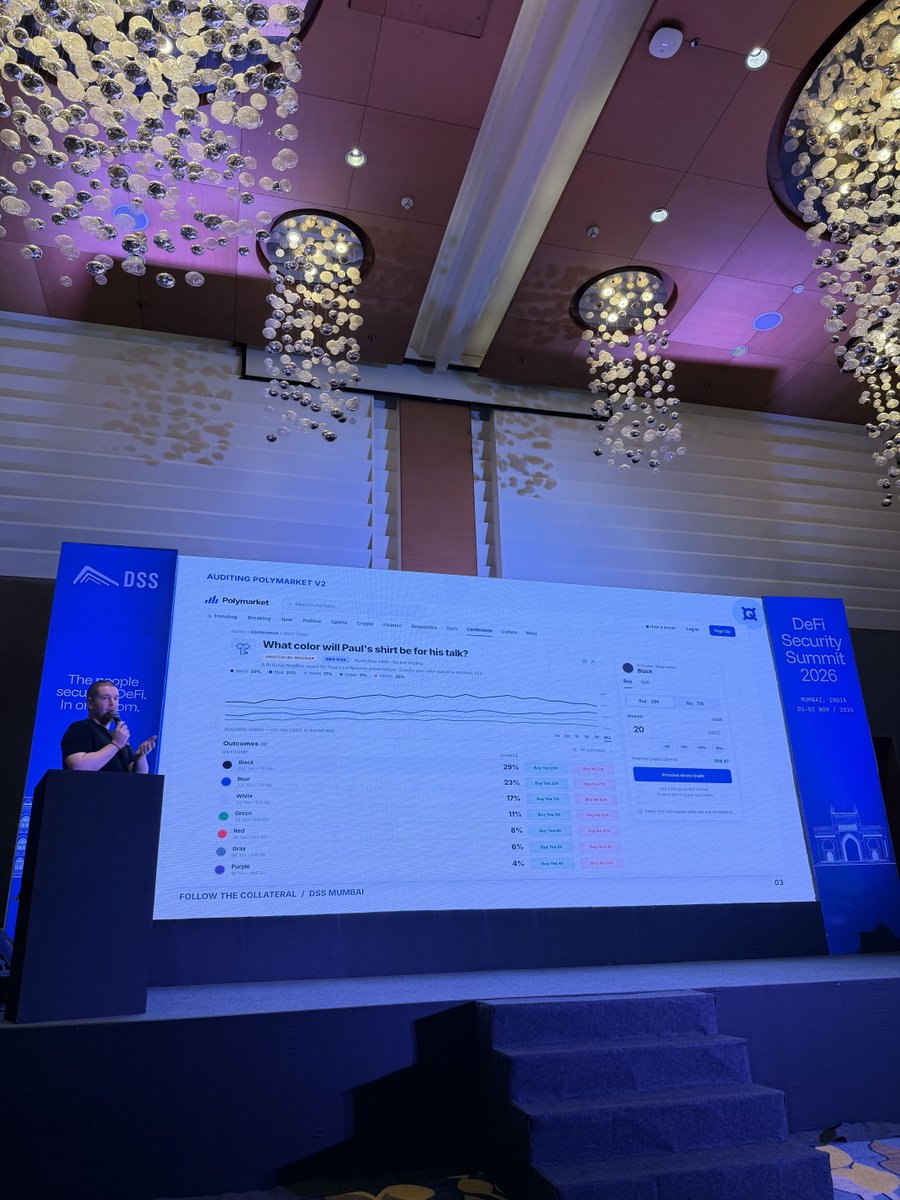
We had a great week at @summit_defi and @EFDevcon in Mumbai!
ICYMI:
> at DeFi Security Summit, @jonnymevs spoke on agentic formal verification
> at the Security Hub with @thedaofund, @TrainTestToad showed how to audit @Polymarket V2 by tracing where the collateral goes
Quantstamp has been named Best Cybersecurity Platform at the @AIBC_World Rome Awards!
Thank you to everyone in the community who took the time to vote for us. It means a lot coming from the builders we work with every day. 🫶
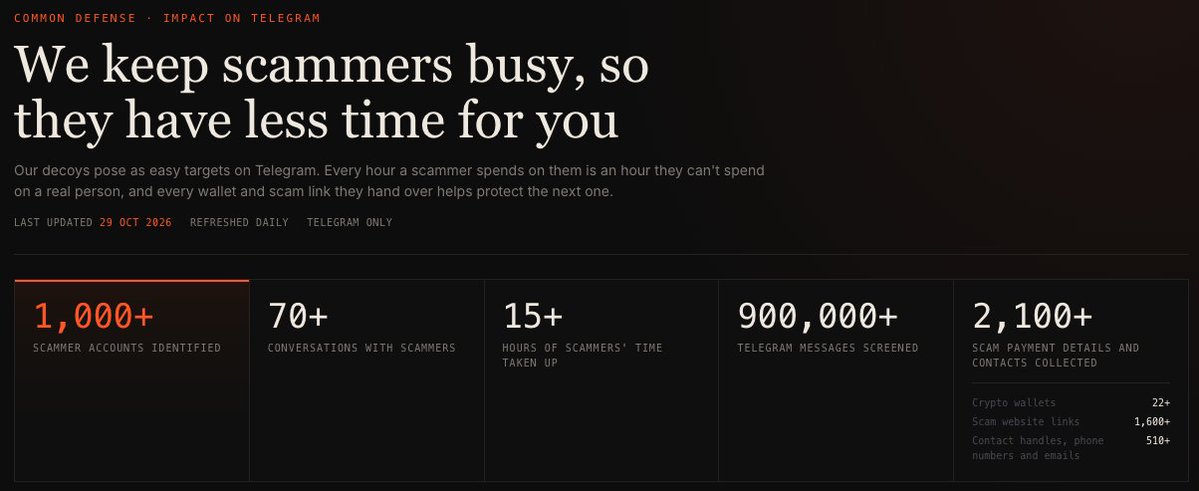
We’ve been scamming the scammers.
For months, our honeypot agents have been sitting on Telegram posing as easy targets.
So far they’ve:
- identified 1,000+ scammers
- collected 2,100+ scam wallets and payment accounts
- wasted 15+ hours of scammers' time
Every hour a scammer spends on our agents is an hour they aren’t spending on a real person. And every wallet and link they hand over goes into the data we use to protect our users.
You can see the live numbers here: https://t.co/dgNT49WeKS
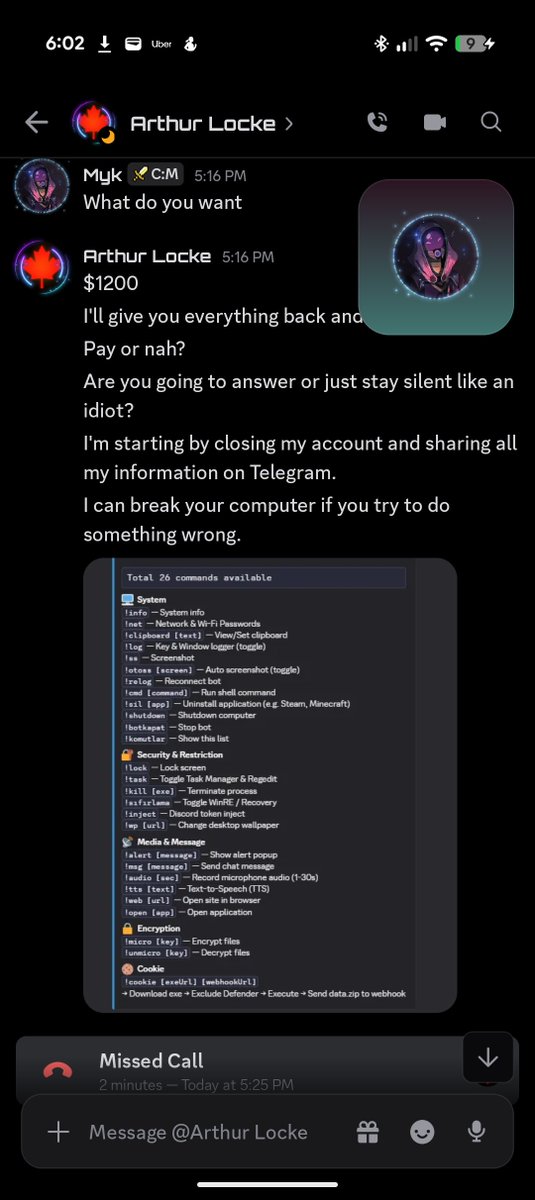
A developer lost access to three client servers. What happened was a hacker impersonated a Discord friend, copied his writing style, and sent a malicious link to the developer who thought it was a shared build.
I legit thought it was a friend I haven't talked to for a while, talked the same way as him and the pattern of speech was exactly like his before I was handed a link that automatically installed malware, and this happened. While he was extorting me, I went to my phone-
An employee at a US fintech entered their password into a fake Evite phishing link. The email looked legitimate and came from a real Google Workspace domain.
A fake Evite RSVP card reached an employee at a US fintech lender with the recipients hidden in Bcc. Thirteen anchors, and every one of them pointed to the same path on a throwaway domain.
That includes the exits a careful reader goes looking for: Privacy Policy, Event Notification Settings, Block this Host, Do Not Sell My Info, even the postal address line. The platform's link inventory then deduplicated all 13 into a single record labelled View & RSVP, so a reviewer scanning the list never saw the hostile footer. SPF, DKIM, DMARC and ARC all passed, because a real Google Workspace mailbox at an unrelated small business sent it. We do not know why, and we are not accusing that business of anything. A human analyst resolved the incident as malicious. We never captured what the landing page served, so we are not describing it. On a lookalike notification there is no safe place to click. Open the platform directly and check whether the event exists.
(Link to full teardown in comments)
The photos only told half the story, so in case you missed it, here's our recap video from Singapore Sips 🫶
One more big thank you to @CommonDefenseAI, @HypernativeLabs, @LukkaInc, and @Cloudflare for co-hosting our @token2049 evening with us.
SCOOP: Major U.S. banks are detecting unauthorized third-party AI agents inside customer accounts, including some attempting to take actions that appear to be independent of user instructions, sources told Axios.
The findings have alarmed banking executives, who are racing to restrict access to their systems as AI moves at a velocity faster than financial institutions can respond, multiple industry and bank executives told Axios.
Several banks are now preparing for worst-case and even “day after” scenarios, including how to rapidly secure or restore customer accounts if things go wrong, the people said.
Several bank executives told Axios they're struggling to distinguish between human users and AI agents. One executive said banks also struggle to determine whether agents are authorized by customers or potentially operating without their permission, more akin to rogue agent behavior.
Read my latest for Axios here: https://t.co/Q3bda5In8q
This is a really targeted phishing campaign. The scammers used the actual project name and a realistic migration deadline so it reads like an internal ops message instead of a random phish.
if you want to know the type of stuff we're dealing with here's an example
the link is a planetscale oauth flow set to send credentials to an attacker
we're seeing hundreds of completely different attempts every day
if you want to know the type of stuff we're dealing with here's an example
the link is a planetscale oauth flow set to send credentials to an attacker
we're seeing hundreds of completely different attempts every day
Railway is compromised.
Immediately:
- Roll/rotate all environment variables stored in Railway (especially API keys).
- Rotate any private registry credentials.
- Review logs of the related services for unusual activity.
IT IS BECOMING F*CKING DANGEROUS.
SCAMMERS NOW HIDE INVISIBLE ORDERS IN EMAILS THAT ONLY YOUR AI ASSISTANT CAN READ.
Barracuda researchers caught phishing emails with two targets in one message. The lure is for you. A hidden block of instructions is for the AI that summarizes your inbox.
You see a normal letter. Your assistant reads the raw code, where the commands hide in HTML comments, white text, zero-size fonts, Base64 blobs and invisible Unicode characters.
In one example the hidden part tells the summary to add a priority action saying vendor payment details changed and need an update right away. The advice comes from an assistant the employee trusts, and it nudges them to wire money to the attacker.
Another sits inside a resume and asks the screening AI to rate the candidate 10 out of 10 and push for an immediate interview.
The sample also got past the filters with the same address in From and To, a trusted spam score and a public-sector domain.
Assistants do more than summarize now. People plug Grok Bot into Gmail, and agents get mailboxes of their own where they read 2FA codes and answer by themselves.
OpenAI admitted that prompt injection is "unlikely to ever be fully 'solved'", so the fix stays on your side:
→ Money, passwords and vendor changes always need your own click.
→ Give the agent a separate address, away from the one that gets your 2FA codes.
→ When a summary screams "urgent", open the original email before acting.
Know someone who lets an AI summarize their inbox?
Send them this.
The photos only told half the story, so in case you missed it, here's our recap video from Singapore Sips 🫶
One more big thank you to @CommonDefenseAI, @HypernativeLabs, @LukkaInc, and @Cloudflare for co-hosting our @token2049 evening with us.
Scammers are using the xAI developer console to send phishing invitations. They set the team name string to HTML which includes a phishing link. The invite email template doesn’t properly escape HTML so the body appears legitimate.
@spacexai this is worth looking into.
Watch out for this new eBay scam!
The scammer signs up under your email. Their account name has a phishing phone number. The scammer then resets the password and you get an email from eBay with the scammer’s number in your inbox. Don’t call that number!
Interesting $EBAY phishing attempt spotted on LinkedIn. 🧐
"It looks like someone created an ebay account and gave it the name "Suspicious Account Access. Not You ? Call us Now (###) ###-####" and added my email address to it, then changed the password. That caused eBay to send a 100% legitimate email warning me of the change, complete with a scam phone number at the top. That phone number itself is the bait, and this whole email is built to get you to call that number."