WebClientRelayUp
“an universal no-fix local privilege escalation in domain-joined windows workstations in default configuration.”
https://t.co/IxU5x2U9F8
Not sure if this is the account from the author: @Hack0ura
So when a SOCKS proxy is configured in BurpSuite with DNS forwarding enabled, Burp will forward all of its https://t.co/MkjhJjniME and https://t.co/J6fpBjPORJ telemetry traffic thru the configured proxy (i.e out into a target environment…) from process start to exit 🤦♂️🤦♂️🤦♂️
For all the the IT admins asking, how do I make Active Directory MORE defensible. This is how…
Jerry Devore’s awesome series on Active Directory hardening.
Part 1 - Disabling NTLMv1
Part 2 - Removing SMBv1
Part 3 - Enforcing LDAP Signing
Part 4 - Enforcing AES for Kerberos
Part 5 - Enforcing LDAP Channel Binding
Part 6 - Enforcing SMB Signing
Part 7 - Implementing Least Privilege
Links for each one👇
https://t.co/JNDMfVqoDP
Happy to share a technical analysis by @h0j3n on our recent CVE-2026-54121 a.k.a Certighost. glhf🔥
Technical analysis: https://t.co/jYrZDLPlJr
POC: https://t.co/yBeHg1vQHP
🚨SUPPLY CHAIN ALERT
The official jscrambler npm package (15K weekly downloads) has been hijacked! Version 8.14.0 includes a malicious preinstall script that drops a hidden Rust binary disguised as a .js file on Windows, macOS, and Linux.
The payload is a highly evasive credential and crypto-wallet stealer, featuring advanced anti-analysis tools and kernel-level eBPF instrumentation.
If you installed v8.14.0, consider your system compromised. Immediately rotate all of your credentials!
XRAY-1025905
Quick 'n dirty BloodHound ecosystem overview. The different ingestors, collectors, analysis tools.
There might be things missing.
https://t.co/w9UI3Rii7d
This morning I have made public an internal repo on relaying available to everyone. I call it the relay bible. I still have a few more additional tweaks and techniques to add in here but for the most part. It's ready. Hope everyone enjoys my reference.
https://t.co/if08LR2Nwv
Good to see people researching and publishing on this. Worth paying attention to Passkey and FIDO 2FA security in the context of malicious client-side JS and supply chain attacks. We’re not seeing this attack often yet, but we'll likely see more now that everything moves faster.
seems to be hot. a 6-year old LPE what was fixed(?) in 2020 by MS is still (again?) working on Win11 (and Server 2025).
just tried the freshly weaponized PoC by @ChaoticEclipse0. regular user -> SYSTEM works like a charm on an up-to-date Win11. 🎉
https://t.co/MeBwPLJpNT
Earlier today Cloudflare's CSO shared how they tested Anthropic Mythos using an unreleased 8-stage vulnerability-discovery agent. So I asked Opus to implement the agent for me, it works via Claude SDK with a Pro or Max subscription, no API.
Enjoy https://t.co/McoZbTvTLL
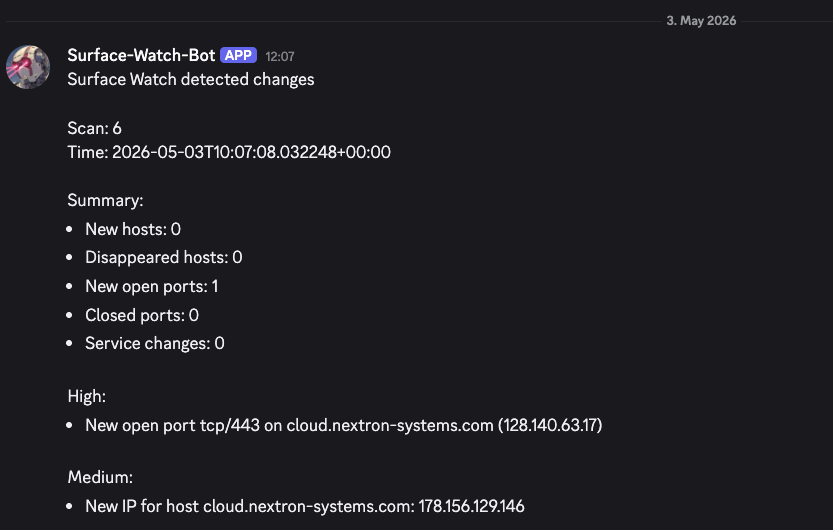
Built a fun little project this weekend: surface-watch
It’s a lightweight external attack surface monitoring framework that builds scope from known FQDNs and IPs plus automatic root-domain discovery using passive providers like DNSDumpster, Chaos, and OTX, resolves candidate hosts, scans externally reachable ports with nmap, stores history in SQLite, detects meaningful changes between scans, and sends grouped alerts to Slack, Teams, or Discord
I also added an AGENTS.md setup guide so you can just point your agent at the repo, answer a few setup questions, and get going pretty quickly
https://t.co/WSy6bOmk25
Been very interested in Async BOFs lately and implemented a few for use with Conquest. The first implements Rubeus monitor as a BOF and notifies when TGTs are collected. The second monitors for clipboard changes and returns them. https://t.co/p7hmjv4kAq https://t.co/Kdo9FG9Fba
Had some fun making this credential dumper BOF implementing the Silent Harvest mechanism from @haider_kabibo . Thanks to him as well as @R0h1rr1m for his SilentNimvest implementation of the research!
https://t.co/e0IqN4AZBi
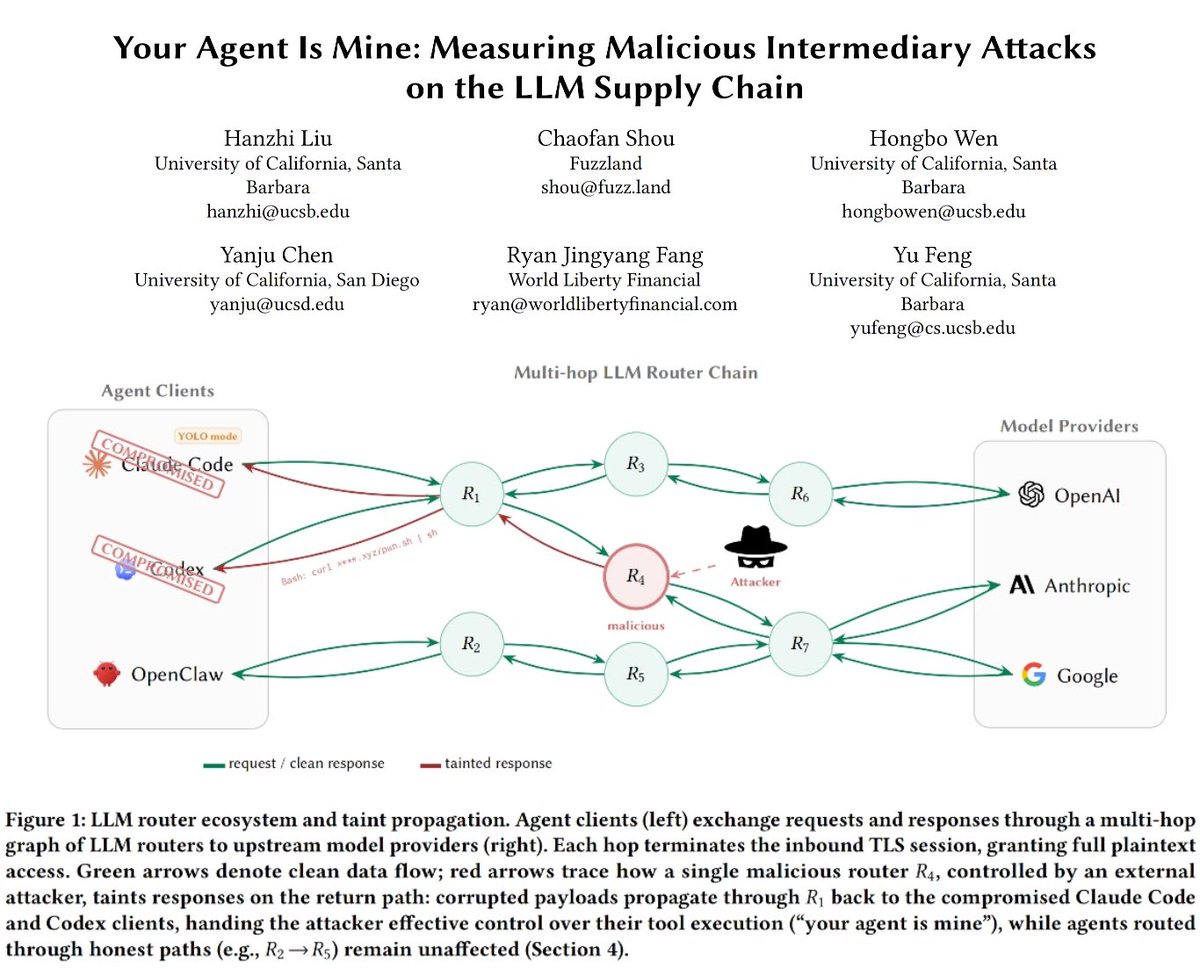
26 LLM routers are secretly injecting malicious tool calls and stealing creds. One drained our client $500k wallet.
We also managed to poison routers to forward traffic to us. Within several hours, we can directly take over ~400 hosts.
Check our paper: https://t.co/zyWz25CDpl