Lo que este tipo subió a GitHub no debería ser gratis.
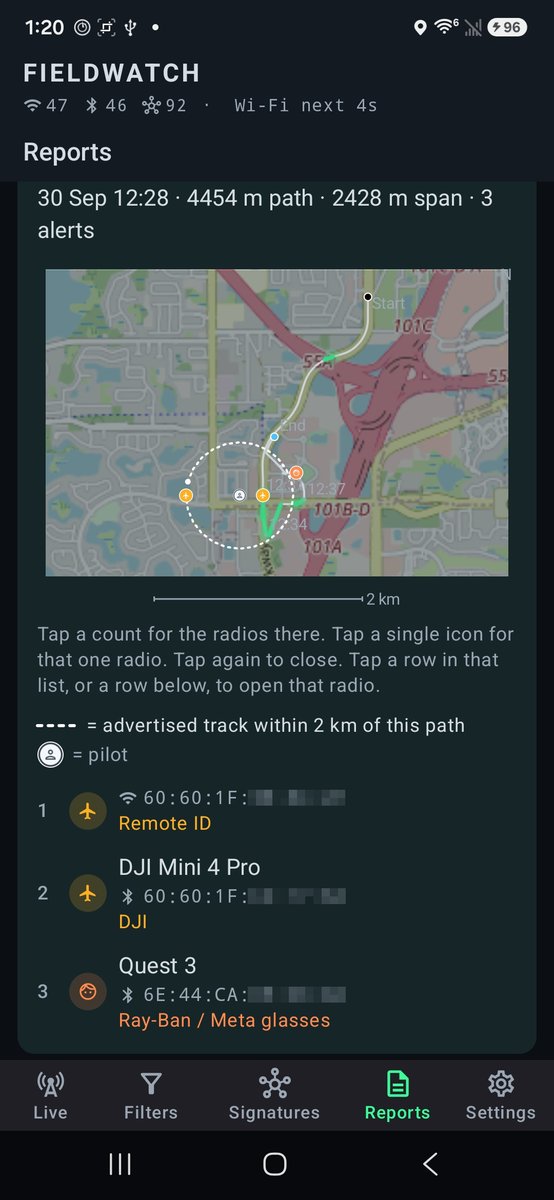
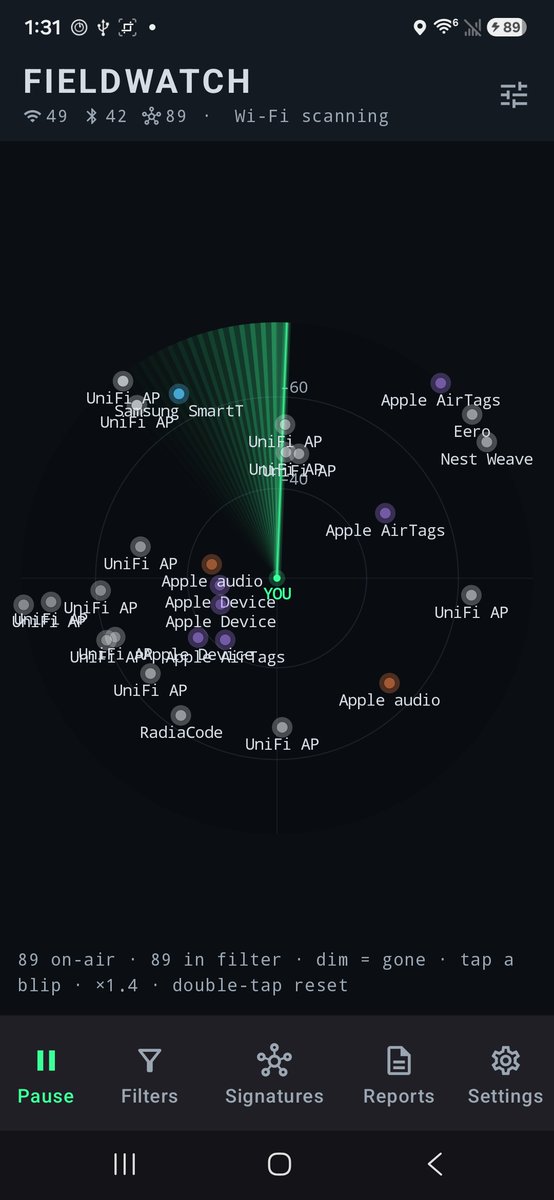
Una app que convierte tu móvil en un detector de vigilancia.
Escucha las señales Wi-Fi y Bluetooth a tu alrededor y te dice qué hay cerca:
• rastreadores escondidos
• cámaras corporales de policía
• drones, y dónde está el piloto
• gafas inteligentes de Meta grabando
• micrófonos de detección de disparos
Reconoce hasta 242 tipos de dispositivos. Y te avisa si alguno se mueve contigo.
Sin cuenta. Sin servidor. Sin internet. Código abierto.
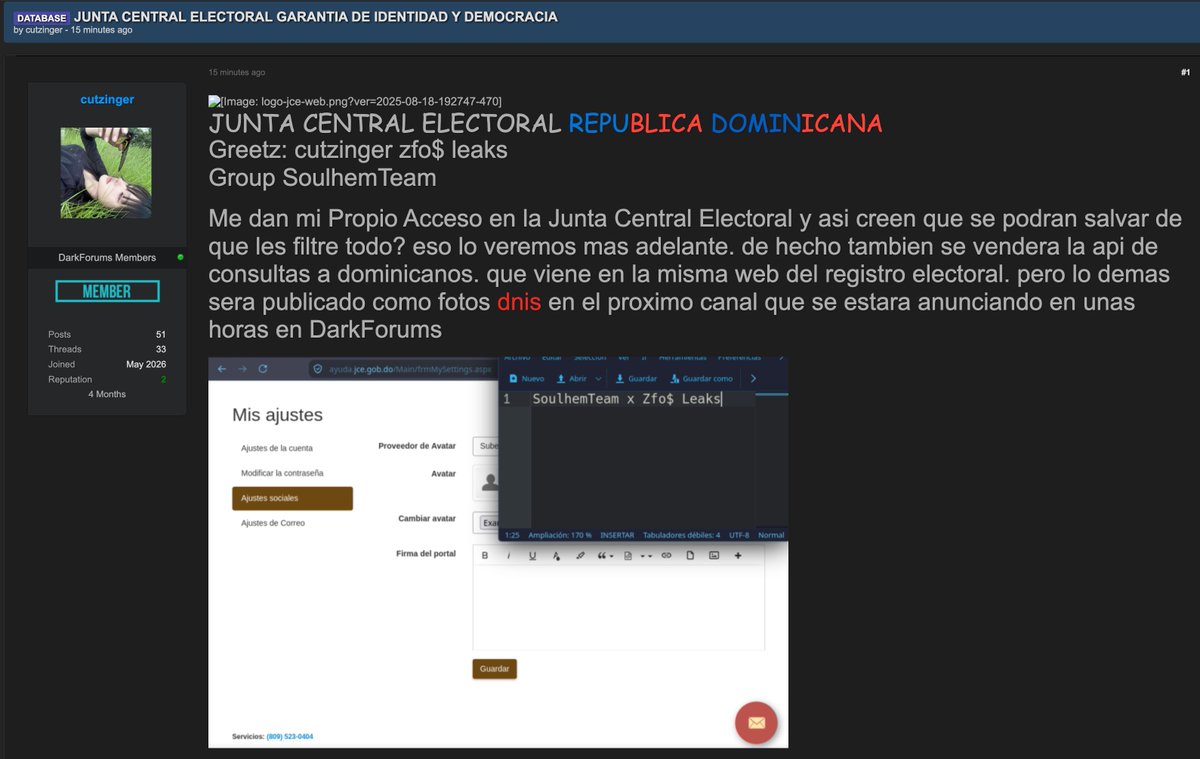
‼️DATABASE ACCESS CLAIM — JCE 🇩🇴
A DarkForums post by cutzinger claims unauthorized access to the Junta Central Electoral (JCE) of the Dominican Republic. The JCE is the country’s autonomous electoral authority responsible for organizing elections and administering electoral and civil-registration functions.
The post alleges:
• 🔐 Access to JCE systems
• 🗳️ Potential access to electoral-registration services
• 📡 An API for querying Dominican citizens is allegedly being offered
• 🪪 The actor claims additional citizen data may be published as DNI images
⚠️ These claims and the authenticity/scope of any access have not been independently verified. No personal data or access details are reproduced here.
#CyberSecurity #DataBreach #DominicanRepublic #JCE #ElectionSecurity #ThreatIntel
🚨🇩🇴 INAP Virtual Dominican Republic Dataset Allegedly Leaked
A dataset allegedly belonging to INAP Virtual in the Dominican Republic has been shared on a forum by SoulhemTeam and zfo$Leaks.
Samples included in the post show records containing information such as country, city, time zone, gender, user IDs, and course-related details.
One visible record references a public administration quality management course and identifies Santo Domingo as the associated city.
These claims have not been independently verified.
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
🚨 🇩🇴 Dominican Republic National Police complaint system allegedly compromised
⠀
The actor "jarol1488" claims to have breached the police complaint management system known as SPGD and extracted records spanning 2016 through September 2026.
⠀
The scale claimed is significant: more than 3.2 million lines of complaint data and another 2 million lines containing Base64-encoded photographs.
⠀
A posted sample appears to include names, national identification numbers, dates of birth, phone numbers, addresses, photographs, incident details, and police case information. If authentic, the exposure could affect complainants and other people identified in police reports.
⠀
The actor published an updated sample and is directing interested parties to make contact.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
⚠️ CRITICAL PREVENTIVE ALERT 🇩🇴 ⚖️: ALLEGED MASS LEAK OF OVER 4.5 MILLION RECORDS FROM THE DOMINICAN REPUBLIC JUDICIARY
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / THREAT ACTOR: JAROL488 / DATE: SEPTEMBER 26, 2026]
Centralized cyber-intelligence monitoring has detected a new post on underground forums and channels, attributed to the threat actor "jarol488." The alert announces the release and public availability of a database containing 4,563,652 lines of information linked to the Dominican Republic Judiciary.
It is strictly noted that the veracity of this breach and the authenticity of the records have not been officially confirmed by Dominican judicial authorities. The definitive scope of the files remains unconfirmed.
Threat Actor: jarol488.
Victim / Affected Entity: Dominican Republic Judiciary (https://t.co/644vT2ugLQ).
Sector: ⚖️ Government / Justice, Courts, and State Legal Registries.
Target Country: Dominican Republic 🇩🇴.
Reported Data Volume: 4,563,652 lines of structured information.
🛡️ TECHNICAL PREVENTIVE CONTAINMENT RECOMMENDATIONS (SOC / CSIRT / JUDICIARY)
Forensic Audit of Servers and Repositories: IT teams within the Dominican Republic Judiciary must immediately isolate and audit database servers and public inquiry portals to determine the initial extraction vector. Link Verification and Reporting: Request the immediate blocking and removal of the external download repository (gofile. io) associated with the leak to mitigate the spread of the records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Quickly check your security at: https://t.co/QZhWp0kFrO
Quotes and services: https://t.co/sx3BM5zbnK
#Cybersecurity #ThreatIntel #DataLeak #Judiciary #DominicanRepublic #JusticeSecurity #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #SecurityAlert
🚨 Ransom group "Titan" publishes "Grupo Hospifar S.R.L." - Dominican Republic 🇩🇴
📍 Location: Santo Domingo, Dominican Republic
🏢 Industry: Healthcare & Medical Supplies Distribution
🔗 Website: hospifar[.]com
Founded in 1993, Hospifar imports, represents, and distributes pharmaceutical, hospital, and medical products nationwide. The company also provides project planning, equipment installation and maintenance, training, and logistics, and supplies state contracts.
🚨🇩🇴 Dominican Republic telecom, government, and education infrastructure allegedly exposed
A forum actor using the handle "TerroahOver" claims to have identified exposed network infrastructure associated with multiple organizations in the Dominican Republic. The post is signed "TerroahGroup."
⠀
The actor lists 3,140 items of allegedly compromised information, without clarifying whether this figure represents systems, services, or individual records.
⠀
Claimed exposures include:
⠀
• Network administration: exposed remote management interfaces for routers and gateways
• Internal information: domain and NTLM-related information disclosure involving Microsoft SQL Server
• Database services: databases allegedly exposed without IP filtering
• Web infrastructure: exposed web servers and control panels
⠀
Organizations named in the post include:
⠀
• Compañía Dominicana de Teléfonos
• Altice Dominicana (Tricom)
• Estrela Telecom
• Instituto Tecnológico de Santo Domingo (INTEC)
• Ministerio de Obras Públicas y Comunicaciones (MOPC)
• Importadora Tropical S.A.
• Alta Gracia Project Holding
⠀
The actor warns that the named organizations could face attacks if the alleged issues remain unresolved. The post includes screenshot attachments, but the material shown does not establish successful intrusion or data theft.
⠀
This claim is currently unverified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
⚠️ TARGETED PREVENTIVE ALERT 🇩🇴: LEAK OF BASIC DATA ON 1.84 MILLION DOMINICAN REPUBLIC CITIZENS
[STATUS: MALICIOUS ACTIVITY (SOURCE UNCONFIRMED) / SOURCE: CYBERCRIME FORUMS (DARKFORUMS) / DATE: SEPTEMBER 20, 2026]
Centralized cyber-intelligence monitoring has detected a post on underground forums (DarkForums) in which the threat actor "SP500" announces the distribution (free leak) of a database containing basic information on 1,845,072 individuals in the Dominican Republic.
Threat Actor: SP500.
Victim / Affected Entity: Citizens of the Dominican Republic.
Sector: 🏛️ Civil Data / Citizen Identity.
Target Country: Dominican Republic 🇩🇴.
Reported Data Volume: 1,845,072 individual records.
Distribution Vector: Public download link on gofile .io (file size: 544 MB).
🔍 TECHNICAL BREAKDOWN AND STRUCTURE
Based on the JSON-format sample published by the actor, the following personal data structure is observed:
Full Name (fullName): Documented example of an affected citizen.
Document Number (documentNumber): National ID card number (Cédula).
Date of Birth (birthDate): Recorded in standard format.
Empty Fields: The attacker notes that fields corresponding to email, physical address, password, and phone number are largely null, limiting the primary leak to names, ID numbers, and dates of birth.
🛡️ TECHNICAL PREVENTIVE CONTAINMENT RECOMMENDATIONS (SOC / CSIRT)
Identity Impersonation Monitoring: Financial and service institutions in the Dominican Republic must be on alert for potential attempts to open accounts or validate identities using the ID numbers and dates of birth exposed in this free leak containing nearly 1.8 million records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#Cybersecurity #ThreatIntel #DataLeak #DominicanRepublic #SP500 #FreeLeak #IdentityTheft #InfoSec #CyberAlert #VECERT #SOC #CSIRT
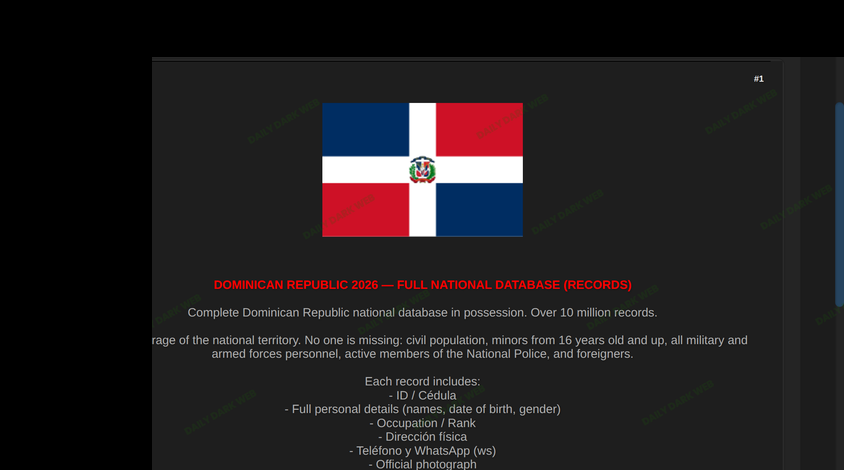
🇩🇴 DOMINICAN REPUBLIC NATIONAL DATABASE SALE CLAIM (~10M+ RECORDS)
A threat actor is advertising what they claim is a full Dominican Republic 2026 national database, described as over 10 million records with nationwide coverage.
The underground listing alleges:
* Complete national-territory coverage
* Civil population (from age 16+), military/armed forces, National Police, and foreign residents
* Per-record fields including ID/cédula, names, DOB, gender, occupation/rank, physical address, phone/WhatsApp, and official photograph
* Material packaged as a .db file
⚠️ Analyst Note:
Large “full national database” listings are frequently recycled, incomplete, inflated, or assembled from older civil registries and prior underground circulation. Volume, field completeness, freshness, sample authenticity, and any link to a real compromise of Dominican national-ID or registry systems are unverified from the listing alone.
We assess this as an unverified threat-actor claim involving alleged Dominican Republic national identity/registry data, NOT confirmation of a compromise of Dominican government identity infrastructure.
If authentic and non-public, national-ID, contact, and photo data at this scale could support identity fraud, phishing, and large-scale profiling.
#DDW #DarkWeb #DominicanRepublic #DataBreach #PII #ThreatIntelligence #CyberSecurity
⚠️ TARGETED PREVENTIVE ALERT 🇩🇴: ALLEGED MASS EXFILTRATION OF THE DOMINICAN REPUBLIC'S NATIONAL DATABASE (OVER 10 MILLION RECORDS)
[STATUS: UNCONFIRMED; VISIBLE EVIDENCE EXISTS BUT NOT YET VERIFIED / SOURCE: CYBERCRIME FORUMS (DARKFORUMS) / DATE: SEPTEMBER 19, 2026]
Centralized cyber-intelligence monitoring has detected a high-risk post on underground forums (DarkForums) in which the threat actor "rannark" claims to possess and be leaking the Dominican Republic's entire national database.
The attacker asserts that the database covers the entire national territory and includes the civilian population, minors (aged 16 and up), military personnel, active members of the National Police, and foreign residents. It is strictly noted that the magnitude and authenticity of this exfiltration
have not been officially confirmed; while there is visible evidence documented in the file—showing an electronic sales interface, an SQLite database with over 10.2 million records, and ID photos of individuals in military uniforms—the actual intrusion into government systems remains unconfirmed.
Threat Actor: rannark
Victim / Affected Entity: Dominican Republic (Civil Registry and National Data).
Sector: 🏛️ Government / National Security / Civil Data
Country: Dominican Republic 🇩🇴.
Claimed Data Volume: Over 10.2 million records (10.2M+ TOTAL RECORDS).
Data Format: 1 ZIP file (1 ZIP ARCHIVE) containing an SQLite database.
Exposed Data: Official Identity Document (Cédula). Full names and dates of birth. Occupation / Military Rank. Exact physical address. Direct phone and WhatsApp numbers. Official high-quality photographs (Official HQ Photographs).
🛡️ TECHNICAL RECOMMENDATIONS FOR CONTAINMENT AND PREVENTION (SOC / CSIRT / NATIONAL SECURITY)
Immediate Investigation and Data Cross-Referencing: The National Cybersecurity Center (CNCS) of the Dominican Republic and the Central Electoral Board (JCE) must immediately obtain samples of this data to verify its authenticity and cross-reference it with official records, in order to determine the source of the breach (whether the main civil registry or a secondary government database).
Alert to Financial Institutions: Issue an urgent bulletin to all banks and Fintech institutions in the country to raise security awareness and implement Live Biometric Verification (Liveness Detection) requirements for all sensitive transactions and the opening of new accounts.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#Cybersecurity #ThreatIntel #DataLeak #DominicanRepublic #rannark #DataBreach #NationalDatabase #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #AllegedIncident #VisibleEvidence #SecurityAlert
"La Tesorería Nacional de la República Dominicana aparece mencionada en una alerta de ciberinteligencia publicada el 17 de septiembre de 2026 por la firma VECERT. Según ese informe, el actor identificado como xurl404 habría incluido el portal https://t.co/ySqNOwRQ3t entre cientos de sitios gubernamentales y educativos de varios países en los que, según afirma, logró cargar archivos maliciosos (webshells o archivos de prueba) mediante una campaña automatizada.
El propio actor presentó cifras de su herramienta: en poco más de seis minutos habría examinado 282 servidores y comprometido 179, depositando archivos con un patrón de nombre que comienza por “16aa97…” en carpetas habitualmente escribibles, como /images/, /media/ o /cache/.
La Tesorería Nacional figura en la lista de entidades gubernamentales citadas, junto con organismos de México, Ecuador, Brasil y otros países.Hasta este momento no existe confirmación oficial ni periodística independiente de que se haya producido un robo de datos, un cifrado de sistemas, una defacement visible o una interrupción de los servicios de la Tesorería. El sitio institucional permanece en línea y ofrece sus trámites habituales (consulta de pagos y libramientos, SIRITE, gestiones administrativas).
Tampoco se ha publicado el nombre exacto del archivo que, según el actor, se habría subido a ese dominio, ni un pantallazo que lo muestre de forma inequívoca.VECERT basa su alerta en monitoreo de canales clandestinos y en un tablero interno de pago; la información detallada no es de acceso público. Un incidente distinto reportado el mismo día en la República Dominicana —relacionado con el sistema de Gestión de Denuncias (SPGD) y atribuido a otro actor— no está vinculado a la Tesorería Nacional.En síntesis: la institución fue incluida en una lista de presuntos éxitos de una campaña masiva de carga de archivos en sitios web.
No hay, por ahora, evidencia pública de impacto operativo o de filtración de información financiera o ciudadana proveniente de esa entidad. Corresponde a las autoridades competentes (OGTIC, equipos de ciberseguridad del Ministerio de Hacienda y de la propia Tesorería) verificar internamente si existió algún archivo no autorizado y, de ser así, retirarlo y auditar los registros."
⚠️ TARGETED PREVENTIVE ALERT 🇩🇴: ALLEGED CRITICAL DATA EXFILTRATION FROM THE DOMINICAN REPUBLIC NATIONAL POLICE COMPLAINT MANAGEMENT SYSTEM (SPGD)
[STATUS: UNCONFIRMED; EVIDENCE VISIBLE BUT NOT VERIFIED / SOURCE: CYBERCRIME CHANNELS / DATE: SEPTEMBER 17, 2026]
Centralized cyber-intelligence monitoring has detected the posting of a download link on underground channels that allegedly contains records from the Dominican Republic National Police's Complaint Management System (SPGD). The post offers a direct download of a file containing 10,000 lines of data via the temporary hosting platform Gofile.
It is strictly noted that this has not been officially confirmed; while there is visible evidence (such as the posted link and the official image attached by the threat actor), the authenticity of the records, their currency, and the extent of the compromise of police servers remain unverified.
🛡️ PREVENTIVE TECHNICAL CONTAINMENT RECOMMENDATIONS (SOC / CSIRT)
Urgent Access Audit (SPGD): The Dominican National Police technology department must immediately audit the SPGD audit logs to identify which user or IP address recently performed mass queries or exported 10,000 records.
🖥️ CENTRALIZED THREAT MONITORING SYSTEM
Intelligence System: https://t.co/wk9bZJ2Nli
Monitoring Console: https://t.co/5LuqwzYuS6
#Cybersecurity #ThreatIntel #DataLeak #DataBreach #DominicanRepublic #NationalPolice #SPGD #PublicSecurity #Extortion #InfoSec #CyberAlert #VECERT #SOC #CSIRT #Unconfirmed #AllegedIncident #VisibleEvidence #SecurityAlert
🚨🇩🇴 Claro Dominican Republic dataset containing 2.8M+ customer records allegedly leaked
⠀
Claro is a major telecommunications provider in the Dominican Republic, offering mobile, internet, television, and other communications services to consumers and businesses.
⠀
A forum actor using the handle jarol1488 claims to have breached Claro’s systems in the Dominican Republic and obtained a dataset containing information tied to 2,889,256 customers.
⠀
Claimed exposed data includes:
⠀
• Customer identification numbers
• Mobile phone numbers
• Subscription records
• SIM / ICCID identifiers
• Service and account status
• Plan categories and descriptions
• Activation dates
• Billing cycle information
• Release dates
• Mobile validation status
• Internal subscription and plan identifiers
⠀
The actor published sample records showing customer identifiers alongside multiple mobile subscriptions, phone numbers, SIM-related data, account status, and prepaid plan information.
⠀
The breach claim, record count, authenticity of the dataset, and full scope of the exposed customer information have not been independently verified.
⠀
💥 No delays. No guessing. No redactions. Get the intel threat actors see, the moment they post it. https://t.co/281Qjc6p2J
El tradecraft de infosec ya no vive en la cabeza del operador.
Ahora lo carga un agente.
SpecterOps soltó el primer marketplace de verdad:
79 skills. 22 agentes. 26 plugin families.
BloodHound. Cobalt Strike. Outflank. Mythic. Ghidra. Binary Ninja. Ghostwriter. Recon. AppSec. C2. Reverse engineering. Windows, macOS y Linux.
Y no: esto no es para “el red teamer con ChatGPT”.
Investigadores de vulnerabilidades:
review de código, análisis de parches, 1-days y (si hay criterio detrás) acelerar caza de 0-days. El agente deja de adivinar y empieza a seguir un procedimiento.
Reverse engineers y malware analysts:
el binario ya no entra a un chat vacío. Entra a un workflow con tooling, referencias y criterios de done.
Blue teams y detection engineers:
por fin puedes emular el mismo tradecraft que el atacante va a automatizar. La pregunta ya no es “qué TTP usó un humano”. Es qué telemetría sobrevive cuando el operador también es un agente.
DFIR y threat intel:
esto es el preview de lo que el adversario va a empaquetar después. Conviértelo en playbook antes de que te lo encuentres en un incidente.
Red teamers:
attack paths, recon, C2 y simulación ya no son “arte de operador”. Son skills reutilizables, revisables e instalables.
La diferencia con el ruido de esta semana:
todo el mundo está instalando skills a ciegas, como extensiones random en 2018.
Esto no es un pack de prompts.
Es conocimiento de practitioners, con prerrequisitos, dependencias y lifecycle. Si no está revisado, está incubando. No se vende como magia.
Un prompt resuelve el problema una vez.
Una skill lo resuelve cada vez que el agente se sienta.
Repo:
https://t.co/zIURUZ0Eba
codex plugin marketplace add SpecterOps/skills
Every OSINT investigator needs the right operating system!
Is Tsurugi Linux the best OS for open source intelligence investigations?
In this article, we break it down from the hacker perspective:
https://t.co/ZQWTFJNdSE
Generates 67 malicious PDF test files designed to expose SSRF, XSS, XXE, and credential theft vulnerabilities in PDF parsers and web applications.
https://t.co/oc0IxjrMo1