🚨We released an ESXiArgs ransomware recovery script on GitHub to allow organizations to attempt recovery of virtual machines affected by the ESXiArgs ransomware attacks: https://t.co/cXpP1m03yw #StopRansomware
🚨We released an ESXiArgs ransomware recovery script on GitHub to allow organizations to attempt recovery of virtual machines affected by the ESXiArgs ransomware attacks: https://t.co/cXpP1m03yw #StopRansomware
Microsoft has discovered Raspberry Robin activity establishing its role in a complex, interconnected malware ecosystem that facilitates human-operated ransomware. Our latest blog details active operations and links to other malware and threat actors: https://t.co/Wm5nH3UQp9
If you have secrets in PowerShell scripts, at the very least, log in with the account that will be running the script and do the following:
Get-Credential | Export-CliXml -Path $env:USERPROFILE\creds.xml
In your script:
$creds = Import-CliXml -Path $env:USERPROFILE\creds.xml
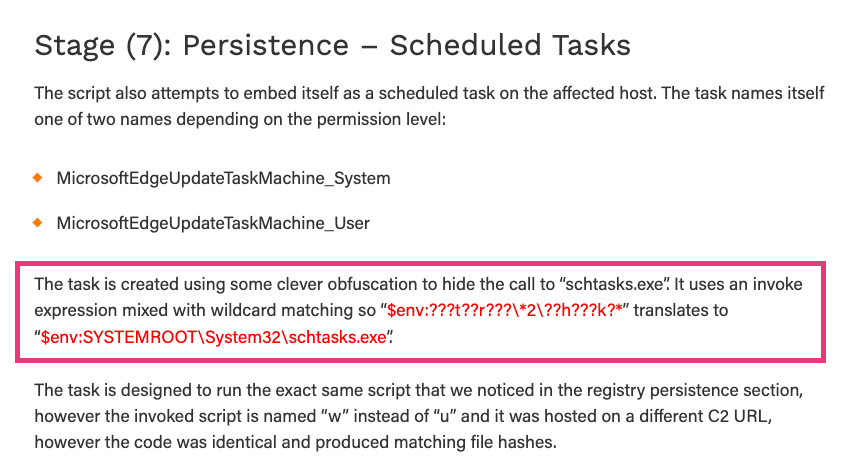
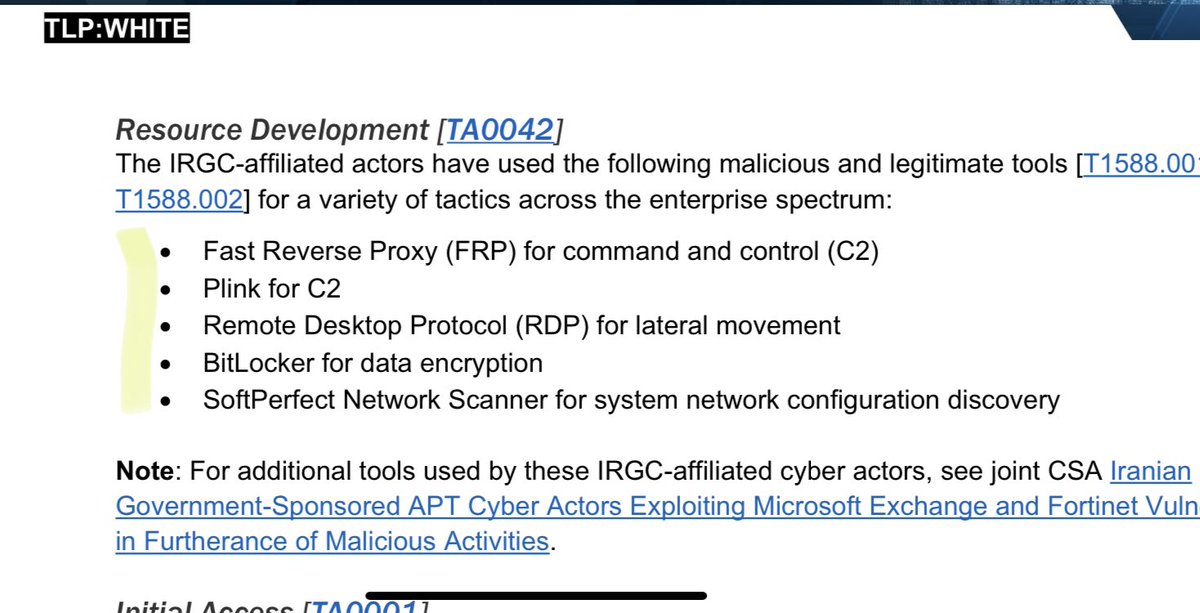
Evading the AV by using legitimate tools — from C2 tunneling, to discovery, data encryption, exfiltration and persistence — a more and more common pattern
https://t.co/3txc9m7WWP
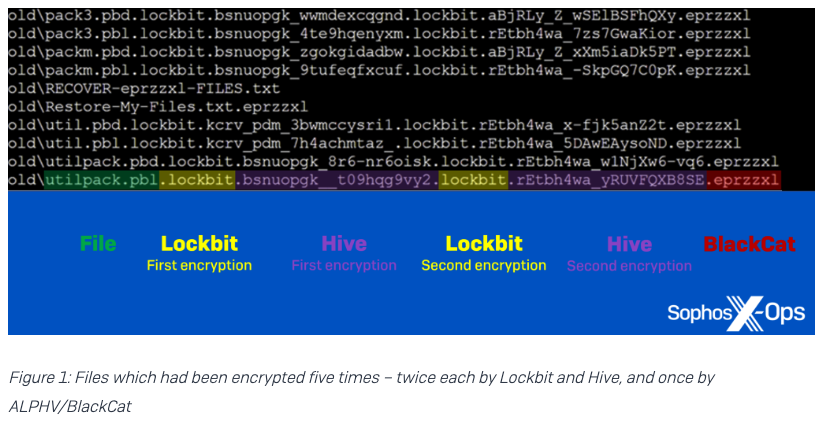
3 attackers, 2 weeks – 1 entry point...
Lockbit, Hive, and BlackCat attack an automotive supplier in this triple #ransomware attack.
After gaining access via RDP, all three threat actors encrypted files, in an investigation complicated by event log clearing and backups.
1/17
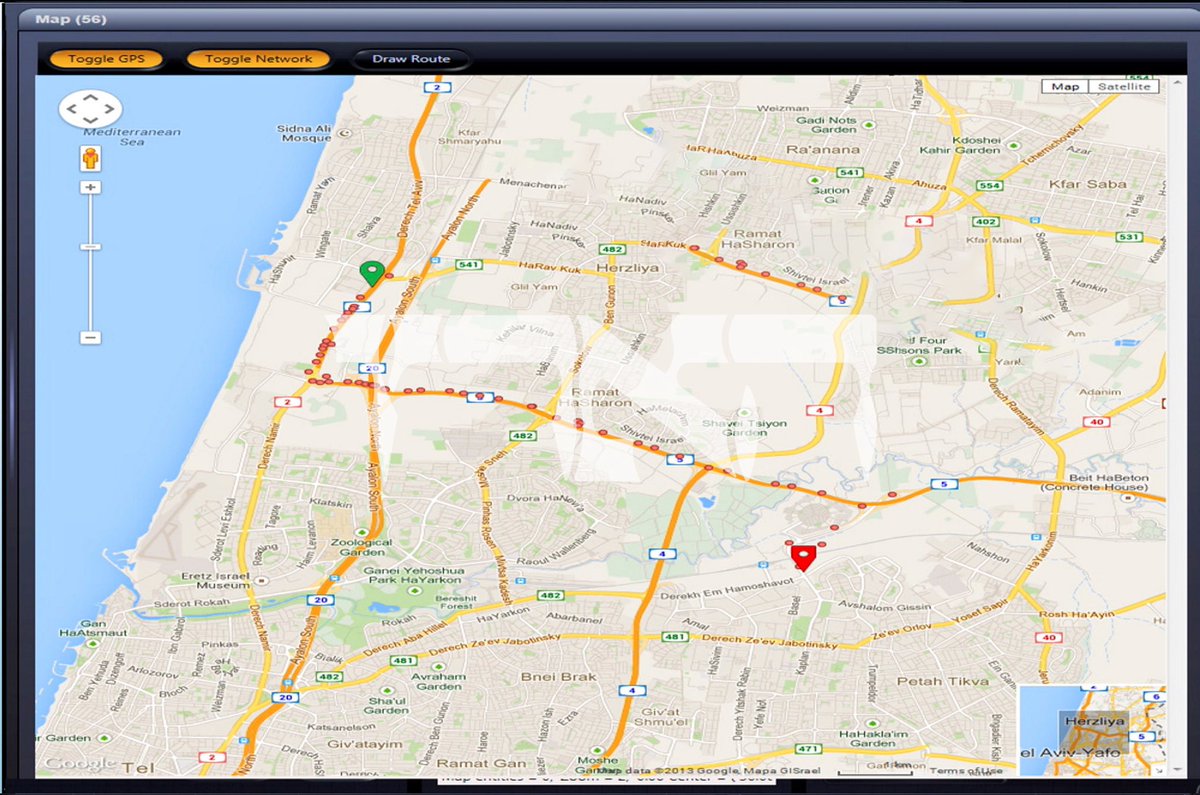
Reporter @omerbenj has obtained screenshots from early versions of the infamous Pegasus android spyware.
Pegasus, developed by Israeli firm NSO group, has been used by various organizations to spy on individuals.