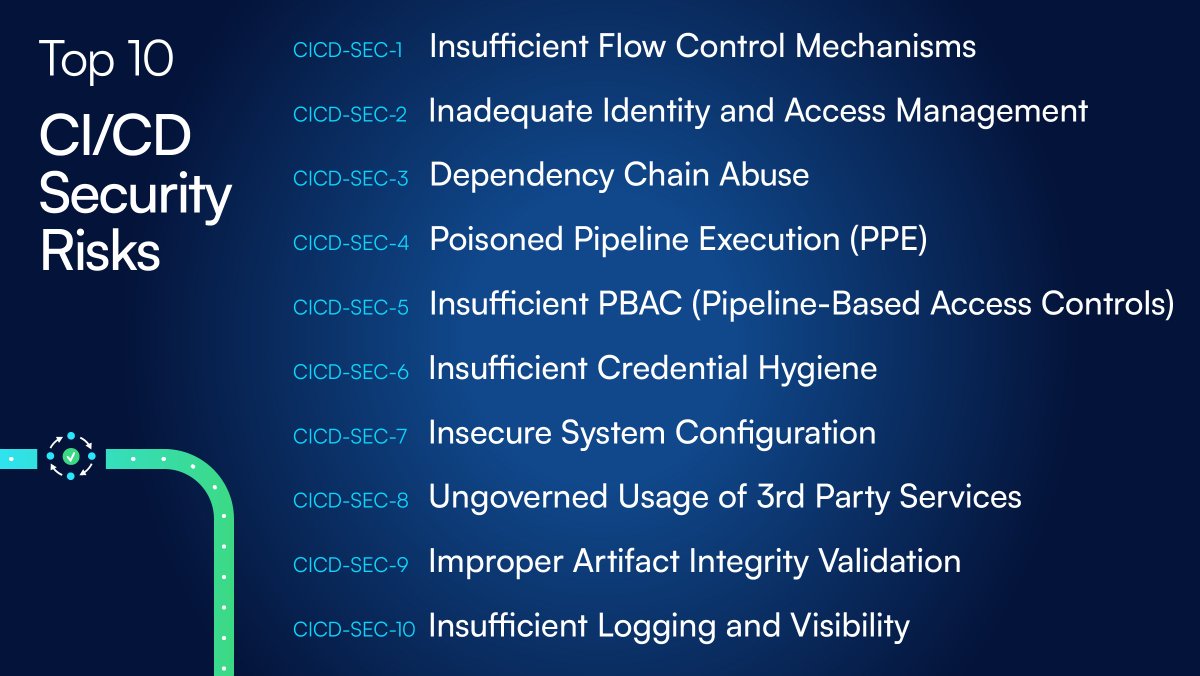
1/13 כשאנחנו נאבקים על הזמנת רכב חדש או פלייסטיישן, התירוץ על ״בעיות בשרשרת האספקה״ נזרק לאויר. יזם סייבר שמע את התירוץ ורץ להקים חברה. הקרב העמוס על הגנת סייבר לשרשרת האספקה🥊
⚠️ GitHub Org Identity Management Risks
When not using SSO
* User personal emails could be compromised
* IdP removal does not remove from GH org
Deactivating user in IdP prevents GitHub website auth- PATs & SSH keys still work
@omer_gil@yaronavital
https://t.co/IaaeVUuofn
This doesn't push my agenda of hating on Jankins but it's a good in-depth analysis of a few CI tools and how they handle creds.
https://t.co/OEoOZiYjO4
Great blog post by @TupleType about credential hygiene risks in engineering environments, with comparison of the different security solutions offered by the main vendors - GitHub Actions, CircleCI, Jenkins and GitLab CI/CD.
https://t.co/s0Q21aqdFr
. @Owasp_DevSlop is going live tomorrow with Omer Gil & Daniel Krivelevich from @cider_sec to discuss the "Top 10 CI/CD Security Risks" initiative.
SET YOUR REMINDER! ⏰ https://t.co/6vRSg9ILYf
Episode sponsor: @datadoghq
I re-read CI/CD top10, I would like to introduce their new term. It's the PBAC(Pipeline-Based Access Controls). Source code management like GitHub and CI/CD has different security aspects to each branch and step. [🧵1/2] https://t.co/T5fGLqM2Qj #Top10CICD
We are airing our eighth and final Episode in Season 3, this season is dedicated to #applicationsecurity, our guest for the show is @Dkrivelev Co-Founder and CTO of @cider_sec
https://t.co/ih0p36ZOEM
🗡️ Exploiting Jenkins build authorization
Jenkins default settings assign every build to “run as SYSTEM" 😱
To harden, use the “Authorize Project” and “Role-Based Authorization Strategy” plugins
By @TupleType
https://t.co/cjo7NxX9Te
Exploiting Jenkins build authorization.
A default configuration we often see unchanged in production environments causes all jobs to run with the highest privileges
https://t.co/rxUcE0ix5T