@GiantessVivi@SaltyySavage_ But it doesn't actually bring more players lol. Because it gets stale and boring once you successfully peacefully loot up. With no incentives to actually keep repeat farming because you no longer are risking gear
The guy who complains about George Soros has now given more money to candidates JUST this midterm election than Soros has donated in the past 10 years.
We had a Linux server that showed two successful SSH logins from an external IP overnight.
The strange part was that there were no failed password attempts before them.
The attacker got in cleanly.
So I checked the SSH logs properly.
Both sessions said:
Accepted publickey
That meant we were not dealing with a guessed password.
I pulled the fingerprint from the logs and compared it with the keys in:
/home/deploy/.ssh/authorized_keys
There was only one key there.
And it matched.
The comment on the key was:
deploy@old-build
That name sounded familiar, so we checked our records.
The build server it belonged to had been retired months ago.
But nobody had removed its SSH key from this production server.
I checked the timestamp on authorized_keys.
The key had been sitting there since November 2025.
So this was not some new persistence the attacker had just created.
It was an old trust relationship we had forgotten about.
That was actually worse in a different way.
I checked the login history and confirmed both sessions came from the same external IP.
Then I looked for files touched during those sessions.
A backup copy of the application’s .env file had been created under /opt/api/.
That immediately raised another concern because environment files often contain things like database credentials, API keys and application secrets.
At that point we disabled the deployment account, removed the stale key, rotated the application secrets and started checking every other server that might still trust the same old build key.
The lesson from this one was simple.
Not every compromise starts with malware.
Sometimes the attacker just finds a credential or key that your own environment forgot existed.
Passwords expire.
Employees leave.
Servers get retired.
But SSH keys can quietly sit in authorized_keys for years if nobody is actually reviewing them.
That is why key rotation and access reviews matter.
The attacker did not need to break SSH.
We had already left the door open.
Funnily enough, Toph bent sand on her first attempt. She used is to strengthen her stance while holding up the library and also to attack the Sand Benders. But because she couldn't see, her attacks were useless. Toph struggled because of her disability, not because it's hard.
So let met get that straight: paying a wealth tax is impossible (“billionaires have no liquidity”, “it would be taxing unrealized gains”, “their wealth is virtual”) but paying half a billion to influence elections is possible. Did I understand well?
I was so excited for KH3 when I was younger I had a dream of fighting Elsa in her ice palace, she dropped icicles and you had to use Firaga on her and everything, I wanted that to be real so bad
You don't even get to go inside the fucking palace in the final game
@uiulex This is unironically one of her best builds and people will tell you to play like this. Personally I don't like kingdom hearts like this which is why I don't like the command deck games as much but I mean
@ryorekuiemu GTA devs have already gotten their money even if a single copy is never actually sold and gta is a multi console title and has a $ dollars in pre orders. Even with the game being leaked it has already sold exceptionally
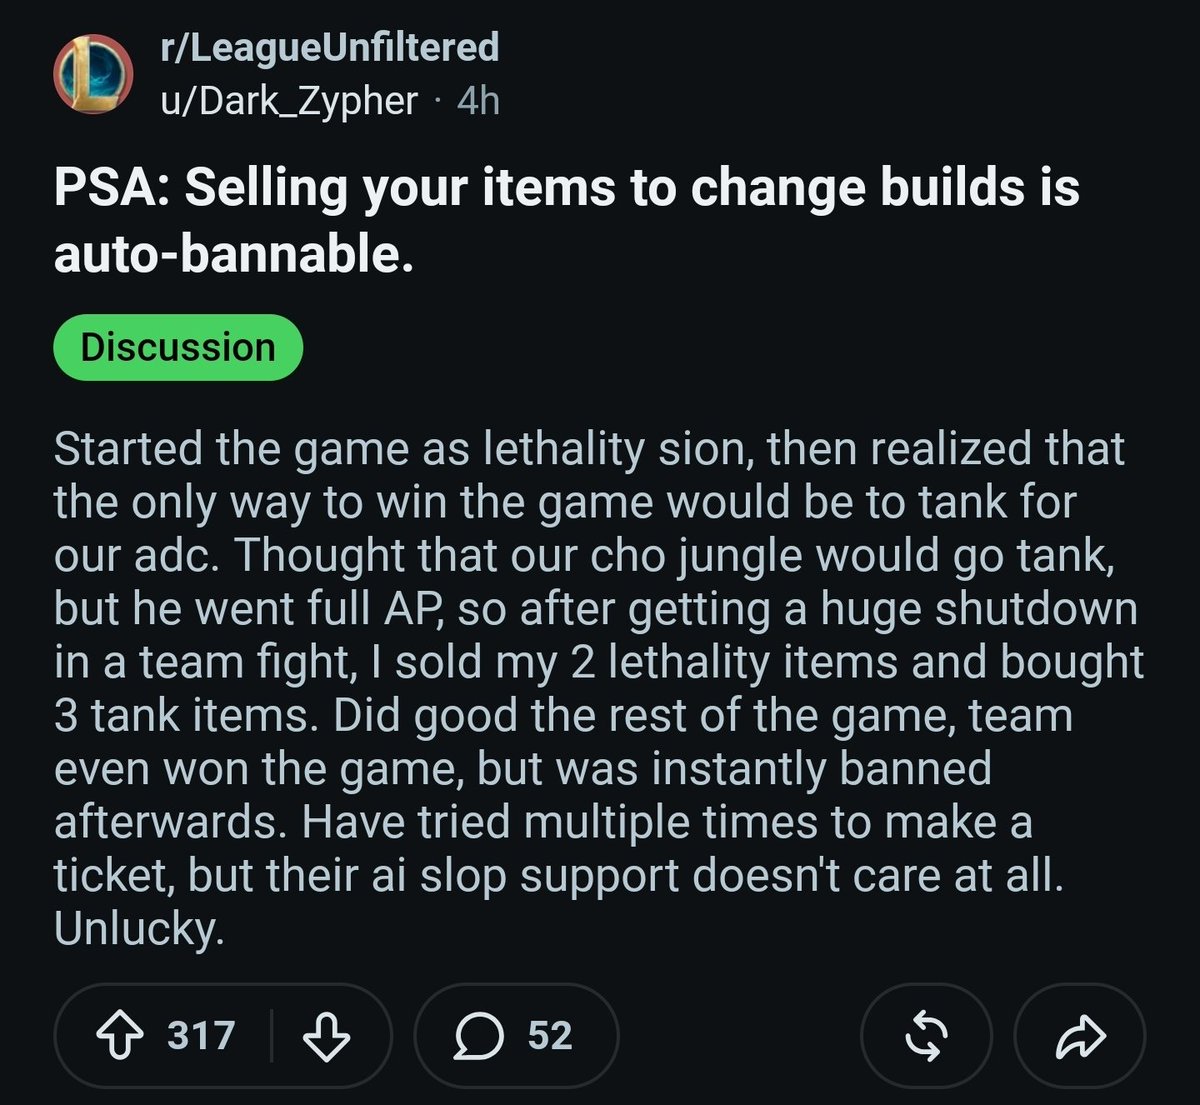
@AcceleratorV9@RiotZac He got a shutdown and instead of buying a third lethality item he got a tank item with the extra gold instead. IDK how you can't do math