10 #Log4Shell Facts vs Fiction: a 🧵
1. 1.x is NOT vuln to this RCE. While it doesn't have another RCE, it requires access to send serialized data to a listener ON the log server. This is much MUCH harder to exploit and kind of rare for a Log4j server to be running.
My mom controlled our AOL account when I was about 13 and would come into my room to sign me in. So, I created an entirely fake AOL login flow in Visual Basic and had her sign me in once to capture the password. Old school phishing.
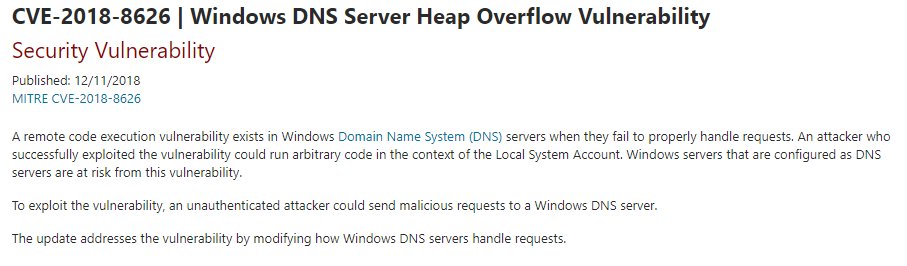
Patch your Domain Controllers running DNS (typical config, so most orgs) ASAP.
DNS remote code execution vulnerability which runs as LocalSystem on Windows DNS server (usually a DC).
https://t.co/lz1r4yA5Ap
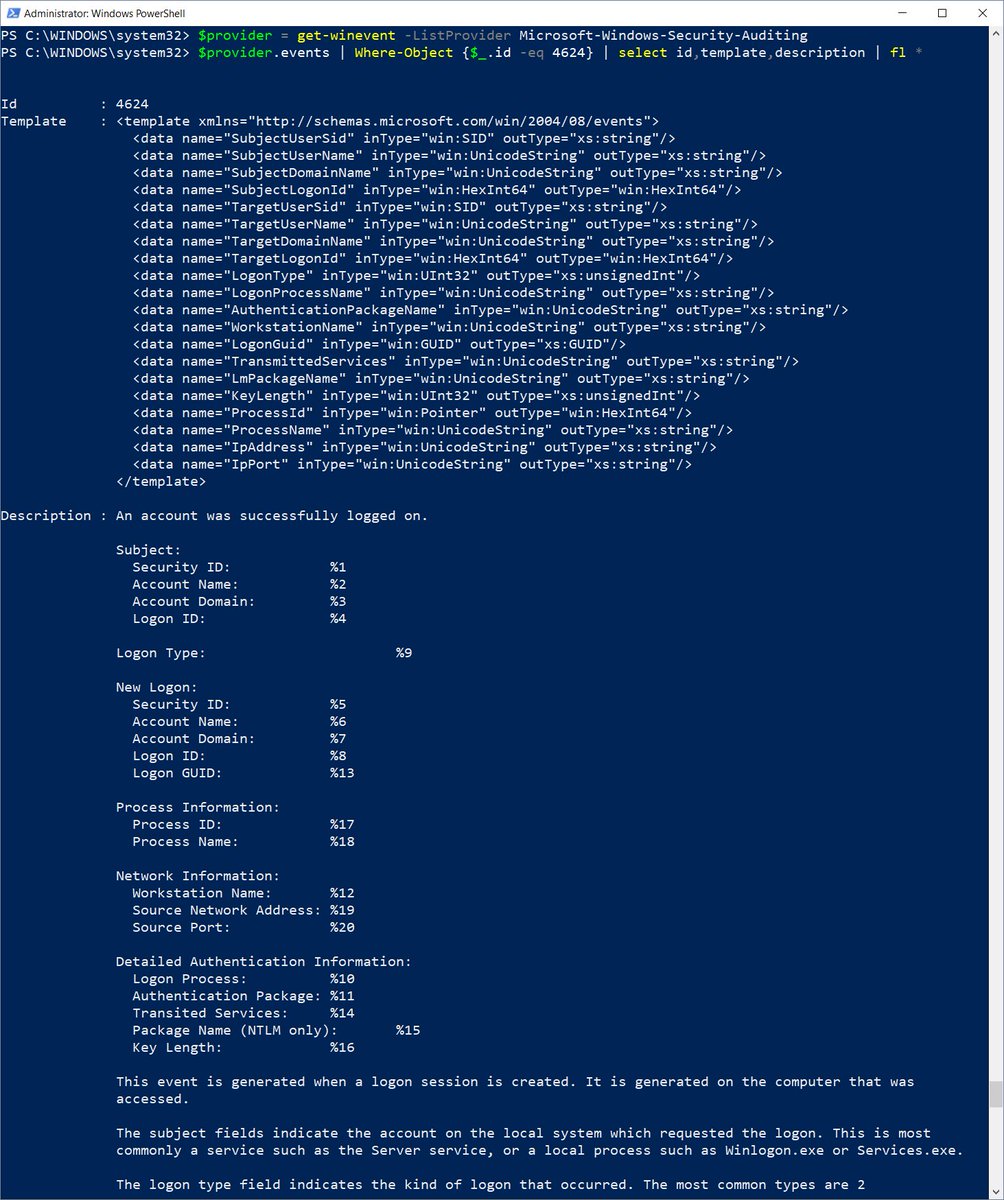
Ever wonder where Windows log descriptions come from? I was going deep on the logging section of my upcoming @SANSInstitute#SEC450 Blue Team Fundamentals class and ended up with this cool PowerShell command. It dumps all the XML fields and message templates for any event ID!
or 1=1 or 1=1-- or 1=1# or 1=1/* admin' -- admin' # admin'/* admin' or '1'='1 admin' or '1'='1'-- admin' or '1'='1'# admin' or '1'='1'/* admin'or 1=1 or ''=' admin' or 1=1 admin' or 1=1-- admin' or 1=1#