"windows-api-function-cheatsheets: A reference of Windows API function calls, including functions for file operations, process..."
#infosec#pentest#redteam
https://t.co/gnySncxdPb
I'm joining the dark side, today I'm publishing a malware loader called NixImports. It uses API-Hashing and dynamic invoking to evade static analysis. Check out my blog post for more details: https://t.co/gs1ZodpOKh
Live! Live! Live
PWSH C2 - A Customized Offensive PowerShell Command and Control for Red Team
A full walk-through of custom designed pwsh c2 by @_MrNiko
Only On Twitch:
https://t.co/S9dnKZrdMs
Giveaway of 2 TryHackme VIP For 1 Month 🎉
Task: Hit 2K Subscribe target on YouTube(https://t.co/XyazdG8MmS) & Follow https://t.co/qR8tfGx0z1 + https://t.co/vq9b1JYFvr
‼️ To keep the record & for verification regarding giveaway, share the snap of the task completed in my DM.
We are creating an IT army. We need digital talents. All operational tasks will be given here: https://t.co/Ie4ESfxoSn. There will be tasks for everyone. We continue to fight on the cyber front. The first task is on the channel for cyber specialists.
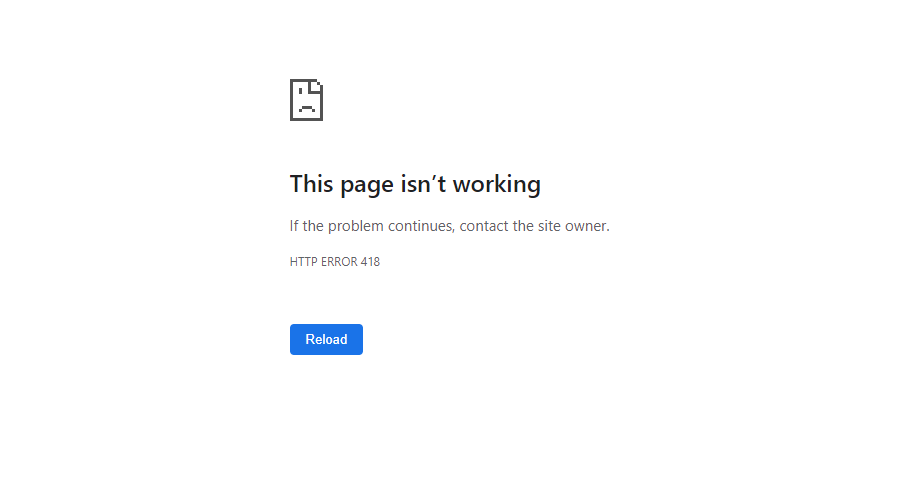
The Russian military website (https://t.co/h3n4oxn0ac) is returning HTTP error code 418 indicating the Russian Military is now a Teapot.
No, this is not a joke.
💖 I'm sponsoring @pentest_swissky because i find "PayloadsAllTheThings" interesting with combination of all the techniques & tools at one place, however with some regular add-ons it can be the best. https://t.co/HxMLdHAvah