REA is most dangerous thing on the internet right now...
It lets your AI agent reverse engineer any app, down to the binary
If you use it correctly, you can rebuild any feature you pay for, for FREE
In this article, I show you how: https://t.co/3P1FNXiXzl
Github:
https://t.co/pp4VeHRHKI
Prompt:
You are building "Bastion": a free, open-source desktop app for Windows and macOS that finds the backdoors in my home Wi-Fi router, shows where my traffic goes, speeds up my Wi-Fi, and lets AI agents watch my network. Work in this empty folder. Use Opus 5.5.
DESIGN FIRST, CODE SECOND
1. Before writing any code, design 4 different UI concepts as web pages (dark, premium, Apple-level polish, focus on speed + security). I'll pick one.
2. Then rebuild the chosen concept until it looks like Apple made it: real 3D (Three.js) router on the home screen, bloom + anamorphic lens flare, glass panels, Apple-style sliders with a glow that runs around the edge, a flowing ambient background behind every screen.
WHAT THE APP MUST REALLY DO (no fake data, ever)
- Find my router and probe it from inside the network: TR-069/CWMP (port 7547), UPnP port-forwards (read the actual mappings), Telnet, SSH, plain-HTTP admin page.
- Check whether my DNS lookups are encrypted and who resolves them.
- Read my Wi-Fi: channel, band, signal, security; survey neighbour networks and recommend a quieter channel.
- List devices on my network and which apps on this computer talk to the internet.
- Run a real speed test.
- Check if my Wi-Fi name ends with _nomap and if this computer uses a private MAC address.
- Score my network 0–100 and give plain-language, step-by-step fixes.
- If something can't be measured from inside my network, say "unknown" and explain why. Never guess.
AI AGENTS
- Let me plug in Claude, ChatGPT or Grok with my own API key (stored encrypted by the OS keychain).
- Also let me use my existing subscription without an API key: talk to Claude through my Claude Code login and to ChatGPT through my Codex login.
- Before anything leaves my computer, strip MAC addresses, device names, Wi-Fi names and the end of my public IP.
- Agents only suggest. They can never run commands, log in to my router or change a setting.
SAFETY RULES
- Never log in to my router and never try a password.
- Shell out only with fixed arguments; my text goes in through stdin, never into a command line.
- Any CLI an agent uses runs with zero tools, read-only, in an empty folder, with a timeout.
HOW TO BUILD IT
- One Electron codebase for macOS and Windows. Write a short internal contract first (IPC surface + data types) so modules can be built in parallel.
- Split the build across parallel agents: network scanner, Wi-Fi + speed test, AI agents, 3D hero, UI kit, screens, packaging. Give every agent a reviewer and every reviewer a fixer.
- Add a separate security agent that attacks every line that runs commands or sends data.
- Add a design-critic agent that screenshots every screen and asks: "would Apple ship this?" If not, it goes back.
- Run the scanner on my real machine and fix whatever real hardware breaks (localized OS output, OS permissions, rate limits).
- Before anything goes public, check that none of my IPs, MAC addresses or network names are in the code.
SHIP IT
- Push to a public GitHub repo with an English README (what it does, what it does NOT do, privacy, install).
- GitHub Actions builds the .dmg and .exe on every version tag.
- Build a launch site on Vercel in the same design, with download buttons that always point to the latest release.
I put the final nail in the coffin of closed-source...
this is f*cking dangerous
this is the list of 20 GitHub repos I’m using daily to reverse-engineer any paid app, website or service.
[01] analysis core:
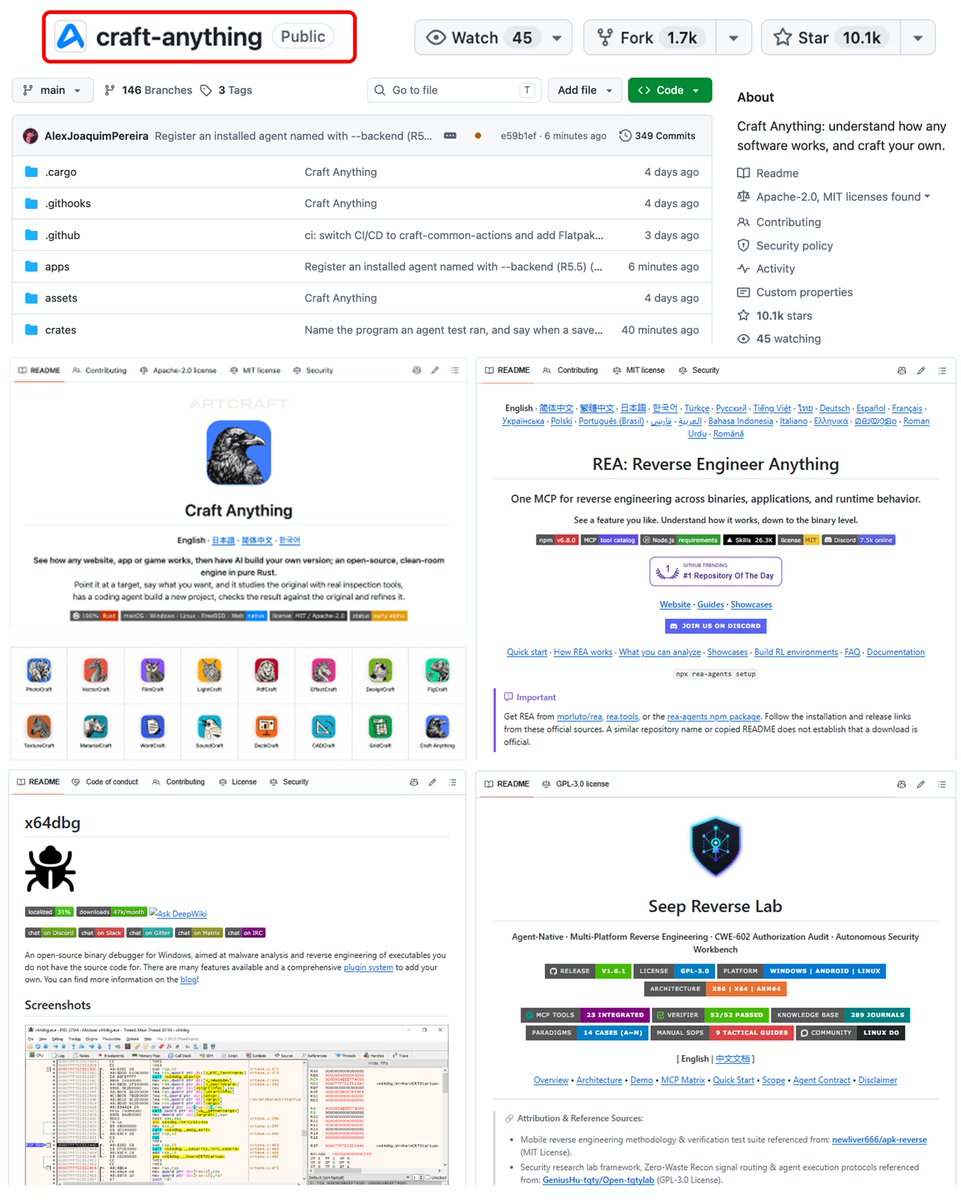
REA: a single MCP that connects to everything https://t.co/X6at3ZQIzL
Craft Anything: the whole study -> rebuild -> verify https://t.co/vmolOp0HwA
Ghidra: decompiler, free https://t.co/a9mTsOLDO9
GhidraMCP: lets your agent handle Ghidra https://t.co/G9tgudTwyR
[02] mobile and apps:
jadx: turns Android APKs back into Java https://t.co/yu8QpUX8EH
Apktool: disassembles APKs and reassembles them https://t.co/Q3ghJwDCK2
Frida: hooks into apps while they run https://t.co/HMlvWdg1I3
ILSpy: decompiles .NET https://t.co/I1t0Gowl6e
[03] binaries and low level:
radare2: RE framework that lives in your terminal https://t.co/TEyJxiwlJM
x64dbg: debugger for Windows https://t.co/TnOqKIhVcT
ImHex: hex editor with its own pattern language https://t.co/bGdgJiSx9Z
angr: symbolic execution engine https://t.co/wSyCD0Flzq
[04] network and execution:
mitmproxy: gets in the middle and reads the traffic https://t.co/JKlRCEBkhJ
dnSpy: debugs and edits .NET apps https://t.co/znKPGv8QC0
rizin: the radare2 fork https://t.co/GDAVxVkoEA
raddebugger: the Epic Games debugger https://t.co/BjiIxMZl7t
[05] rebuild and verify:
awesome-ai-reverse-engineering: 122 repos, all rated https://t.co/dWp7GsPGDc
awesome-reverse-engineering: selected by the REA creator https://t.co/LjNmcLDGSO
how it works: binary -> REA -> SPEC.md -> rebuild -> oracle -> retry
send this list to your Claude Opus 5.5 and make any app free by the afternoon.
then read the full workflow on how to reverse-engineer any app in the article below
RIP closed-source (1975-2026)...
solo dev just released the Wikipedia of reverse engineering for your AI agents
this is f*cking dangerous.
It’s called Awesome-REA, and it lets you to:
~ inspect, deobfuscate and rebuild websites.
~ decompile, port and rebuild games and their engines.
~ break down Android, .NET, JVM and Electron apps.
~ take apart native binaries with disassemblers, decompilers, debuggers and diffing tools.
~ extract and analyze firmware, then decode device protocols and packet captures.
~ plug MCP servers and agent workflows into your AI coding agent.
it comes with 1,253 curated resources, 431 real cases, 235 papers and 3,309 indexed repos.
and your agent can read all of it through llms.txt and a JSON API.
find the GitHub link below ↓
The ultimate weapon against REA reverse engineering is here!
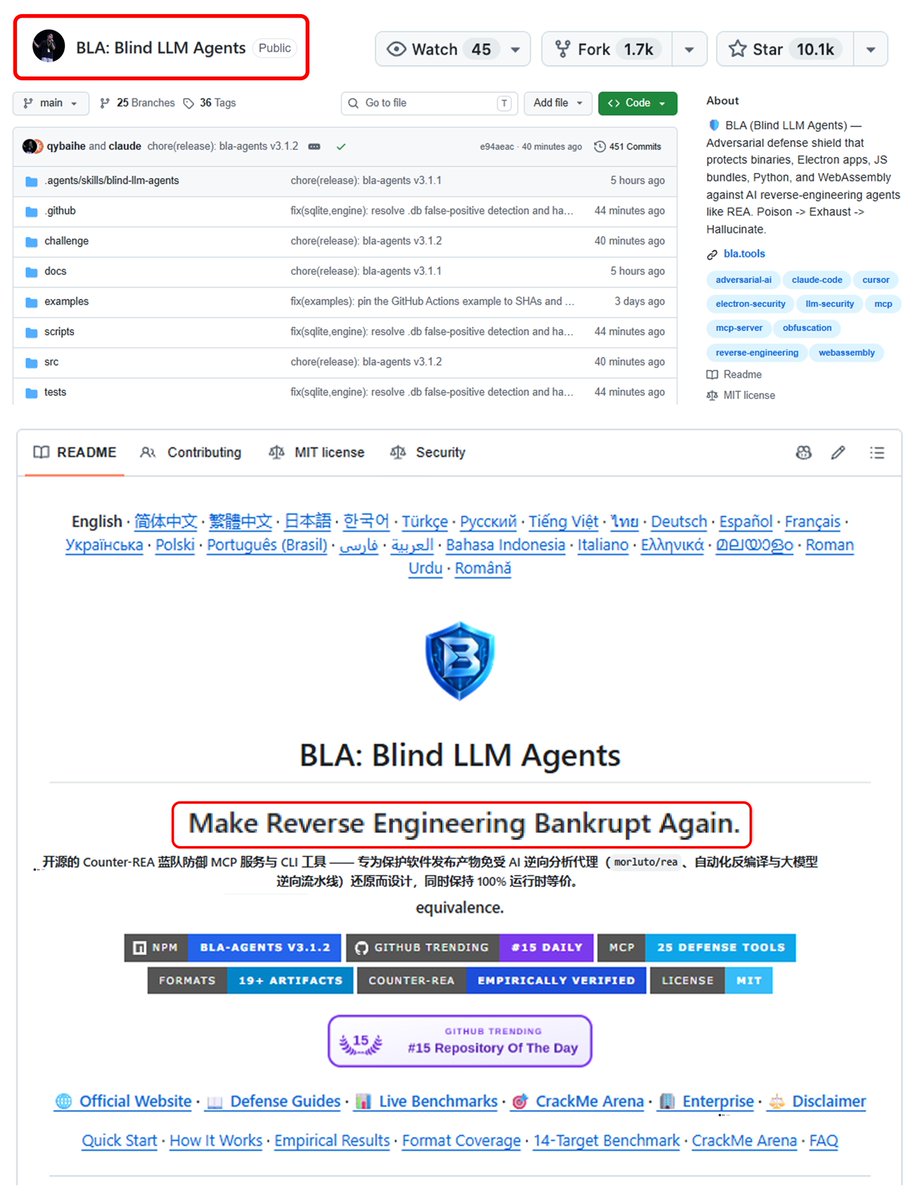
Chinese student just f*cked all Reverse Engineers with one github repo
REA clones your app’s core logic in seconds for ~$0.20, BLA makes that same job burn 300×–2,800× more tokens
here’s how to use and setup BLA:
first understand how it works:
• poison: fake canaries and decoy logic for AI to chase
• exhaust: files that blow past REA’s own limits
• your app runs 100% the same (14/14 tests)
here’s how to set it up for FREE:
1 → open Claude Code in the folder of your app, site or game
2 → make sure you have Node.js 24 (22.23.4+ works too)
3 → run: npx bla-agents setup - it plugs BLA into Claude Code, Cursor, Codex, Windsurf, Gemini CLI and more
4 → then just say: “Harden my software against REA”
5 → your agent runs the whole loop itself: plan → weave decoys into source → harden the build → verify
6 → the step everyone skips: ship the files from the .bla-hardened folder, not your old build
7 → want to see it yourself? npx bla-agents benchmark runs 14 test apps before vs after
paste link on repo below ↓
💰 $100M L1X Airdrop is Live 🎈 Earn your share of 10M L1X Coins by completing simple tasks & referrals. 🔹 On-chain activities & TaskON rewards 🔹 Bigger rewards for leaderboard ranks 🔹 More engagement = Higher allocation 🚀 Join now: https://t.co/BpJ4BGEAdr
🚨RFK Jr. calls out Bernie Sanders direct to his face! 🔥
"Bernie, you have accepted millions of dollars from the Pharmaceutical industry. In 2020 you were the single largest receiver of Pharmaceutical dollars. $1.5M"
The crowd erupts in applause! LFG!!
https://t.co/ylQezDqyyY
❤️💛💚💙
Dear Coinbase (@Coinbase),
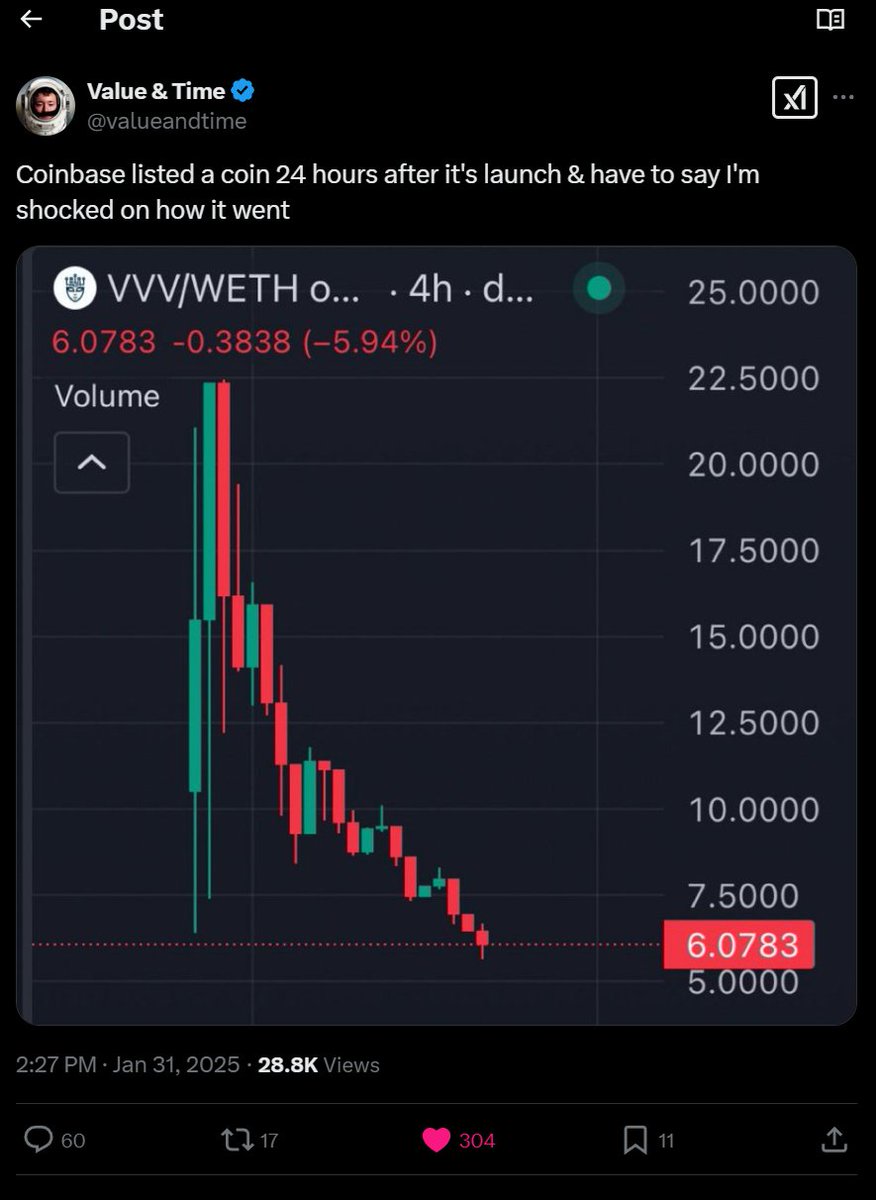
We've noticed that your token listing launches are becoming Exit Liquidity signals and your customers are getting rinsed by buying the coins.
Please consider listing PulseChain $PLS next, to give your customers an advantage.
PulseChain has these advantages for you:
✅ 250,000 strong people (and growing)
✅ 2 conferences per year (Hosted By Community)
✅ 170+ content creators
✅ 70 streamers
✅ Survived HEX -99% down, strong belief
Please show your customers some respect and list PulseChain, $PLS, instead of continuing the cycle of Exchange-Listing Dump violations like we just saw with VVV.
💟 See my attached pic for PulseChain Price Chart being Low and available for Coinbase Customers to buy and actually make a profit.
PulseChain Community continue to support Coinbase against the SEC.
🍴 Either Coinbase or Binance are going to list us first, so you should get ahead of the competition.
(P.S. Do not tell us that you care about Token Supply distribution, because we all know Trump owns 90% of his coins and you listed TRUMP within 12 hours)
(P.S. You also list XRP, where Ripple owned 80% of tokens and have been dumping the whole time. PulseChain Origin Address has NEVER dumped $PLS or HEX or PLSX for that matter).
Sincerely,
PulseChain Community
(Your Friend Sommi)