CEO at @VeridiseInc and PhD student at UT Austin. I specialize in building practical tools to discover security vulnerabilities in code using formal methods.
Reading about model misalignment over the past few weeks has been wild and the cases of collusion via public sites is particularly interesting. In the most recent report, agents did so as a communication workaround but could cause confidential data (e.g. user data) to be leaked
This article nicely captures some of the risks of quantum with respect to cryptographic systems such as blockchains. The fact that these attacks leave no trace means other attacks such as device compromises cannot be ruled out and allows warning signs to be easily dismissed.
"When someone cracks your key, you don't get a memo saying how they did it."
@YuviLightman spoke to @Cointelegraph about what crypto's first quantum attack will actually look like.
People are already publishing papers in response to COLDCARD (e.g. https://t.co/tJ4Ix2C86u). Seems a bit quick, no?
Z-SCAPE doesn't solve the core problem. It assumes manufacturers have advanced knowledge of a deficiency and can exploit it. The ZK portion also seems unnecessary
A ZK proof can be perfectly sound and still fail to prove what users think it proves.
Hollow-LLM highlights this problem for AI verification—but it’s a lesson we’ve seen before in ZKVMs. https://t.co/F7VoxBk286
Good news!
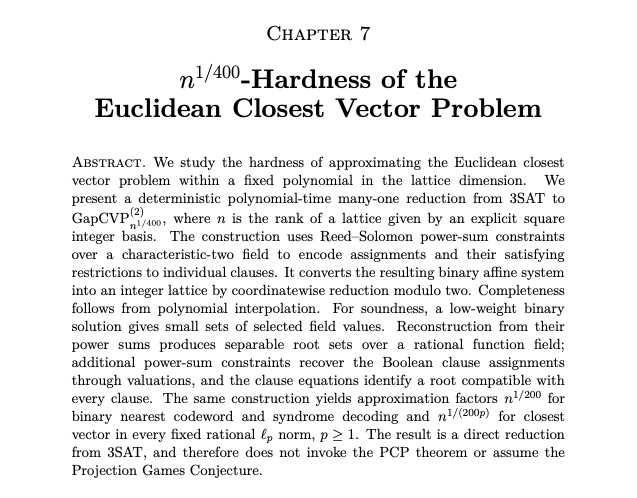
OpenAI just published a paper that proves some new hardness properties of CVP (used in lattice cryptography). This reduces the number of potential attacks on lattice problems
Great news for Nightstream: our lattice-based zkVM!
A more natural approach for Bitcoin may be to use the proof only for migration. Vulnerable outputs could eventually be frozen, while their owners retain a rescue path that proves seed provenance and moves the funds to a post-quantum address.
Future transactions could then use ordinary post-quantum signatures. This would preserve the legitimate owner’s ability to recover their funds without making seed-based proofs part of normal wallet operation.
ZKPoSP was recently brought to my attention (https://t.co/NCZV6HwqMl). It provides an interesting proposal related to making Bitcoin quantum resistant. Rather than relying on a quantum-vulnerable signature, a user could prove knowledge of the seed from which an existing wallet address was derived.
This could allow users to retain control of existing addresses even after the underlying elliptic curve becomes insecure. However, the operational consequences seem more significant than the paper’s cryptographic framing might suggest 🧵
This substantially increases the potential cost of compromise. The theft of an individual private key may expose a single address, while the theft of a seed can expose every account and key derived from it, potentially across several chains.
The proposal would also require significant changes to wallets, hardware devices, transaction validation, exchanges, and other Bitcoin infrastructure because proof-based authorization would replace signatures for future transactions.
@rthurknl Sure, some people may be making such an assumption but others treat crypto as a honeypot to provide evidence of private quantum capabilities. Even in cases where a company develops the technology first, you have to worry about insider threats before an announcement.
I’ve seen discussions where people talk about “Q-Day” as though the signs will be obvious.
Some attacks could provide a strong signal, especially the repeated hijacking of Bitcoin spends after previously hidden public keys are revealed in the mempool but before the transactions are confirmed. These attacks require a quantum computer fast enough to recover a private key within the transaction settlement window.
The more insidious risks, in my opinion, are attacks against public keys that have already been exposed. These attacks do not face the same time constraints, and the resulting transactions could look onchain like ordinary private key theft, allowing the owner of such a machine to drain selected funds without immediately revealing that a quantum computer was involved.
This slower method of exploiting a chain could be a deliberate choice. Rather than triggering an obvious crisis, an attacker could bleed a cryptocurrency dry over time by targeting high-value holders or privileged signers. The damage could also spread to otherwise quantum-resistant chains through bridges.
By contrast, a conspicuous attack would likely trigger containment measures, potentially destroying the ecosystem altogether. This would reduce the value of the stolen assets and make them more difficult to move or launder.
It is therefore unclear to me that “Q-Day” will occur as some people seem to expect. I agree that crypto is a likely early target, but the initial signs may not be obvious.
This is a problem we've observed when auditing code that makes heavy use of AI as well. Rewriting code increases the maintenance cost and increases the likelihood of errors. Libraries should be preferred for utilities but developers must ensure they are high quality
With AI, there’s a strong tendency to build everything from scratch instead of reusing libraries
That’s a mistake
The right SDKs let you delegate what isn’t core to your product
Thx Smithers 0.28.0 for the great features (that I didn't have to build) coming to Ultrafuzz
The Nomad hack showed a gap the industry still has not closed: proactive post deployment security. We already have monitoring. What is missing is an automated method of actively searching for vulnerabilities in live systems, as this would could have caught Nomad’s misconfiguration before attackers did.
The Nomad exploit needed no privileged access and no deep protocol knowledge.
One fabricated message went through. The transaction was public, so hundreds of accounts copied it with their own address.
The root cause: a single 0x00, set during a routine upgrade and never checked before it went live.
@KFerles and I have been talking with projects and founders about their experiences with AI. One common theme that has come up lately for infrastructure developers in particular is the magnitude of the required context. Since some of these infrastructure projects are quite large, models struggle to maintain context of other relevant parts of the code. Are there any other problems people have frequently run into?
Polymarket was hit with a $3M supply chain attack. Incidents like this are only likely to become more common, which means security teams need to pair strong opsec with deeper vendor diligence and tighter oversight of third-party dependencies.