No single person can track every geopolitical narrative. Together, we can.
Every time you paste a news article into https://t.co/gn9njymdNA and run a scan, you help expand our understanding of the global information landscape.
At the end of each day, LucidSignal aggregates recent community scans into Daily Cluster Briefings, revealing the narratives, themes, and developments shaping world events.
Help build a shared map of today's information environment.
🌍 One scan at a time.
#LucidSignal #NarrativeIntelligence #CollectiveIntelligence #OSINT #DecisionIntelligence #Geopolitics #OpenSourceIntelligence #Research #InformationAnalysis
NEW: Director of National Intelligence Jay Clayton warned on October 23 that US intelligence assessments indicate that Iran is in the "advanced stages" of planning attacks against US targets in the region.
Other Key Takeaways:
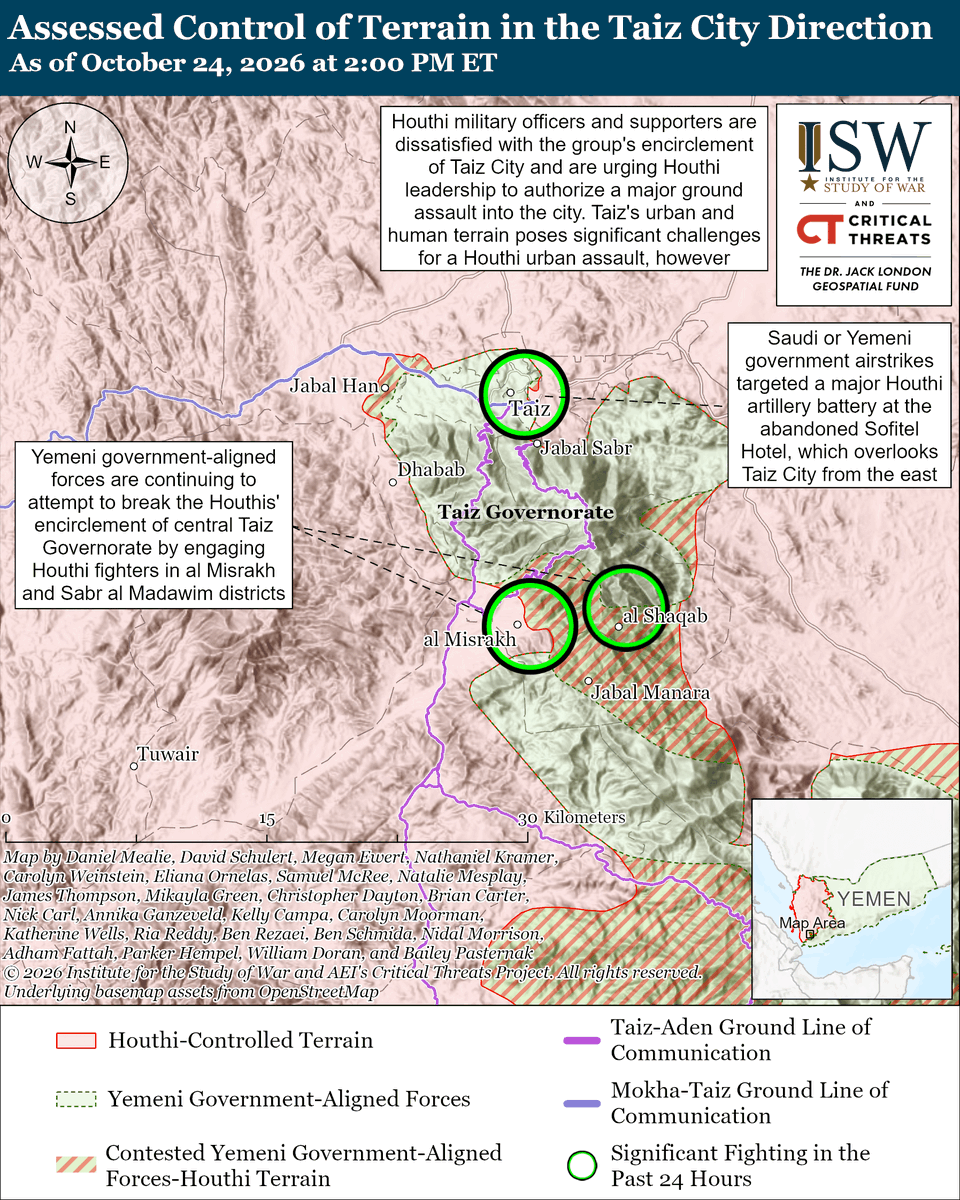
Houthi supporters and military officers have reportedly expressed dissatisfaction with the group’s military progress near Taiz City and are urging Houthi leadership to conduct a large-scale ground assault to capture the city.
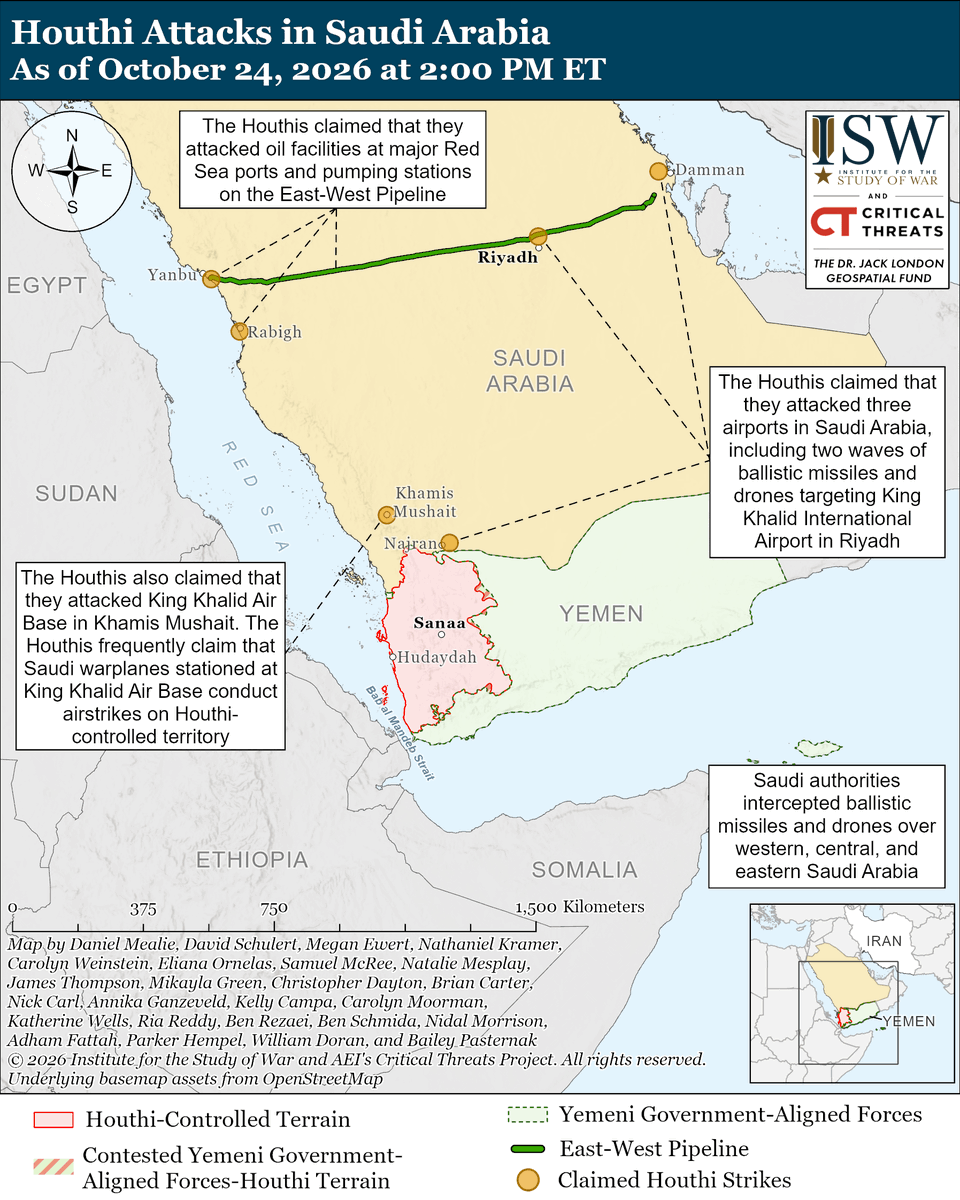
The Houthis claimed that they attacked three Saudi airports, pumping stations on the East-West Pipeline, and oil facilities at major Saudi Red Sea ports.
« Aujourd’hui, un acte terroriste odieux a été commis lors de funérailles tenues dans une église grecque orthodoxe à Karak, en Jordanie. Cette attaque a bafoué le caractère sacré d’un lieu de culte et a frappé des familles à un moment où elles vivaient un profond chagrin.
The FBI continues to warn about two critical security flaws in PHP, a programming language used to build many websites and online services. Attackers could exploit these vulnerabilities to break into systems, putting sensitive information and business operations at risk. Security updates are available and should be applied immediately.
If you are a business owner or website operator, check whether your systems are affected. Contact your IT support team, website developer, or hosting provider for help identifying vulnerable systems and applying the necessary updates.
The FBI urges organizations to take the following steps now:
➡️ If an immediate update is not feasible it is recommended that organizations take the system offline until it can be fully mitigated.
➡️ Immediately update affected PHP installations following the guidance on https://t.co/JFOW6jG9Ws. Inventory where PHP runs in your environment, prioritizing internet-facing systems and vendor products that bundle PHP.
➡️ Monitor web servers for suspicious activity, including PHP processes unexpectedly launching command shells or downloading files. Ensure appropriate process-monitoring capabilities are in place to help identify potential exploitation.
➡️ If you find signs of compromise, isolate affected systems, preserve your web server and PHP logs, and report it to your local FBI field office or https://t.co/ZWC7Se2YdU. Those reports help us identify the actors involved and warn other organizations before they become victims.
For the latest information on these vulnerabilities (CVE-2026-109618 and CVE-2026-109619), follow PHP’s announcements on https://t.co/JFOW6jG9Ws, CERT-EU Security Advisory 2026-018, and CISA’s Known Exploited Vulnerabilities catalog.
Our discussion forum is the only software we have using PHP. We've taken it down temporarily while waiting for the patches for https://t.co/CjXGfNY2ff due to vulnerability details already being available and proof of concept exploits being developed. Don't want to take the risk.
Italy: Protests, demonstrations, and gatherings may occur across Italy over the next few days. Recent demonstrations in Milan and Bologna resulted in looting and violent clashes. More demonstrators may gather in city-center squares and near main railway stations. Even demonstrations intended to be peaceful can escalate quickly. Local authorities may increase security measures, including road closures, traffic restrictions, or more police in areas where demonstrations occur. Expect more police around tourist sites, transportation hubs, and schools. More at https://t.co/tE4fbs3sqz
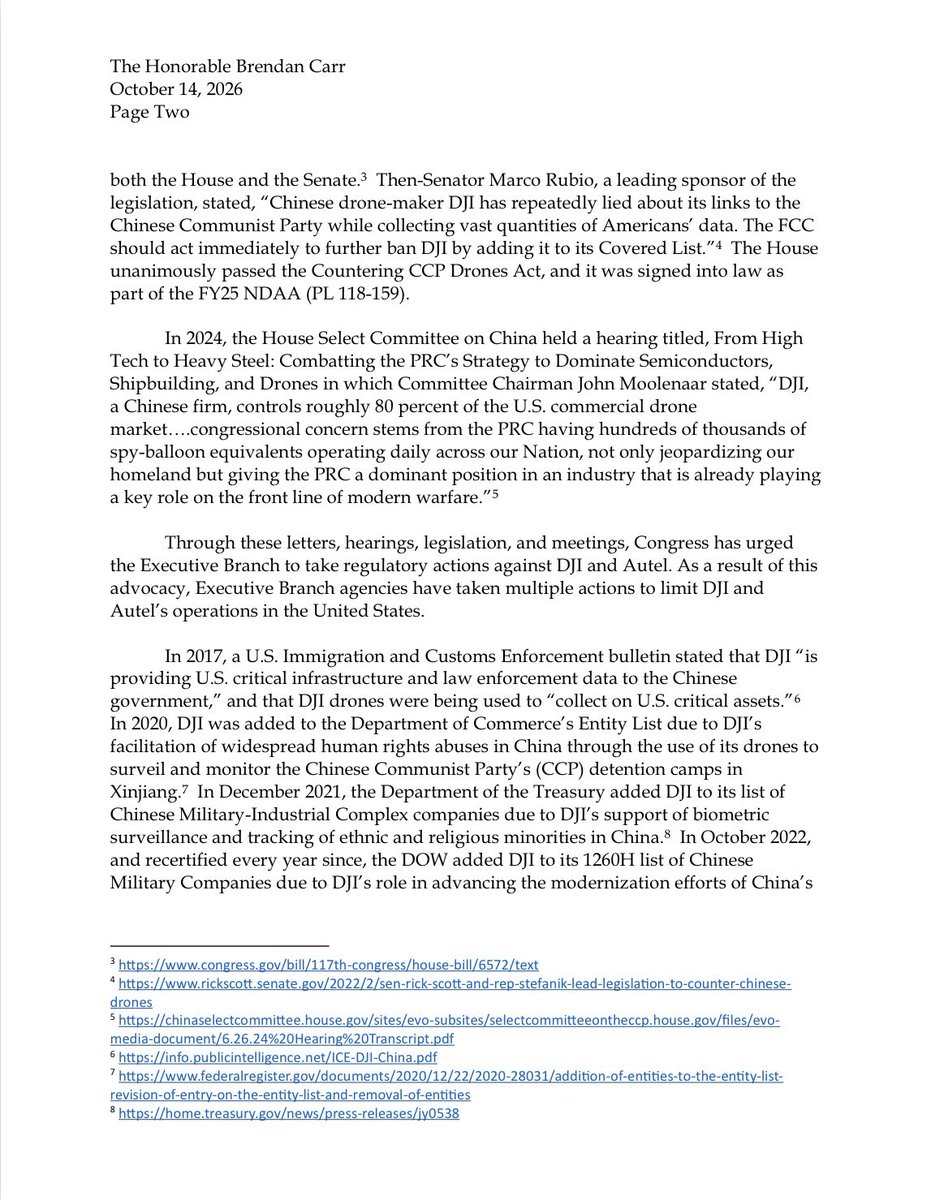
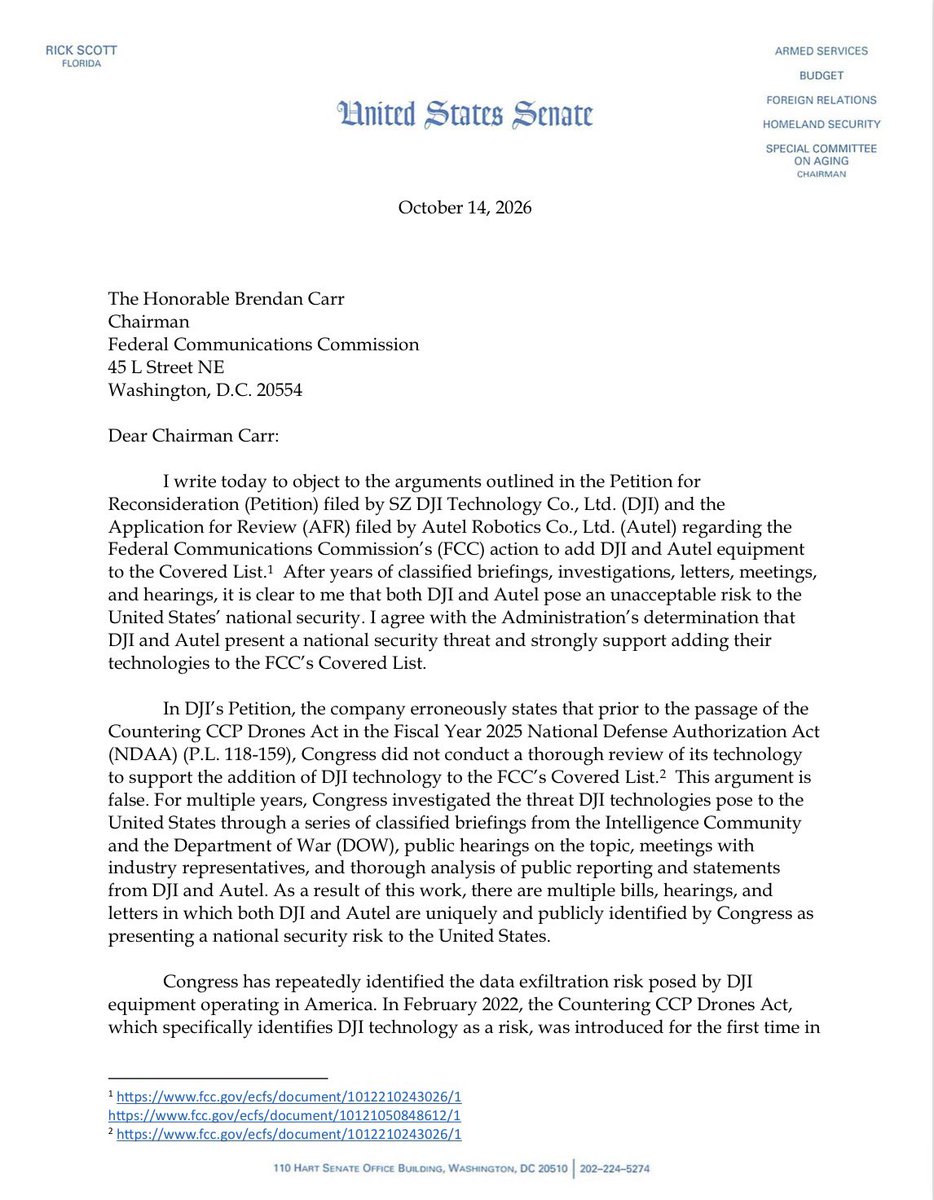
Communist China-linked companies like DJI and Autel present unacceptable national security risks to our country, and the CCP is using them to undercut American drone manufacturers. We can’t let that happen!
I worked for years to get them on the FCC's covered list. They must stay there, which is why I shared years of Congressional oversight and the threats these companies pose to @BrendanCarrFCC ⬇️
Asked how so many soldiers were killed and injured at CFB Wainwright, and whether any interim safety measures are in place, Defence Minister @DavidMcGuinty would not say.
"This is not the moment... to be speaking about what did or did not happen."
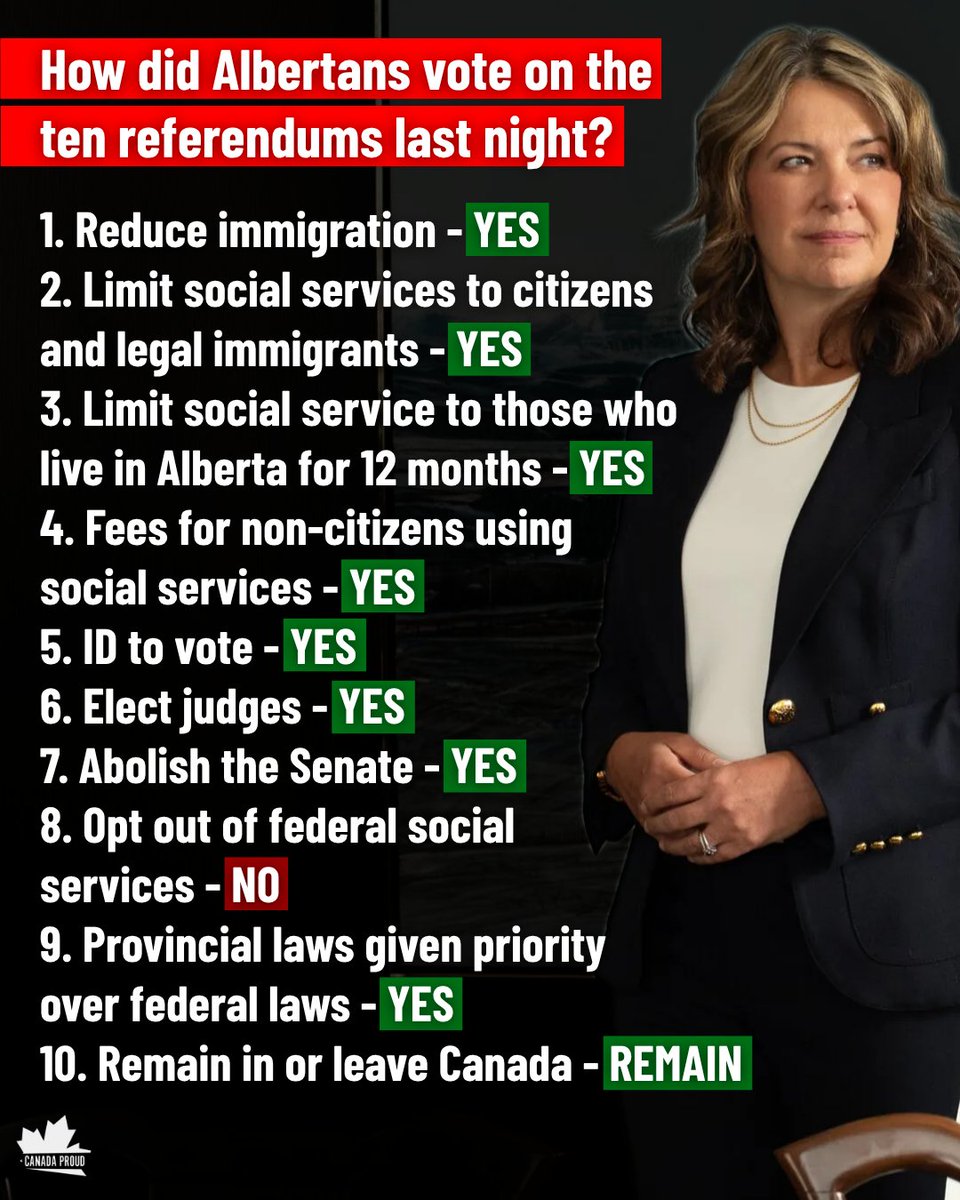
The results are in, and one thing is for certain: last night was a very good night for Danielle Smith.
Of the ten referendum questions posed to Albertans last night, Danielle Smith's endorsed option won nine of them.
That includes:
-Reducing immigration
-Requiring an ID to vote
-Electing judges
-Abolishing the unelected Senate
And many more important changes!
What do you make of the results?
Comme mentionné durant la campagne électorale, le premier ministre élu, @PaulPlamondon, a formellement demandé à la lieutenante-gouverneure de ne pas participer à la cérémonie d’assermentation du nouveau conseil des ministres. Au Parti Québécois, on croit que la légitimité de nos actions politiques relève de la volonté du peuple et non de celle d’un monarque étranger.
Rappelons que les institutions que sont la gouverneure générale et les lieutenants-gouverneurs coûtent 60 millions de dollars aux contribuables du Canada. Notre gouvernement réitère son intention d'abolir la présence de la monarchie au Québec à rediriger les sommes que nous pouvons récupérer au Québec vers les besoins en itinérance.
The Pentagon recently announced the results of its research security audits of major American universities and the termination of dozens of collaborations between universities and Chinese entities of concern. Chairman @RepMoolenaar released the following statement:
Au nom du Québec, je présente mes condoléances aux familles et aux proches des victimes de la tragédie de Wainwright, en Alberta.
Les dernières informations communiquées aujourd'hui font état du décès de quatre soldats des Forces armées canadiennes et 39 personnes blessées ou hospitalisées, dont 19 sont toujours dans un état critique.
J'ai fait parvenir une lettre à la première ministre Danielle Smith afin de mettre à sa disposition tout le soutien et l’expertise québécoises dont elle aurait besoin dans ces temps difficiles. Le Québec est prêt à déployer l’aide nécessaire au besoin des Albertains.
Je joins également ma voix à celle de la première ministre Danielle Smith pour souligner le travail exceptionnel des pompiers et des premiers répondants, qui travaillent depuis maintenant plusieurs jours à venir en aide aux blessés.
It is with profound sadness that we confirm that a fire incident at CFB Wainwright on October 17 resulted in fatalities and injuries. Our immediate priority is supporting those affected and notifying next of kin.
https://t.co/XT21ihOR53
Defence Minister David McGuinty provides an update on the situation at CFB Wainwright in Alberta, confirming that "there have been both fatalities and injuries as a result of an incident on the base."
#cdnpoli
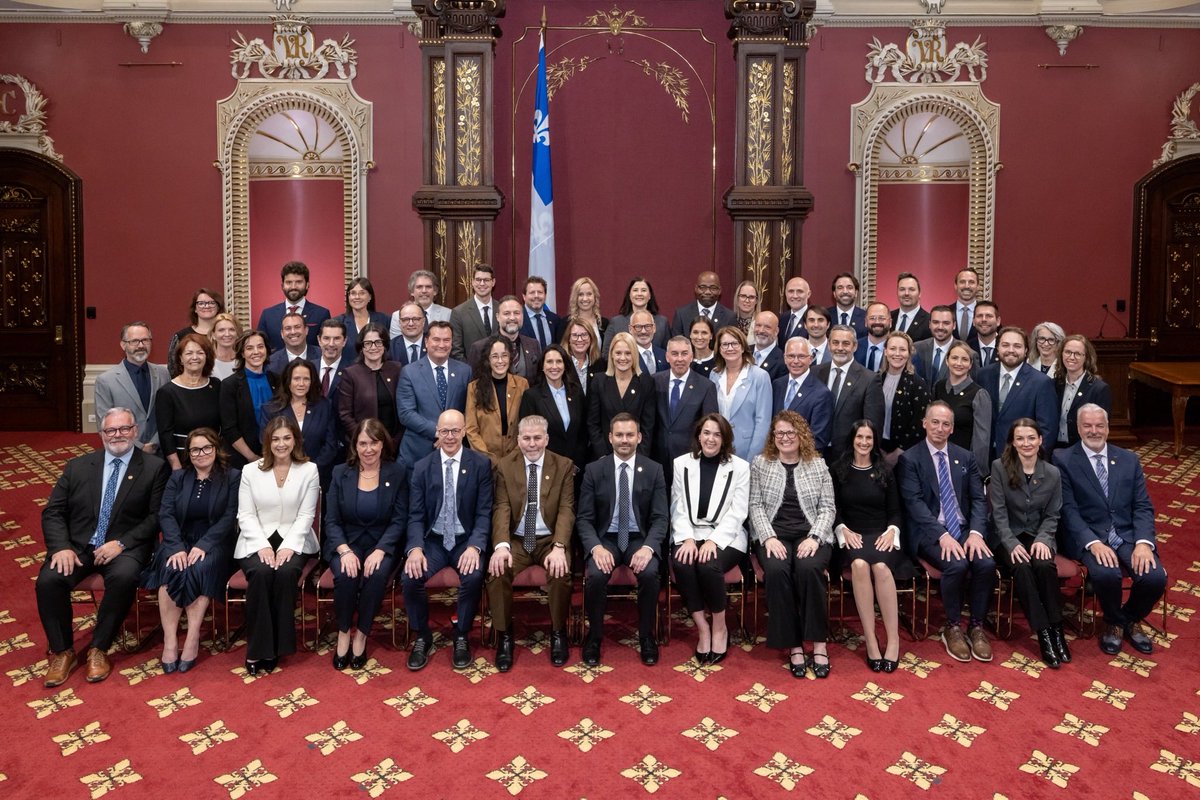
Hier, la plus grande députation péquiste depuis 1998 a fait le serment d’être loyale envers le peuple du Québec et sa constitution. C’est la seule autorité que nous reconnaissons.
Comme l’a dit notre chef, Paul St-Pierre Plamondon, dans son discours: «Le lys est en train de refleurir»!
«Un jour, le lys refleurira»
Il y a quatre ans, alors que nous étions que trois députés à l’assermentation, j’avais dit cela à mon ami Pascal Bérubé. Aujourd’hui, c’est 59 députés du Parti Québécois qui ont prêté serment à la Constitution du Québec.
L’équipe d’élus qui se présente devant vous aujourd’hui, c’est votre équipe. Elle se battra pour vous.
Que vous ayez voté pour le Parti Québécois ou pour une autre formation politique, chacun des députés du gouvernement du Québec sera à votre service.
Leur rôle ne sera pas de penser à la prochaine élection, mais bien de penser à vous. Vos intérêts, vos besoins, vos priorités.
On ne sera pas un gouvernement parfait. On va probablement faire des erreurs. Mais on va toujours donner l’heure juste, et donc l’authenticité et la cohérence de notre démarche est acquise, ce qui en soi, constituera un changement rafraîchissant pour la politique québécoise, un changement rempli de potentiel.
Nous allons agir par étape en réduisant le coût de la vie des Québécois qui en arrachent.
Nous reprendrons le contrôle des finances publiques en faisant le ménage dans le gaspillage et la bureaucratie. On fera preuve d’exemplarité en gelant nos salaires ainsi que ceux des dirigeants des sociétés d’État jusqu’au retour à l’équilibre budgétaire.
Enfin, nous allons recentrer l’État sur ses missions fondamentales: soigner, éduquer et protéger notre monde, ainsi que notre culture. Réduire de moitié l’itinérance au Québec.
On va faire en sorte de remettre le Québec sur les rails, de remettre la maison en ordre, pour qu’à nouveau on puisse avoir confiance dans notre État et notre gouvernement.
Qu’on retrouve confiance dans notre capacité à régler collectivement nos problèmes. Qu’on considère qu’il est à nouveau possible d’accomplir de grandes choses.
À ce moment-là, nous pourrons reprendre la discussion essentielle sur notre avenir national. Nous pourrons reprendre notre marche vers la normalité, celle d’un peuple normal qui veille à ses propres intérêts.
Qui adopte toutes ses lois, qui négocie en son nom avec ses partenaires à l’international et qui gère tout son budget lui-même, comme tout peuple qui se respecte est capable et content de faire ça lui-même.
Être maître chez nous, être maître de notre avenir et des décisions qui sont vitales pour nous, tel est notre destin. Et ce destin vous appelle, tous et chacun, aujourd’hui à travers ce rite de passage hautement significatif. Vive le Québec, vive la liberté, donc vive le Québec libre.
The House Select Committee on the Chinese Communist Party released more than 700 pages of previously nonpublic federal investigative files on Oct. 13, documenting undisclosed foreign affiliations, funding streams, and talent programs among researchers at U.S. universities.
The National Science Foundation (NSF) Office of Inspector General records accompanied a congressional report pressing for stricter oversight of taxpayer-funded science and highlighting systemic reporting lapses across academic institutions.
Committee Chairman John Moolenaar (R-Mich.) cited the findings to advocate for passage of the Securing Innovation and Research from Adversaries (SIRA) Act, which aims to bar federally supported research partnerships with foreign entities designated as national security risks.
Among the disclosed files was a 2020 NSF inquiry into materials scientist Enrique Lavernia, the former executive vice chancellor and provost of the University of California, Irvine.
Investigators found Lavernia held undisclosed affiliations with Chinese entities—including Wuhan University of Technology and Beijing's Thousand Talents recruitment drive—where Chinese Academy of Engineering records credited his research with advancing domestic defense and materials manufacturing.
The files included an unsigned contract offering Lavernia $50,000 per month alongside lab funding, while noting he omitted these Chinese connections from federal research submissions and a Department of Energy Top Secret security clearance review.
The NSF identified roughly $5.2 million in federal grant money linked to Lavernia since fiscal year 2012, prompting the agency to impose a government-wide suspension in July 2020 that barred him from receiving federal awards.
Lavernia transitioned to Texas A&M University in 2023 and received its highest faculty title in March 2026, with institutional records noting ongoing federal research support; the released documents do not specify how his suspension was concluded.
A separate October 2022 NSF probe focused on Stanford University, identifying at least 26 research grants tied to undisclosed foreign-funded initiatives, representing over $12.8 million in claimed project costs.
NSF agents recommended suspending 14 Stanford awards over disclosure failures, though the case files do not confirm whether the full funding sum was misused or if all proposed suspensions took effect.
Stanford grant administrator Michiko Pane told investigators that the university did not independently verify researchers' funding disclosures, leaving the burden of compliance entirely on individual faculty members.
The investigation singled out Stanford professor Richard Zare for holding a Thousand Talents appointment requiring three months of service annually in China, an arrangement Stanford reportedly knew about in 2019 but did not report to the NSF, spurring a suspension recommendation for his $464,000 grant.
Stanford, Texas A&M, UC Irvine, Zare, Lavernia, and the NSF did not provide substantive responses to requests for comment prior to publication.
The committee's report urges mandatory federal research standards, tougher compliance tracking, and more frequent debarments for non-compliant academics under the proposed SIRA framework.
NSF spokesman Mike England stated that the agency mandates full foreign disclosure, blocks participation in malign talent programs, and is drafting broader policies to prevent grant recipients from maintaining concurrent roles with restricted foreign entities.
https://t.co/2AdJPAD647
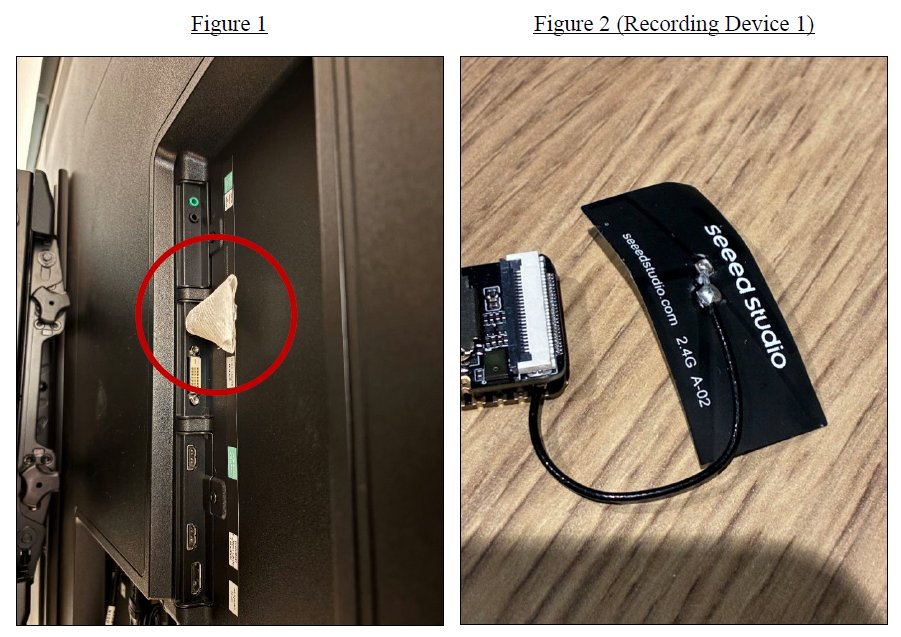
The #FBI#SanFrancisco Field Office, in coordination with the U.S. Attorney’s Office for the Northern District of California, has arrested a former employee of a San Francisco super‑intelligence company for allegedly installing a covert audio recording device inside a secure executive conference room. The device was positioned to capture sensitive, nonpublic company communications.
SAC Scott Schelble: “Any attempt to illicitly obtain protected information from U.S. super‑intelligence and technology companies threatens both American innovation and the national security interests those advancements support. We will continue working closely with our government and private‑sector partners to identify threats, safeguard critical advancements, and ensure the Bay Area’s innovation ecosystem remains secure.”
Read more: https://t.co/WkKump1vgr