🎉 Ready for four days of inspiring talks, hacking, and great community moments at #hacklu!
💬 You can also share your thoughts and comment on the talks over on our Discourse platform: https://t.co/8u6Qm2MC1C
or https://t.co/CmYeCmPbse
#cybersecurity#conference#Luxembourg
We are kicking off 2025 with Kali Linux 2025.1a! This update builds on existing features, bringing enhancements and improvements to streamline your experience. New themes, major desktop updates NetHunter car hacking and more!
Available for download now!
https://t.co/dm8EcCfxtb
@albinowax bug bounty money = hush money
companies don't want bad publicity.
agreeing with @LiveOverflow:
do not accept their conditions. just report and publish after two months.
Kali 2024.1 release is now live! Check out all the details at:
https://t.co/wtXfcJFUlT
Including:
Micro Mirror Free Software CDN
2024 Theme Refresh
Other Desktop Environment Changes
NetHunter Updates
New Tools!
Back from @hack_lu 2023. It was a great conference. Thanks to @Ministraitor everybody who missed can watch the presentations on YouTube.
#hacklu#infosec
Explore the ever-evolving world of hacking and creative computer problem solving with our new bundle of ebooks from @nostarch Press!
Pay what you want & support @ncacensorship
https://t.co/uO81EwnJjZ
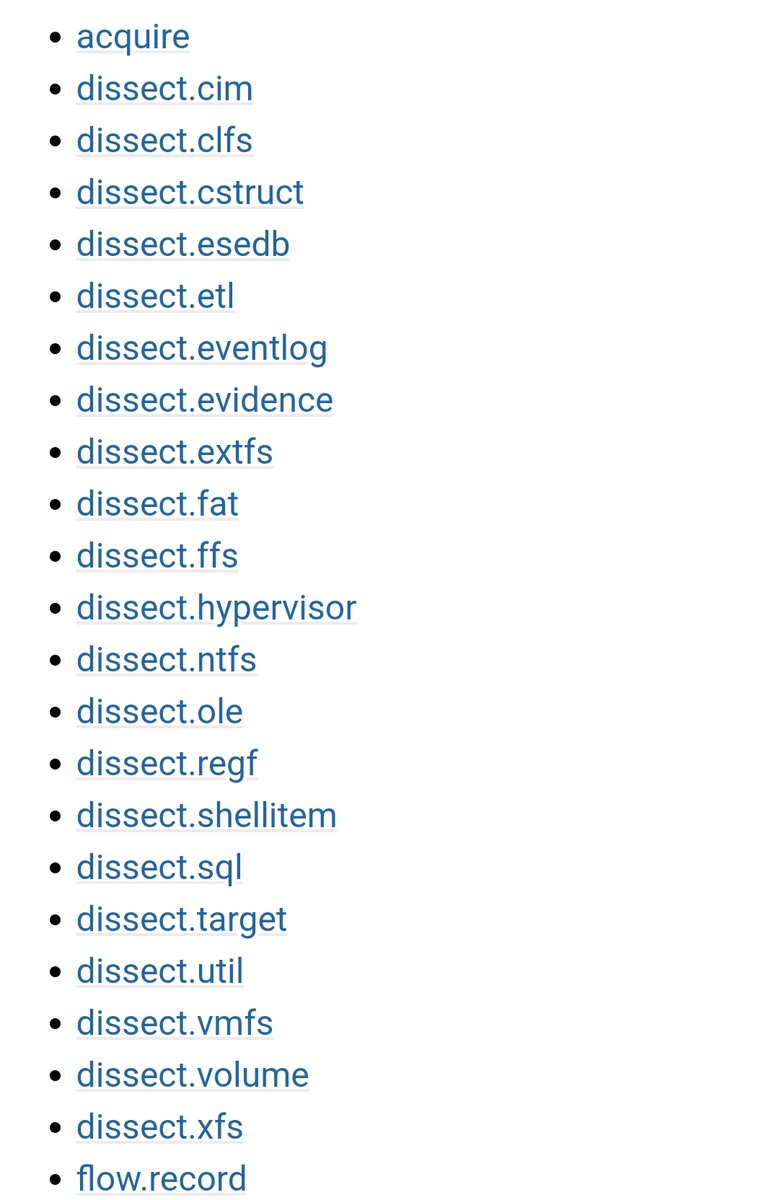
Fox-IT just open sourced their enterprise forensics tooling dissect. This is a big project that some of the smartest people I know have worked on. It supports many filesystems and file formats, all as Python libraries. Docs: https://t.co/M6YAygmW3E / code: https://t.co/HKT4eYIm1a
The first blog post is here. This one covers the technical details of CVE-2022-26923 (Active Directory Domain Services Elevation of Privilege Vulnerability).
The vulnerability was patched as part of the May 2022 Security Updates from Microsoft.
https://t.co/MJKEoZTuo2
📣 Only 10 DAYS until #RuhrSec Day 2022! 📣
Can you believe it?!
The team is so excited to see you all again ❤️
Are you late?! Don’t worry! Get a ticket here ⬇️
🎫 https://t.co/j9BlugF5HO
#itsecurity#CyberSecurity#ITSicherheit#conference
@PolarGlobal Dear Polar team, I did not receive any reply from [email protected] to my email of December 20th. Can you send me the contact address of a human being so that I can submit the information about the vulnerability in your Android application?
Dear @PolarGlobal, we want to report a security vulnerability in the Polar Flow Android app. I already contacted your support without success.
[email protected] didn't answer and mail to [email protected] is rejected. How can we contact your security team?
#ResponsibleDisclosure