Check out the growing infosec community on Mastodon https://t.co/sFDdjUQbwC I’m https://t.co/rU2vzjXk21 quite a few popular tweeters already tooting 🐘 Happy Days!
@GossiTheDog The security guy who knows how it really is in organisations, un pretentious, honest, tells it how it is. Good sense of humour with good ethics. When you took a twitter break in Jan I honestly missed you, that says a lot!
Exciting news! dnsReaper (1.4k stars on Github) is coming to Blackhat EU 22.
Blackhat is the premier cyber security conference in the world, and we've had a long-running relationship with Blackhat. Its fantastic to be invited to talk about our tools right here in the UK!
Always fabulous to see editors low the Windows Security level
When Citrix SSO is enabled... passwords are stored in *user processes* (in addition to system ones)
Ho yeah, *even if you have Credential Guard*
Yeah, that's what Citrix is calling "SSO"
> Will be in #mimikatz 3 🥝
@foxtrotluna We have a CDN, offer many of the same services, and do not conduct business with companies who promote violence or hate: https://t.co/dPP6yjeks4
Plus, if the project you’re working on is open source, we may be able to help for free: https://t.co/YVlA7gJkit
Compromises happen to everyone, and it's how you respond that matters. Nice work to @TalosSecurity for sharing a detailed blog post on what happened during their incident: https://t.co/USFiMXplmp - along with a clear statement: https://t.co/9V8LkPVwlj
Post-exploitation here is extremely straightforward, as ADAudit Plus recommends giving the tool a Domain Admin account.
https://t.co/W5tubAvfvo
Because of course it does.
@PyroTek3 rightfully rants about services "requiring" Domain Admin, and THIS. IS. WHY.
Want to learn about the "Top 10 Ways to Improve Active Directory Security Quickly"?
Sean Metcalf @PyroTek3, Tyler Robinson @tyler_robinson, & Darryl Baker @DFIRdeferred cover AD attacks & improving AD security
June 23rd
3pm-4:15pm (ET)
Register here:
https://t.co/xAhmhAt70n
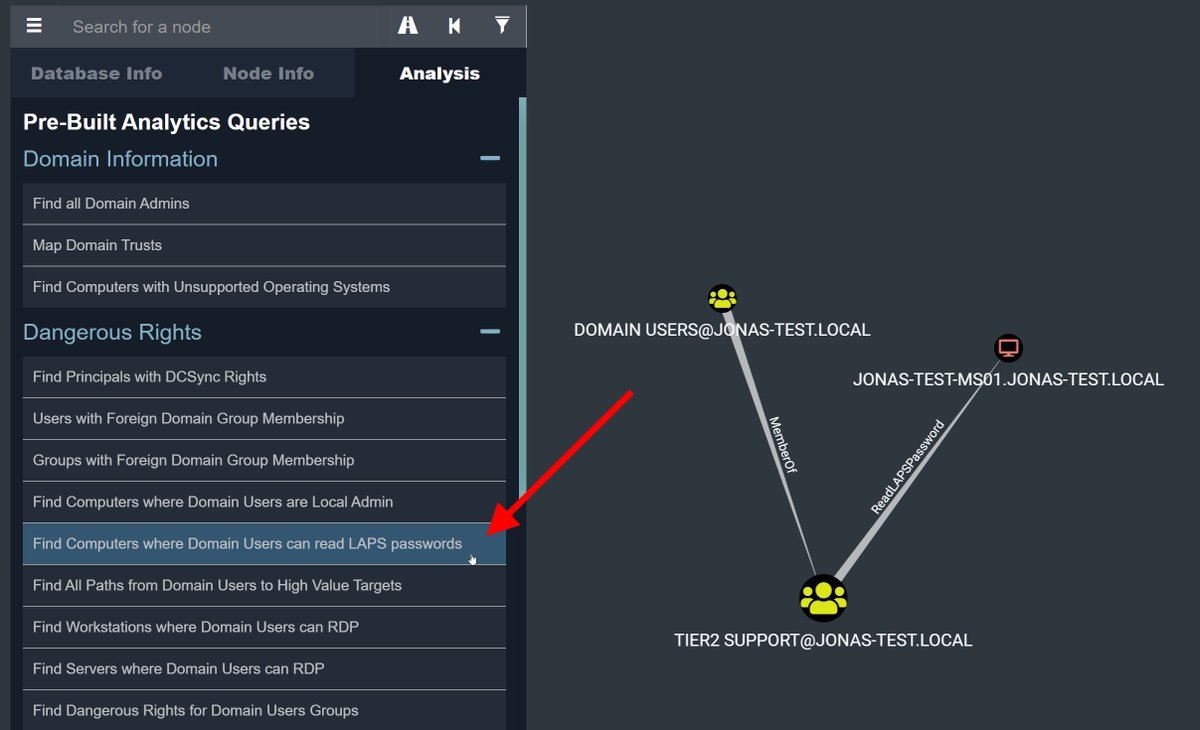
It’s Friday, which means it’s #BloodHoundBasics day.
You’ve admin access to a computer if you can read its LAPS password from AD. BloodHound makes it easy to see if Domain Users can read the LAPS password for any computer:
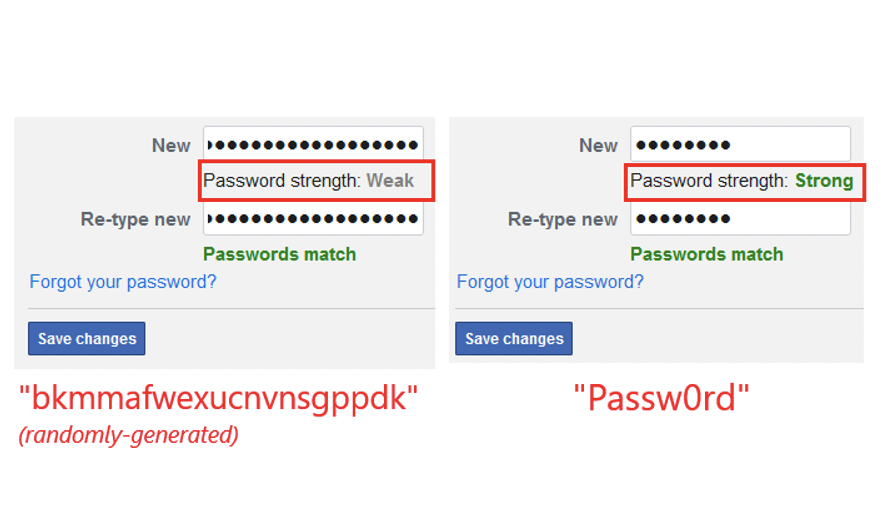
We facepalmed a lot while researching the password policies of 120 websites, but this took the cake. Facebook tells users 20-char random pw's are weak, but "Passw0rd" is strong, because hackers could never guess that pw's might have uppercase or digits. https://t.co/LrWQ673Gl1
I stand in both the world of Ops and Security. I increasingly see little argument for the difference. You can't do this thinking you're pulling on opposite sides of a rope. There is no rope. You're both sinking get a fucking bucket.
Corporate Infosec sends a phishing test email, I click, and somehow I'm the asshole because "[I] failed the test; had this been real it would have destroyed the company network"?
If me clicking can destroy the network, I'm not the one in this conversation who sucks at their job.