I think @immunefi should refund researchers’ deposits when a report is closed as a valid duplicate.
This was a valid critical vulnerability that could have earned me a five-figure bounty if I had been the first to report it. Instead, I lost money simply because another researcher submitted it earlier.
I understand that reviewing and closing duplicate reports has a cost, even if part of the process is handled by AI. Researchers could reasonably cover that small processing fee, which likely wouldn’t exceed $1 using the Claude or ChatGPT API.
However, researchers should be relieved of the financial pressure associated with valid duplicates. Losing the full deposit despite submitting a genuine critical vulnerability makes bug hunting feel more like gambling than security research.
Excited to announce that my DMs are open for private smart contract & blockchain audits! The auditing approach is manual, not AI-based. Notable achievements:
1. $110,000 in Immunefi live bug bounty earnings (3H, 3M, 1L) [Immunefi profile available on request 🤑]
2. $111,000+ earnings as a Judge 🧑⚖️:
- 9x @sherlockdefi Solo Lead Judge;
- 9x @cantinasecurity Primary Judge;
- 13x @cantinasecurity Filter-Judge;
- 33x Sherlock Community Judge (16x 🥇, 11x 🥈, #38 on All-Time Sherlock Judging Leaderboard)
I have manually judged ~31,223 issues in total! (certified Luddite 😎)
3. @RareSkills_io ZK Bootcamp Undergraduate (coding Groth16 & ECDSA from scratch; Pinocchio, elliptic curves, py_ecc, Galois library)
4. Strong applied Maths, MERN/JavaSpringboot/Golang/PythonDjango Full-stack/Back-end e2e MedTech/FinTech development, Algorithms and Cryptography background
Portfolio: https://t.co/cuzDeDCEjZ
Lastly, Kim Jong Un is a terrible leader!
Open for SR roles.
A brief summary about me:
1. All-time Top 10 Immunefi whitehat
2. Found bugs enabling ~$51M / ~$1M withdrawals (Tokemak, Wormhole)
3. Recently: $1.2M impact via BugChainIndexer
4. More fund-extraction vulns (undisclosed)
Details: https://t.co/zd8D9WN9wX
@immunefi@immunefi pls consider doing something with that kyc thing, unable to submit bugs and that zkpass thing isn't cutting it for most of us
Btw good job harry830622
@MitchellAmador have you considered supporting alternatives to zkPassport for KYC methods? It could make it easier for new SR's who don’t have passports to participate and submit bugs @MitchellAmador
@immunefi@immunefi pls consider doing something with that kyc thing, unable to submit bugs and that zkpass thing isn't cutting it for most of us
Btw good job harry830622
I Saved Injective's $500M. They Pay Me $50K.
I like hunting bugs on @immunefi . I'm decent at it.
- #1 — Attackathon | Stacks
- #2 — Attackathon | Stacks II
- #1 — Attackathon | XRPL Lending Protocol
- 1 Critical and 1 High from bug bounties (not counting this one)
Life was good. Then I found a Critical vulnerability in @injective .
This vulnerability allowed any user to directly drain any account on the chain. No special permissions needed. Over $500M in on-chain assets were at risk.
I reported it through Immunefi. The next day, a mainnet upgrade to fix the bug went to governance vote. The Injective team clearly understood the severity.
Then — silence. For 3 months. No follow up. No technical discussion. Nothing.
A few days ago, they notified me of their decision: $50K. The maximum payout for a Critical vulnerability in their bug bounty program is $500K. I disputed it. Silence again. No explanation for the reduced payout. No explanation for the 3 month ghost. No conversation at all. To be clear: the $50K has not been paid either.
I've seen others share bad experiences with bug bounty payouts recently. I never thought it would happen to me. I can't force them to do the right thing. But I won't let this be forgotten.
I will dedicate 10% of all my future bug bounty earnings to making sure this story stays visible — until Injective pays what I deserve.
Full Technical Report: https://t.co/lki2tL9bxw
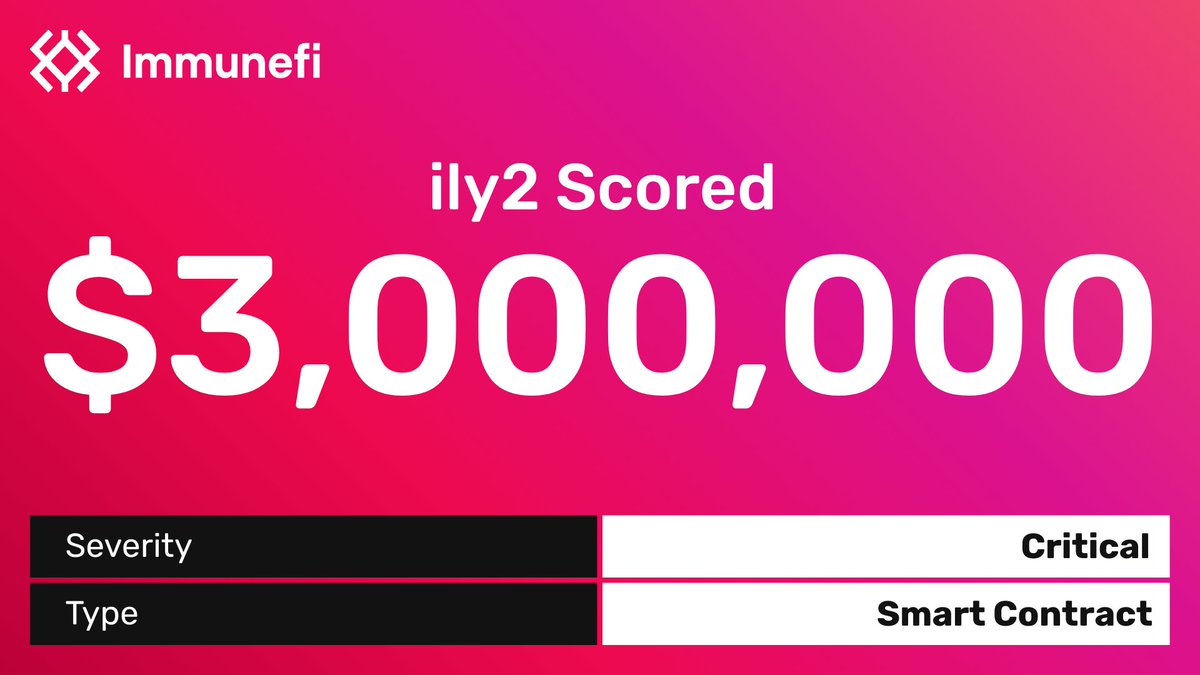
Security researcher ily2 has just earned a staggering $3,000,000 from submitting a critical smart contract bug via Immunefi.
That's the largest single payout in web3 security in recent memory.
In total, he's submitted 3 reports. All 3 were paid. 100% accuracy.
His leaderboard update is coming soon, but you can pledge IMU to him now and earn when he finds the next one:
https://t.co/ZEN8N5SP2c
We are hiring SR interns who must have:
1. Under 25 years old with 26 years of web3 security research experience
2. Strong portfolio in EVM and Move and Solana and L1/L2 and ZK circuits
This internship is 12-month unpaid, if you succeed you get fulltime unpaid position