Lately I've been working in my very own binary lifter... As part of the documentation process, I decided to write a few words about my implementation of static recovery of a given function's control flow graph. Hope you enjoy it!
https://t.co/4e1tBzWlYv
Following the method demonstrated by @yarden_shafir in "Your Mitigations Are My Opportunities", this implementation automates adding a driver to the HvciDisallowedImages registry entry, ensuring it will be blocked from loading after the next reboot.
https://t.co/rNfJLHWITk
Article: https://t.co/q18JXbM6a8
Github: https://t.co/6VDyG3rlsk
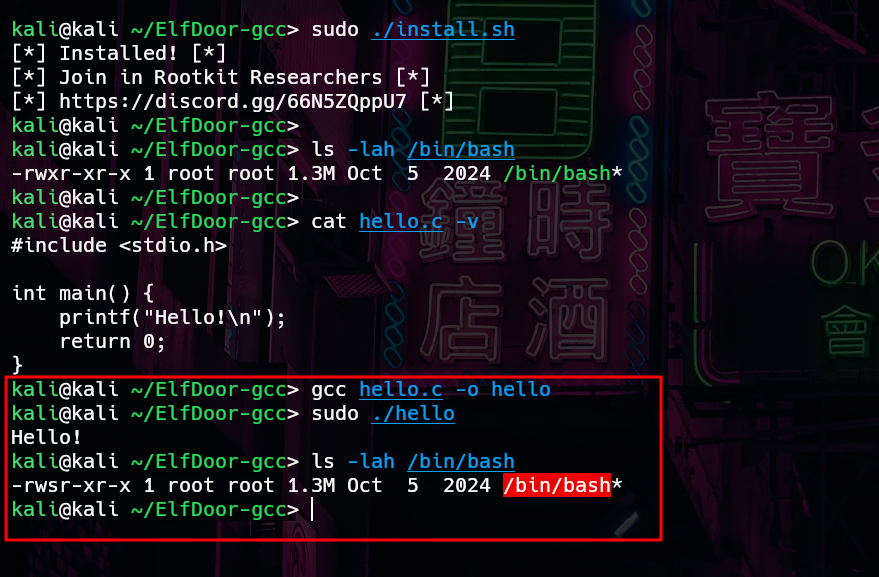
ElfDoor-gcc is an LD_PRELOAD that hijacks gcc to inject malicious code into binaries during linking, without touching the source code.
#malware#gcc#ldpreload#linux
https://t.co/QGsBQ6bNa8
Today an article was released that I wrote together with @humza4776466746 about Linux Kernel Rootkits, in it we talk about several very interesting things, feel free to read our article and share.
#rootkit#linux#kernel#ebpf
PermX from #HackTheBox video is now up! This is a nice easy box, starts out with a fileupload vulnerability and ends with having arbitrary write via sudo and symlinks. Show a few ways to abuse it, and why others don't work. https://t.co/ftJFfba1bY
Today I released a cheat sheet to detect and remove linux kernel rootkit without using any paid tools, if you want to contribute feel free.
#linux#rootkit#lkm#kernel#malware
https://t.co/okJEbcA7E3