🔥 Google's Pixel smartphones under attack!
Two new #Android security flaws - CVE-2024-29745 & CVE-2024-29748 - uncovered, exploited in the wild by forensic companies.
Learn more: https://t.co/jYqyaQp8r8
#CybersecurityNews#Hacking
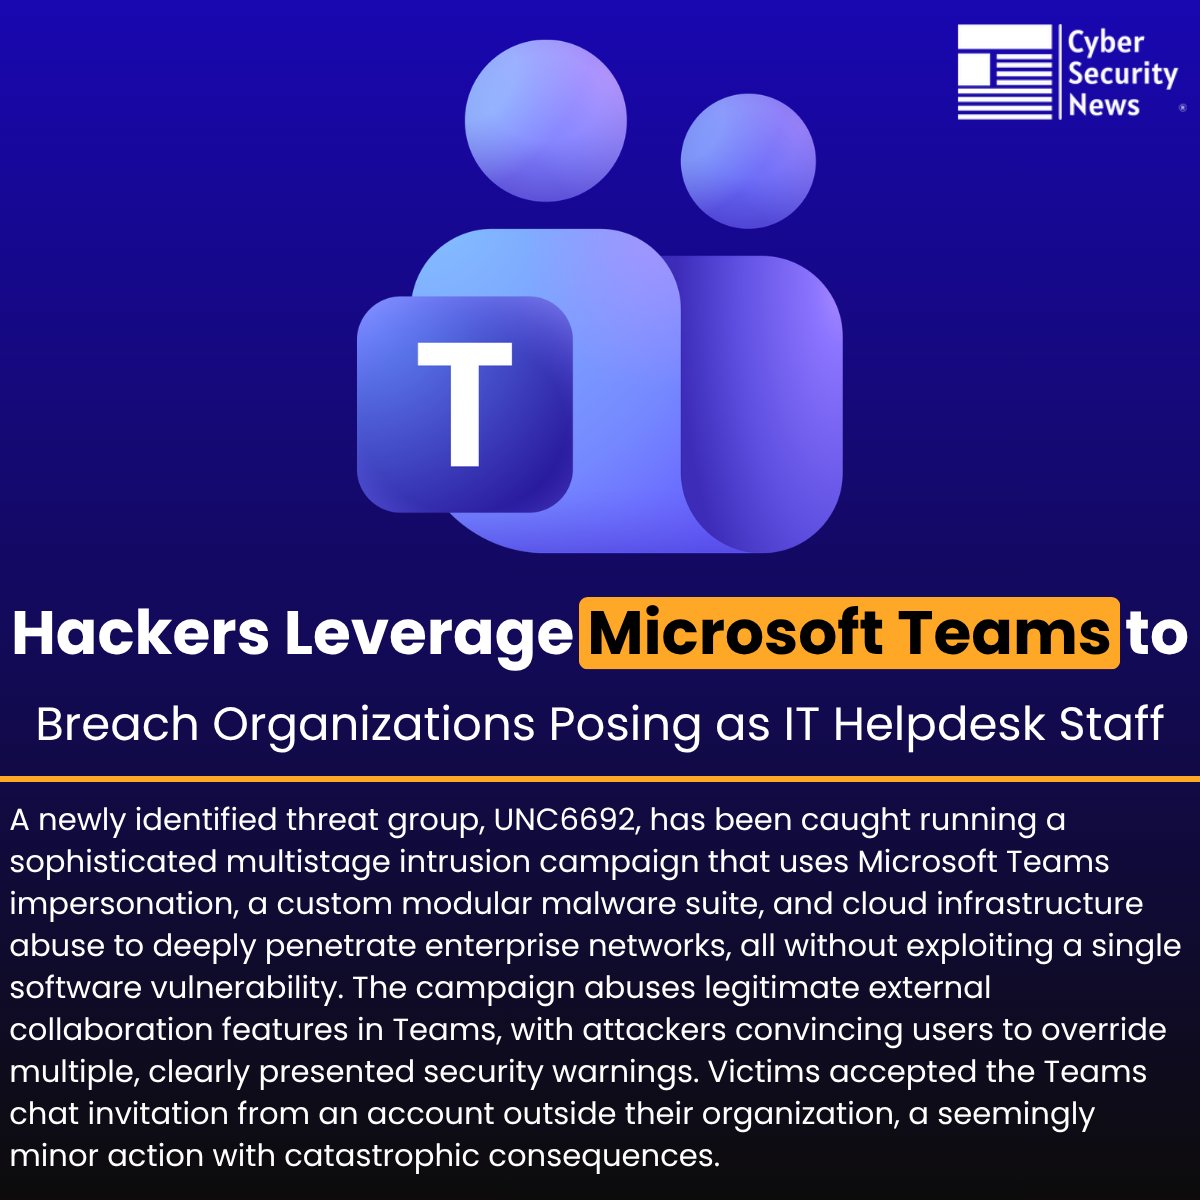
🚨 Hackers Leverage Microsoft Teams to Breach Organizations Posing as IT Helpdesk Staff
Source: https://t.co/dldRzGb0OW
A newly identified threat group, UNC6692, has been caught running a sophisticated multistage intrusion campaign that uses Microsoft Teams impersonation, a custom modular malware suite, and cloud infrastructure abuse to deeply penetrate enterprise networks, all without exploiting a single software vulnerability.
The campaign abuses legitimate external collaboration features in Teams, with attackers convincing users to override multiple, clearly presented security warnings. Victims accepted the Teams chat invitation from an account outside their organization, a seemingly minor action with catastrophic consequences.
#cybersecuritynews #teams
ANTHROPIC PAYS $750,000 A YEAR FOR ENGINEERS WHO UNDERSTAND WHY AI WORKS.
STANFORD JUST PUT THE SAME KNOWLEDGE ON YOUTUBE FOR FREE.
WATCH IT THIS WEEKEND. NOT EVENTUALLY. THIS WEEKEND.
⚠️ CrowdStrike LogScale Vulnerability Allows Remote Attackers to Read Files from Server
Source: https://t.co/ZIk1ToJCb8
An urgent security advisory for a critical unauthenticated path-traversal vulnerability (CVE-2026-40050) affecting its LogScale platform, warning that a remote attacker could exploit the flaw to read arbitrary files directly from the server’s filesystem without authentication.
The vulnerability resides in a specific cluster API endpoint within CrowdStrike LogScale. If this endpoint is exposed, a remote attacker can leverage it to traverse the server’s directory structure and access sensitive files without needing credentials.
#cybersecuritynews
LIVE: After returning to Earth on Dec. 9, @JonnyKimUSA is here today to recap his mission aboard the @Space_Station. Tune in to hear about his eight months on the orbiting lab. https://t.co/Yt2OjTvr1E
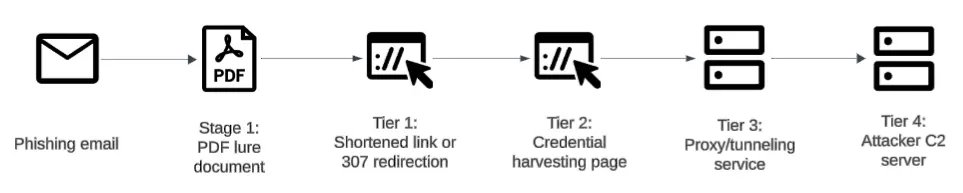
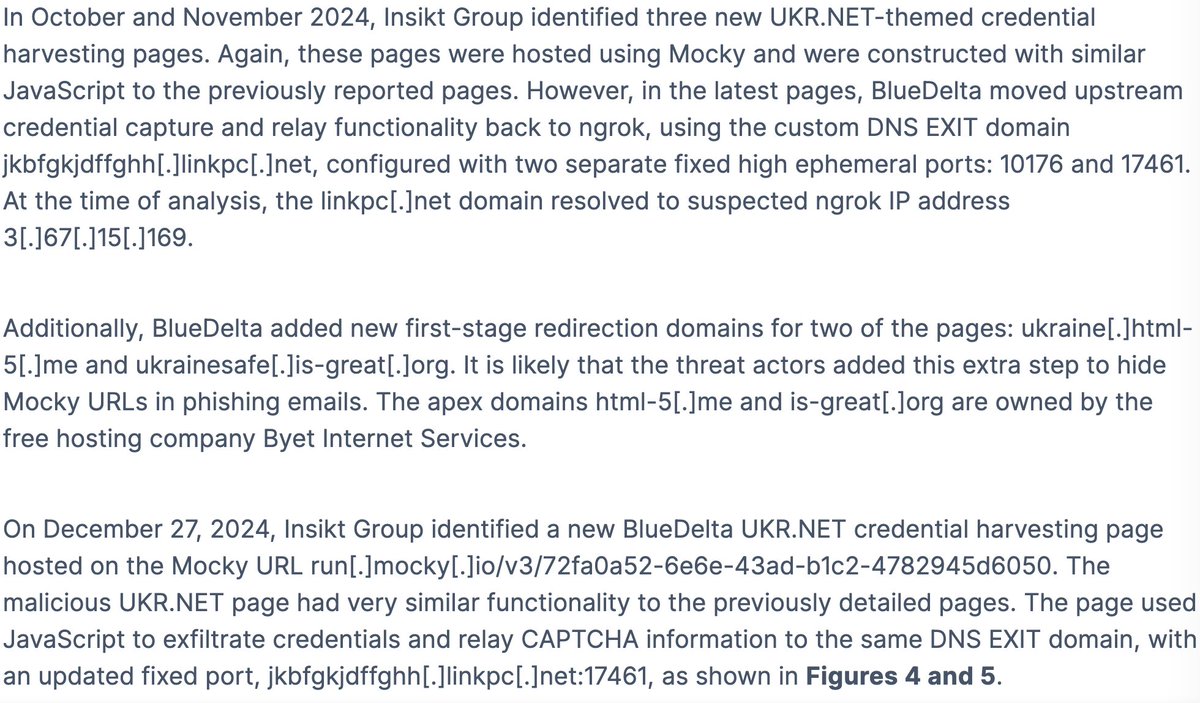
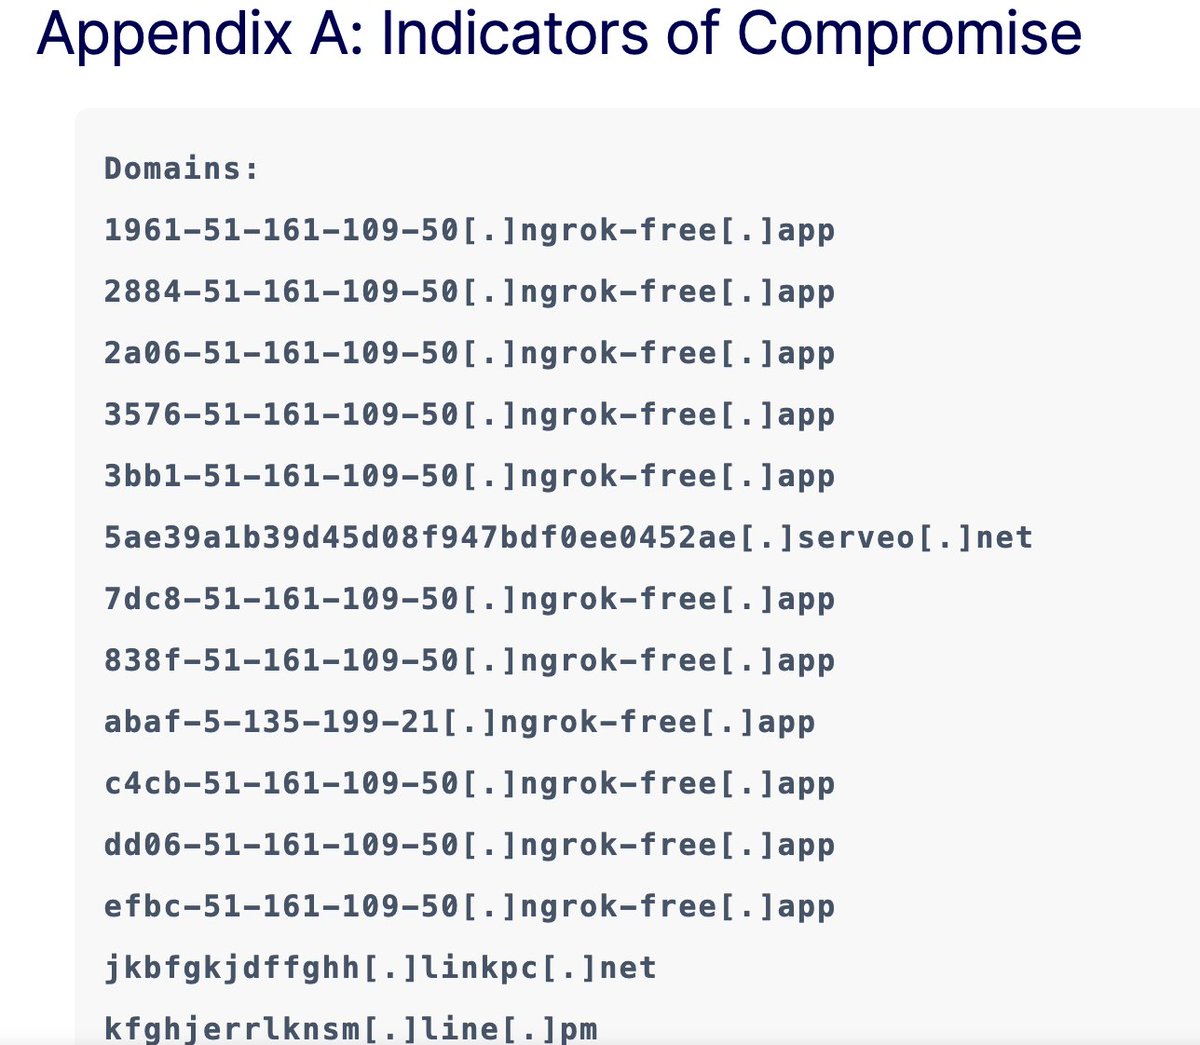
#APT28 transitioned from compromised routers to proxy tunneling platforms, such as ngrok and Serveo, to relay credentials and bypass CAPTCHA and two-factor authentication challenges.
https://t.co/zQiQyntt7S
Tired of your recon data getting bloated with static files?
Here is a quick katana one-liner to actively crawl deep, parse JS, and strip out the noise (css, svg, fonts, etc.) automatically.👇
katana -u subdomains_alive.txt -d 5 -kf -jc -fx -ef woff,css,png,svg,jpg,woff2,jpeg,gif,svg -o allurls.txt
🔥 Wild find from Microsoft.
Even when your AI chats are encrypted, someone watching the network can still guess what you’re talking about.
They call it "Whisper Leak" side-channel attack.
And in tests, models like #OpenAI and Mistral gave away topics with 98% accuracy.
Worth your attention ↓ https://t.co/xdco1xgGeE