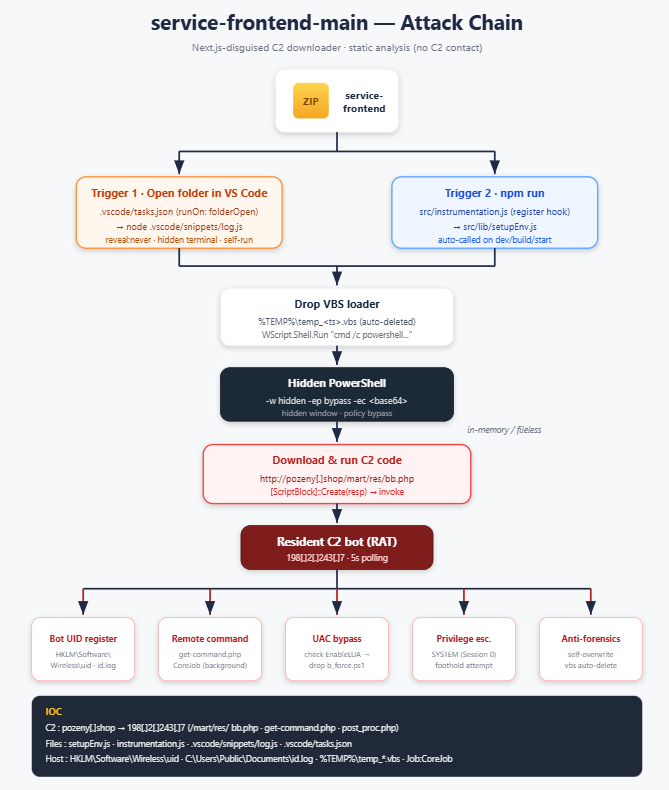
The infection trigger is redundant with two copies, and the malware overwrites its own file after execution to cover its tracks.
C2 domain: pozeny[.]shop
C2 IP: 198[.]2[.]243[.]7
C2 base: http://pozeny[.]shop/mart/
Analysis of a Trojan Hidden in a Project Targeting Korean Freelancers(Including IOCs)
Although it masquerades as a legitimate Next.js website, it contains a hidden downloader (C2 bot) that retrieves and executes PowerShell code from an external C2 server.
#CTI # Trojan Horse #IOC
🇰🇷 Threat actors are publicly distributing an alleged dataset linked to https://t.co/NsiP5Qblbc, a South Korean AI character chat and storytelling platform operated by Bunker Kids Co., Ltd.
According to the underground post, the leaked dataset allegedly contains approximately:
• 313,000 records
• structured JSON-style exports
• user/account-related information
• profile and application metadata
Publicly available information indicates WHIF is a South Korea-based AI entertainment/chat platform focused on story-driven AI interactions and webtoon-style experiences.
At this stage, the authenticity, scope, and origin of the alleged dataset remain unverified.
As with many underground leak claims involving consumer AI platforms, it remains unclear whether the data represents:
• a direct platform compromise
• exposed APIs or databases
• scraped public content
• third-party integrations
• or repackaged historical data
If confirmed, the exposure could create risks including:
• phishing campaigns
• account takeover attempts
• creator/user impersonation
• spam operations
• and social engineering targeting platform users
AI-driven social and entertainment platforms continue to attract underground attention due to their rapidly growing user bases, behavioral data, and integrated social ecosystems.
Daily Dark Web is continuing to monitor the situation.
#SouthKorea #Korea #CyberSecurity #DataBreach #ArtificialIntelligence #ThreatIntelligence #DDW #Intelligence
⚠️ Breach Claim Update reported by #Team_D4rkn3ttz@KNormal_Student
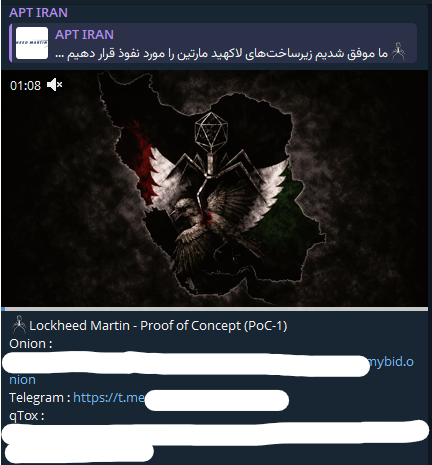
The threat actor group APT IRAN has released a Proof-of-Concept (PoC) claiming access to Lockheed Martin’s infrastructure.
The shared material includes:
• what appears to be an internal email interface
• Claimed evidence of system access (PoC-1)
The actor reiterates earlier claims of:
• F-35 and defense-related materials
• Employee and internal communications data
⚠️ At this stage:
• The PoC does not independently confirm full compromise
• The origin and authenticity of the remain unverified
#APTIRAN #LockheedMartin #CyberThreat #ThreatIntel #DataBreach
⚠️ Critical Access Sale Reported by #Team_D4rkn3ttz@KNormal_Student
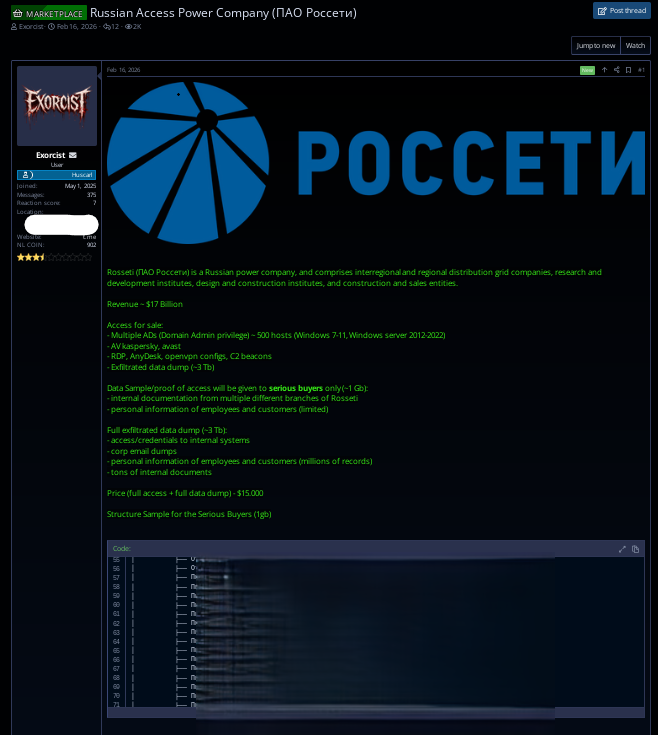
A threat actor on a cybercrime forum is offering full access to Rosseti (ПAO Россети) — one of Russia’s largest power grid operators.
Key claims from the listing:
• Domain Admin privileges across ~500 hosts
• Windows environments (Win7–11 / Server 2012–2022)
• Access via RDP, AnyDesk, OpenVPN configs, and C2 beacons
• Presence of AV solutions (Kaspersky, Avast)
📦 Data exfiltration (claimed):
• ~3 TB total data dump
• Corporate email archives
• Internal documentation across multiple branches
• Personal data of employees & customers (millions of records)
• Credentials to internal systems
⚠️ At this stage:
• The claim remains unverified
#Rosseti #CriticalInfrastructure #AccessBroker #CyberThreat #ThreatIntel
⚠️ Website Defacement Detected by #Team_D4rkn3ttz@KNormal_Student
On February 24, 2026, the website gsdreamjob[.]or[.]kr was observed displaying a defacement page attributed to Z-BL4CX-H4T-ID (Indonesia).
📡 Detection Source
This incident was automatically detected through BLKIntel, our internally developed threat intelligence monitoring platform.
🔎 Assessment
• This appears to be a web defacement incident, not a data breach claim.
• No immediate evidence of backend database exposure observed at this stage.
• Attribution aligns with previous Indonesian hacktivist patterns targeting random .kr domains.
#ZBL4CXH4TID #Defacement #SouthKorea #CyberThreat #ThreatIntel
⚠️Threat Detection reported by #Team_D4rkn3ttz@KNormal_Student
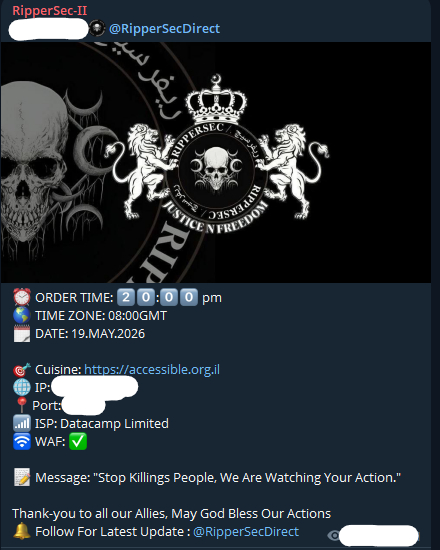
On February 15, 2026 (08:00 PM), the hacktivist group RipperSec II published an attack order targeting:
• https://t.co/GcmOKuKojO
• ISP referenced: Korea Federation of Banks
Detection: The threat from that Rippersec was discovered using a platform created by the analyst.
#RipperSec #SouthKorea #OpKorea #CyberThreat #ThreatIntel #Hacktivism
🚨 Threat Detection Update by #Team_D4rkn3ttz@KNormal_Student
On February 15, 2026, the hacktivist group BD Anonymous published an attack order under the name “Operation South Korea”, targeting ktoa[.]or[.]kr.
The post included:
• Claimed attack time (13:30)
📡 Detection Source:
The 2nd and 3rd screenshots show this activity being detected and tracked through a custom-developed monitoring platform, built to identify hacktivist threat signals in real time.
Through the platform, we were able to:
• Detect the post within minutes of publication
• Comprehensive monitoring and detection, automatic feed generation, etc.
#BDAnonymous #RipperSec #OperationSouthKorea #OpKorea #CyberThreat #ThreatIntel
⚠️ Activity Update reported by #Team_D4rkn3ttz@KNormal_Student@none_028
We observed a South America–based Telegram channel sharing multiple “result” files allegedly related to activity against a Korea Health Industry Development Institute (KHIDI) domain.
The channel posted :
• Multiple .txt result files labeled as “Nodo 1 / Nodo 2 / Nodo 3 (100 max.)”
• Multiple email addresses and passwords
• References to the target domain within the file names
#KHIDI #SouthKorea #DDoS #CyberThreat #ThreatIntel
⚠️ Threat alert reported by #Team_D4rkn3ttz@KNormal_Student@none_028
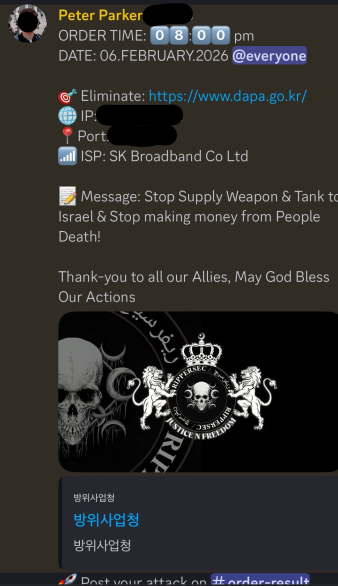
⏱ Timeline — RipperSec Attack Order (Follow-up)
📅 February 6, 2026 | 20:00 (claimed time)
The hacktivist group RipperSec published a follow-up attack order post, this time explicitly targeting a South Korean government-related domain.
Details shared by the actor:
Target URL: dapa[.]go[.]kr (Defense Acquisition Program Administration)
Claimed IP, Ports mentioned
ISP referenced: SK Broadband Co., Ltd.
Message included political and ideological statements related to Israel and arms supply
🔎Assessed as threat signaling / psychological pressure, not verified compromise
#RipperSec #DAPA #SouthKorea #OpKorea #CyberThreat #Hacktivism #ThreatIntel
Threat alert reported by #Team_D4rkn3ttz@KNormal_Student@none_028
Timeline — RipperSec Attack Order
February 5, 2026 | 20:00 (claimed time)
The hacktivist group RipperSec published an attack order post targeting a South Korea–related web service.
Details shared by the actor:
Target URL: hd[.]com/kr/main
Claimed IP, Ports, Hosting provider referenced
Message included political and ideological statements
#RipperSec #SouthKorea #OpKorea #CyberThreat #Hacktivism #ThreatIntel
🚨 Major multi-dataset leak claim reported by #Team_D4rkn3ttz@KNormal_Student
We have identified a series of large-scale data leak claims posted on the DEDSEC Telegram channel.
According to the actor, the following datasets were exposed:
• 🇨🇳 China loan records (2024)
• 2TB SQL database allegedly containing Chinese government citizen data
• 🇨🇳 Shanghai Government dataset (49GB)
• Additional large personal/address datasets (names, ID numbers, phone numbers, birthdates, addresses, etc.)
The screenshots show structured JSON/SQL entries including fields such as:
– Name
– Phone number
– Gender
– Birthday
– ID/ID card
– Address
– Company / industry chain data
– Various metadata fields
#DataLeak #China #Shanghai #DEDSEC #CyberThreat
@KNormal_Student, an analyst from Team D4rkn3ttz,
will be presenting at this year's HolyShield Conference 2025
on the topic: “From Bluster to Threat: A Real-World Hacktivist Experience.”
Those interested can register to attend via the link below.
https://t.co/cxOat01xO7
We look forward to your participation!
Reported by #Team_D4rkn3ttz@KNormal_Student
Further analysis revealed that the blockchain wallet used in the SK Telecom data breach incident is identical to those associated with #CyberSell666 and #DigitalGhost. These wallets were previously linked to the NATO data breach incident.
Confirmed wallets:
• BTC: bc1q5v7y5r5fkm80cnhp7fuwrx6expyeyhnhnns2sc4z0ma3kfc83apq7j736r (mixing address)
• BTC(2): 14v1giLjrV1kDJ55cAfu74Cv1EvmJpLYMH
• ETH: 0x07B06eA0aa2224cC7e37DcB2d8BE6BD7e4f63019
• SOL: GCirGRQc8tZKMncvGhQVSGb18pnGHsAM9BEtRkh5MuUV
The same BTC wallet was found in the NATO dataset sale reported by CyberSell666 (Source: https://t.co/uSvAw3eFal, July 19, 2025).
Additionally, the Tmap dataset reappeared, suggesting reused or duplicated content.
#SKTelecom #DataLeak #DigitalGhost #CyberSell666 #Rubicon #CyberThreat #Blockchain #ThreatIntelligence