I think most people had a misconception of how Ledger devices worked, and I think it’s a very important distinction.
Most people assumed ledger had no access to your private key. Simply put this isn’t true at all. Ledger can easily install a backdoor in their firmware. They could already have a backdoor. They could’ve had one since day 1.
Using a ledger is *trusting* ledger in a big way.
Arguably it’s not better than storing your crypto on an exchange like Coinbase. Either way you’re fundamentally trusting some entity.
It has different trade offs to something like a hot wallet.
I think most importantly this highlights that we need *better solutions*. These current hardware wallets solutions are unacceptable for wide scale adoption. There’s counter party risk.
Ledger secures approx $200B in assets. That’s a lot of incentive to do something malacious. What happens when it’s $2T, $20T? Or when a state comes and forces them to put a backdoor? Have they already? Would we even know?
We need to do better. What many would call the gold standard, Ledger, is again centralizing power in a way that can be exploited.
Is anyone working on a better solution? It’s not a good look for the space that this is the best we have after 14 years.
@hosseeb@Ledger If the older Ledger Nano S (non-“plus” version) doesn’t have the capability of exporting the private key then why are you fine with the newer devices being able to?
I have personally used Ledger hardware wallets for about 7 years. Today is the first day I've decided to look elsewhere.
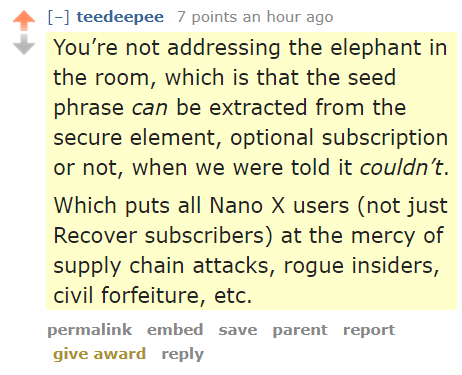
Apparently, newer Ledger hardware devices (Nano S plus and Nano X) have the capability of sending the private key from the device. Not good.
This just came to light as Ledger unveiled its #LedgerRecover service. This "recovery service" is actually not the core issue. It's what it tells us about the hardware wallet's capabilities.
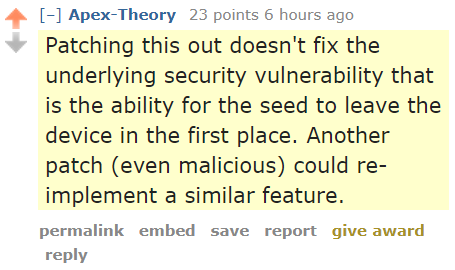
A properly secure hardware wallet shouldn't be capable of sending the private key. Period.
The fact that the device has the capability of sending the private key is the flaw. Even if Ledger were to release a patch to "address the issue", they can't fix this issue because they have just admitted the hardware device is capable of sending the private key.
I've seen some red-herring discussions regarding this (for example, some will say "Don't worry. It's an opt-in feature. Just don't opt in." or "Just don't update to the newest firmware", etc.) but they are all missing the above, single, massively important point.
Btw, supposedly the older Ledger Nano S (non-"plus" version) doesn't have this capability (flaw).
A temporary, stop-gap solution can be to use an older, Nano S (non-"plus") device. But, Ledger as a company isn't really trustworthy at this point, imo, especially after they already leaked all of our personal information on the Internet in 2020. ( https://t.co/qXZ0Wc18Gl )
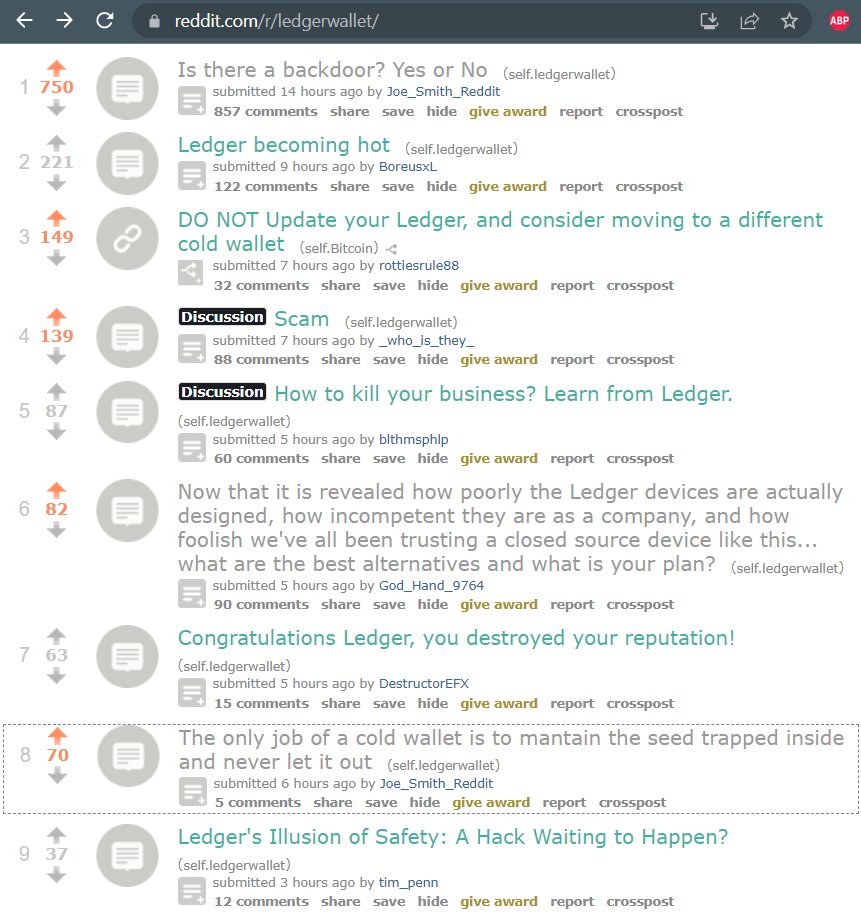
I suggest you educate yourself and read up on this topic further. There's a lot of discussion about this on the Ledger sub-reddit right now:
https://t.co/XYz20N4JlN
@Ledger No disrespect, just a balanced Reddit post for all the “new people” entering Crypto... don’t want you to fall for a substandard security device produced by a company with substandard journalism and reporting. #BoycottLedger
People should be terrified that @Ledger can claim for marketing how much crypto their users collectively have 🙈
Is your crypto/Bitcoin part of their 20% figure? If so, get it out now. 👇
I started seeing posts about #Ledger on my timeline.
Probably because of some new announcement done recently. But it was obvious a long time ago...
If you're still unsure whether your seed can be leaked from your #Ledger, read this:
https://t.co/wzXF02D4Vy
⚠️WARNING ⚠️
I am extremely angry now with @Ledger and their incompetence getting hacked, (scam emails, text messages and phone calls I get this email just now!)
Now I will be taking this further as @Ledger just saying sorry isn't good enough when my family is threatened
So I've Been A @Ledger Affiliate For Years...
Making Them Thousands of Sales....
Ive Contacted Support as Im Locked Out of My Acct
Due to A Change From Their Secret Key
To a Acct/PW System
They Have Ghosted Me & Now Arent Replying to Any of My Inquiries
WTF!? @Ledger_Support
Next level phishing attempts ongoing, yet @Ledger never ceased to downplay the impacts of the hack of their databases.
This level of negligence is unforgivable and should be punished by the market but unlikely to happen given their millions invested into marketing efforts.
A hacker attacked #Ledger and has stolen ~$484K assets.
#LedgerExploiter transferred 4.334 $ETH to #AngelDrainer.
And the #AngelDrainer is also receiving assets currently and holds $363K assets.
https://t.co/ZG5SRlKBjW
What happened?
In short, @Ledger made a chain of terrible blunders.
1. They are loading JS from a CDN.
2. They are not version locking loaded JS.
3. They had their CDN compromised.
I would avoid using ANY dApps until their teams confirm that they have mitigated the attack.
Ledger betraying their customers for
the 60th time in last 6 years
They are like we can always fuck your
keys up but you just didn’t know and
trusted us.
Like BROO! We didn’t know that’s why
we trusted you. Not anymore
LEDGER IS DONE
How about a class action lawsuit against @Ledger for lying to us all these years?
What good is a hardware wallet if this is the case?
Get bent, Ledger.
Ledger’s response to accusations of having backdoors and the ability to share seed phrases with government officials: a strong and reassuring statement. Solid reply and a good read.