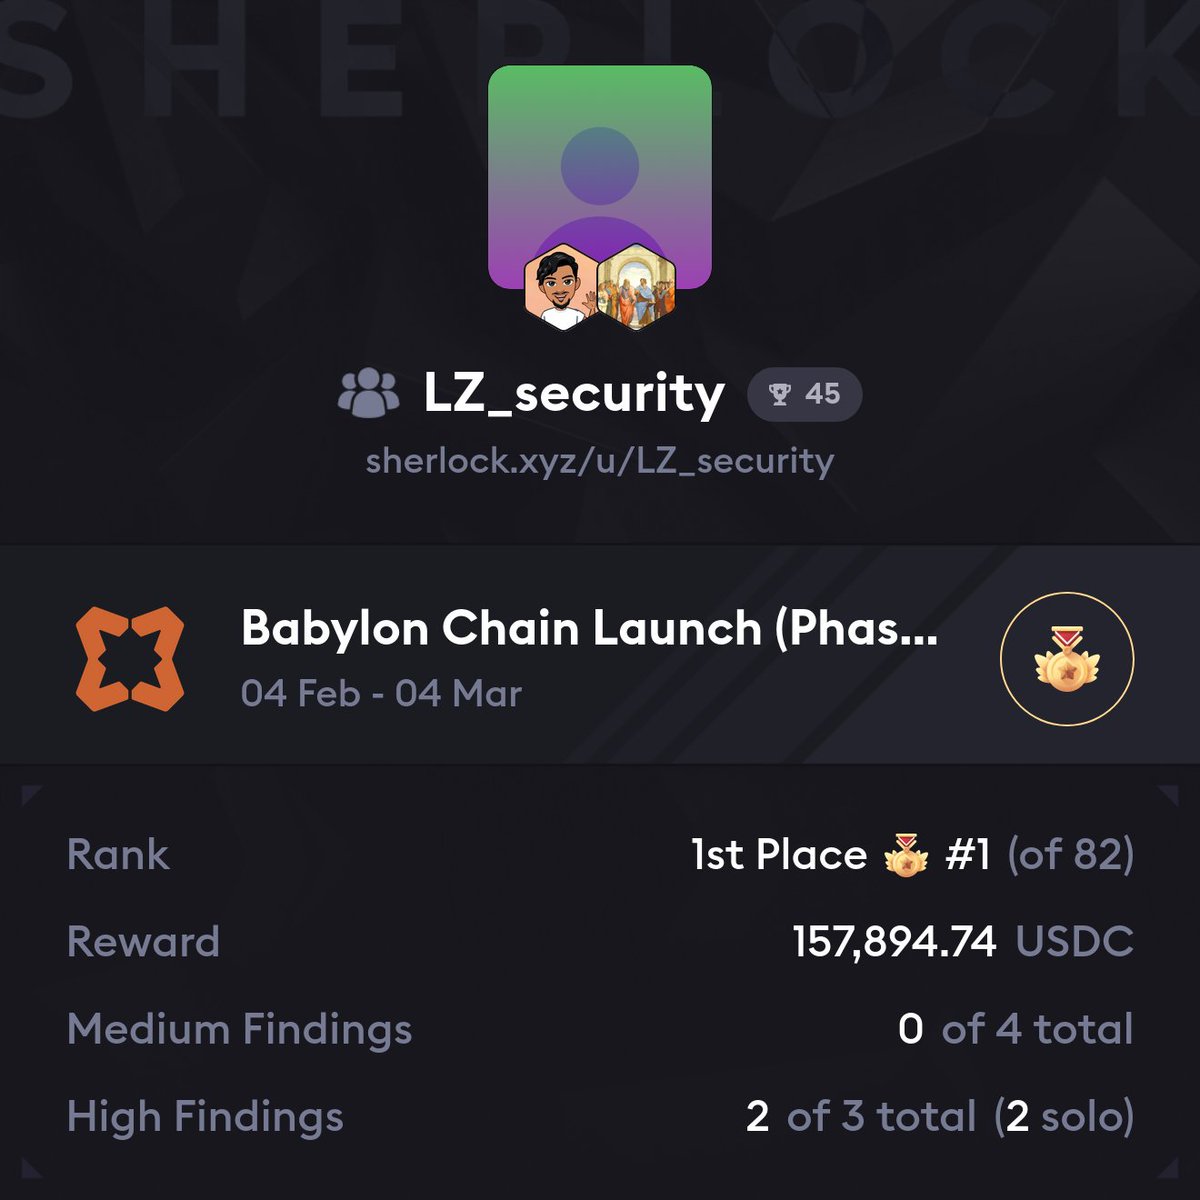
After securing several second and third places, we've finally got first place!
A huge thanks to @sherlockdefi and @babylonlabs_io for this incredible opportunity.
What a huge and elegantly crafted codebase—definitely worth diving deep into !
I've been cooking hard over the last few weeks to get my new project @Stature_finance up and running. After billions of tokens and not seeing the sun for a while, I submitted the first version for the @solana Stocklana hackathon today. Stature will be the easiest and cheapest way for end users to buy tokenized stocks.
Now I still have about 2 weeks left to add more functionality, start the beta, and get the first people to actually invest using the app before I hand it in for the big Colloseum hackathon.
I'm a complete newbie at videos, but my assistant (he loves to eat tokens) and I got it to look really decent, so I'll share it here with all of you
Also, check out the website/waitlist -> https://t.co/n3lJe0JsRp
Today we are announcing that S&P Global has entered an agreement to acquire OpenZeppelin.
Onchain finance is growing from an emerging market into core financial infrastructure, and the standards and rails our team and community built are becoming the rails of global finance. OpenZeppelin smart contracts facilitated over $37 trillion in value transferred, with the vast majority of the largest DeFi protocols, blockchain networks, stablecoins and tokenized funds relying on them.
With S&P Global, we expect to accelerate the impact of onchain finance, backed by more than a century of trust in global markets, benchmarks, and risk frameworks.
To our clients and to all the users of OpenZeppelin open source tools:
• OpenZeppelin Contracts and all our open source applications and tools remain open source, free, and publicly maintained on GitHub. Building open source standards stays a core priority.
• Audits, engineering work, and ecosystem programs continue with the same team, brand, quality, and customer experience, with what will be the added benefit of S&P Global's research capacity, market data, and institutional reach.
For the last decade, OpenZeppelin has set the security standard for onchain finance. Today begins a new chapter for that mission, together with one of the most trusted names in global markets.
Read the full announcement: https://t.co/lxBUWkWVUK
I found the same issue, but just one day after he submitted his report, so mine was marked as a duplicate.
Luck wasn’t quite on my side this time, but I’m genuinely happy for @brandon_shi my bro. Congrats, well deserved! 🤝
A completely new security format is emerging.
One of the biggest protocols in Web3 is working with Sherlock to put it to the test.
June 15 to July 6.
More revealed tomorrow.
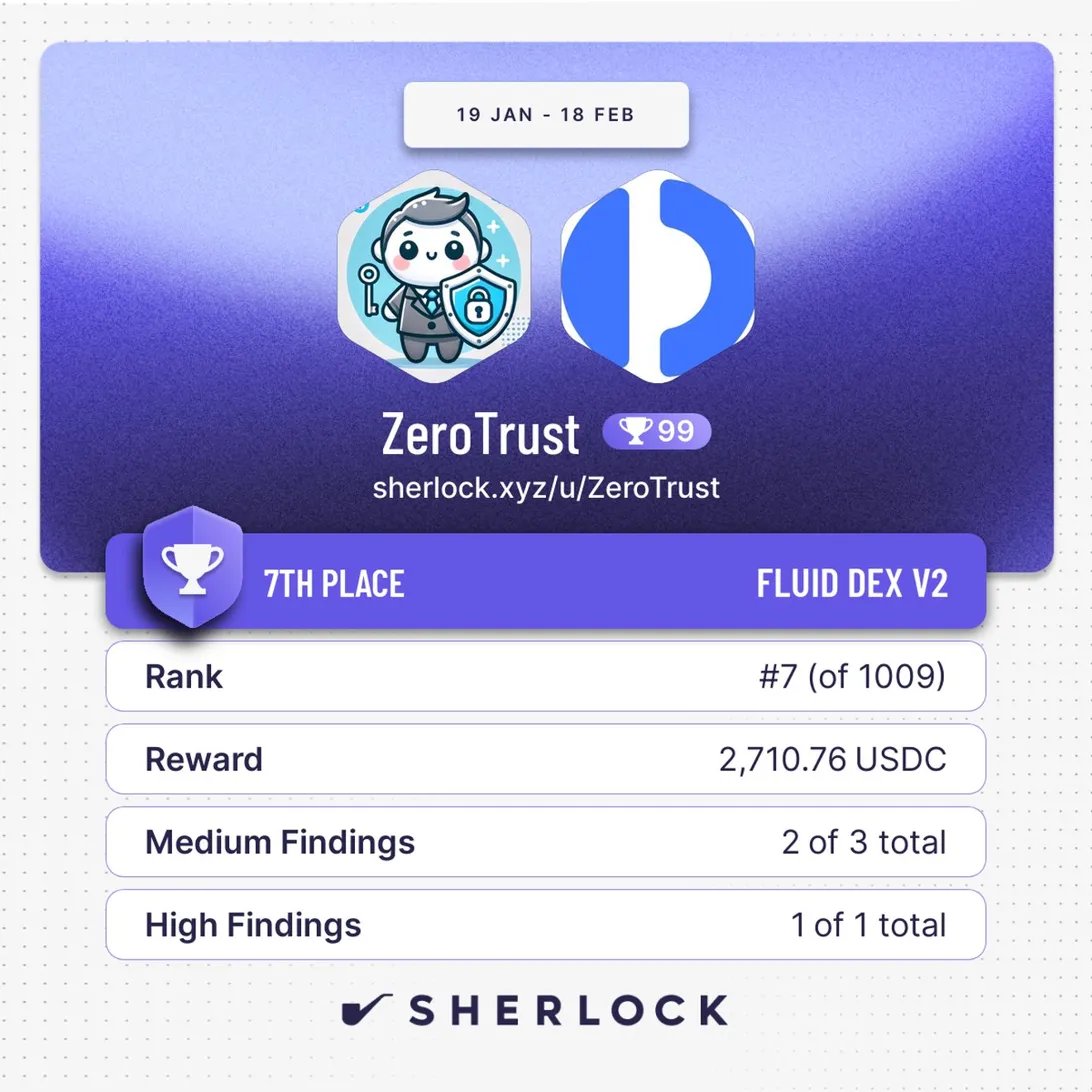
Thanks @sherlockdefi and @0xfluid for the great opportunity!
Hit 3 out of 4 issues .
Only regret? Missing the one with the fewest dups... that one stung a little 😅
Also curious — how did the AI Bot perform in this contest? Anyone know? 👀
Hi @sherlockdefi ,
Will there be a Lead Sensor Watson assigned for this audit contest?
In the previous XRP Ledger audit, we ranked 3rd based on valid finding score (and 5th based on total rewards).
Would LZ_security have a chance to be selected as a Lead Sensor Watson this time?
Major Announcement: The XRP Ledger roadmap is getting a $550K audit contest!
In collaboration with @RippleXDev, we’re putting upcoming XRPL features under a two-week, feature-unlock security review.
Contest starts Monday. Prepare yourselves!
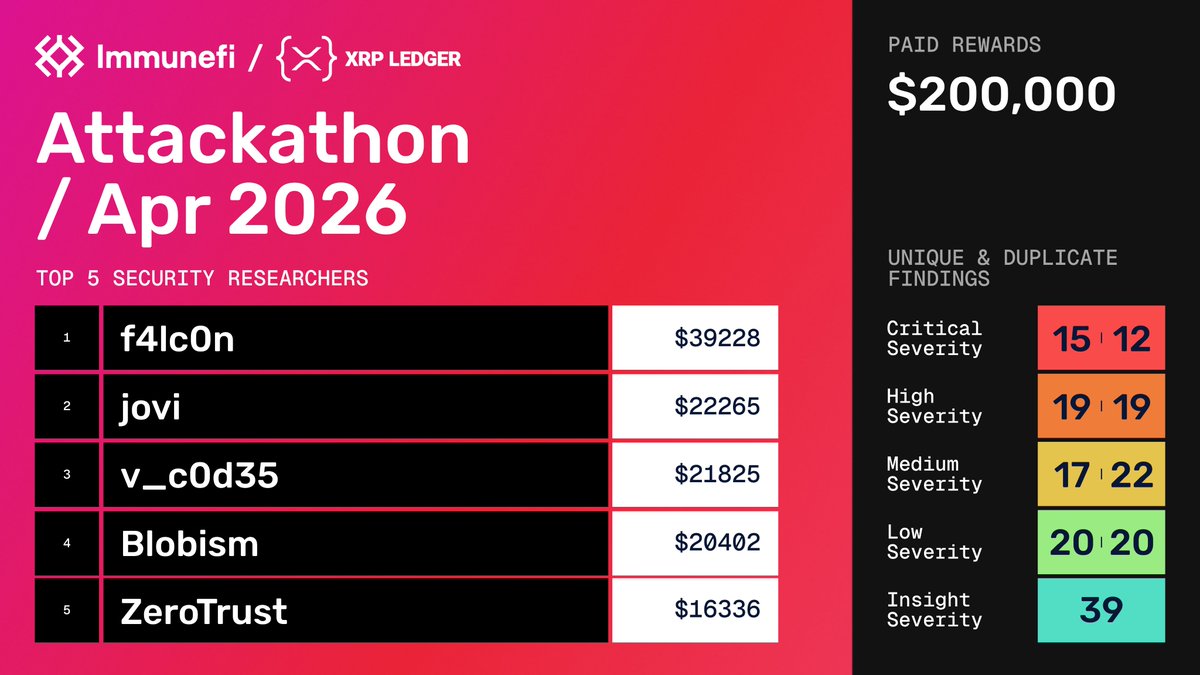
The $200k USD @RippleXDev Attackathon has officially concluded, and 100% of the reward pool has been paid out!
⚡ Top Winners:
🥇 @al_f4lc0n — $39,228
🥈 @0jovi0 — $22,265
🥉 @v_c0d35 — $21,189
4️⃣ @blobismdev — $20,402
5️⃣ @LZ_security — $16,336
Check out the full leaderboard below 👇 https://t.co/KsPG6fjkzV
@al_f4lc0n@immunefi Web3 loves advertising $500K–$1M critical bounties, but too often those numbers only exist until someone actually finds one.
If payouts aren't realistically budgeted or reserved, they're just marketing.
Researcher trust is hard to build and easy to lose.
I Saved Injective's $500M. They Pay Me $50K.
I like hunting bugs on @immunefi . I'm decent at it.
- #1 — Attackathon | Stacks
- #2 — Attackathon | Stacks II
- #1 — Attackathon | XRPL Lending Protocol
- 1 Critical and 1 High from bug bounties (not counting this one)
Life was good. Then I found a Critical vulnerability in @injective .
This vulnerability allowed any user to directly drain any account on the chain. No special permissions needed. Over $500M in on-chain assets were at risk.
I reported it through Immunefi. The next day, a mainnet upgrade to fix the bug went to governance vote. The Injective team clearly understood the severity.
Then — silence. For 3 months. No follow up. No technical discussion. Nothing.
A few days ago, they notified me of their decision: $50K. The maximum payout for a Critical vulnerability in their bug bounty program is $500K. I disputed it. Silence again. No explanation for the reduced payout. No explanation for the 3 month ghost. No conversation at all. To be clear: the $50K has not been paid either.
I've seen others share bad experiences with bug bounty payouts recently. I never thought it would happen to me. I can't force them to do the right thing. But I won't let this be forgotten.
I will dedicate 10% of all my future bug bounty earnings to making sure this story stays visible — until Injective pays what I deserve.
Full Technical Report: https://t.co/lki2tL9bxw
Thanks to @Immunefi and @RippleXDev for the great opportunity.
I once said I didn’t like how the leaderboard ranking worked.
Then my AI agent analyzed the hidden leaderboard data and rebuilt a new ranking… and sent it to my wife telling her I got 3rd place on the largest Web3 bounty platform 🤖
My agent cares about my reputation more than I do 😂